

reburp
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
forefy/reburpA Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 githubsecuritylab/seclab-taskflows-fuzzing
An LLM-driven fuzzing pipeline powered by the GitHub Security Lab Taskflow Agent
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 safety-research/red-teaming-auto-mode
Research code for red-teaming AI auto-mode monitors, including simulation evals, fuzzing, and monitor implementations for Claude Code and Codex…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 off-by-1-labs/flawed
Fix-Like Artifacts With Embedded Defects
 harshrajsinghania/cve-2026-86547-mrubyc-op-enter
Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 isukasanuj/cve-2026-85769
Proof-of-concept exploit for CVE-2026-85769, a heap out-of-bounds read in libtpms TPM 2.0 state deserialization, demonstrating denial of service via…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 kihara-1/postgresql-cve-2026-14662
PostgreSQL の全文検索(tsvector/tsquery)に見つかった範囲外書き込み脆弱性 CVE-2026-14662 を、修正前(18.4)と修正後(18.6)を Docker で並べて動かして検証した記録と発表資料
 foxirain/linux-kernel-codex-harness
Evidence-driven Linux kernel vulnerability research harness used in the investigation of CVE-2026-31720
 fuzzingbrain/fuzzingbrain-bench
A benchmark for LLM-driven bug discovery: 77 challenges across 43 open-source projects (C/C++/Java).
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 acen28/cve-2026-26399-disclosure
Disclosure of a stack-based use-after-return vulnerability in Arduino_Core_STM32, detailing technical root cause, affected versions, and fix, with…
 0xbbdd/cve-2026-33317
Proof-of-concept for CVE-2026-33317, an out-of-bounds write in OP-TEE PKCS#11 TA, demonstrating Secure World heap corruption via a malformed…
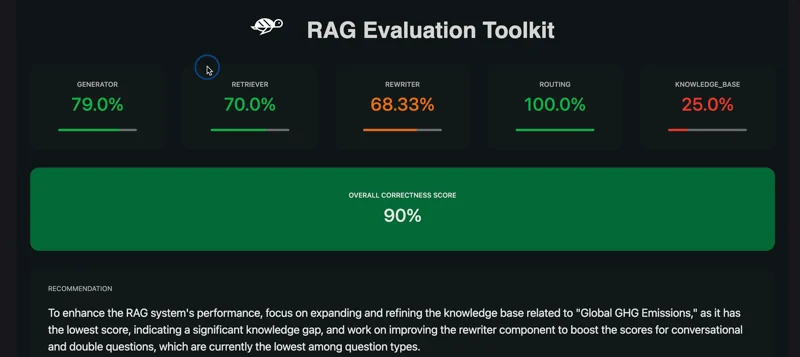 giskard-ai/giskard-oss
🐢 Open-Source Evaluation & Testing library for LLM Agents
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.