
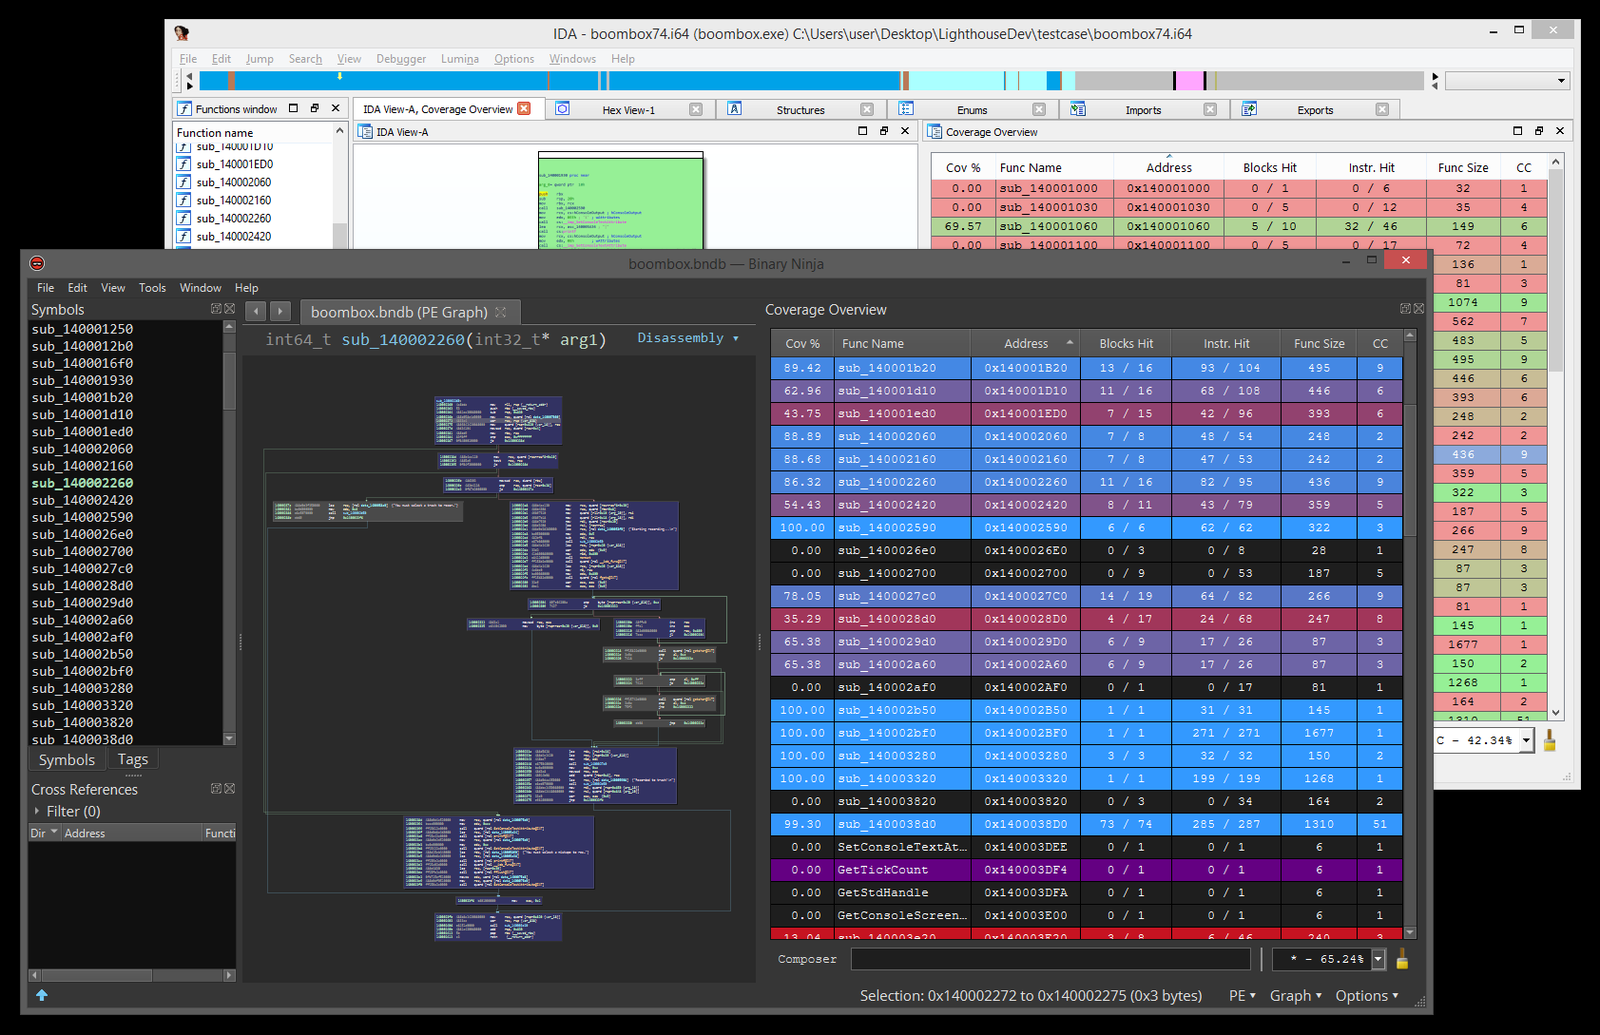
lighthouse
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
binary-analysiscode-analysisdebuggers+6
gaasedelen/lighthouseA Coverage Explorer for Reverse Engineers
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 devrodt2/cve-2026-28609-matroska-pcm-oob
Proof-of-concept and instrumented reproduction harness for CVE-2026-28609, an out-of-bounds write in Android's MatroskaExtractor reachable via a…
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
 m4rc0s-s3c/cve-2025-5548-freefloat-ftp-lab
Laboratorio académico de análisis y explotación de CVE-2025-5548 en FreeFloat FTP Server 1.0.
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
 alvarosr/cve-2025-5548
Documented technical analysis and controlled exploitation of CVE-2025-5548 in FreeFloat FTP Server, covering lab setup, static/dynamic binary…
 r3n3r0/cve-2026-27280
In-depth analysis and proof-of-concept for CVE-2026-27280, an out-of-bounds write in Adobe DNG SDK's dng_render_task::ProcessArea, reachable via…
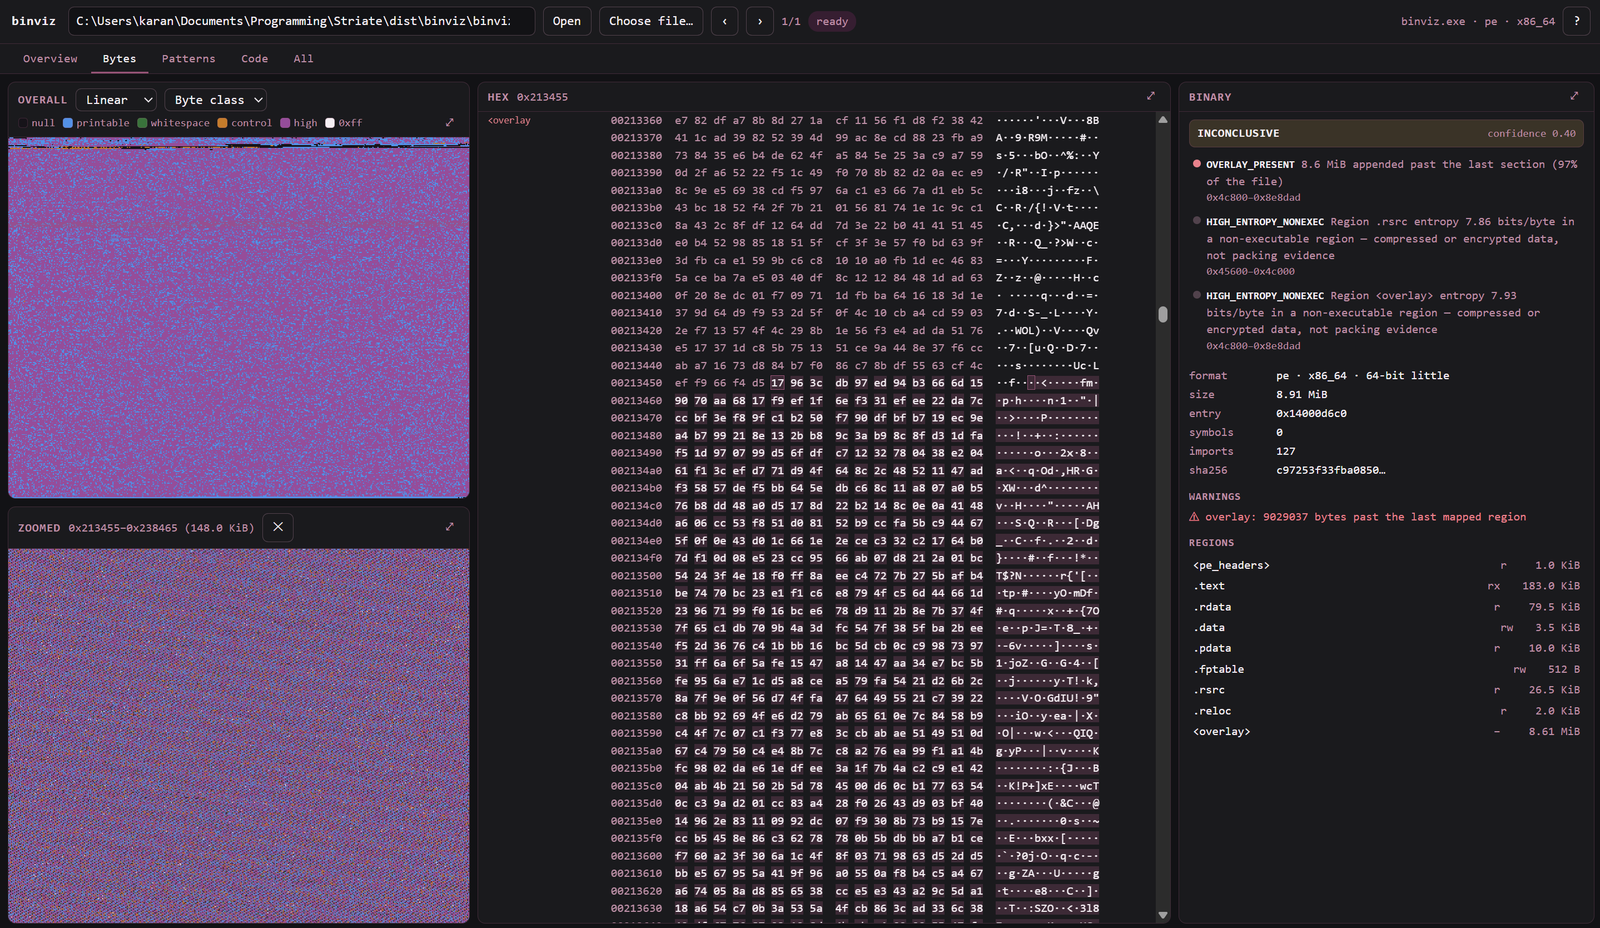 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 thisistfs/rogue-framework
Desktop workbench for AFL++ fuzzing, cross-architecture QEMU emulation, harness development, Ghidra headless analysis, custom mutators, and patch…