
fuzz
 xsscx/fuzz
Commodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
curated-resourcesexploitationfuzzing+6
xsscx/fuzzCommodity Injection Signatures, Malicious Inputs, XSS, HTTP Header Injection, XXE, RCE, Javascript, XSLT
 minimaxir/big-list-of-naughty-strings
Curated list of malicious and edge-case input strings (blns.txt/blns.json) for QA and security testing of user-input validation, injection, and…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 yuatemycat/superghidra
Python toolkit accelerating Ghidra with a cached daemon, ARM64 P-code lifting, Z3 equivalence proofs, GPU-accelerated scanning, binary diffing, and…
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
 gach0ng/agentstalker
End-to-end security audit framework for LLM agents: static AST and taint modeling, attack synthesis, Docker sandbox replay, and deterministic verdict…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
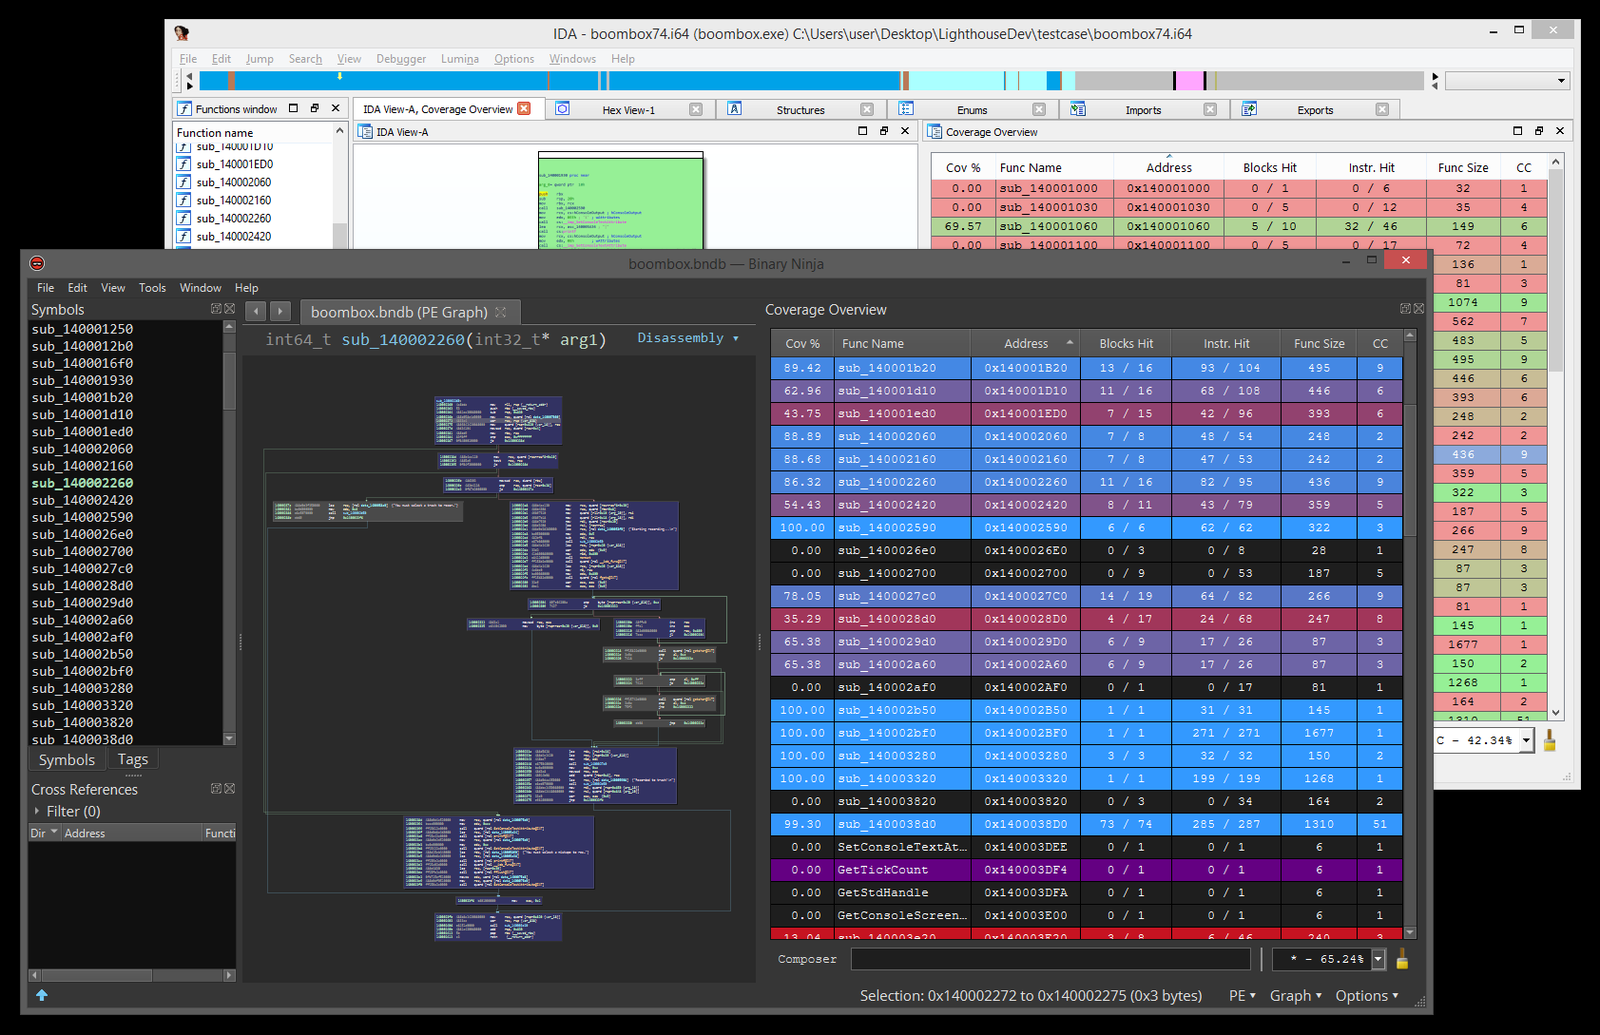 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 akha-security/akca
Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
 rix4uni/wordlist
Curated collection of custom wordlists for fuzzing, DNS enumeration, parameter discovery, and default credentials, plus a Go generator for nuclei…
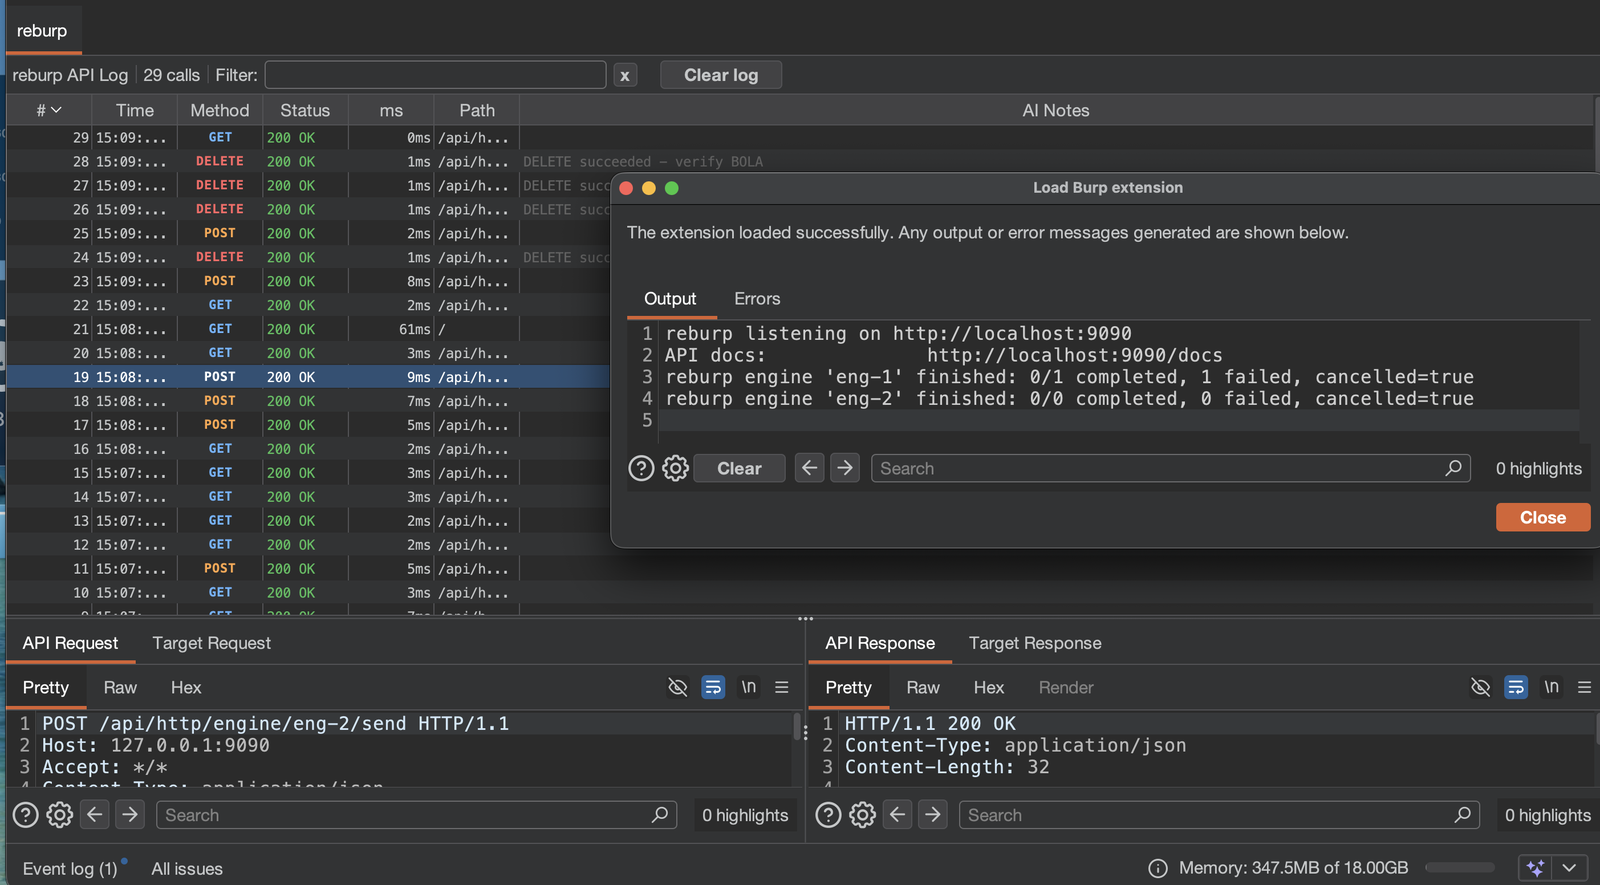 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.