
h2spacex
 nxenon/h2spacex
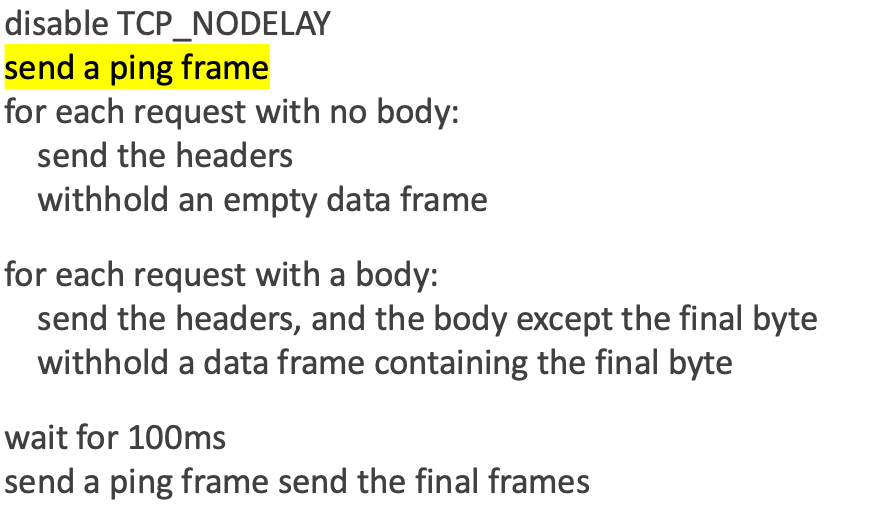
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
exploitationfuzzingnetwork-security+6
229
nxenon/h2spacexHTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 manishkanyal/log4j-scanner
A Log4j vulnerability scanner is used to identify the CVE-2021-44228 and CVE_2021_45046
 hardik05/damn_vulnerable_c_program
An example C program which contains vulnerable code for common types of vulnerabilities. It can be used to show fuzzing concepts.
 nccgroup/triforceopenbsdfuzzer
System call fuzzing of OpenBSD amd64 using TriforceAFL (i.e. AFL and QEMU)
 maximilianljungblut/hipcam-rtsp-format-validation-vulnerability
This POC exploits a format validation vulnerability in the RTSP service of the Hipcam RealServer/V1.0, inducing a crash for approximately 45 seconds…
 rfidtool/esp-rfid-tool
A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
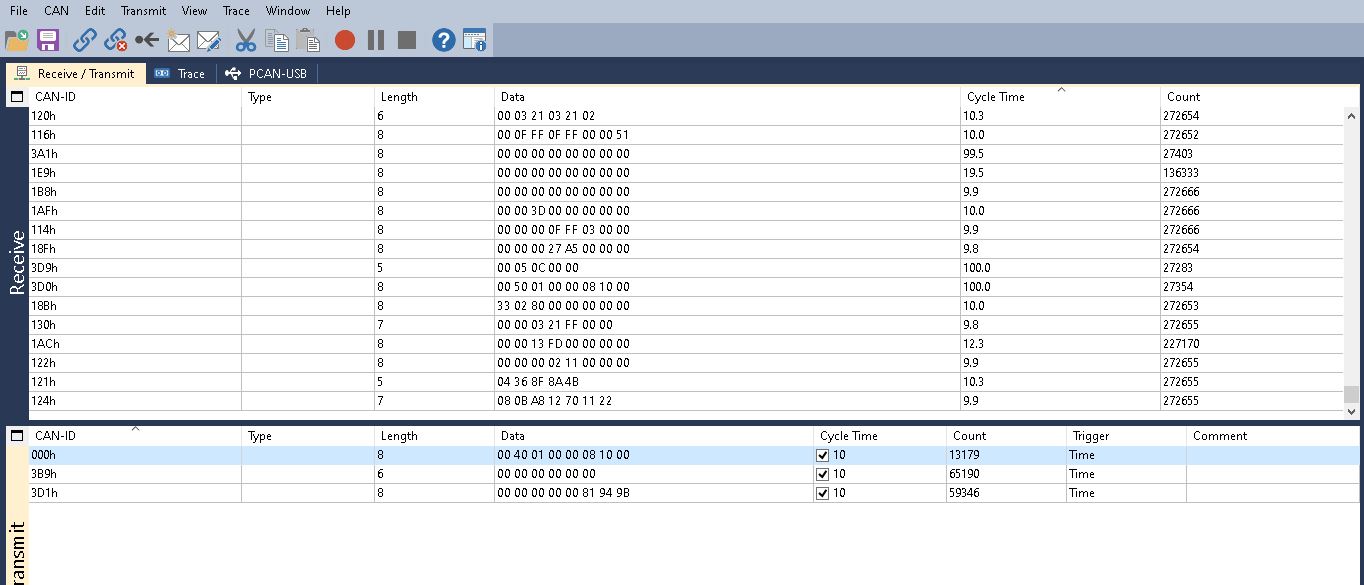 nsbogam/cve-2022-26269
Suzuki connect app is used to get the car information like Fuel, Ignition status, Current location, Seat buckle status etc. In Ignis, Zeta variant…
 mavproxyuser/httpfuzz-robomiller
Dumb Fuzzer used to find CVE-2010-1411
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 fath0218/cve-2016-2233
Step-by-step guide to exploiting a stack-based buffer overflow in HexChat (CVE-2016-2233) with a malicious IRC server, including a patch to fix the…
 zeusbox/cve-2021-21017
Proof-of-concept exploit for Adobe Reader type confusion leading to heap overflow, with detailed root-cause analysis and detection guidance.
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 ayoubfathi/leaky-paths
A collection of special paths linked to common sensitive APIs, devops internals, frameworks conf, known misconfigurations, juicy APIs ..etc. It could…
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
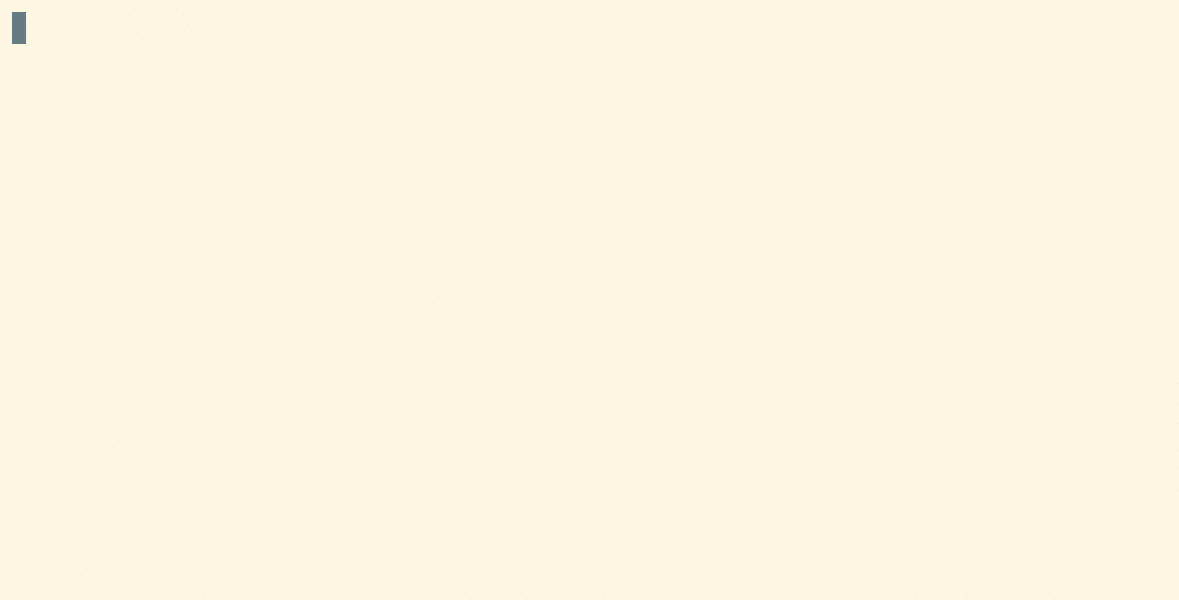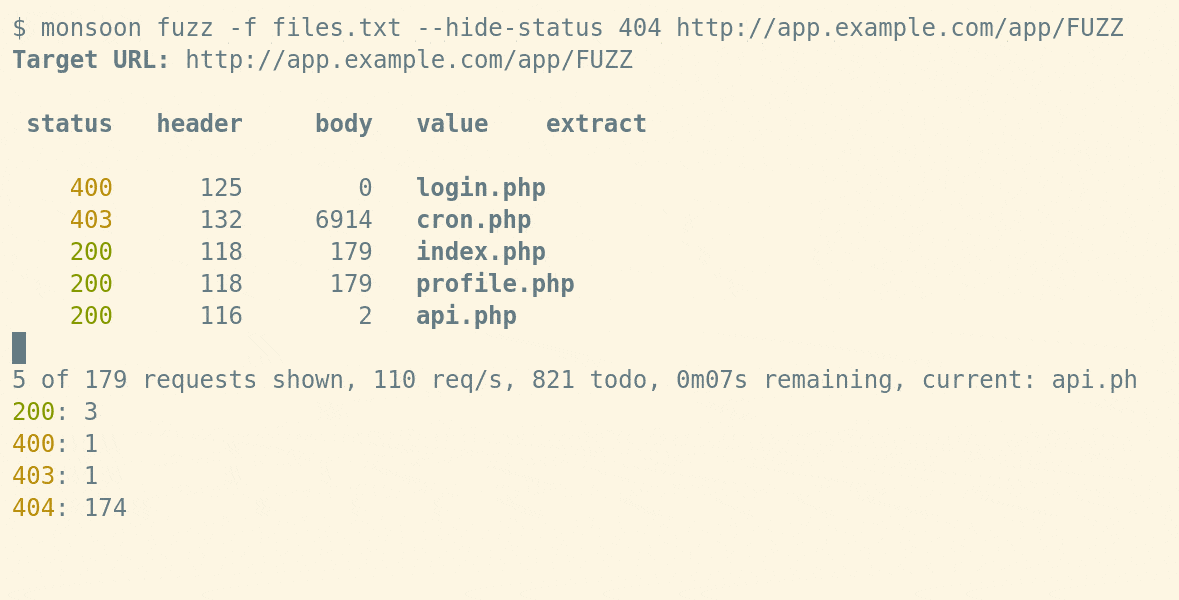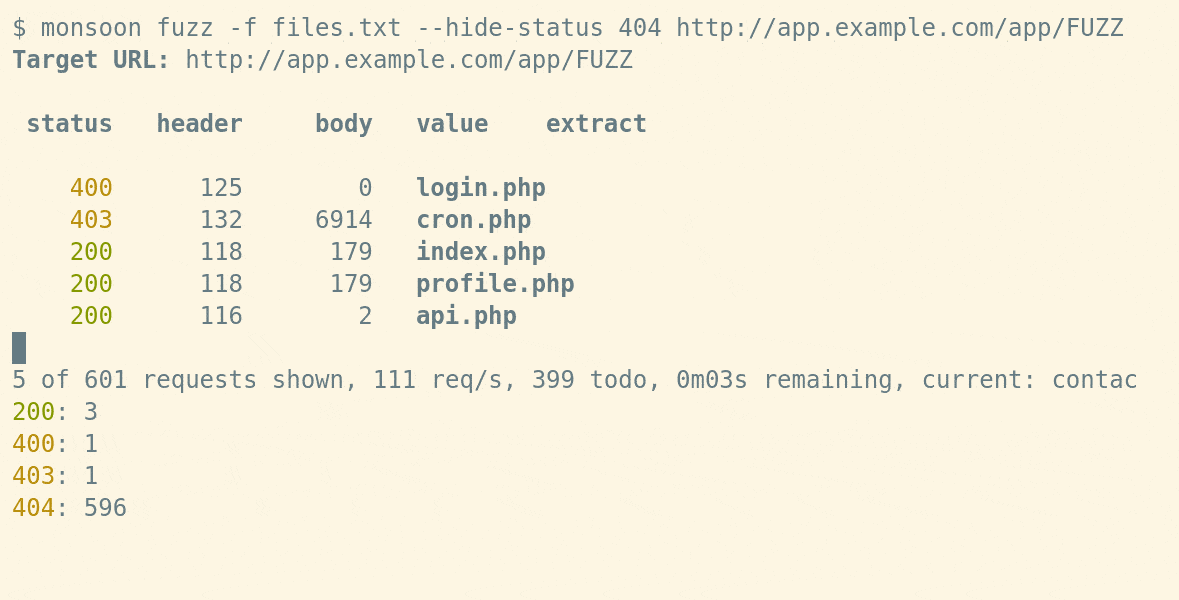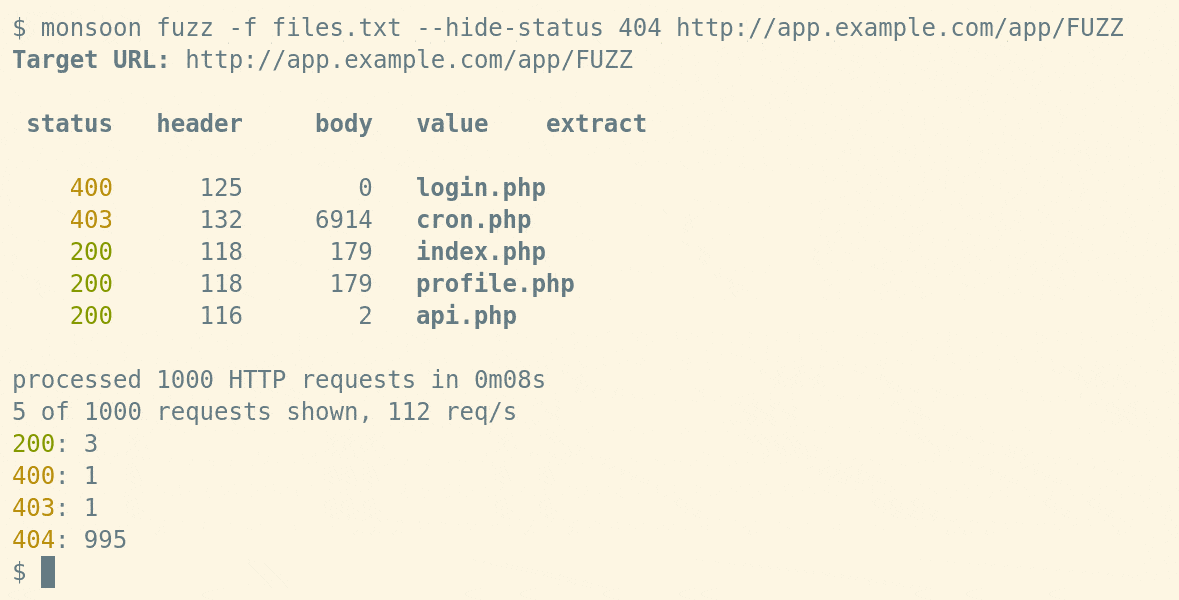 redteampentesting/monsoon
Fast HTTP enumerator
 ashemery/exploitation-course
Offensive Software Exploitation Course