

ESP32-DIV
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
bluetooth-securityeducationembedded-systems-security+8
4.1k
cifertech/esp32-divESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner

 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 alone/mutator
Generate mutations over a wordlist
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 libnet/nemesis
A command-line network packet crafting and injection utility
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
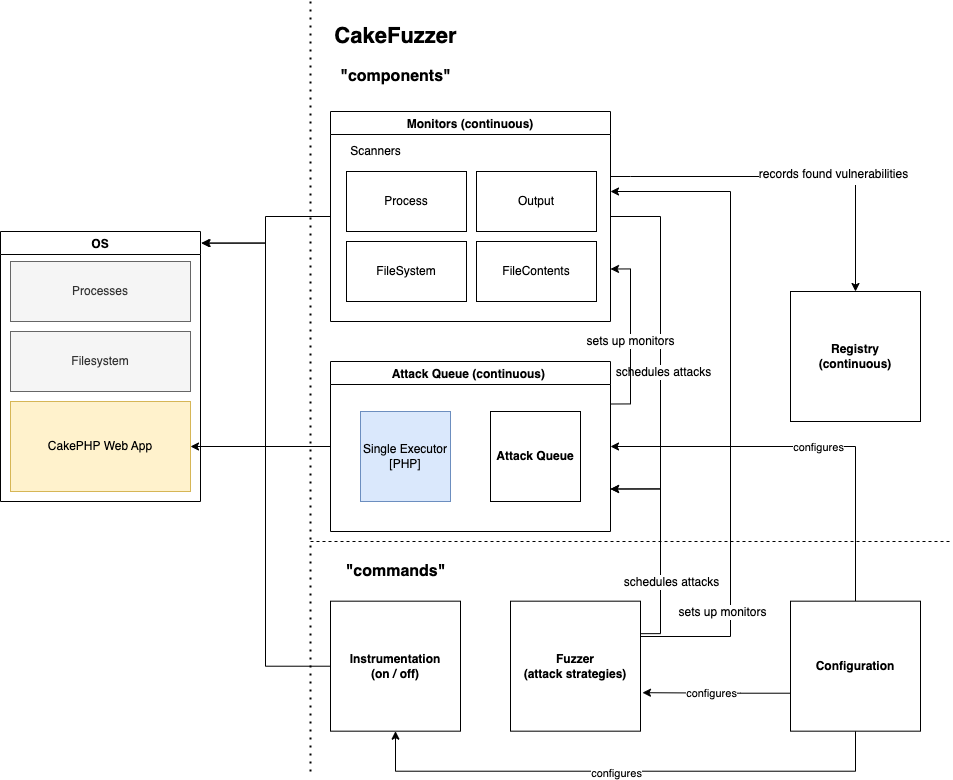 zigrin-security/cakefuzzer
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.