

firmware
 brucedevices/firmware
Predatory ESP32 Firmware
bluetooth-securityembedded-systems-securityexploitation+9
brucedevices/firmwarePredatory ESP32 Firmware

 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
 riverloopsec/killerbee
IEEE 802.15.4/ZigBee Security Research Toolkit
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 cclabsinc/rfcrack
A Software Defined Radio Attack Tool
 openl2d/moc3ingbird
MOC3ingbird Exploit for Live2D (CVE-2023-27566)
 9lyph/cve-2022-29593
Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…
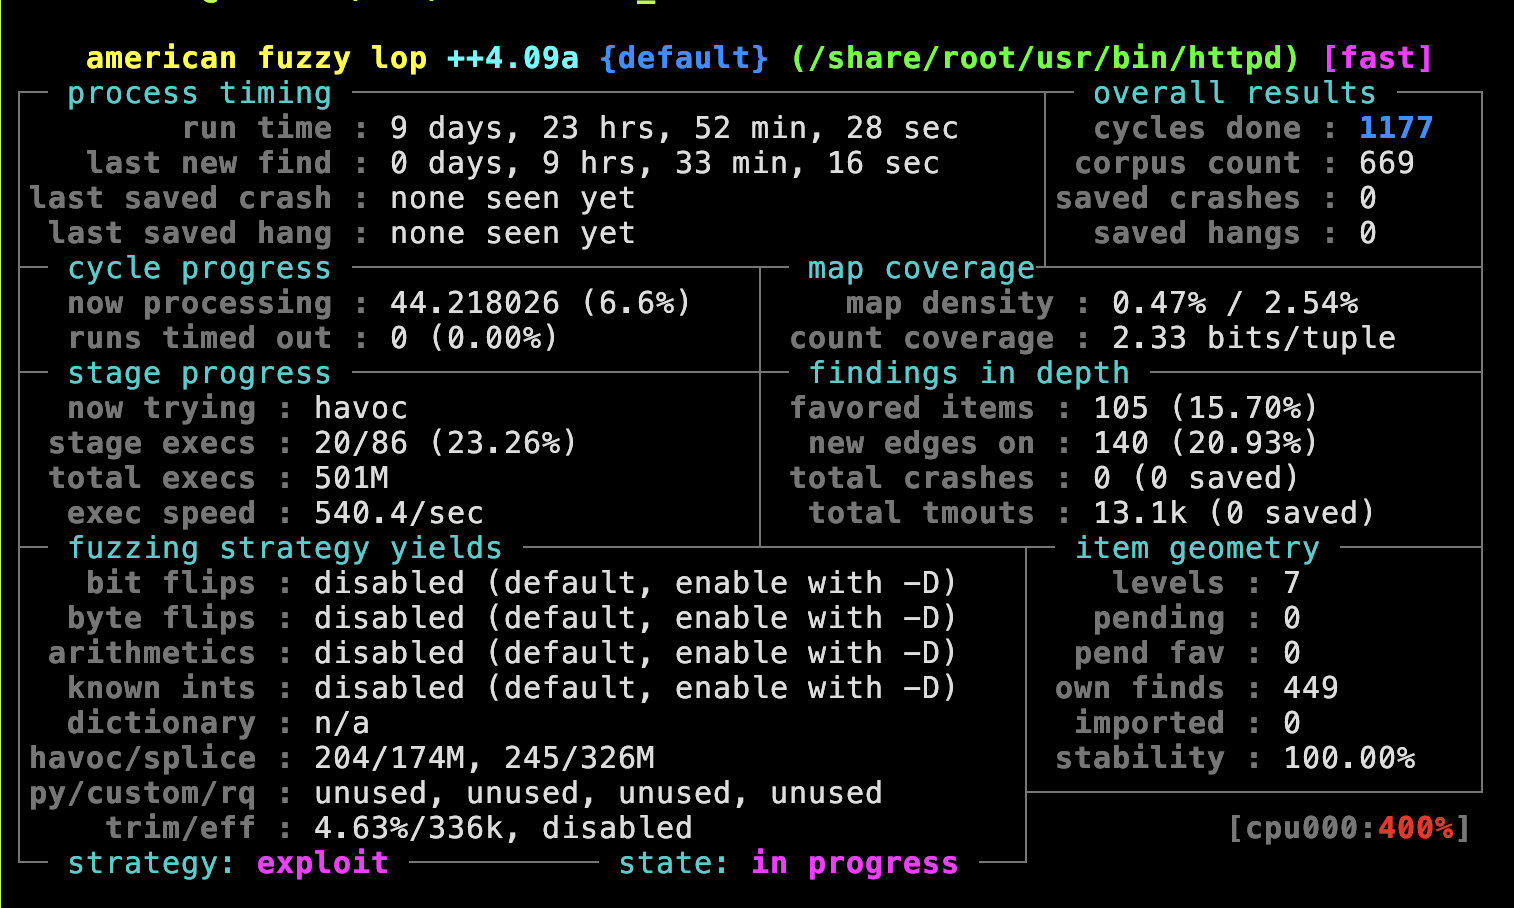 otsmr/blackbox-fuzzing
Fuzzing IoT Devices Using the Router TL-WR902AC as Example
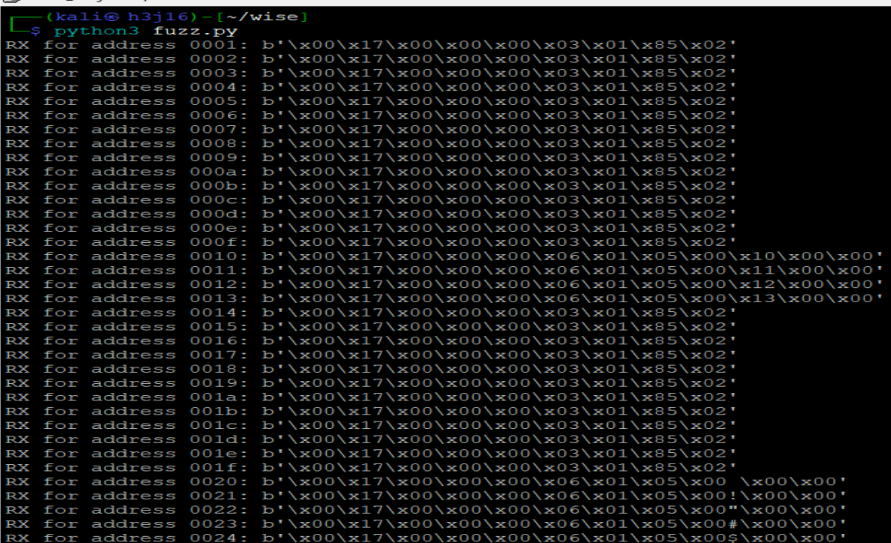 shipcod3/cve-2025-48466
Modbus Packet Injection on Advantech WISE 4060LAN / IoT Gateway for door control
 samsung/cotopaxi
Set of tools for security testing of Internet of Things devices using specific network IoT protocols
 expliot-framework/expliot
Read only mirror - No pull requests
 maximilianljungblut/hipcam-rtsp-format-validation-vulnerability
This POC exploits a format validation vulnerability in the RTSP service of the Hipcam RealServer/V1.0, inducing a crash for approximately 45 seconds…
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…
