

lighthouse
 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
binary-analysiscode-analysisdebuggers+6
gaasedelen/lighthouseA Coverage Explorer for Reverse Engineers
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 greatscottgadgets/facedancer
Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET
 google/clusterfuzz
Scalable fuzzing infrastructure with coverage-guided engines (libFuzzer, AFL, Honggfuzz), automated crash deduplication, bug filing, and regression…
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 panda-re/lava
LAVA: Large-scale Automated Vulnerability Addition
 google/oss-fuzz
OSS-Fuzz - continuous fuzzing for open source software.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 kevinbackhouse/djvulibre-poc-cve-2025-53367
Proof-of-concept exploit for CVE-2025-53367, a vulnerability in the DjVuLibre library. Demonstrates exploitation of a memory corruption bug in DjVu…
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
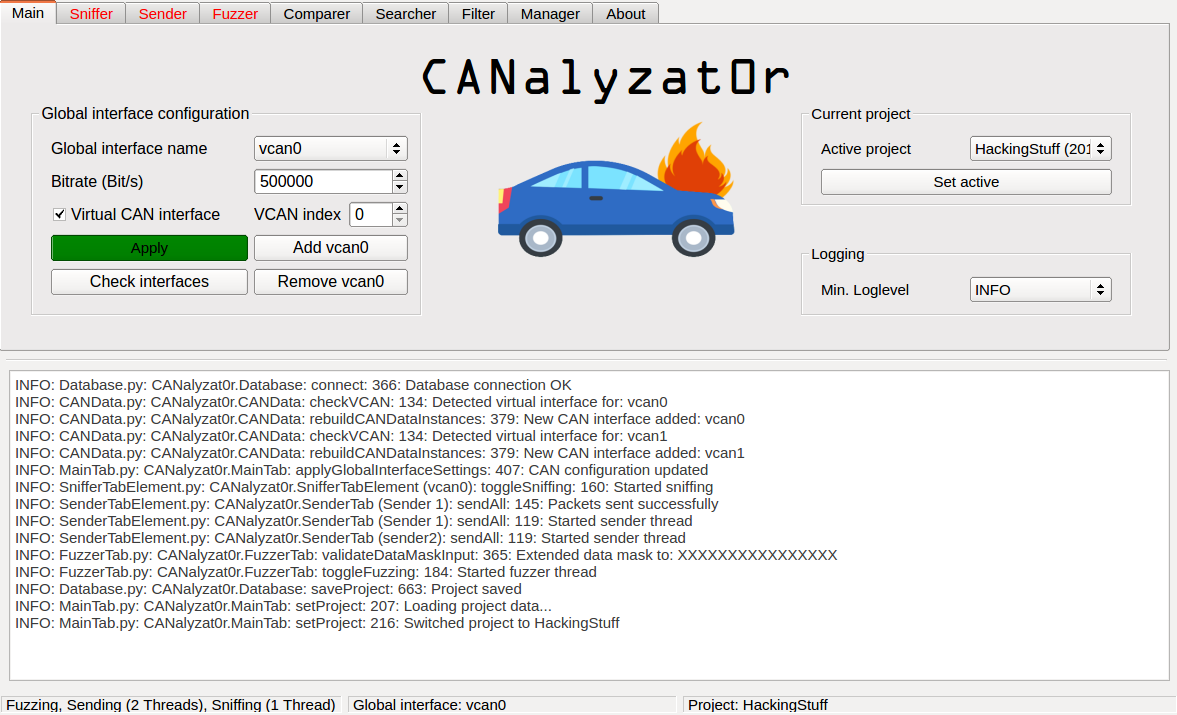 schutzwerk/canalyzat0r
Security analysis toolkit for proprietary car protocols
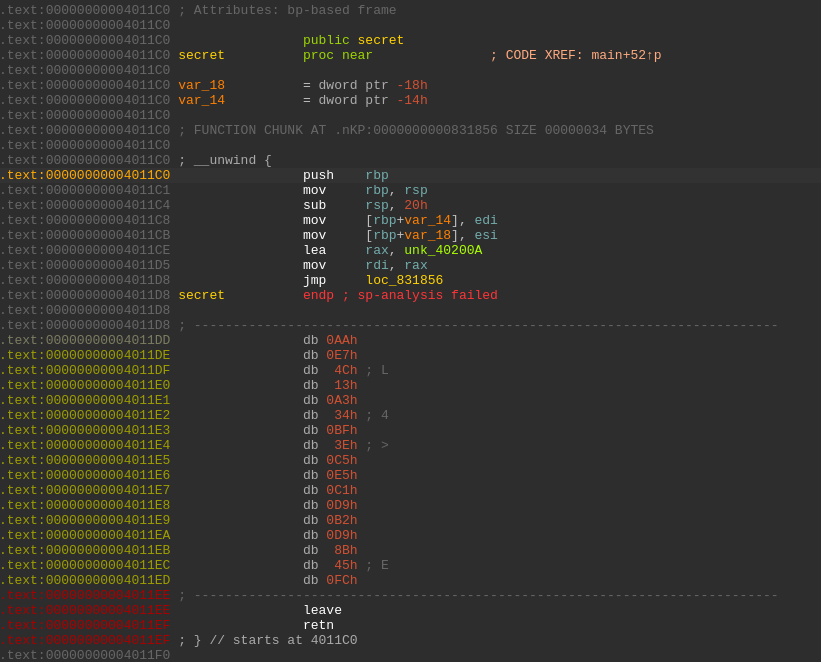 jonathansalwan/vmprotect-devirtualization
Playing with the VMProtect software protection. Automatic deobfuscation of pure functions using symbolic execution and LLVM.
 alex-acero-security/cve-2025-20260-poc
Proof-of-concept exploit for CVE-2025-20260, a buffer overflow in ClamAV's PDF scanning. Includes a Python script to generate a malicious PDF and…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 cclabsinc/rfcrack
A Software Defined Radio Attack Tool