
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…

Implement your own USB device in Python, supported by a hardware peripheral such as Cynthion or GreatFET

CANToolz - framework for black-box CAN network analysis

Static binary vulnerability scanner using abstract interpretation on Ghidra Pcode. Detects CWE classes like buffer overflows, use-after-free, and…

An impish, cross-platform binary parsing crate, written in Rust


Disclosure of Accfly camera vulnerabilities: CVE-2020-25782, CVE-2020-25783, CVE-2020-25784, CVE-2020-25785.


PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.

Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…

This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…

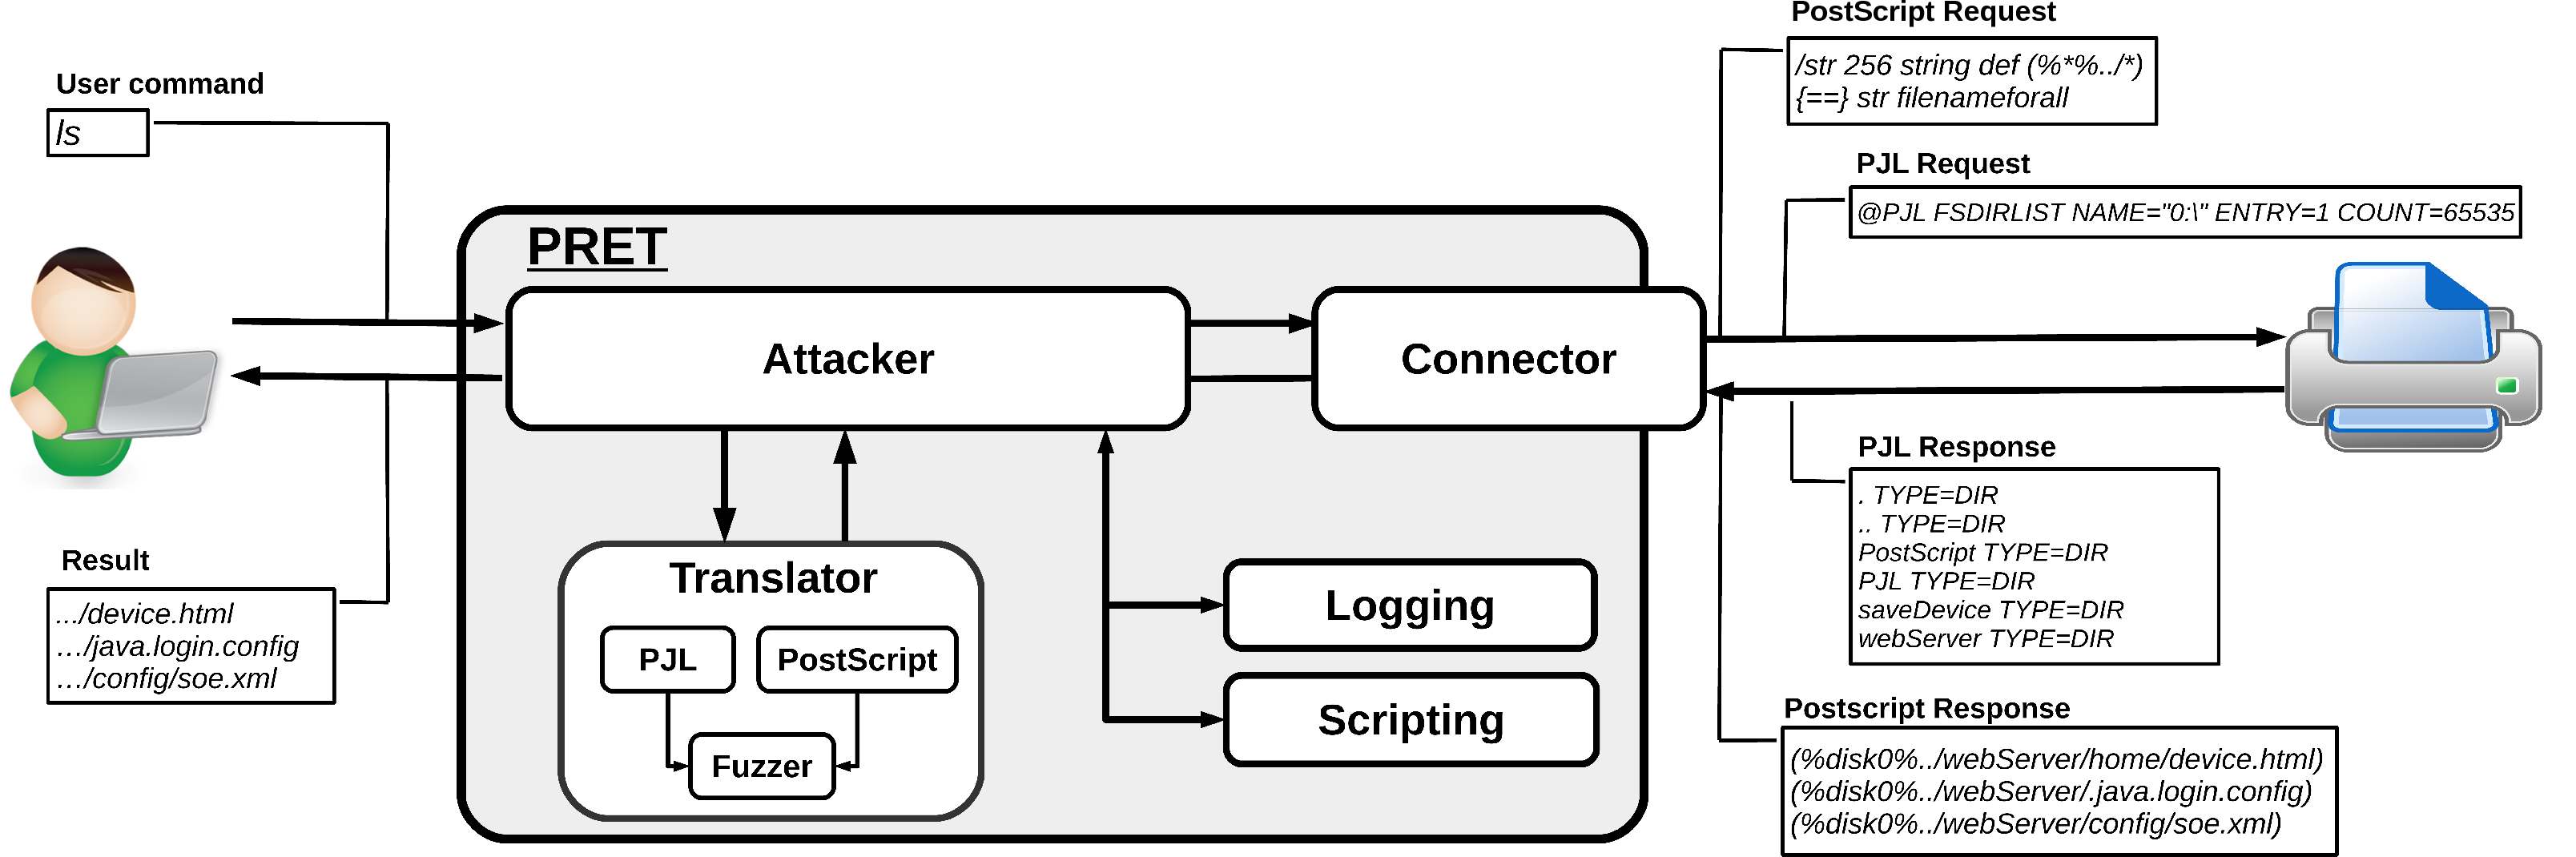
Printer Exploitation Toolkit - The tool that made dumpster diving obsolete.

Standalone proof of concept for CVE-2026-86547, a NULL pointer dereference in mrubyc op_enter() through 4.0.0.

A tool for logging data/testing devices with a Wiegand Interface. Can be used to create a portable RFID reader or installed directly into an existing…

CANToolz - Black-box CAN network analysis framework

IEEE 802.15.4/ZigBee Security Research Toolkit

ARM64 ELF Virtual Machine Protection System