
subparse
 jstrosch/subparse
Modular malware analysis artifact collection and correlation framework
dynamic-analysis-sandboxingforensicsinformation-gathering+3
56
jstrosch/subparseModular malware analysis artifact collection and correlation framework
 volatilityfoundation/volatility3
Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
 volatilityfoundation/volatility
An advanced memory forensics framework
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 viper-framework/viper
Binary analysis and management framework
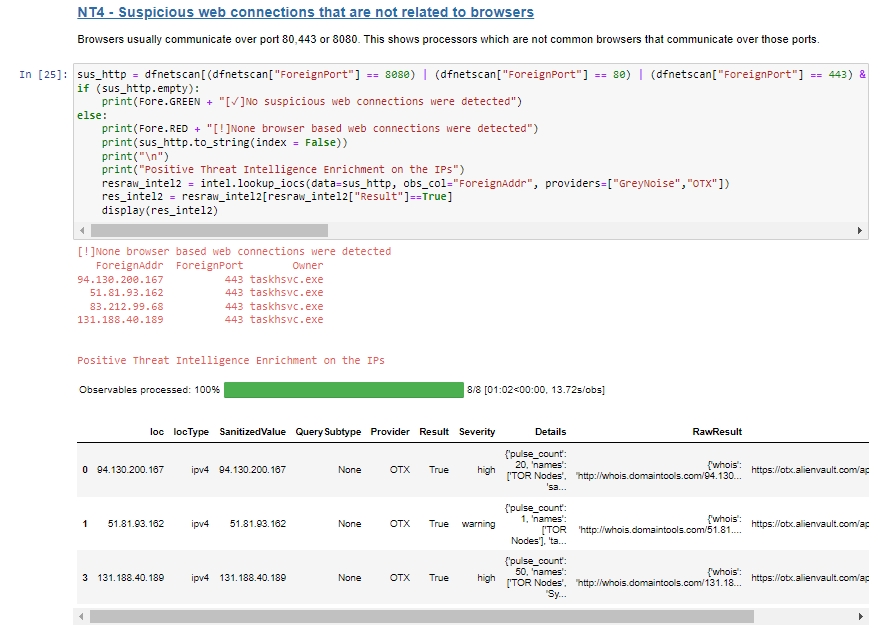 blueteam0ps/memoptix
A Jupyter notebook to assist with the analysis of the output generated from Volatility memory extraction framework.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
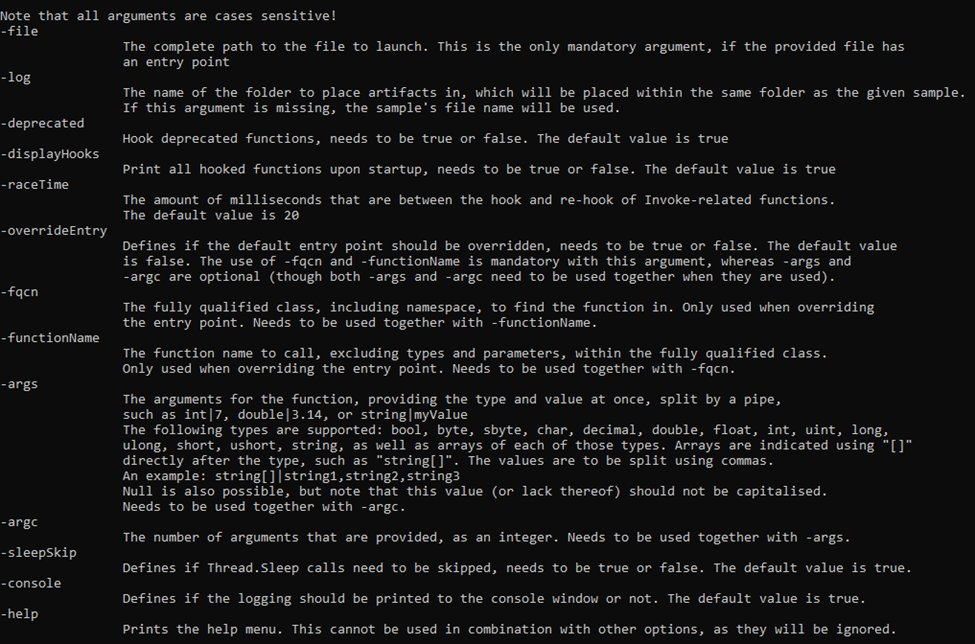 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 fox-it/dissect
Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources