Digital-Forensics-Guide

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

Digital Forensics Guide. Learn all about Digital Forensics, Computer Forensics, Mobile device Forensics, Network Forensics, and Database Forensics.

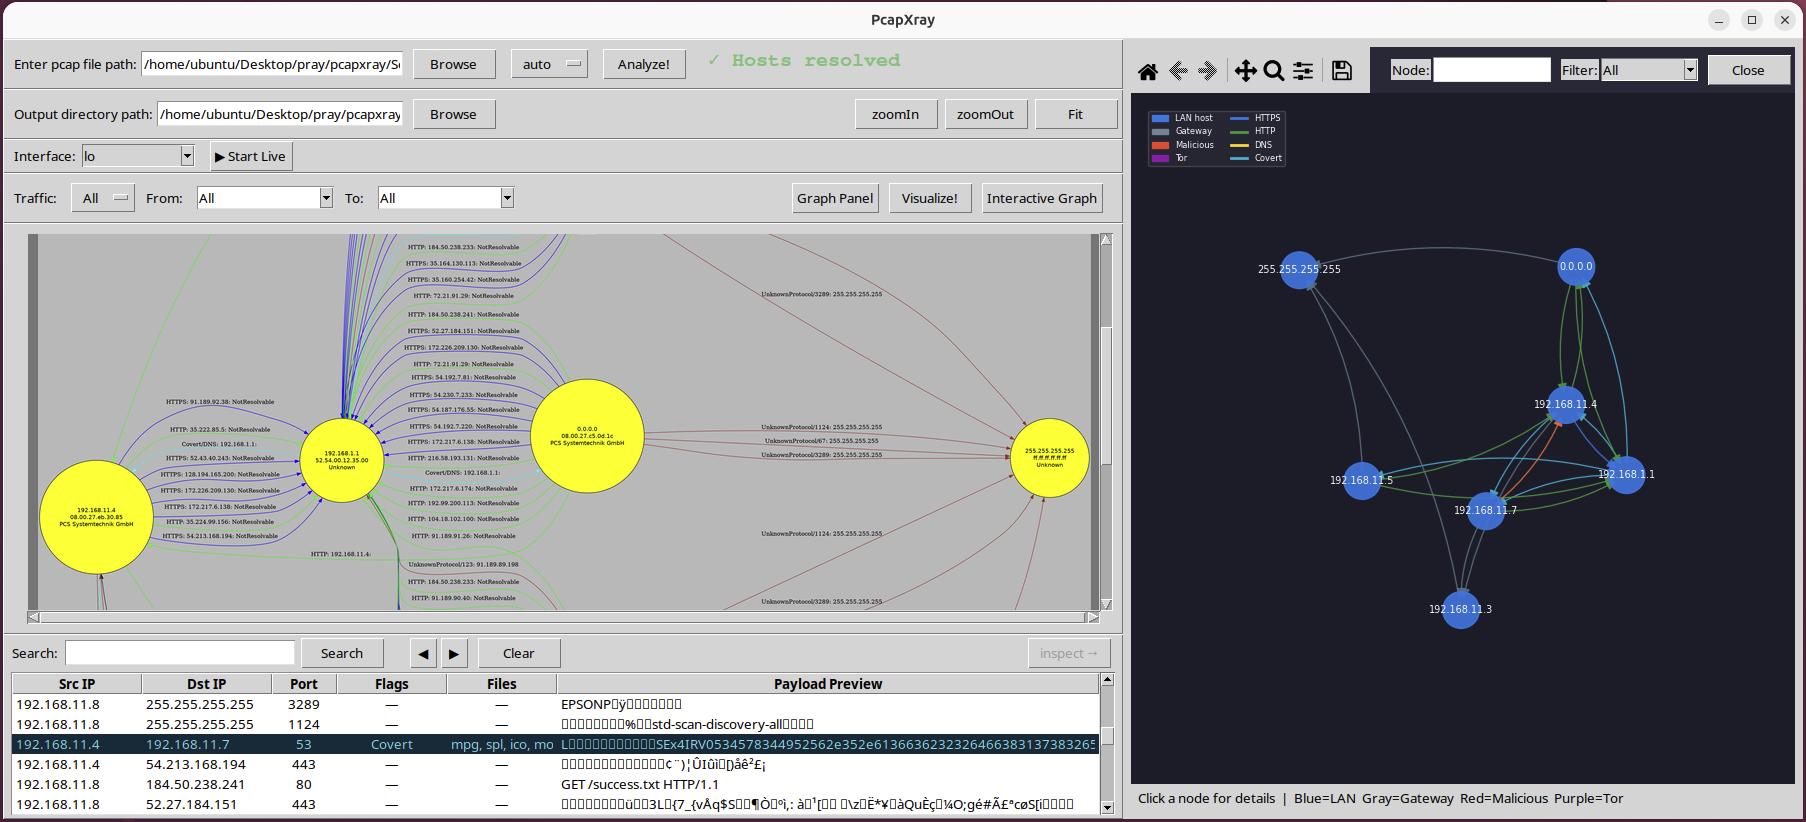
❄️ PcapXray - A Network Forensics Tool - To visualize a Packet Capture offline as a Network Diagram including device identification, highlight…

Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

Reverse-engineered analysis of Microsoft's Global Device Identifier (GDID) revealing its generation as a server-assigned MSA Device PUID, storage in…

Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)


ATAboy is a user-friendly bridge that allows legacy CHS only style IDE (PATA) hard drives to be connected to a modern computer as a standard USB Mass…

Bash script to extract data from a "chekcra1ned" iOS device

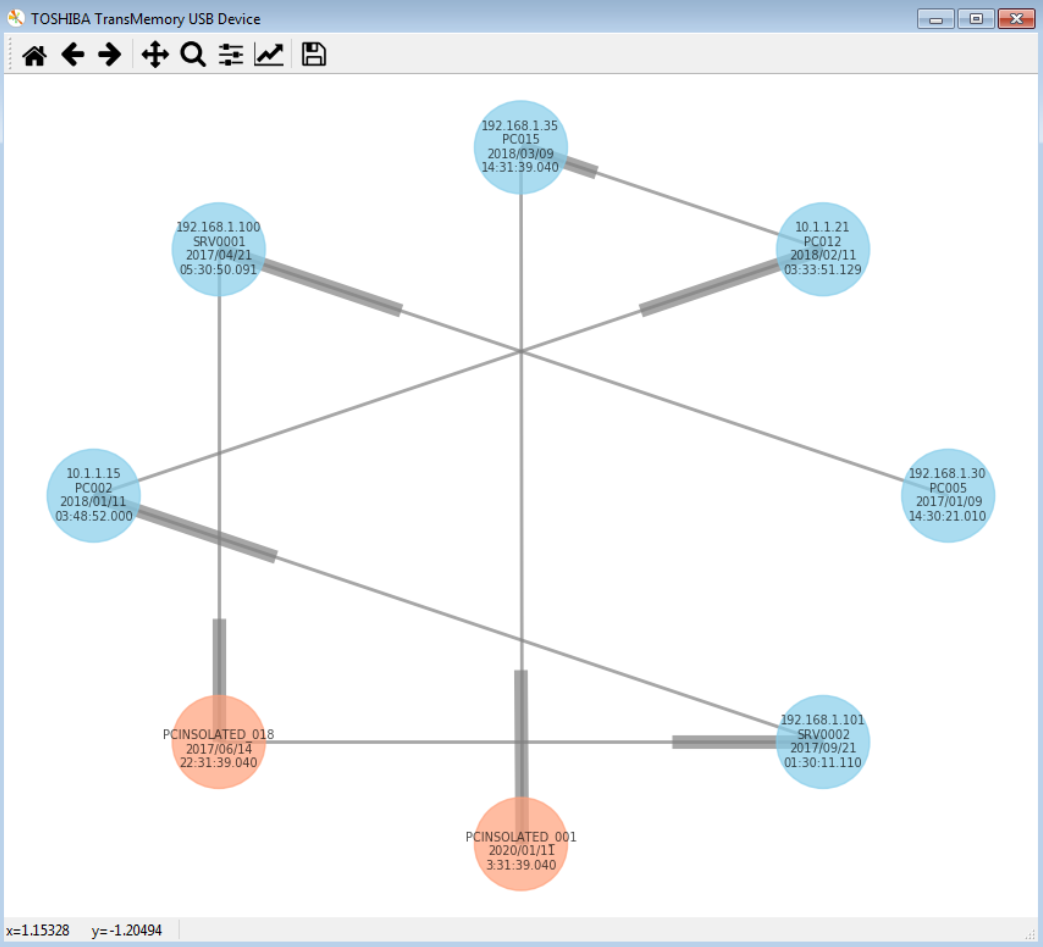
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…

Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.

"A single malicious packet can own your device." — Android Security Team, Nov 2025

Comprehensive Android security vulnerability demonstrations featuring CVE-2017-13156 (Janus), broadcast receiver exploitation, external storage…

Simple Process Dumper using DMA over a PCIe FPGA device

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…

A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.

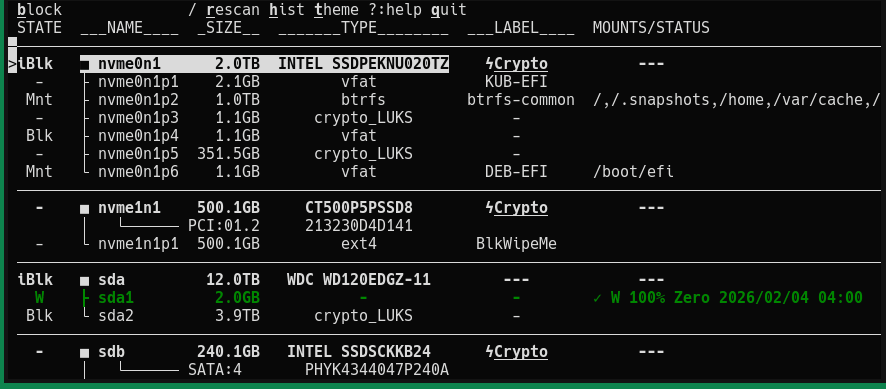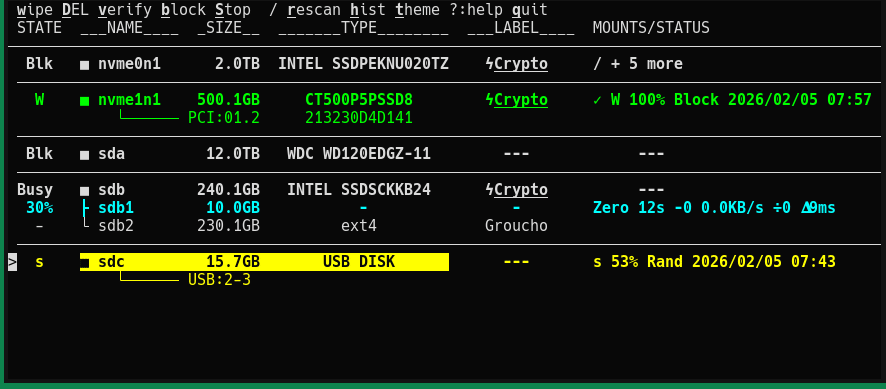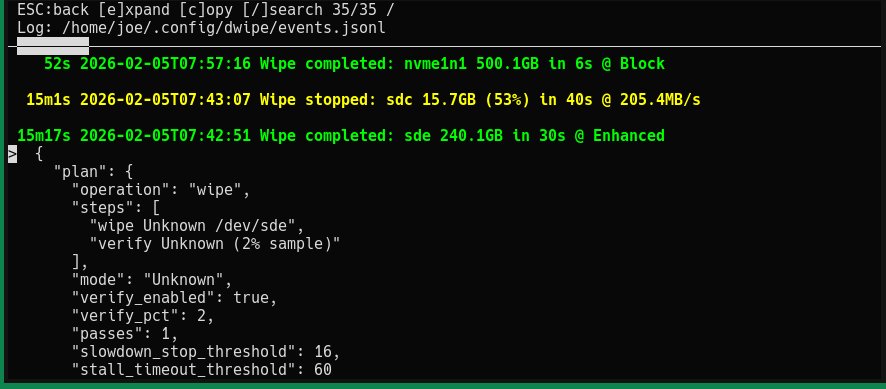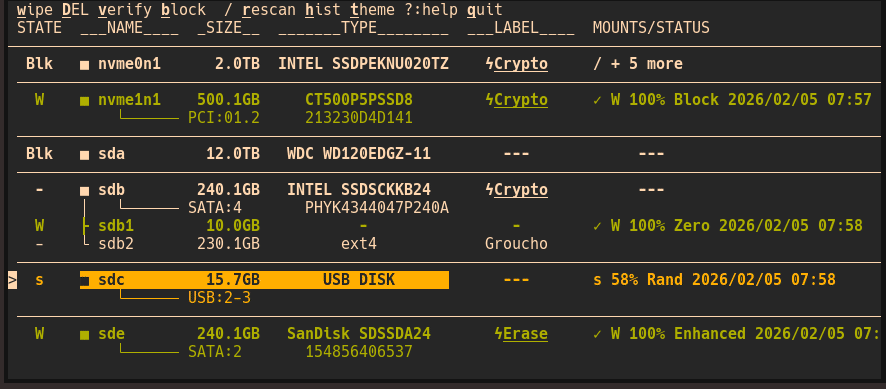
Tool to securely and efficiently wipe devices and partiitions for Linux

Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…

Tool for reconstructing SPI flash images via logic analyzer captures