

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.5k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 den4uk/andriller
📱 Andriller - is software utility with a collection of forensic tools for smartphones. It performs read-only, forensically sound, non-destructive…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
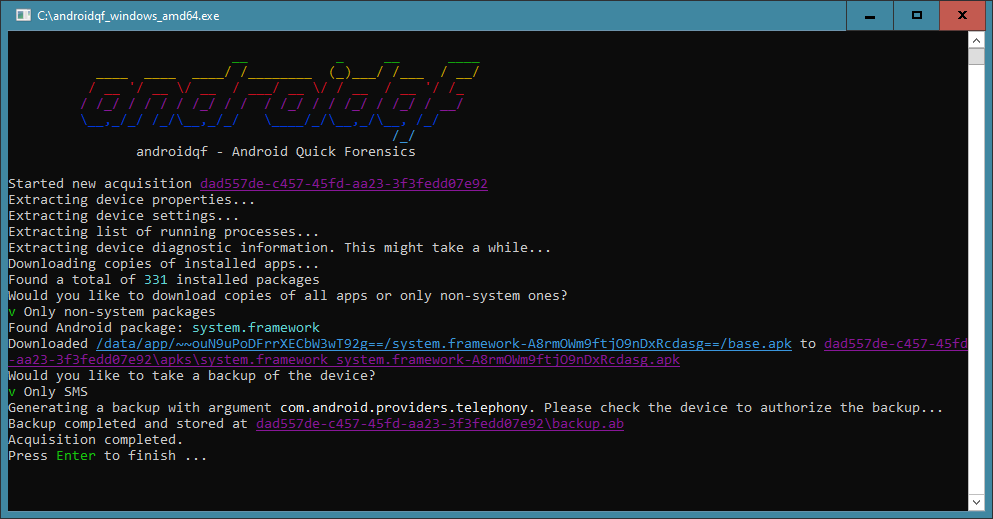 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 jacktekno/chrome-forensic_cve-2024-0044
A robust digital forensics tool for extracting and analyzing Google Chrome artifacts from Android devices
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 b16f00t/whapa
Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
 nelenkov/android-backup-extractor
Extract and repack Android ADB backups (ICS+). Supports encrypted archives, tar conversion, and standard I/O for forensic analysis or data recovery.
 honeynet/apkinspector
APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…

 packetlss/android-locdump
android location service cache dumper