
columbo
 visma-prodsec/columbo
ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
anomaly-detectionbinary-analysisdigital-forensics+3
61
visma-prodsec/columboML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…
 mvt-project/androidqf
androidqf (Android Quick Forensics) helps quickly gathering forensic evidence from Android devices, in order to identify potential traces of…
 sucuri-labs/cve-2025-57819-ioc-check
This is repository contains a script to check for current IOCs listed in the freepbx forum topic of the CVE-2025-57819
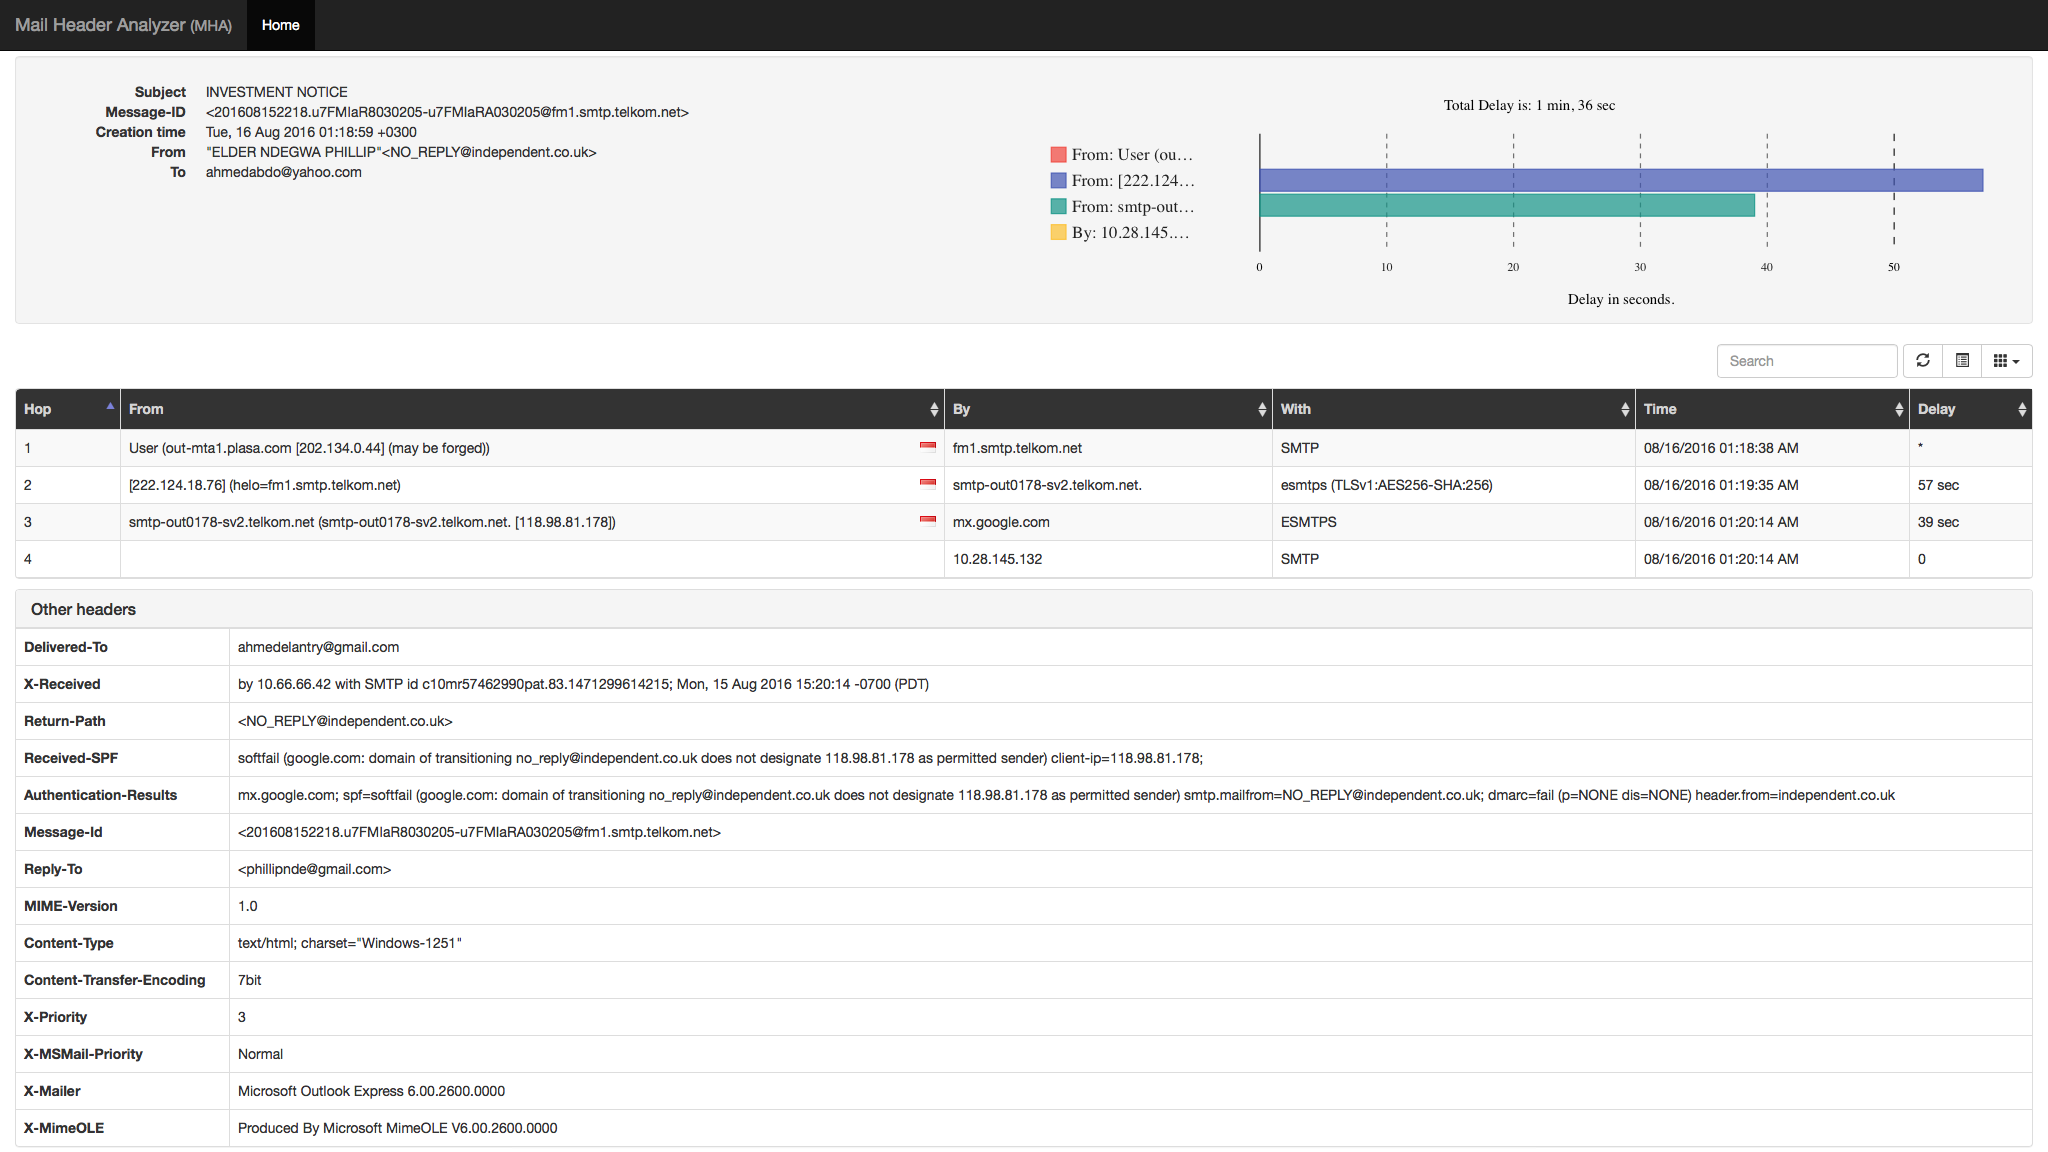 cyberdefenders/email-header-analyzer
E-Mail Header Analyzer
 gr33nm0nk2802/mailmeta
An forensics tool to help aid in the investigation of spoofed emails based off the email headers.
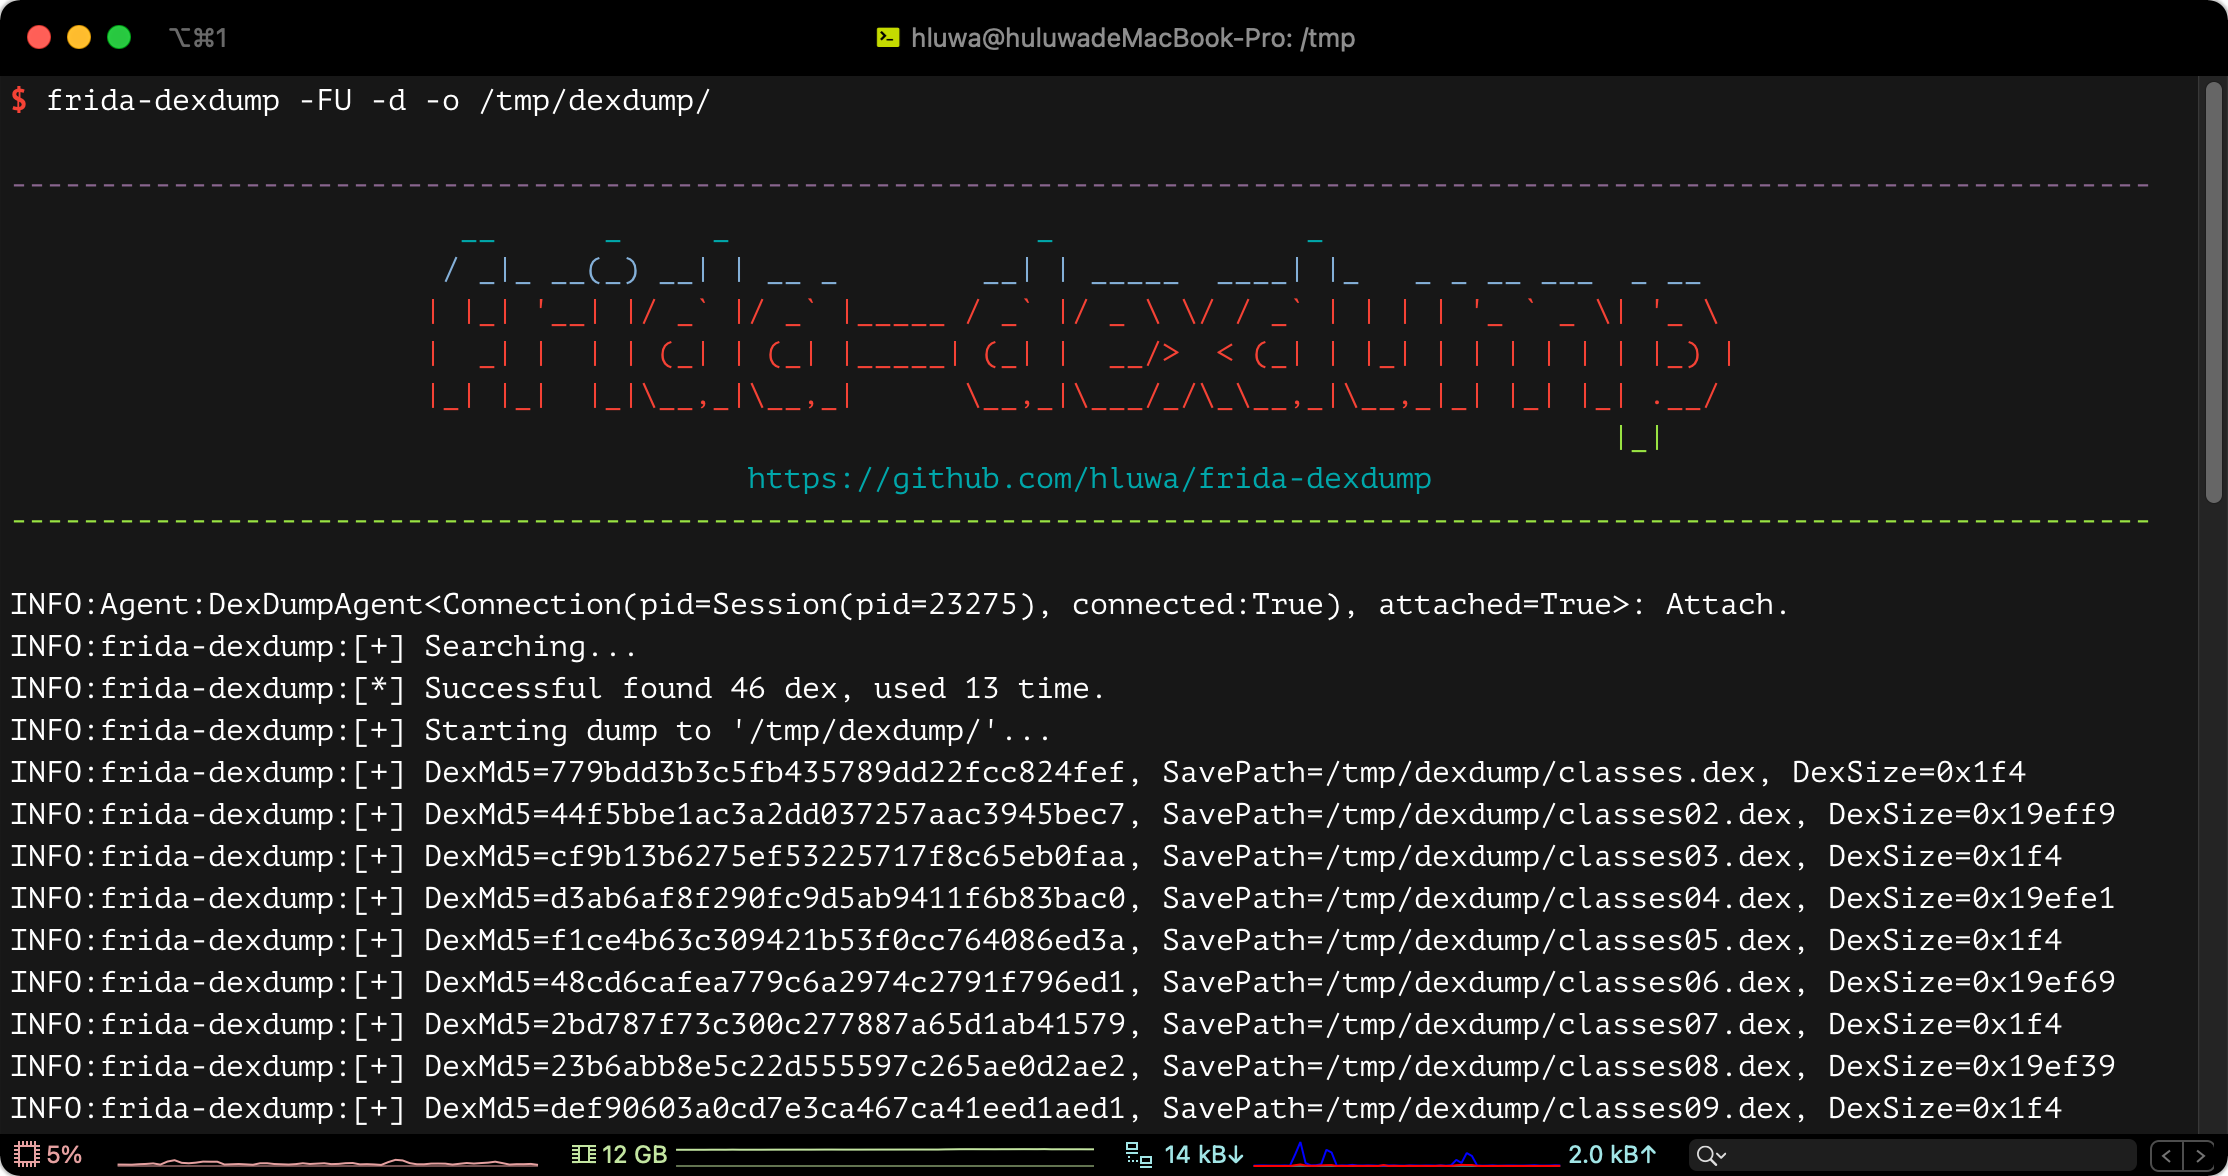 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 elevenpaths/foca
Tool to find metadata and hidden information in the documents.
 gregwar/fatcat
FAT filesystems explore, extract, repair, and forensic tool
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
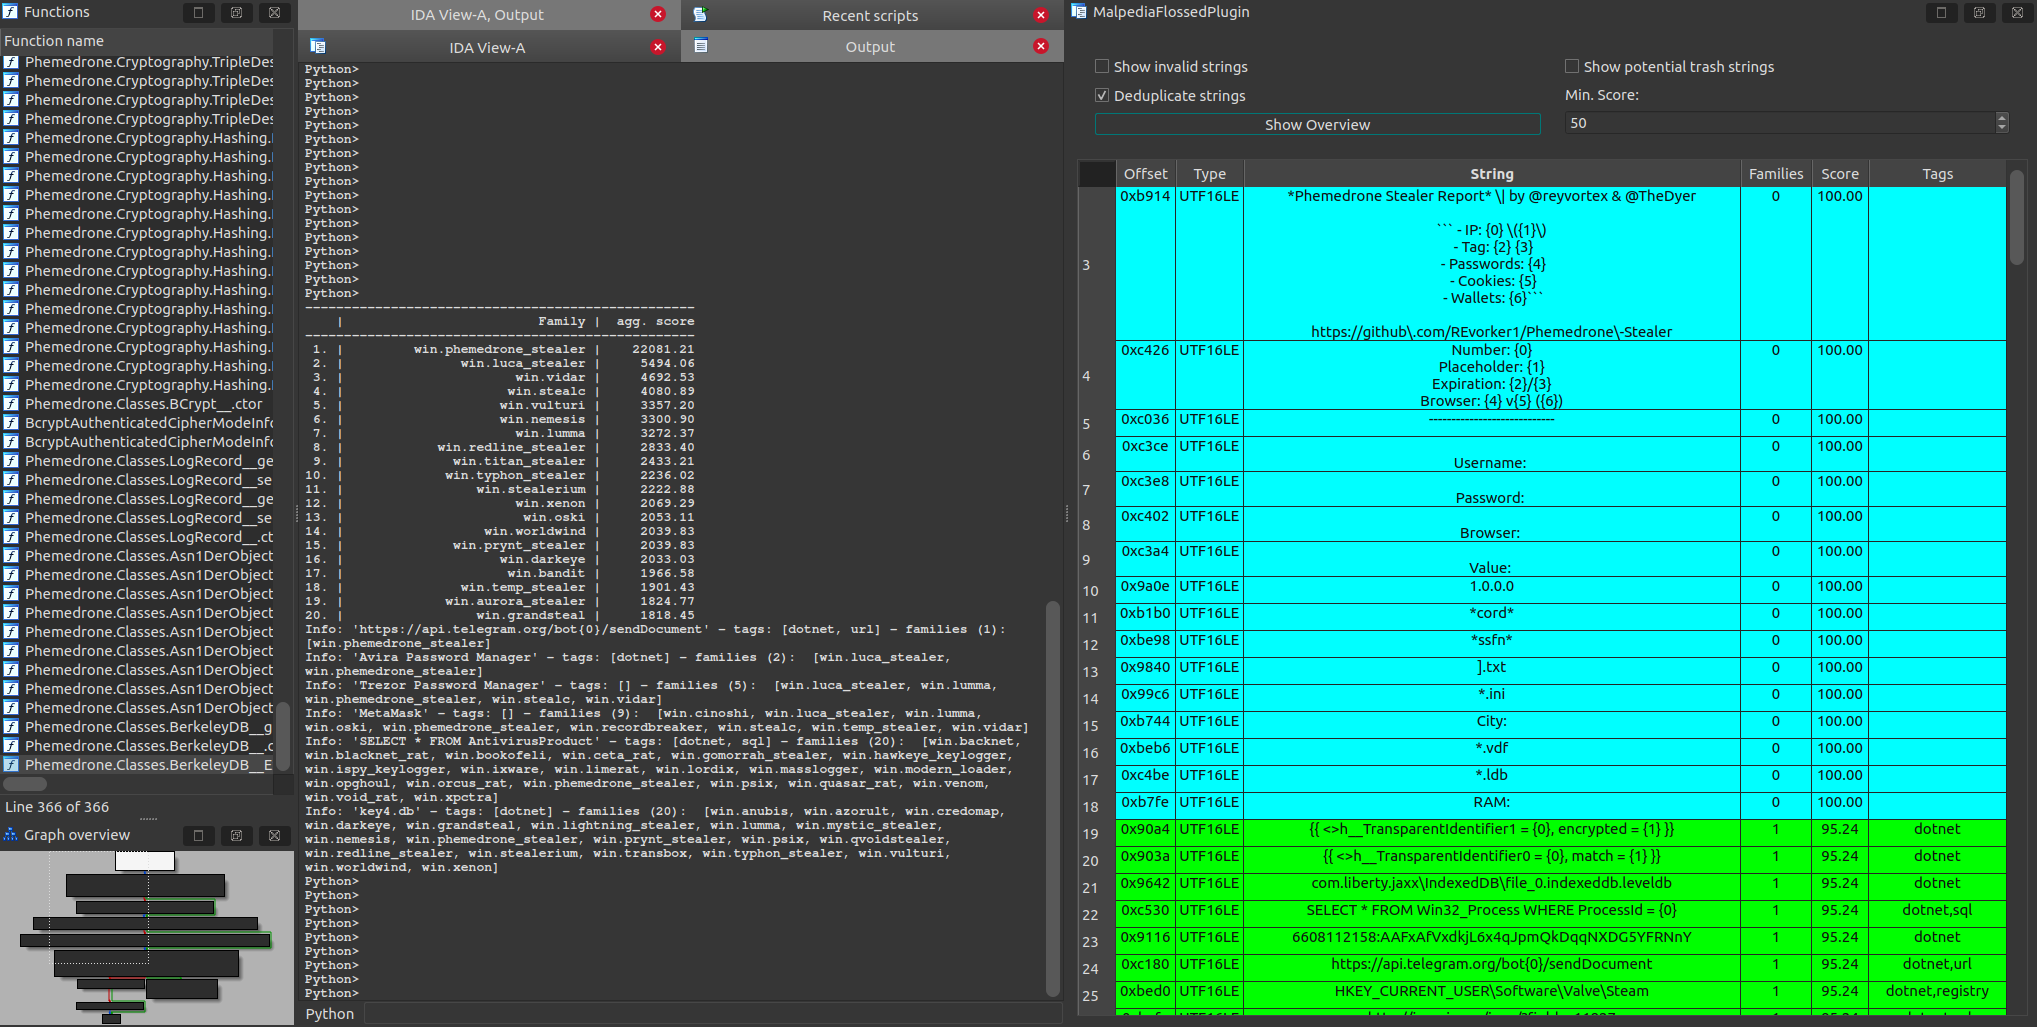 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 utkusen/wholeaked
a file-sharing tool that allows you to find the responsible person in case of a leakage
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
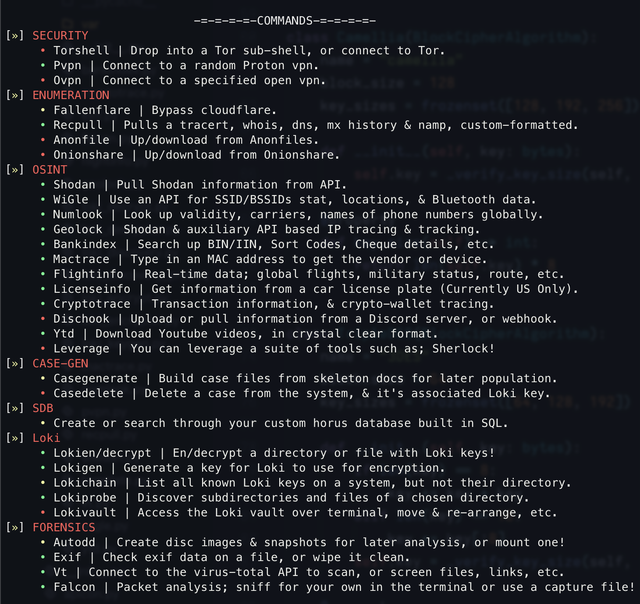 6abd/horus
An OSINT / digital forensics tool built in Python