
drakvuf-sandbox
 cert-polska/drakvuf-sandbox
Automated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
dynamic-analysis-sandboxingforensicsmalware-analysis+2
1.4k
cert-polska/drakvuf-sandboxAutomated hypervisor-level malware analysis sandbox with agentless guest introspection, web-based result exploration, and guided installer for…
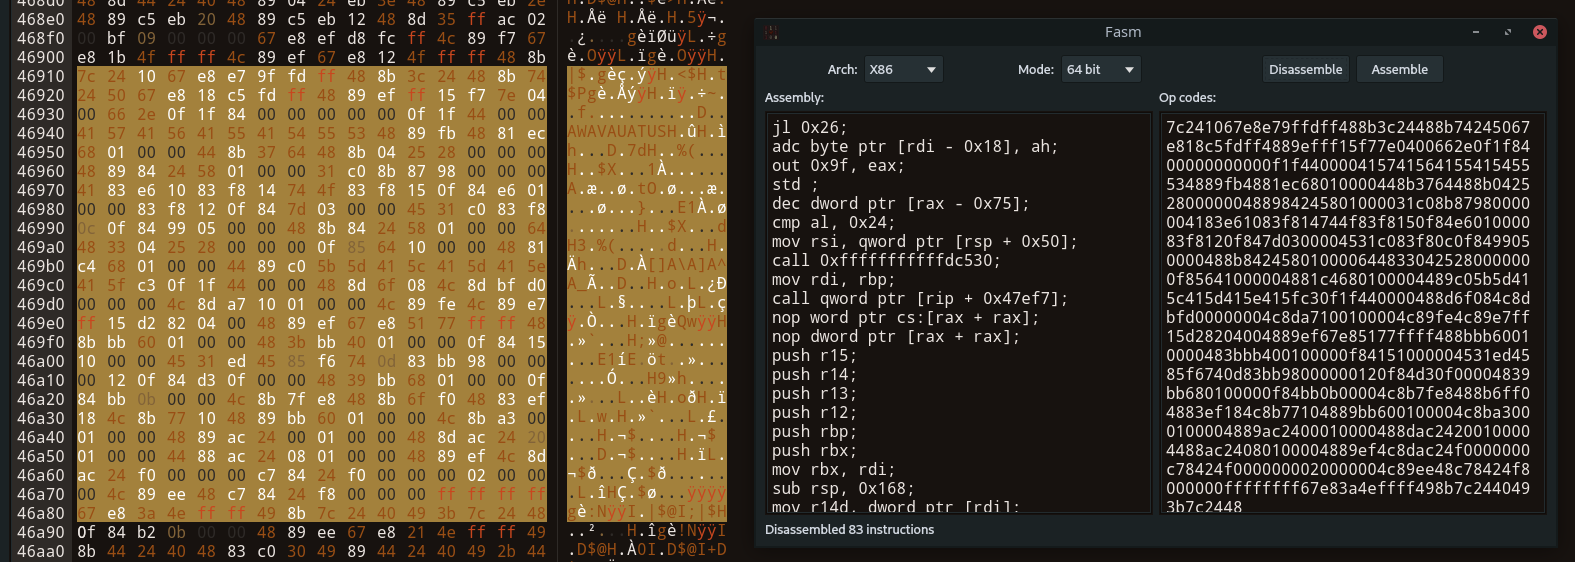 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
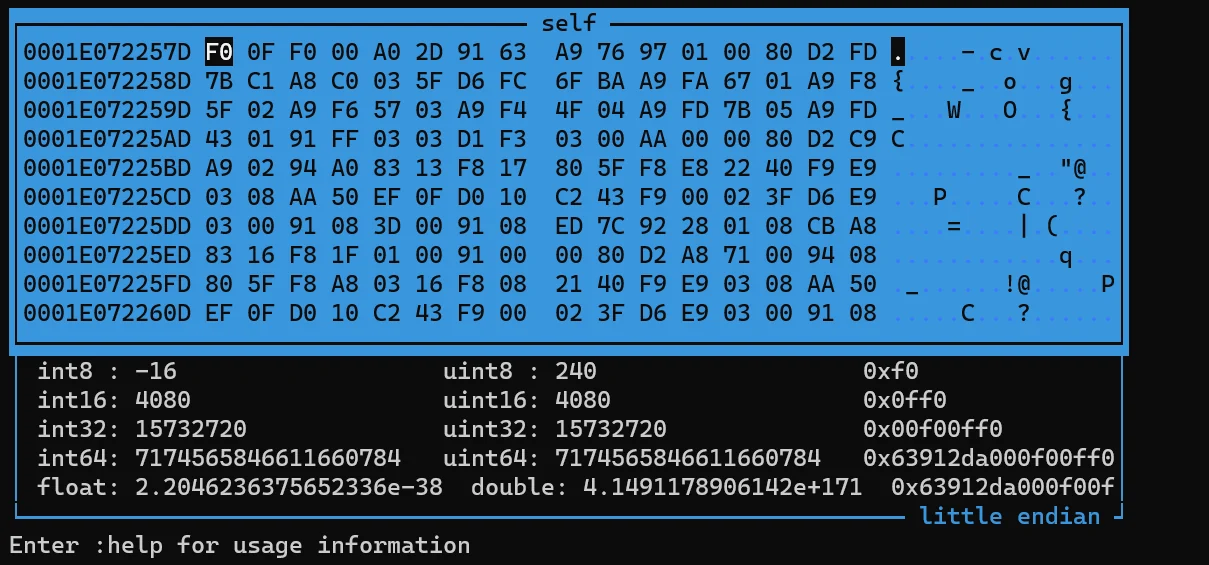 gmh5225/frida-medit
Cross-platform CUI process memory scanner built on Frida for finding, filtering, patching, and dumping live process memory during reverse engineering…
 malienist/lupo
WinDbg plugin for automated malware dynamic analysis and IOC extraction. Executes within the debugger to collect predefined indicators and writes…
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 fuzzysecurity/powershell-suite
My musings with PowerShell
 kevthehermit/ratdecoders
Python Decoders for Common Remote Access Trojans
 rurik/noriben
Python-based malware analysis sandbox that integrates with Sysinternals Procmon to automatically collect, analyze, and report runtime indicators with…
 mandiant/flare-learning-hub
Free educational content on reverse engineering and malware analysis from the FLARE team
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
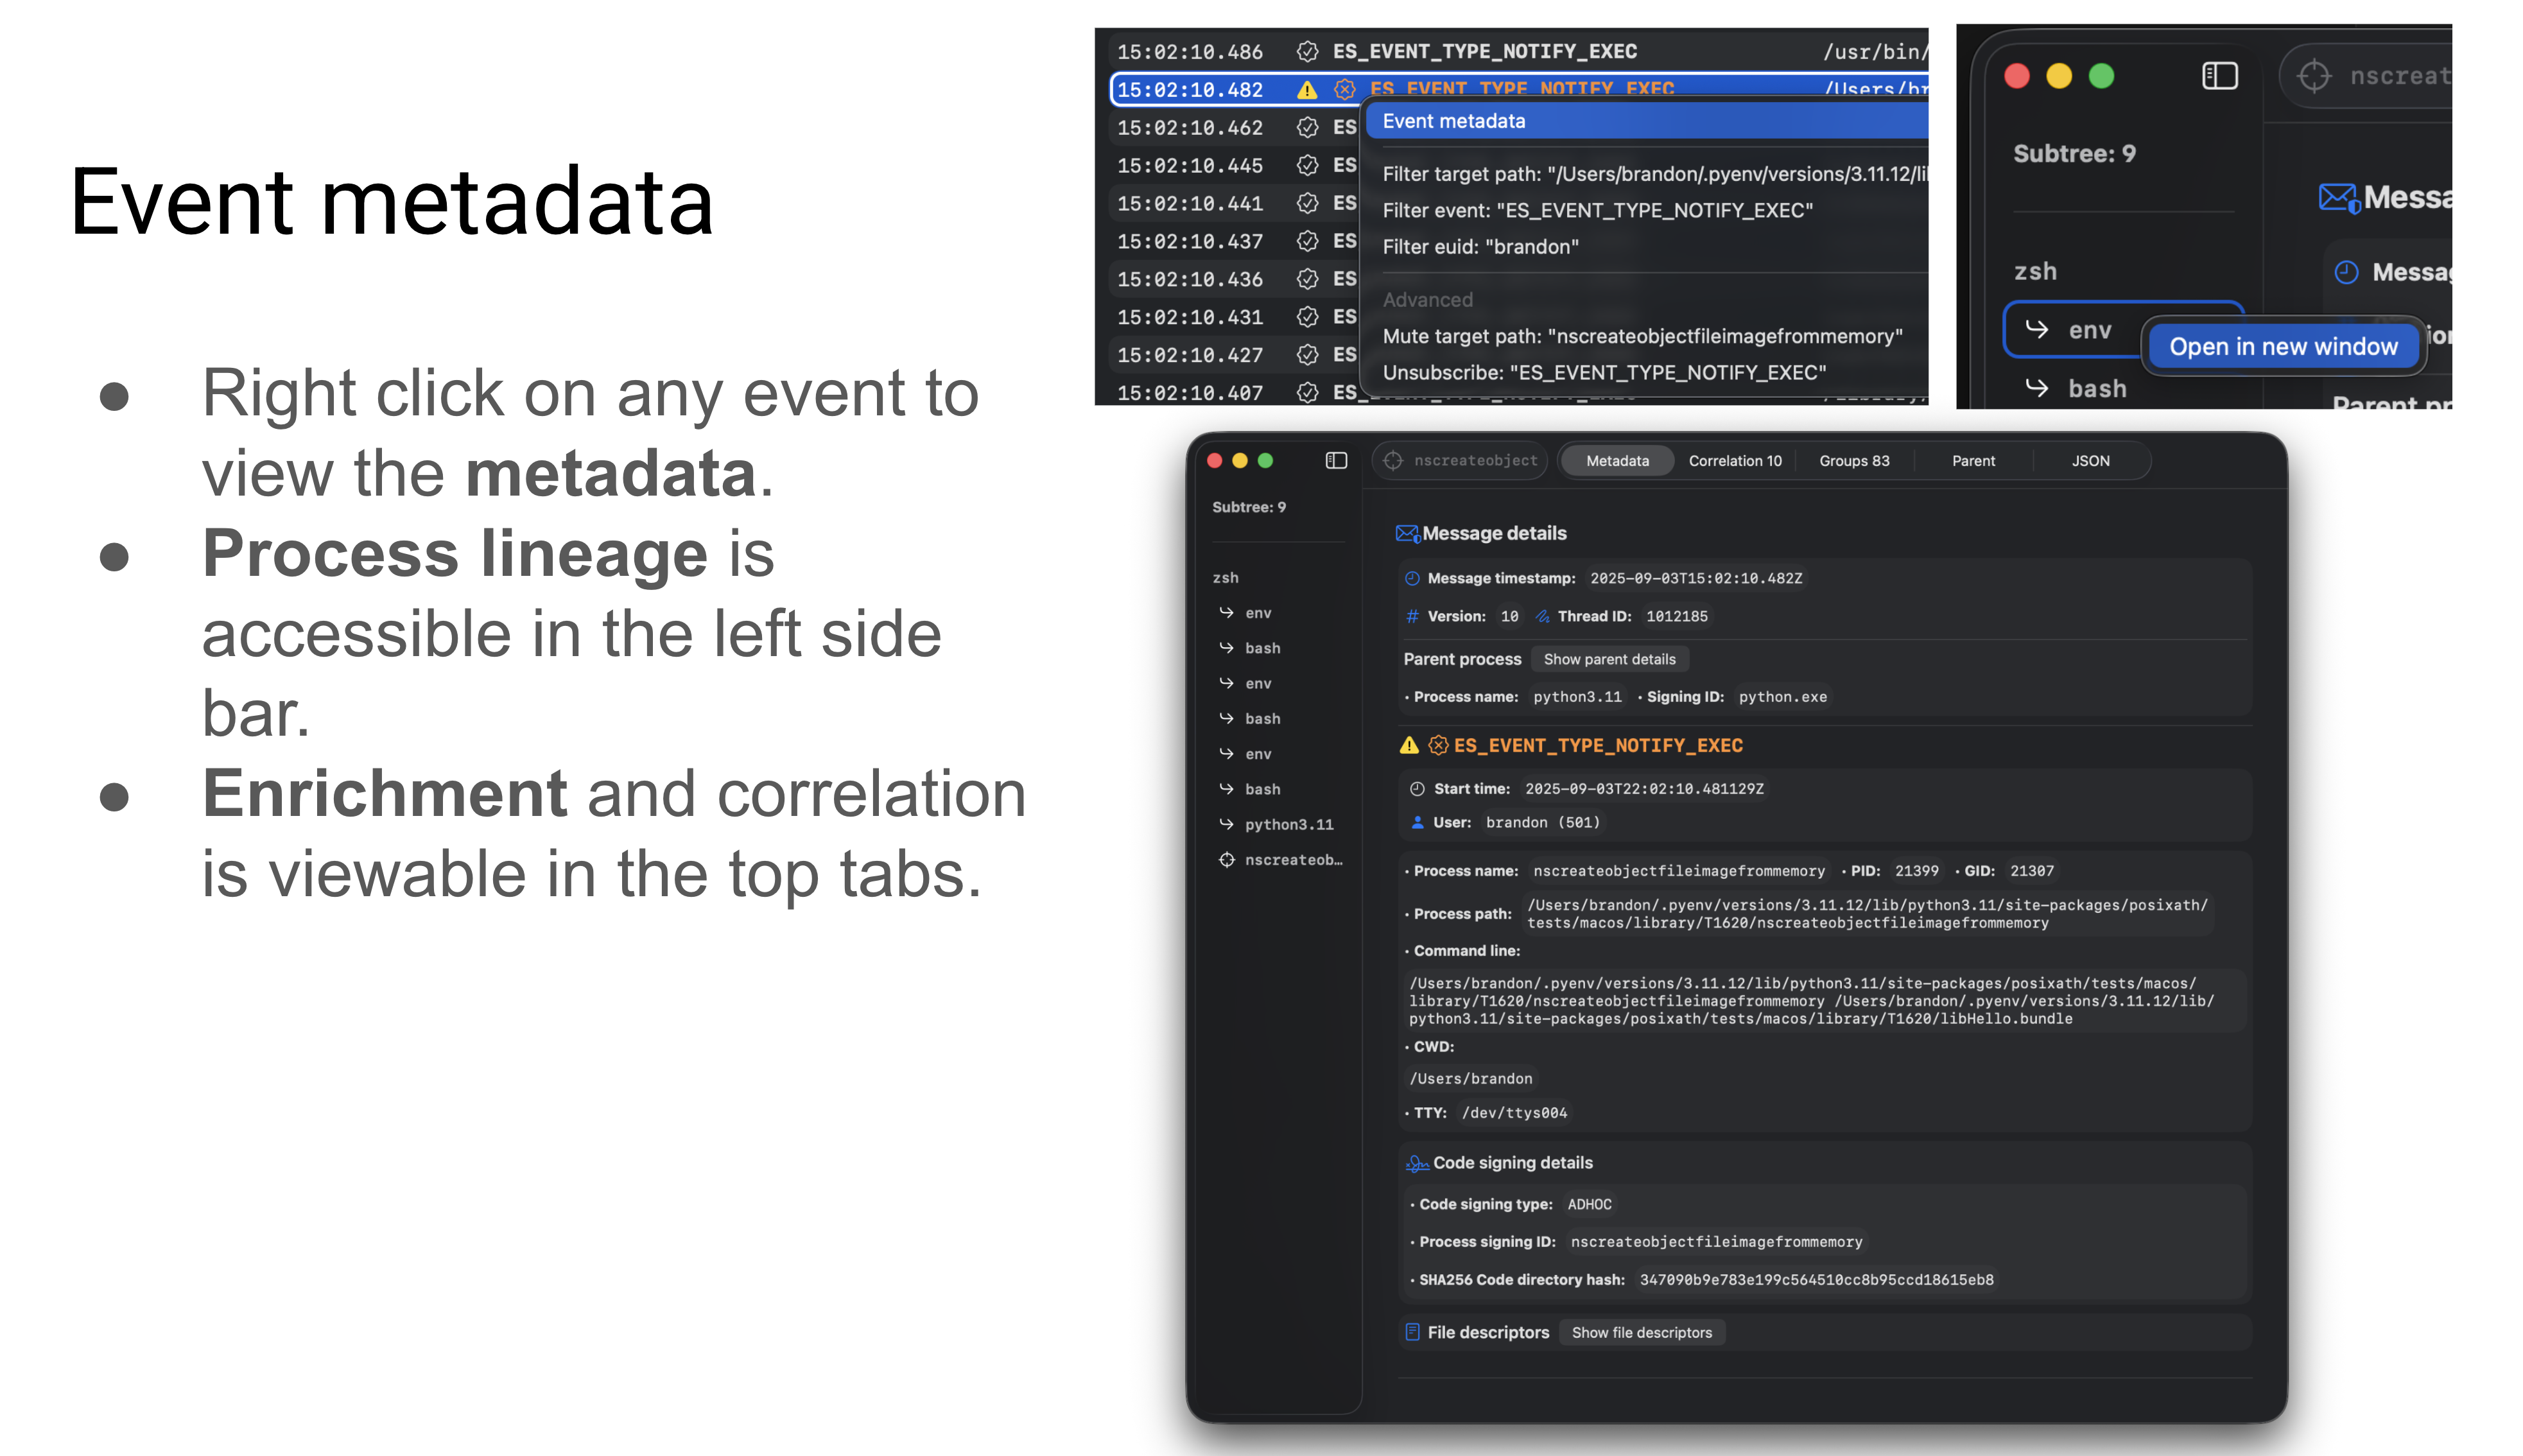 brandon7cc/mac-monitor
Advanced macOS system monitor leveraging Apple Endpoint Security to collect, enrich, and display process, file, memory, and XPC events for malware…
 cecio/usbvalve
Expose USB activity on the fly