

sleuthkit
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
data-recoverydigital-forensicsdisk-forensics+3
3.2k
sleuthkit/sleuthkitForensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 wiltodelta/remove-ai-watermarks
Remove visible and invisible AI watermarks and provenance metadata from images and video. Python library and CLI for SynthID, C2PA, EXIF, IPTC, XMP,…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 zeecka/aperisolve
Automated steganalysis platform that detects hidden data in images using 16 parallel analyzers, bit-layer visualization, and an in-app wiki for CTF…
 ddz/whatsapp-media-decrypt
Decrypt WhatsApp encrypted media files (images, videos, audio, documents) using media keys extracted from iOS ChatStorage.sqlite or Android…
 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
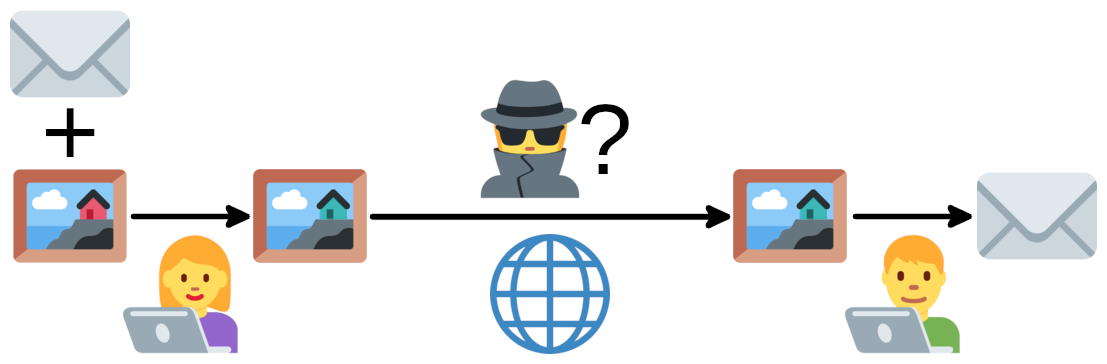 ragibson/steganography
Least Significant Bit Steganography for bitmap images (.bmp and .png), WAV sound files, and byte sequences. Simple LSB Steganalysis (LSB extraction)…
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 korczis/foremost
File carving utility that recovers deleted files from disk images and raw drives by matching headers, footers, and internal structures via…
 redaelli/imago-forensics
Imago is a python tool that extract digital evidences from images.
 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 cleasbycode/jdvrif
Steganography Tool for JPG Images
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 jas502n/010-editor-template
Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures