

imago-forensics
 redaelli/imago-forensics
Imago is a python tool that extract digital evidences from images.
digital-forensicsforensicsosint+1
2697 years ago
redaelli/imago-forensicsImago is a python tool that extract digital evidences from images.
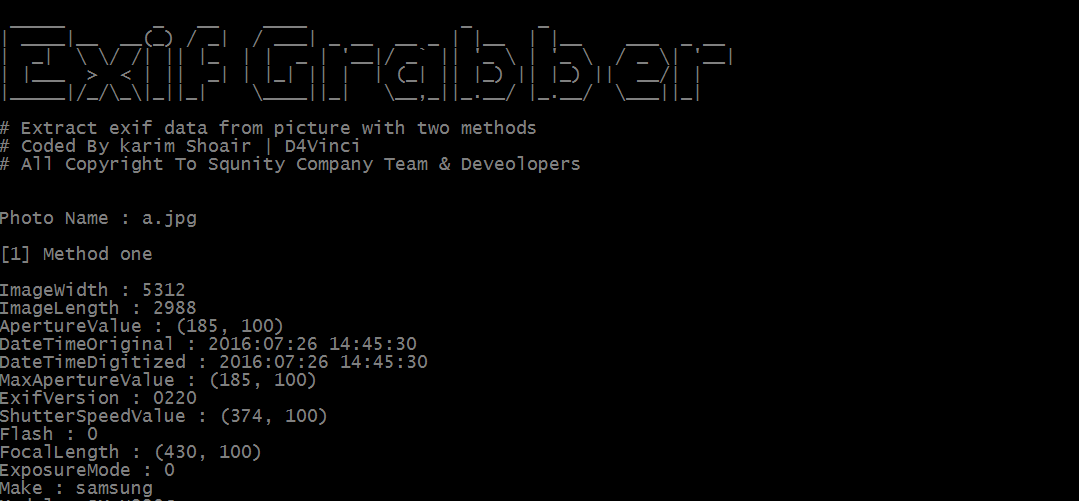 d4vinci/exif-grabber
A python tool that will extract exif data from picture with two methods
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
 trustedsec/tscopy
Python tool that parses the NTFS $MFT to copy locked files during incident response, bypassing OS locks by reading raw disk locations. Supports…
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 omriher/captipper
Malicious HTTP traffic explorer
 pelock/total-commander-ftp-password-recovery-tool-python
Total Commander FTP Password Recovery Tool for Python allows you to decrypt the FTP account password information for all Total Commander versions…
 rowingdude/analyzemft
analyzeMFT.py is designed to fully parse the MFT file from an NTFS filesystem and present the results as accurately as possible in multiple formats.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
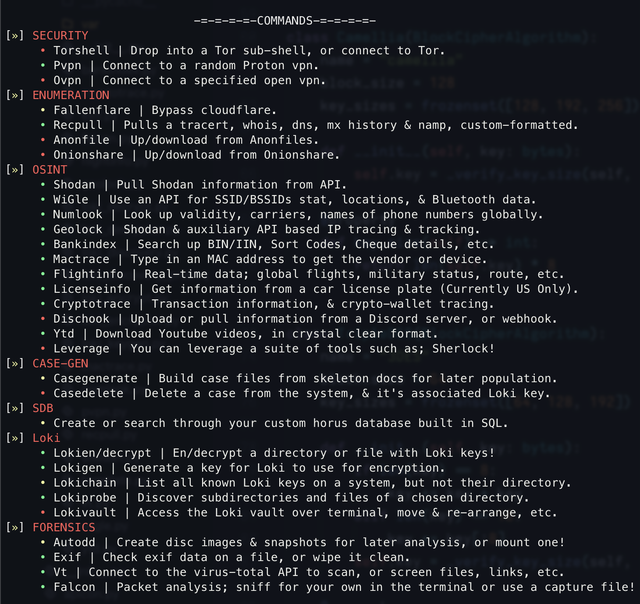 6abd/horus
An OSINT / digital forensics tool built in Python

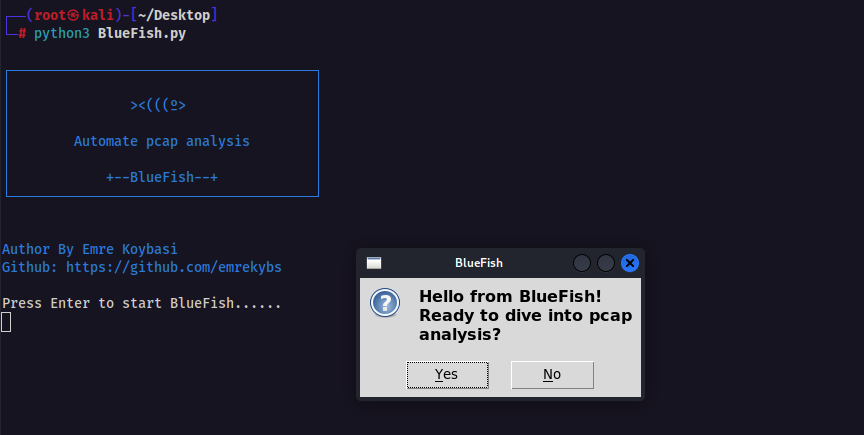 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
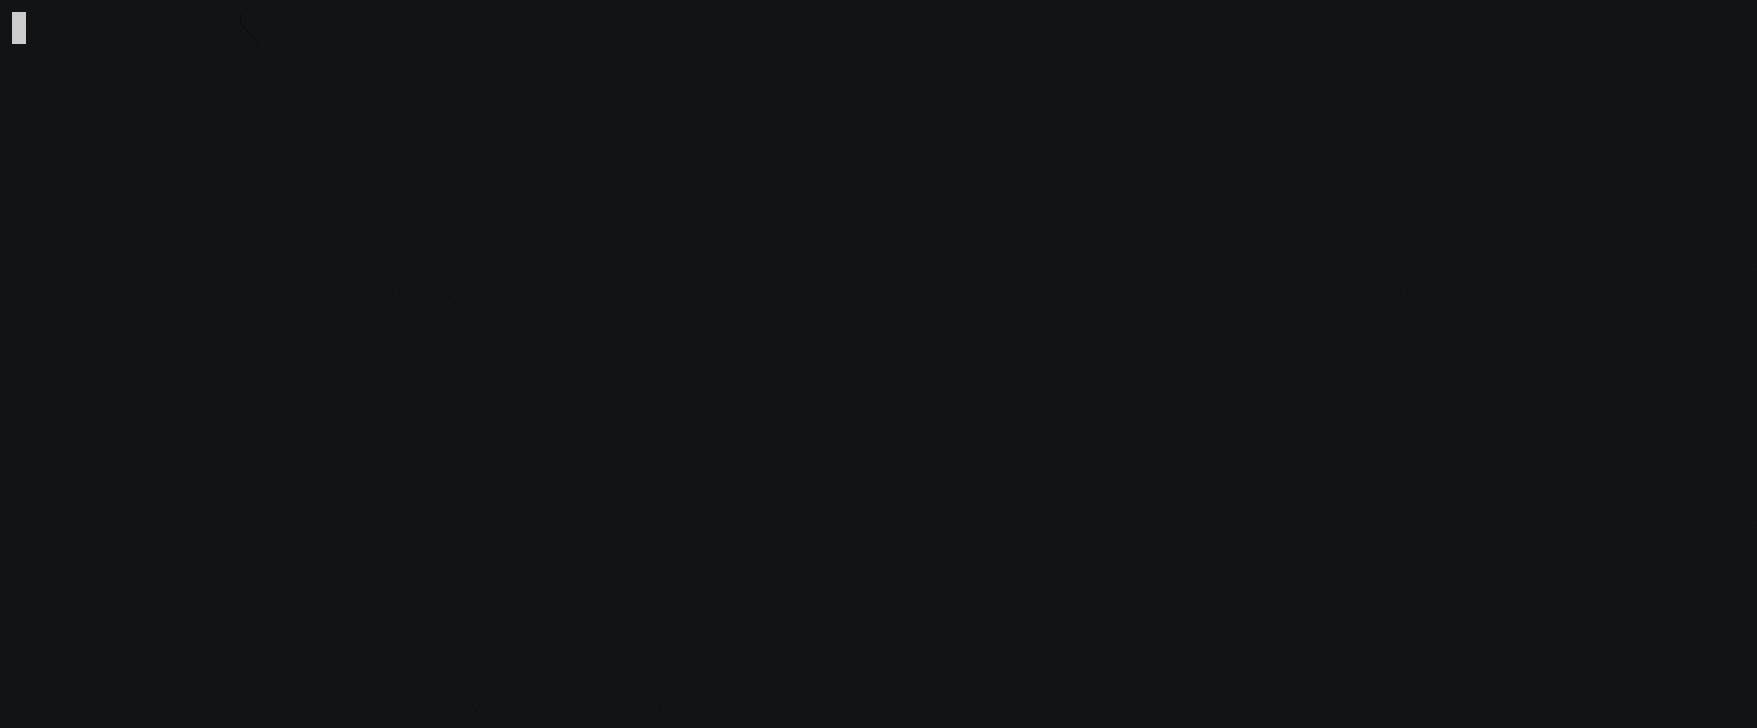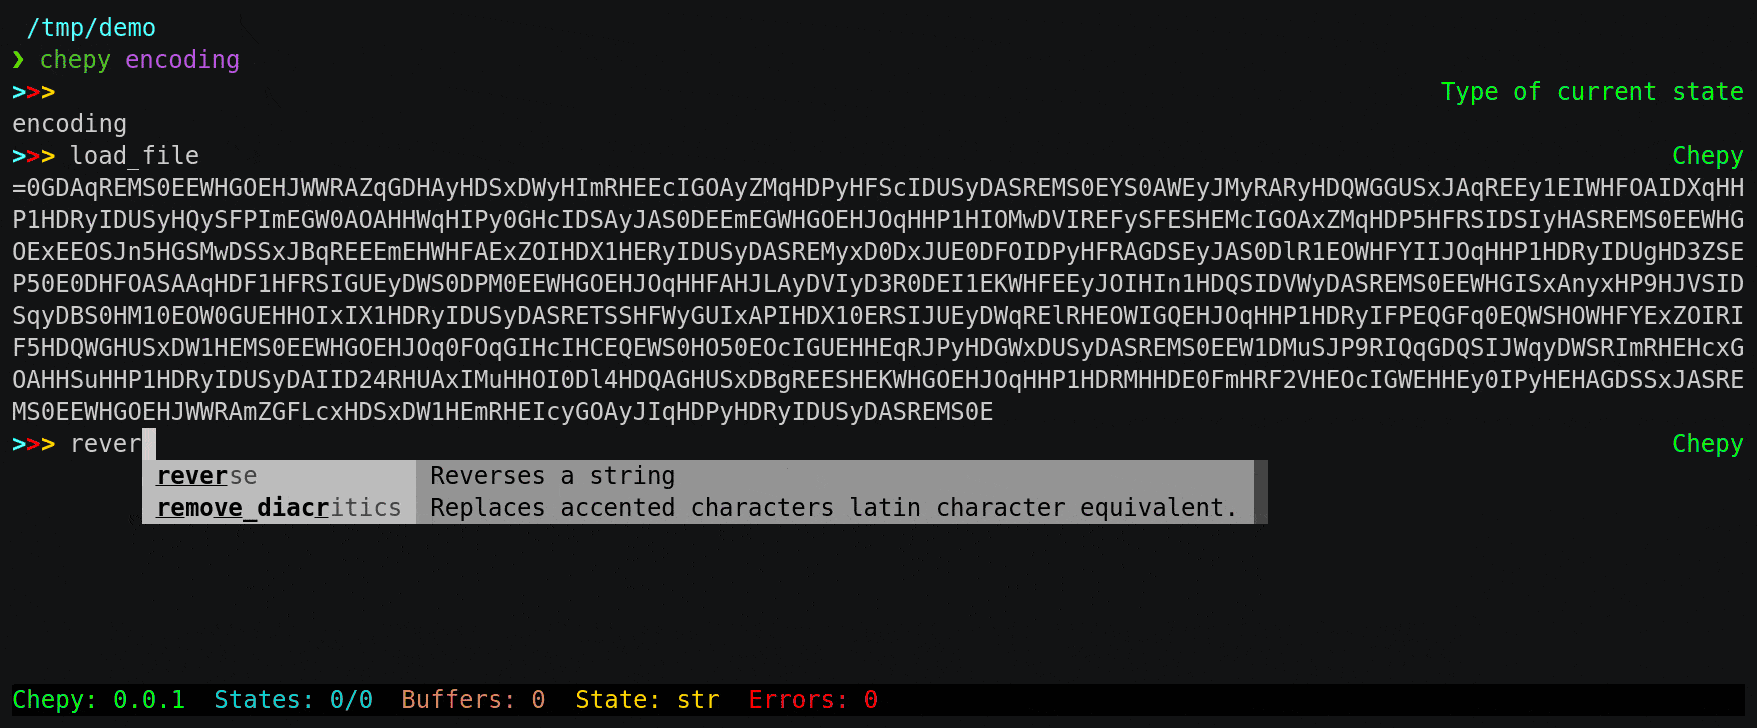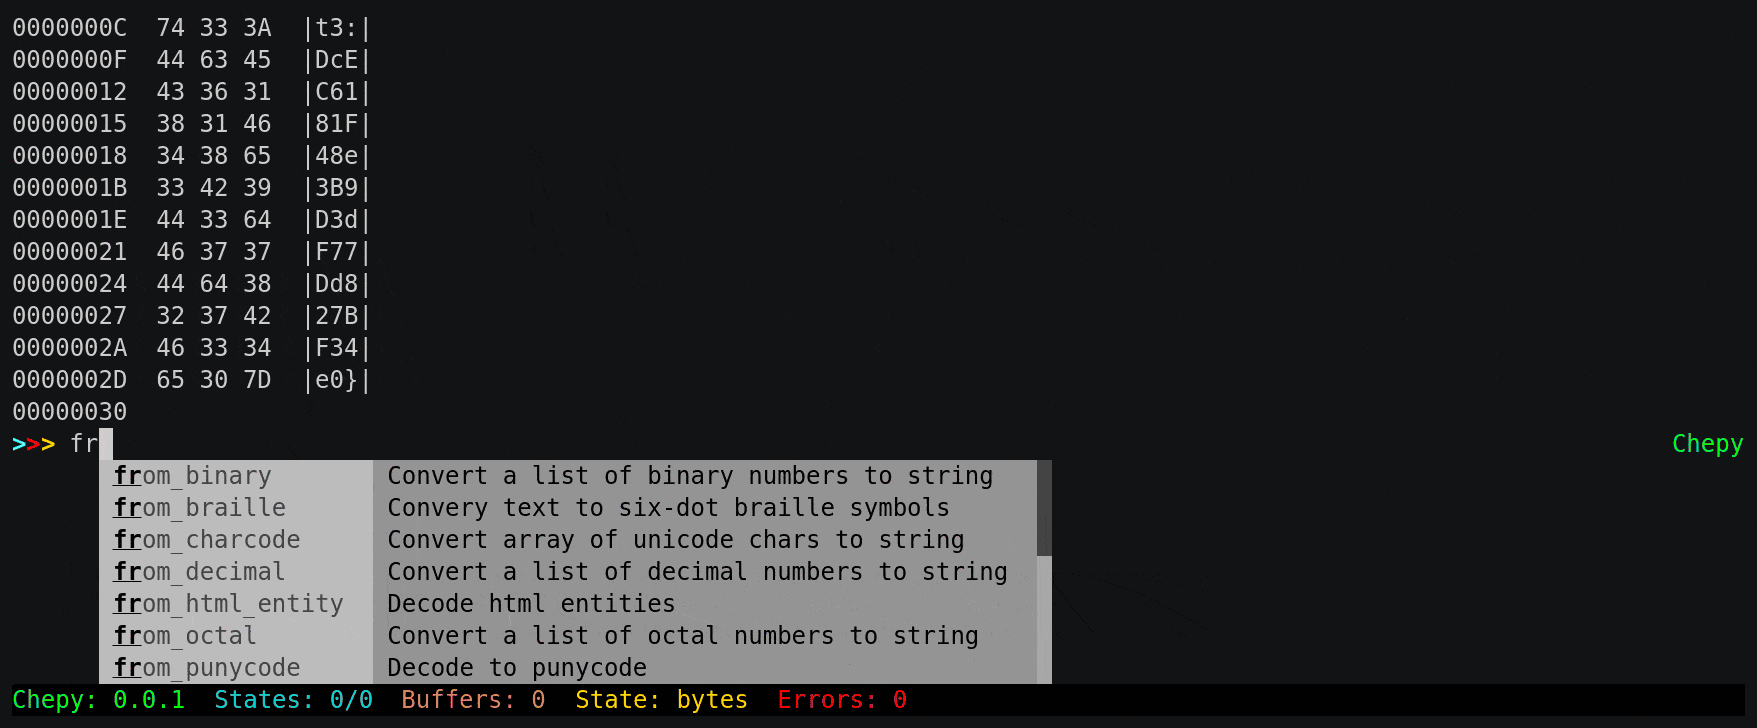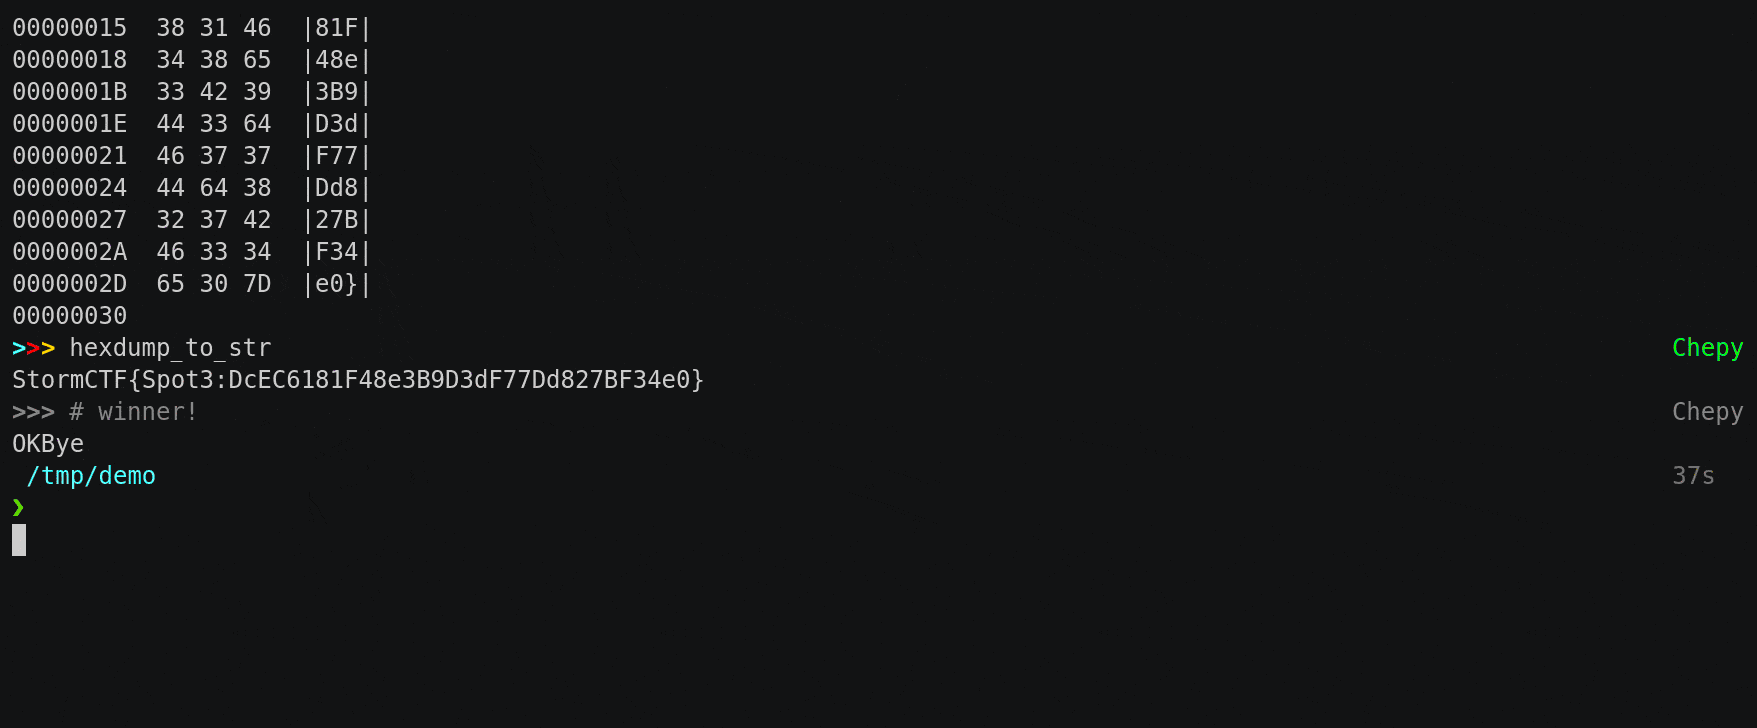 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
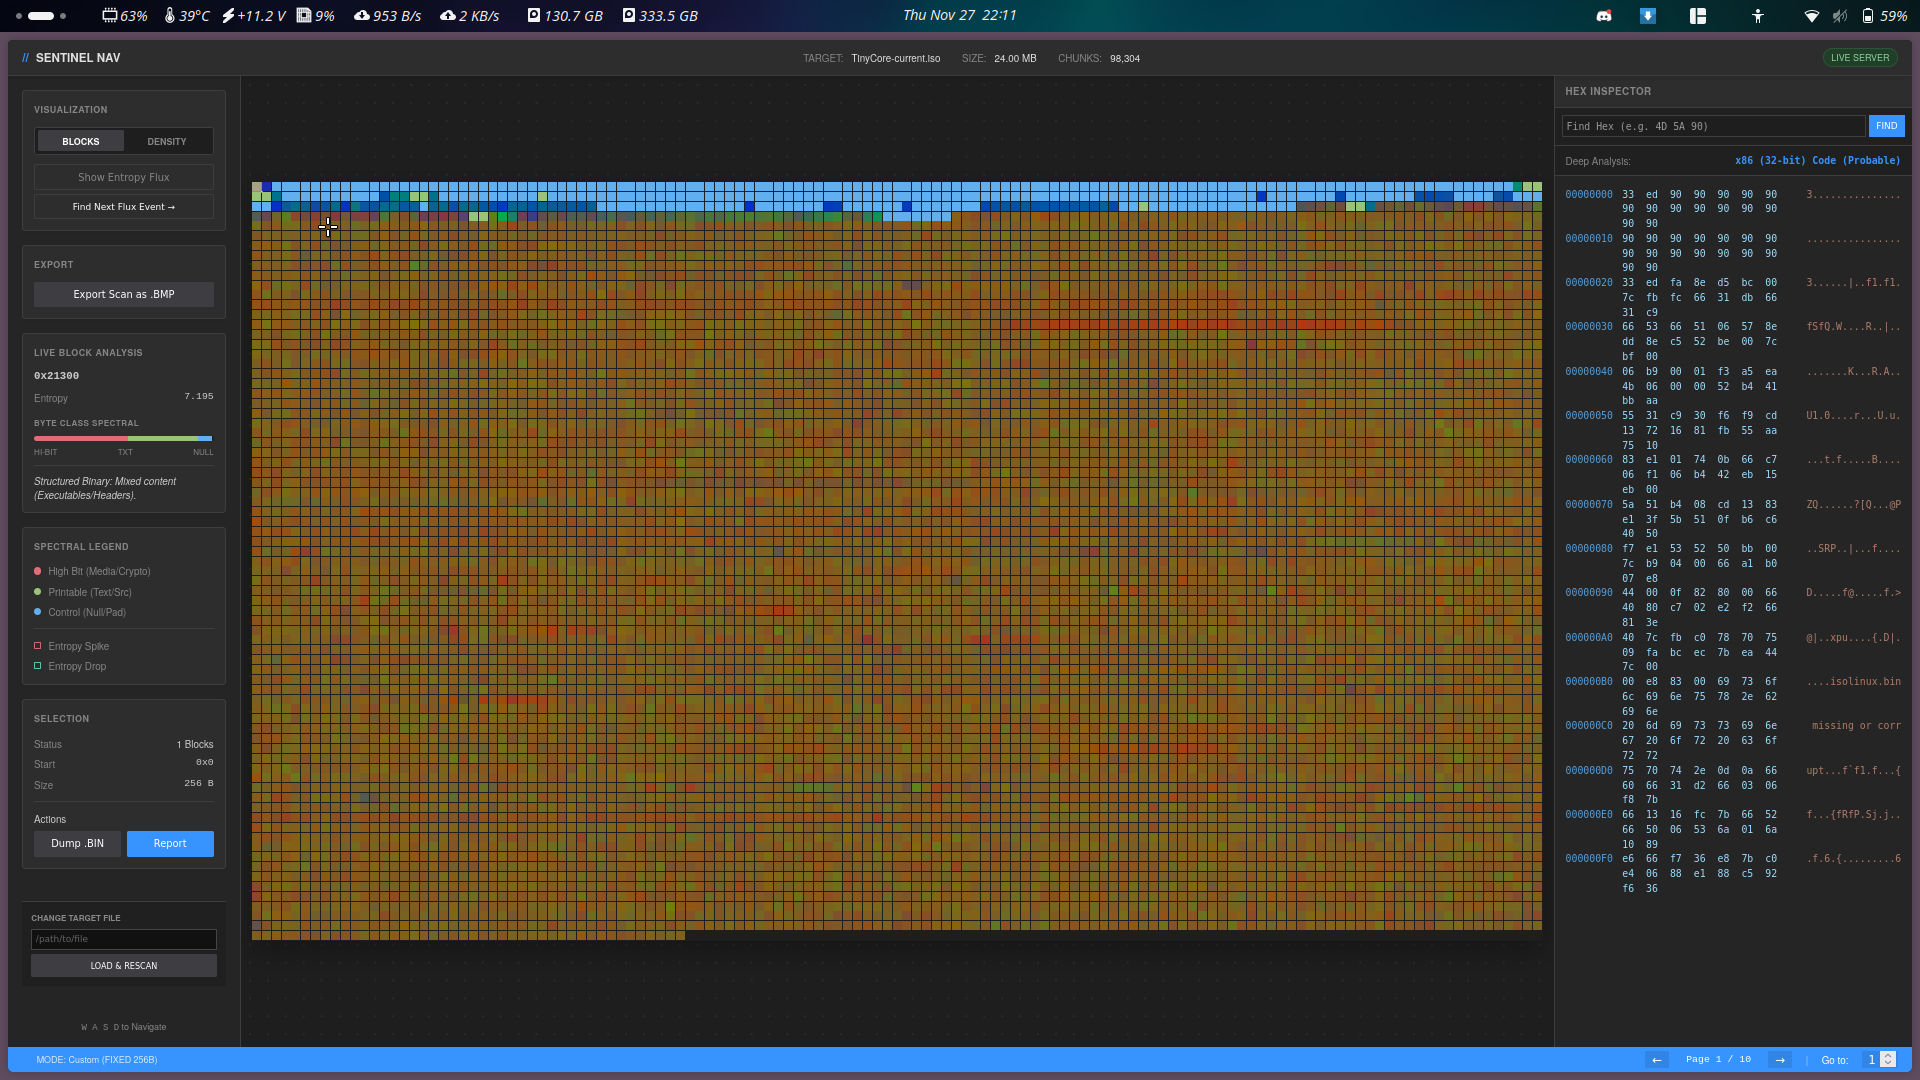 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.