
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
123 results
uac preview

uac

GitHubtclahr/uac

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.5k18 days ago
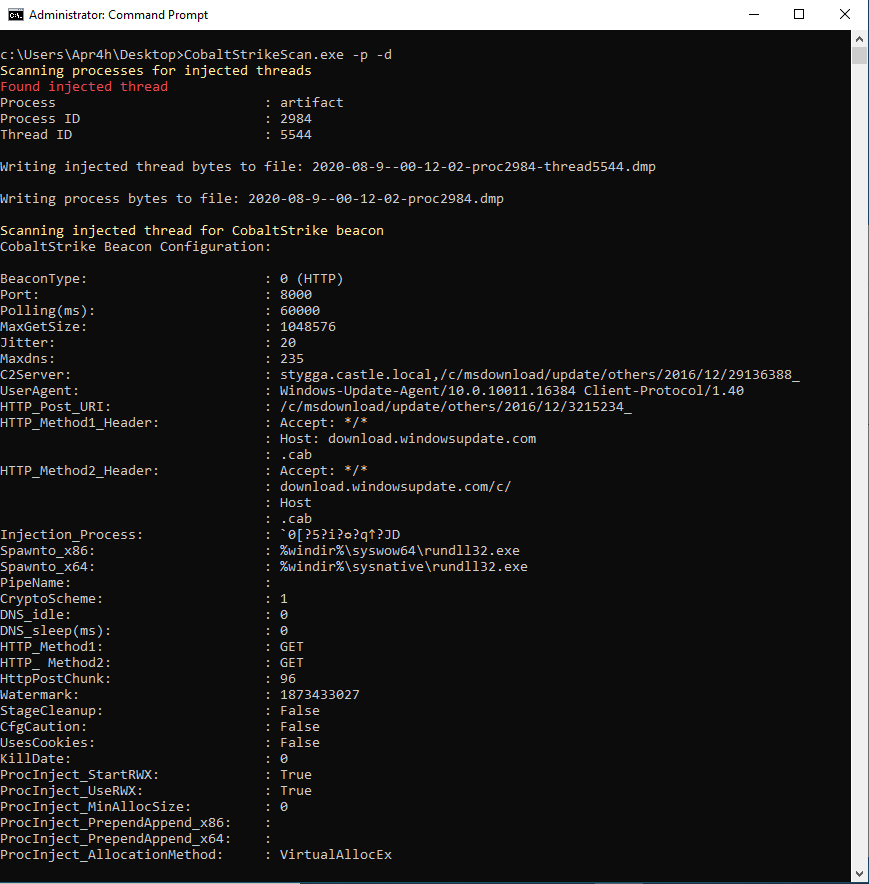
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

Scan files or process memory for CobaltStrike beacons and parse their configuration

defensive-toolsdigital-forensicsforensics+4
9175 years ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
binary-analysisdefensive-toolsforensics+3
6818 months ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
digital-forensicsdisk-forensicsforensics+3
5215 years ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3911 month ago
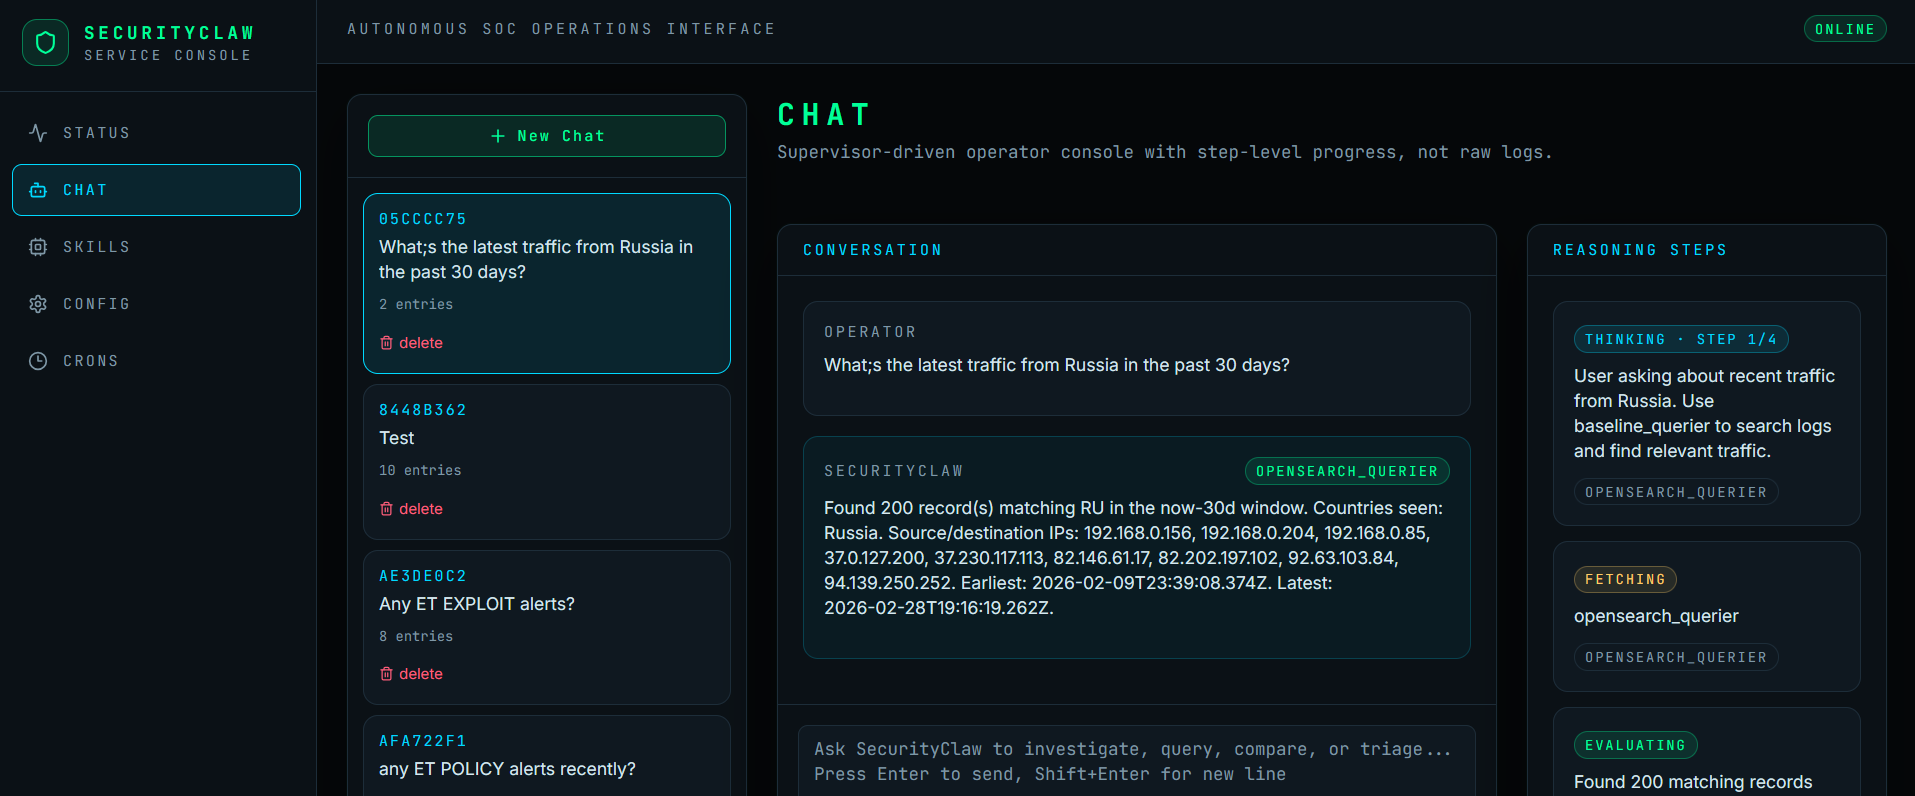
SecurityClaw preview

SecurityClaw

GitHubsecurityclaw/securityclaw

A modular, skill-based autonomous Security Operations Center (SOC) agent that monitors OpenSearch/Elasticsearch data, builds RAG-based behavioral…
ai-securityanomaly-detectionforensics+8
2722 months ago
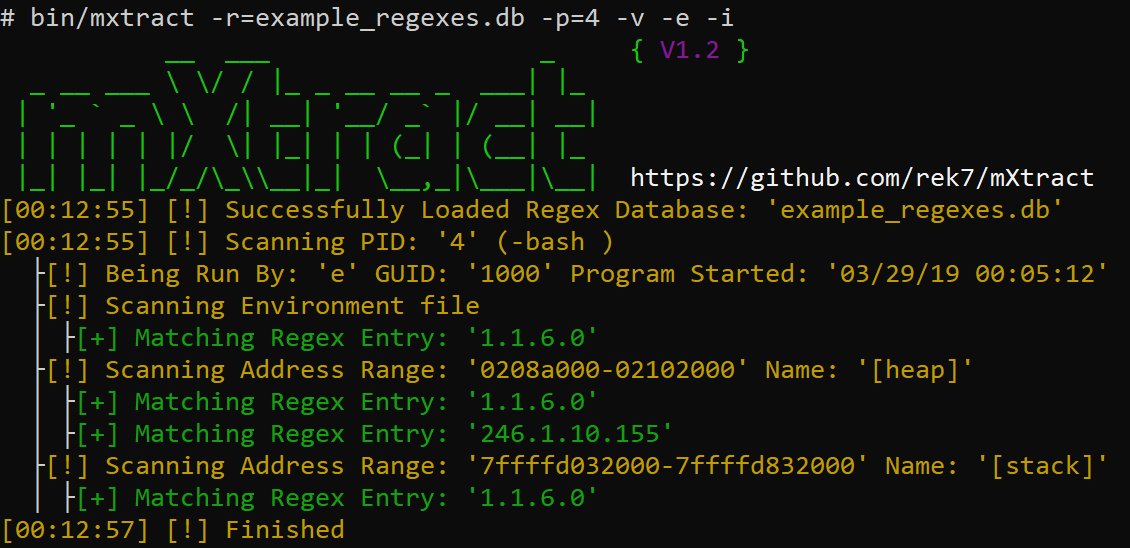
mXtract preview

mXtract

GitHubrek7/mxtract

mXtract - Memory Extractor & Analyzer

forensicsinformation-gatheringmemory-forensics+2
5874 years ago
SuperMem preview

SuperMem

GitHubcrowdstrike/supermem

A python script developed to process Windows memory images based on triage type.
digital-forensicsforensicsincident-response+2
2682 years ago
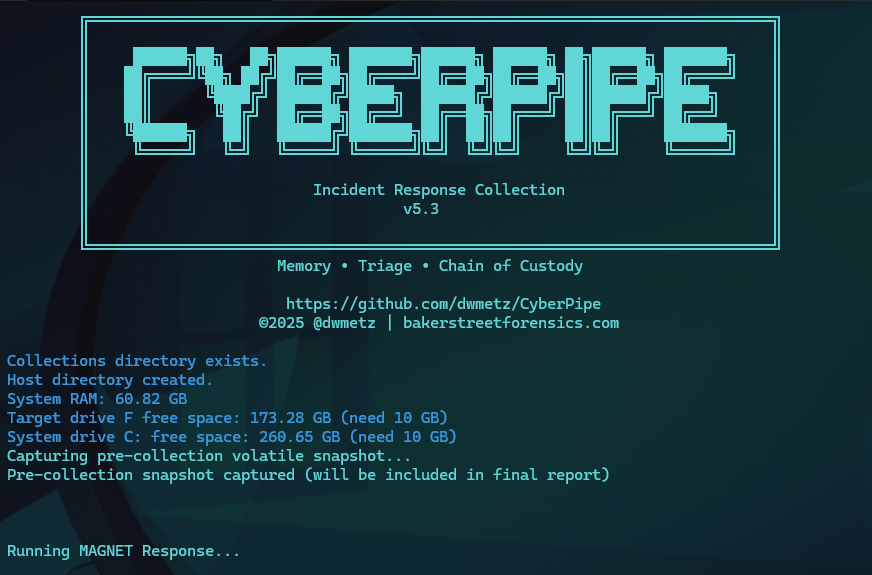
CyberPipe preview

CyberPipe

GitHubdwmetz/cyberpipe

An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
digital-forensicsdisk-forensicsforensics+2
3479 months ago
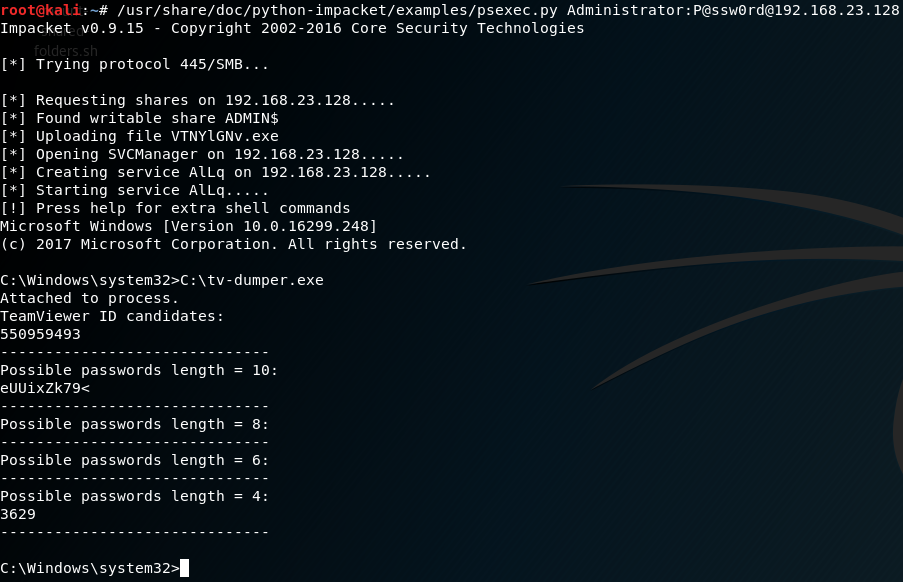
teamviewer-dumper preview

teamviewer-dumper

GitHubattackercan/teamviewer-dumper

Dump TeamViewer ID and password from memory. Works much better than other tools.

digital-forensicsforensicsinformation-gathering+3
988 years ago
TuxResponse preview

TuxResponse

GitHubla3ar0v/tuxresponse

Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
digital-forensicsdisk-forensicsforensics+5
915 months ago
BareMetal-RAM-Dumper preview

BareMetal-RAM-Dumper

GitHubpiat0n/baremetal-ram-dumper

A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.

data-recoverydigital-forensicsexploitation+3
1042 months ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
672 months ago
openclaw-security-monitor preview

openclaw-security-monitor

GitHubadibirzu/openclaw-security-monitor

Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.
defensive-toolseducationforensics+9
488 days ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
cryptographydigital-forensicseducation+7
314 months ago
zettelforge preview

zettelforge

GitHubthreatrecall/zettelforge

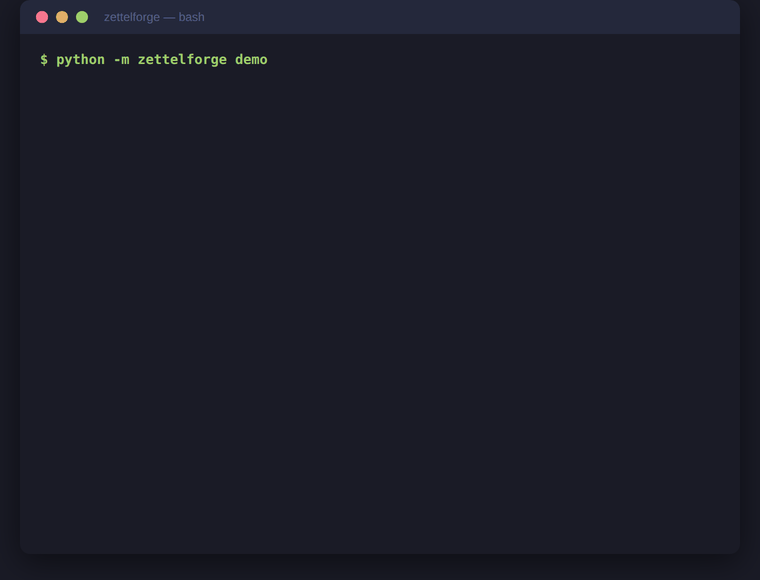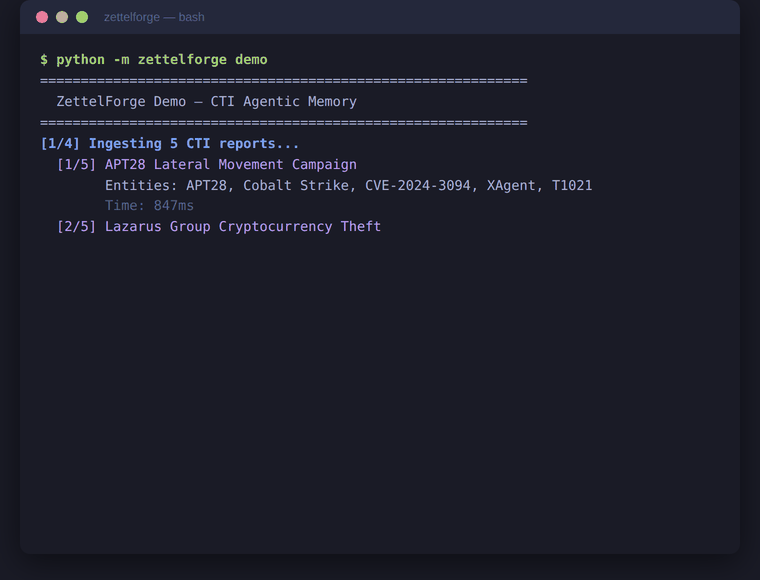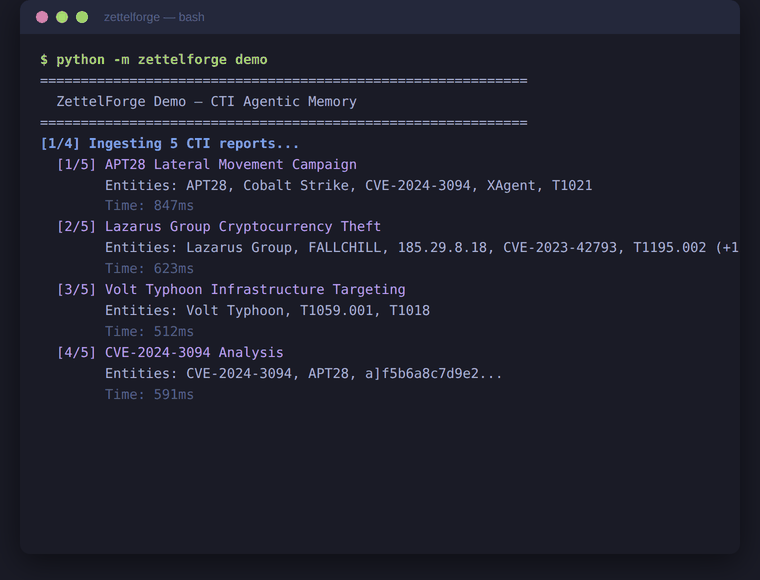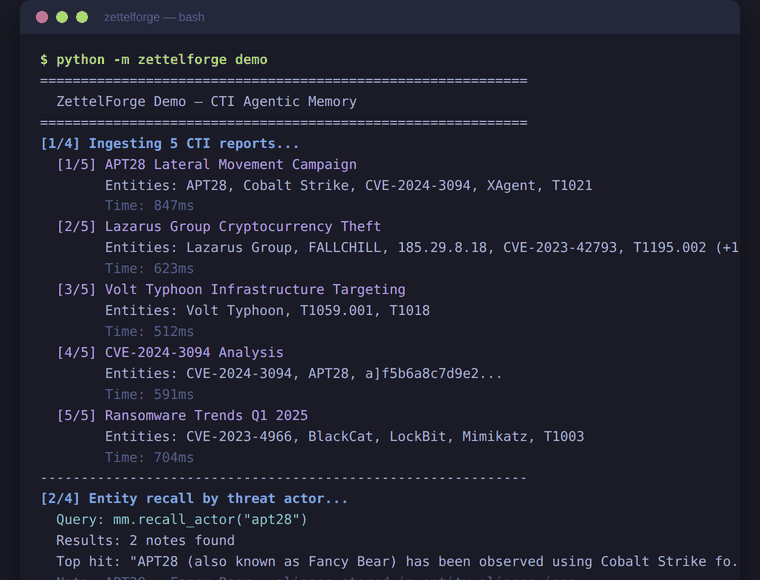
Agentic memory for CTI in Python — STIX knowledge graphs, threat-actor alias resolution, offline-first RAG, MCP server for Claude Code and LangChain…
ai-securityeducationforensics+8
632 months ago
mboxshell preview

mboxshell

GitHubdcarrero/mboxshell

mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…

data-recoverydigital-forensicsemail-security+4
432 days ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
Previous1234567Next