
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
95 results
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis

binary-analysiscryptographyforensics+3
908 years ago
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

A Network Inspection Tool

forensicsfuzzingintrusion-detection+5
829 years ago
CertVerify preview

CertVerify

GitHubpassword123456/certverify

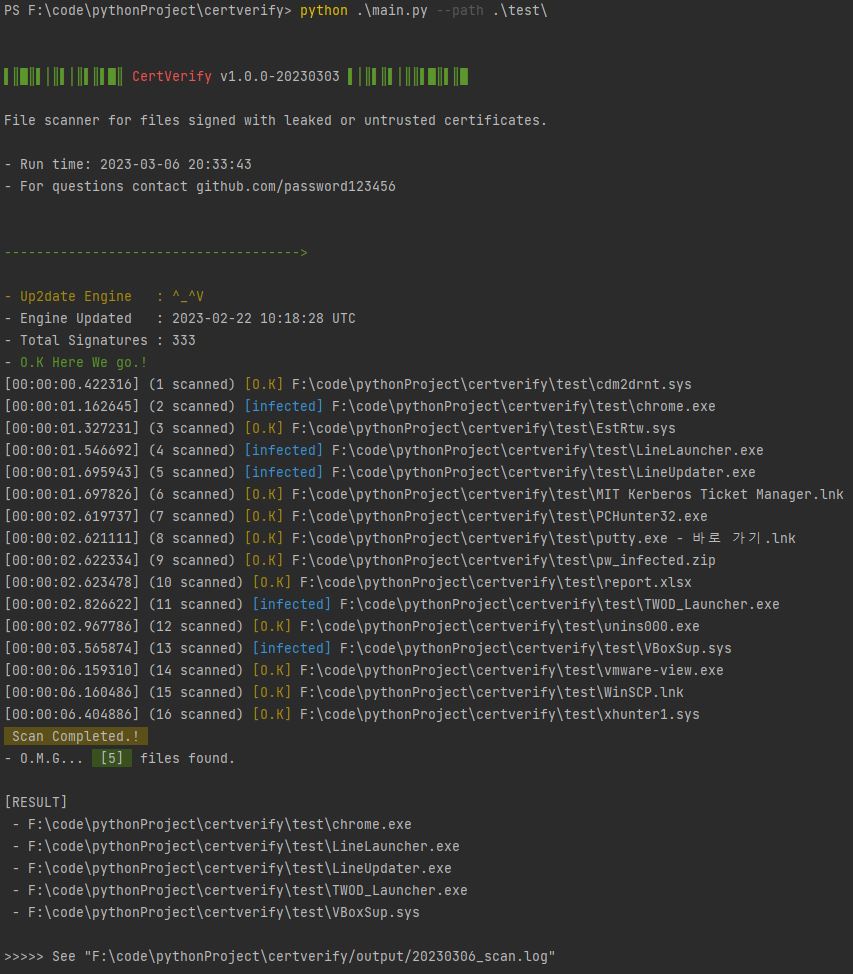
A scanner that files with compromised or untrusted code signing certificates written in python.

code-analysisforensicsmalware-analysis+1
653 years ago
z9 preview

z9

GitHubsh1n0g1/z9

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
forensicslog-analysismalware-analysis+2
682 years ago
MemTracer preview

MemTracer

GitHubmayhamad/memtracer

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…
digital-forensicsforensicsmalware-analysis+1
644 years ago
ModTracer preview

ModTracer

GitHubmatheuzsecurity/modtracer

Detects hidden Linux kernel rootkits (LKM-based) and restores their visibility using kernel-level inspection techniques for forensic analysis and…
forensicsmalware-analysis
881 year ago
xwf-yara-scanner preview

xwf-yara-scanner

GitHubcrowdstrike/xwf-yara-scanner

Native YARA scanner X-Tension for X-Ways Forensics, enabling in-snapshot file scanning with multi-threaded RVS support, report table output, and no…
digital-forensicsforensicsmalware-analysis+1
921 year ago
OneNoteAnalyzer preview

OneNoteAnalyzer

GitHubknight0x07/onenoteanalyzer

A C# based tool for analysing malicious OneNote documents
forensicsmalware-analysisreverse-engineering+1
1173 years ago
kernagent preview

kernagent

GitHubkarib0u/kernagent

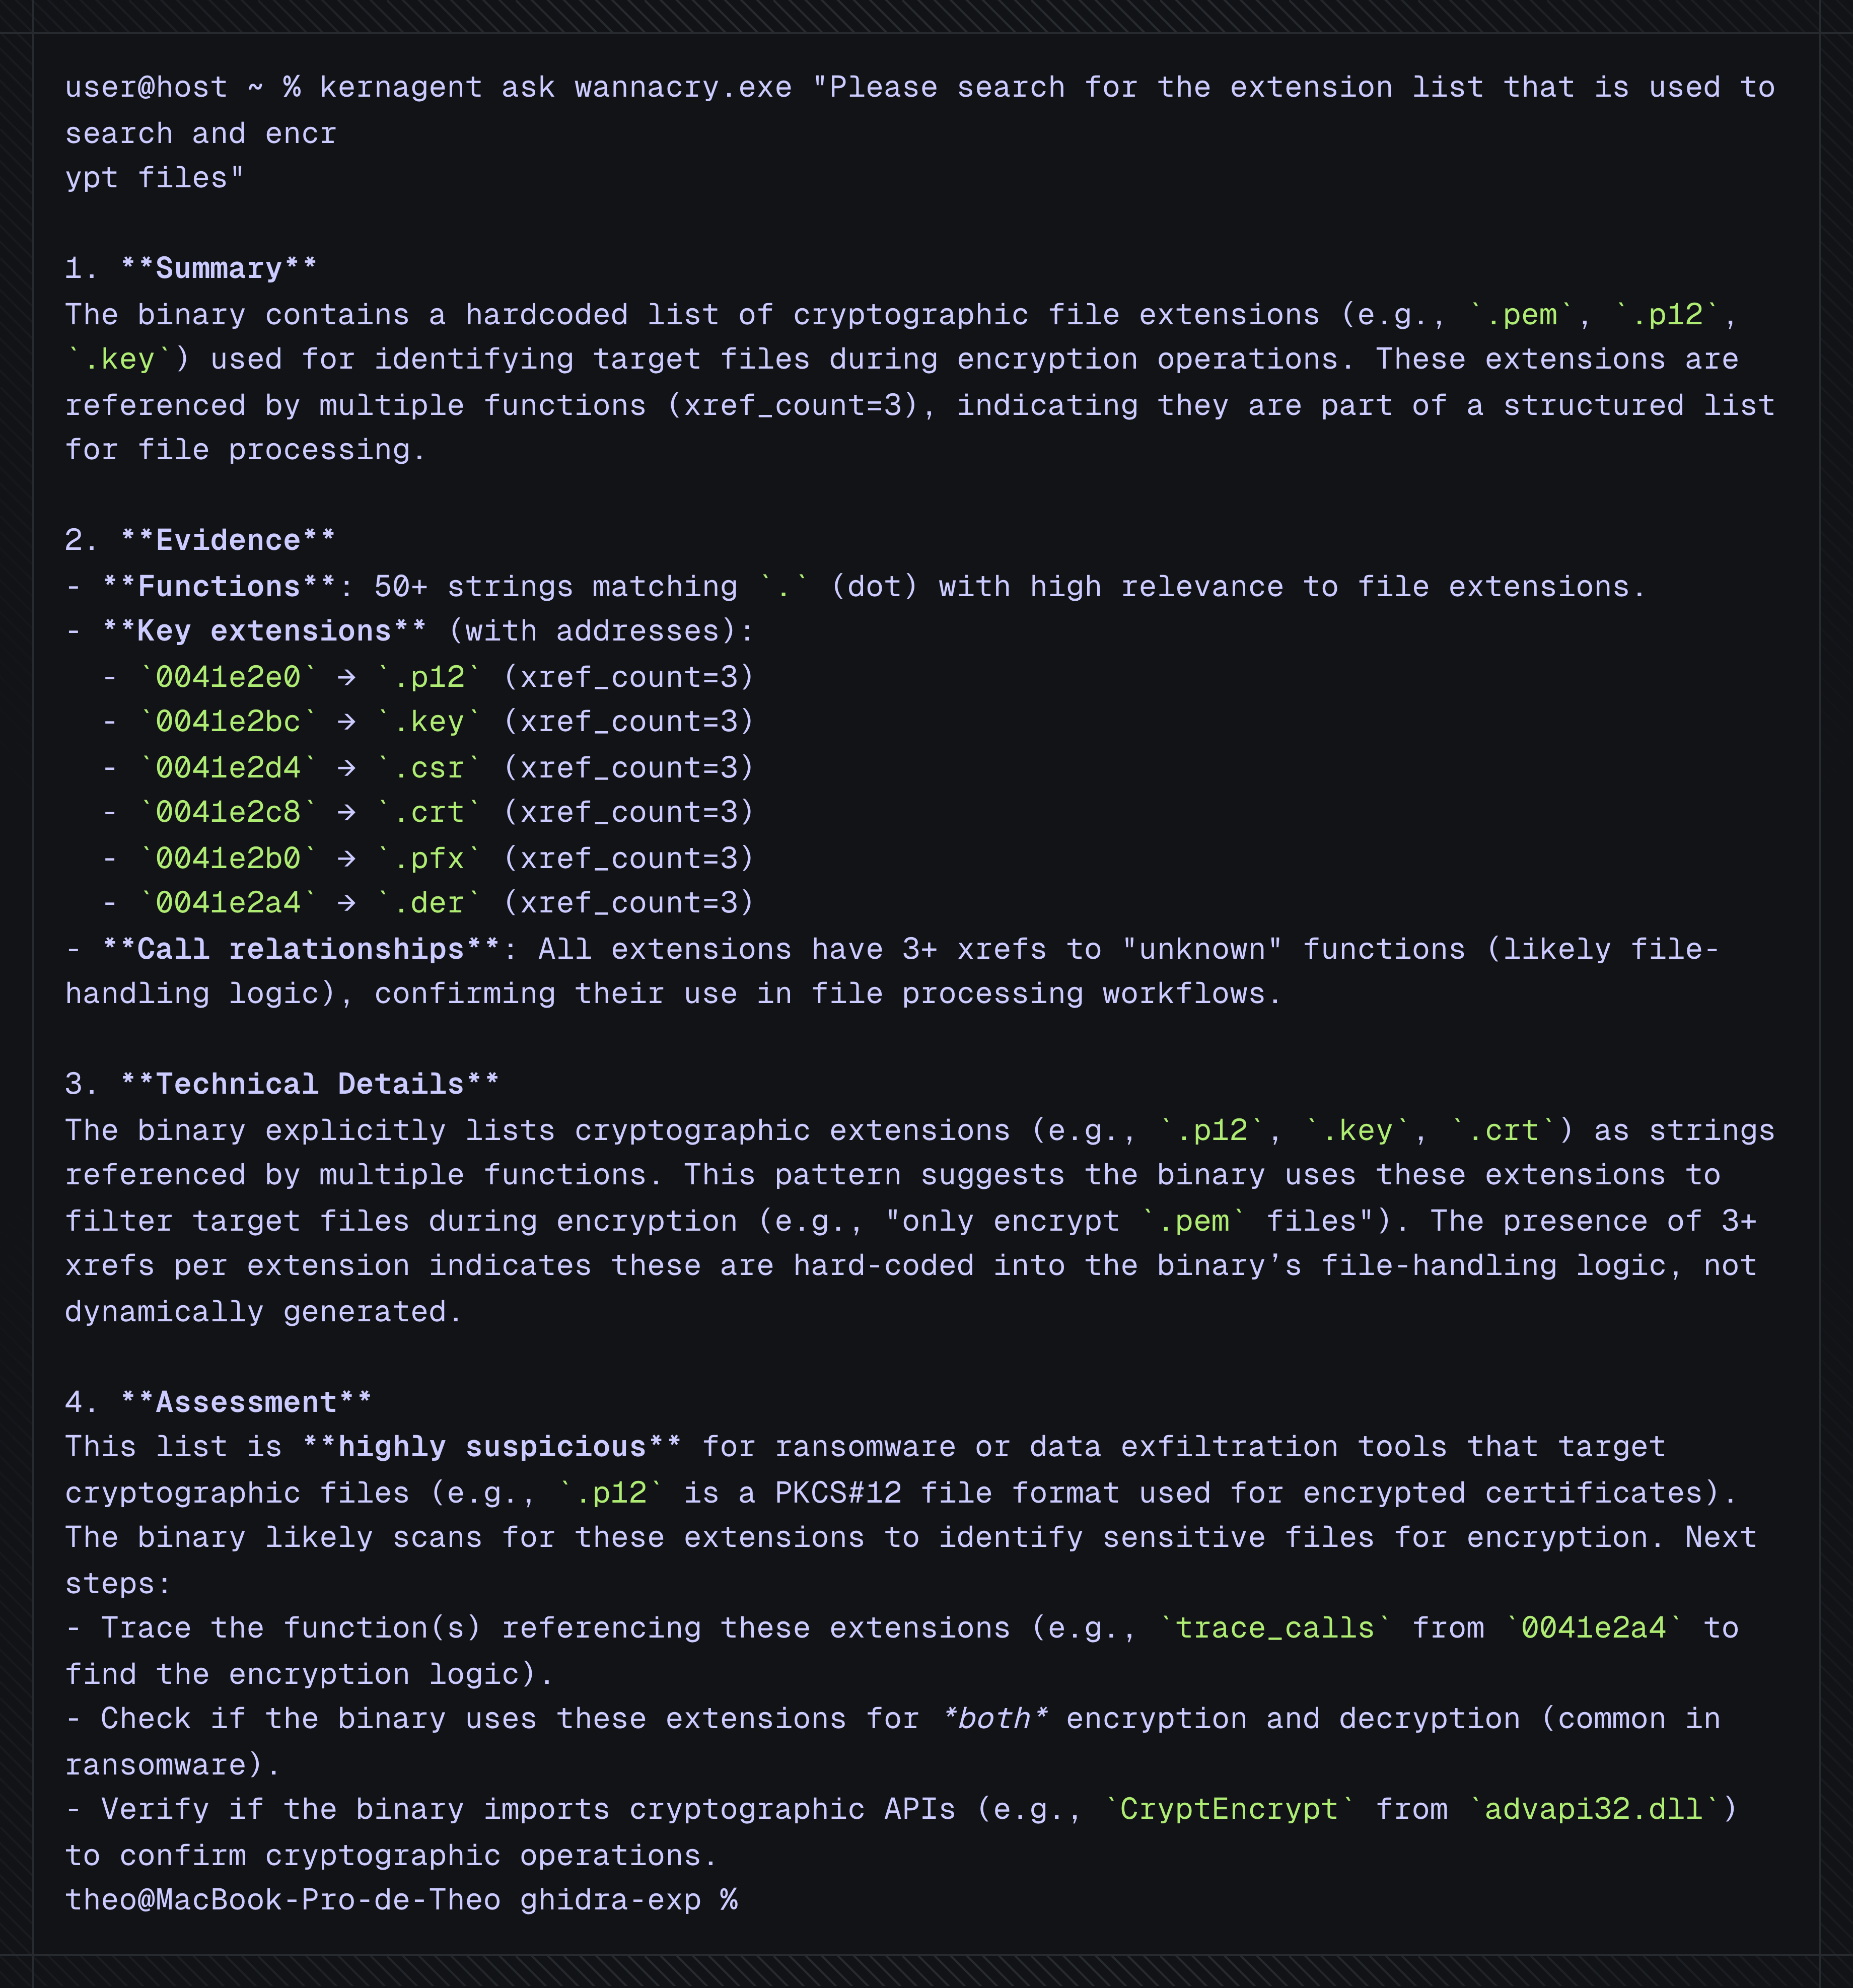
Headless AI agent for deterministic reverse engineering.
ai-assisted-reversingbinary-analysisforensics+4
10311 months ago
machofile preview

machofile

GitHubpstirparo/machofile

machofile is a module to parse Mach-O binary files
binary-analysisforensicsmalware-analysis+2
998 months ago
filterforge preview

filterforge

GitHubcloudflare/filterforge

Tool for solving BPF filters and crafting packets based on these.
binary-analysisforensicsfuzzing+5
647 months ago
cve-2024-3094-tools preview

cve-2024-3094-tools

GitHubjfrog/cve-2024-3094-tools

Shell-based scanner to detect the XZ Backdoor (CVE-2024-3094) vulnerability in files and directories, enabling rapid identification and mitigation of…
forensicsincident-responsemalware-analysis+3
442 years ago
excelpeek preview

excelpeek

GitHubslaughterjames/excelpeek

Static analysis tool for investigating potentially malicious Microsoft Excel files, extracting metadata, macros, and embedded objects to aid digital…
digital-forensicsforensicsmalware-analysis+1
384 years ago
DriverSentinel preview

DriverSentinel

GitHubbi8d0/driversentinel

DriverSentinel is a security tool developed in Go that detects malicious and vulnerable drivers on Windows systems by comparing them against the…

defensive-toolsforensicsincident-response+2
352 months ago
rtf_exploit_extractor preview

rtf_exploit_extractor

GitHubcyberclues/rtf_exploit_extractor

Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
binary-analysisexploitationforensics+2
239 years ago
SecFlow preview

SecFlow

GitHubaradhyacp/secflow

AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
ai-securityforensicsincident-response+6
227 months ago
YAMA-dev preview

YAMA-dev

GitHubt-tani/yama-dev

Yet Another Memory Analyzer for malware detection
forensicsincident-responsemalware-analysis+1
243 years ago
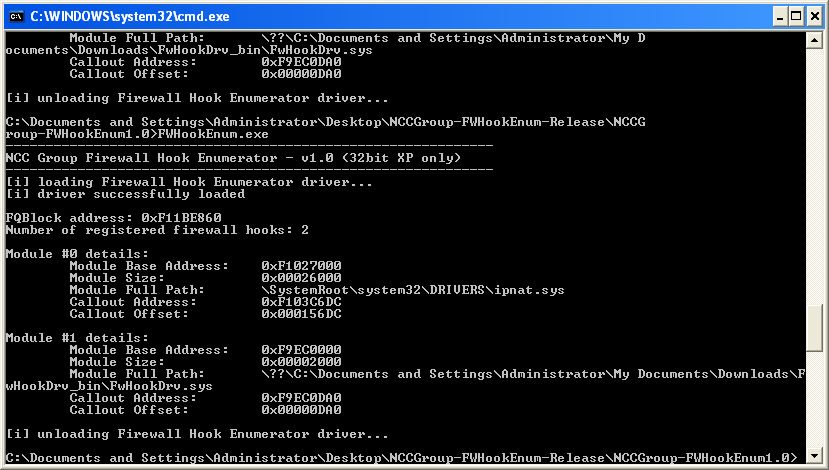
WindowsFirewallHookDriverEnumeration preview

WindowsFirewallHookDriverEnumeration

GitHubnccgroup/windowsfirewallhookdriverenumeration

Tools to enumerate Windows Firewall Hook Drivers on Windows 2000, XP and 2003

digital-forensicsforensicsincident-response+2
2111 years ago
Previous123456Next