

uac
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
digital-forensicsforensicsincident-response+3
1.4k1 month ago
tclahr/uacPortable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
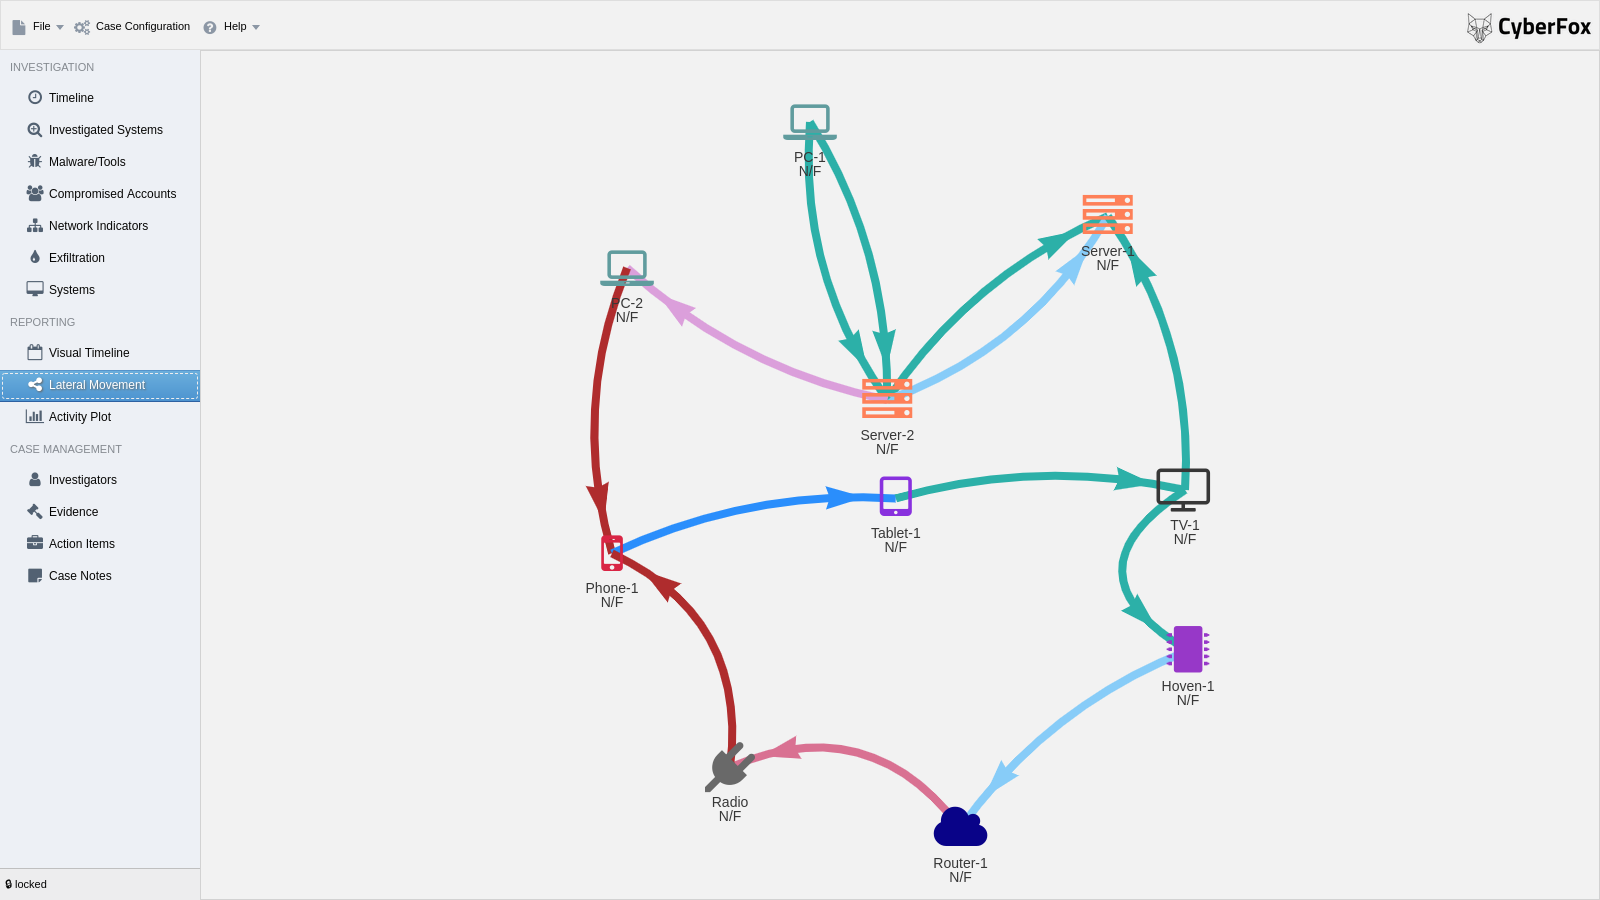 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders

 graniet/operative-framework
operative framework is a rust investigation OSINT framework, you can interact with multiple targets, execute multiple modules, create links with…
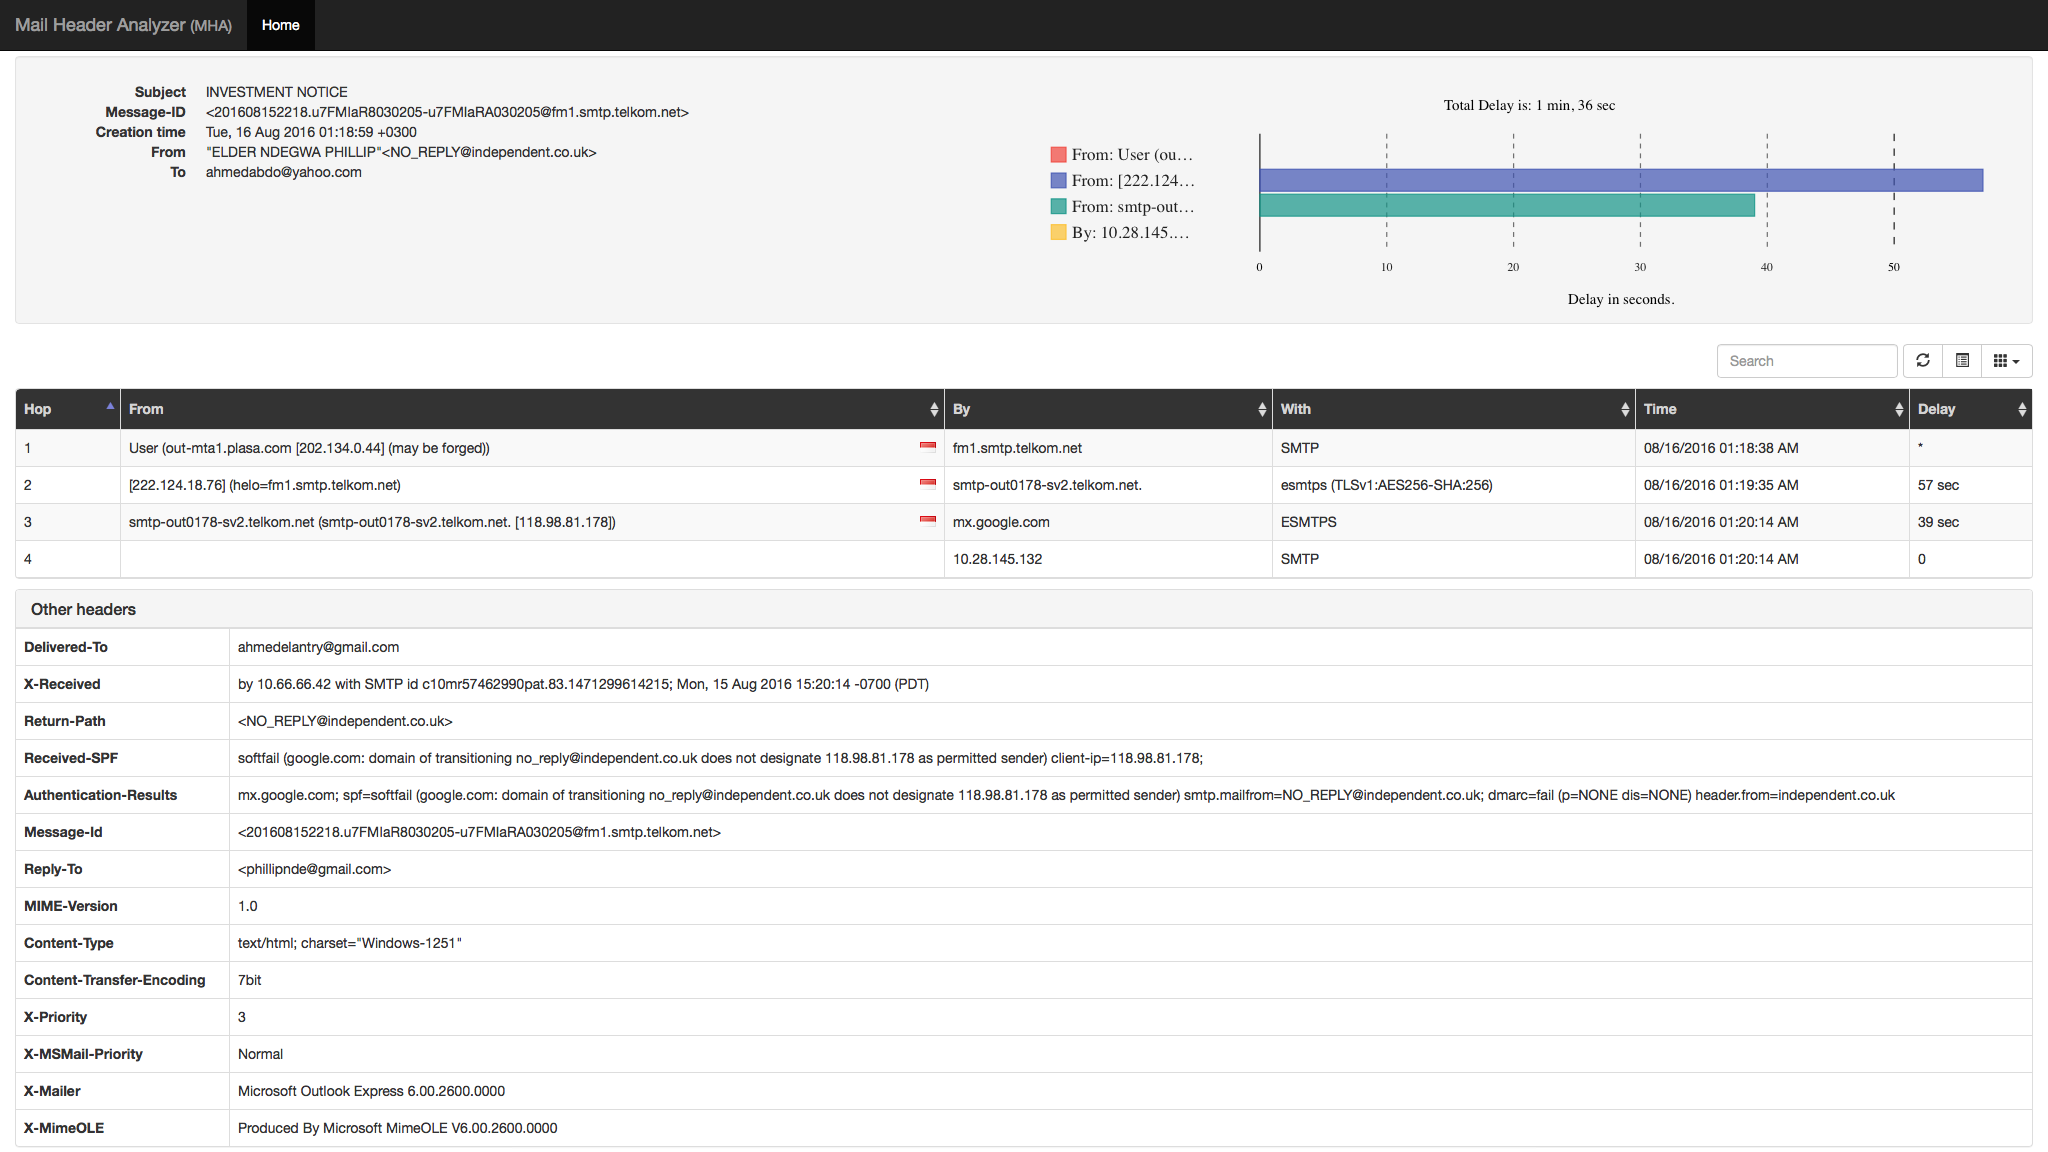 cyberdefenders/email-header-analyzer
E-Mail Header Analyzer
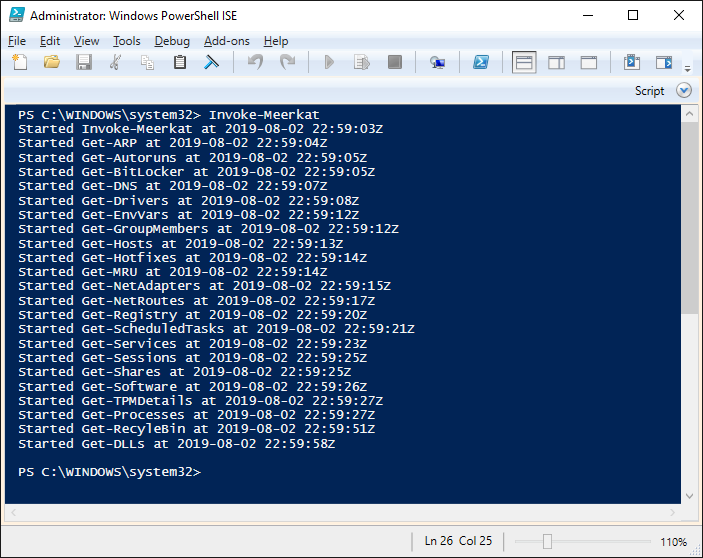 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
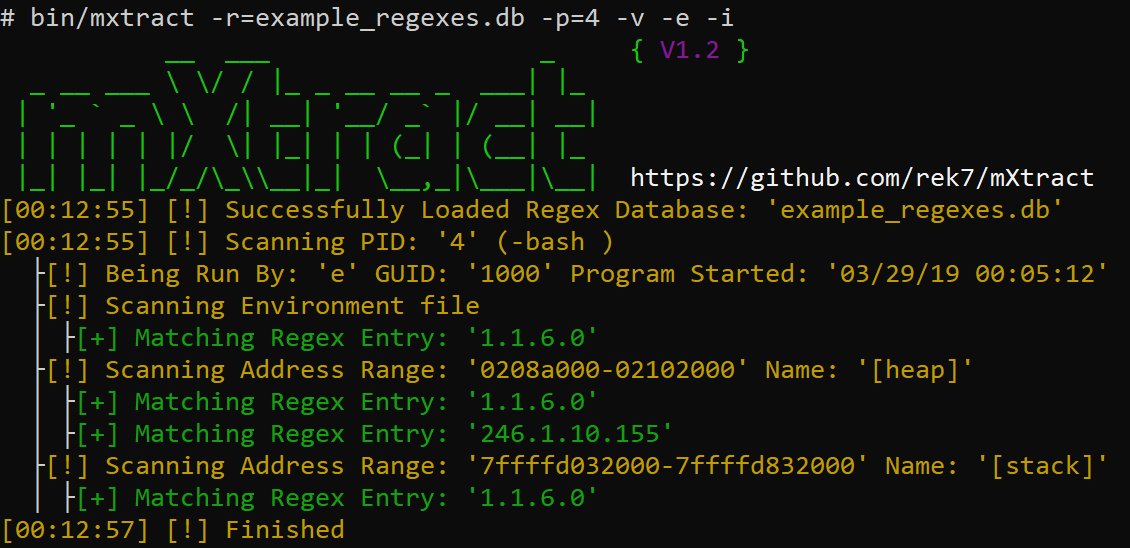 rek7/mxtract
mXtract - Memory Extractor & Analyzer
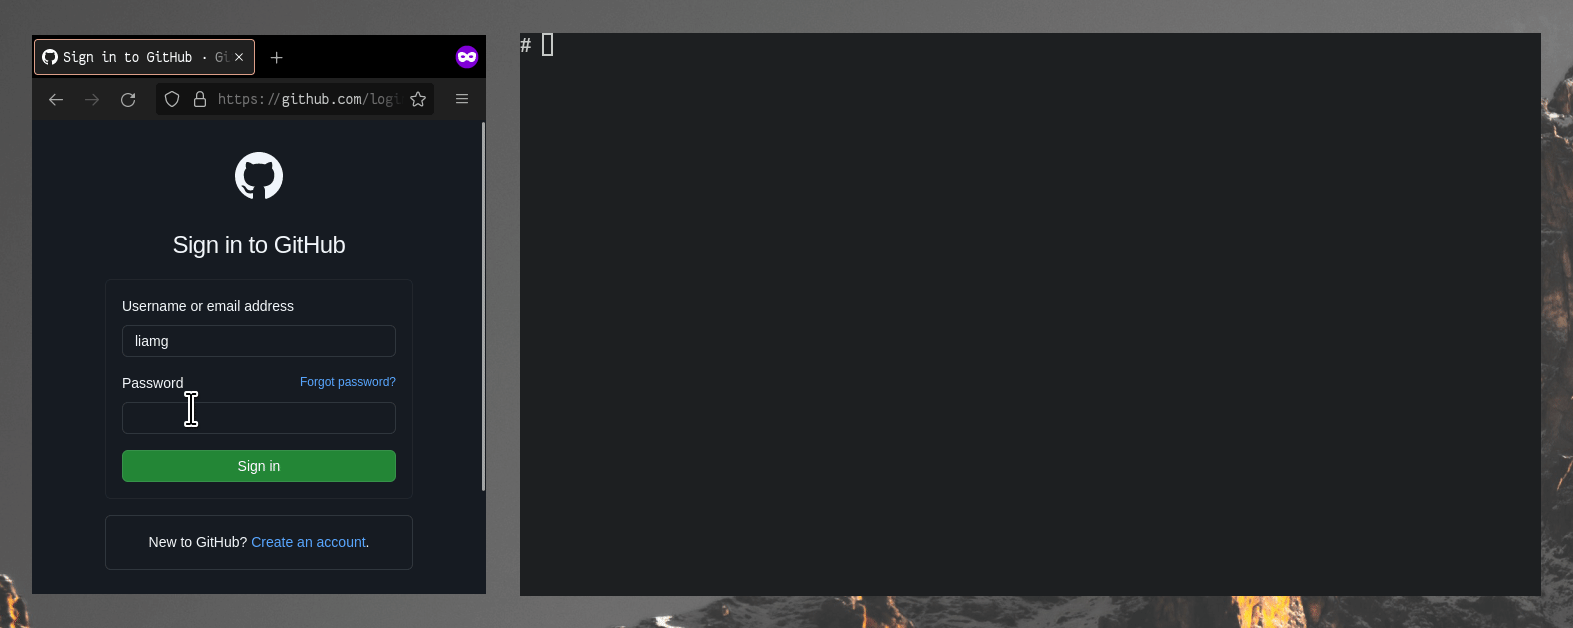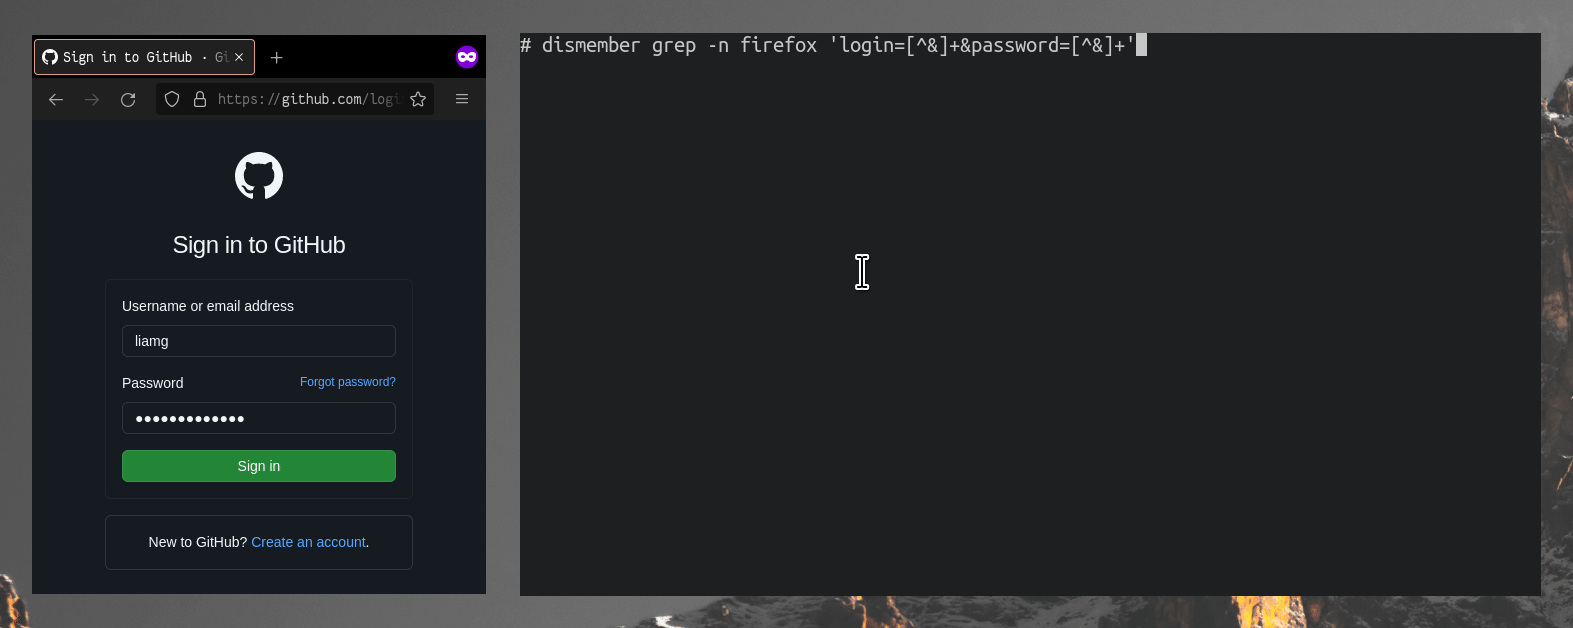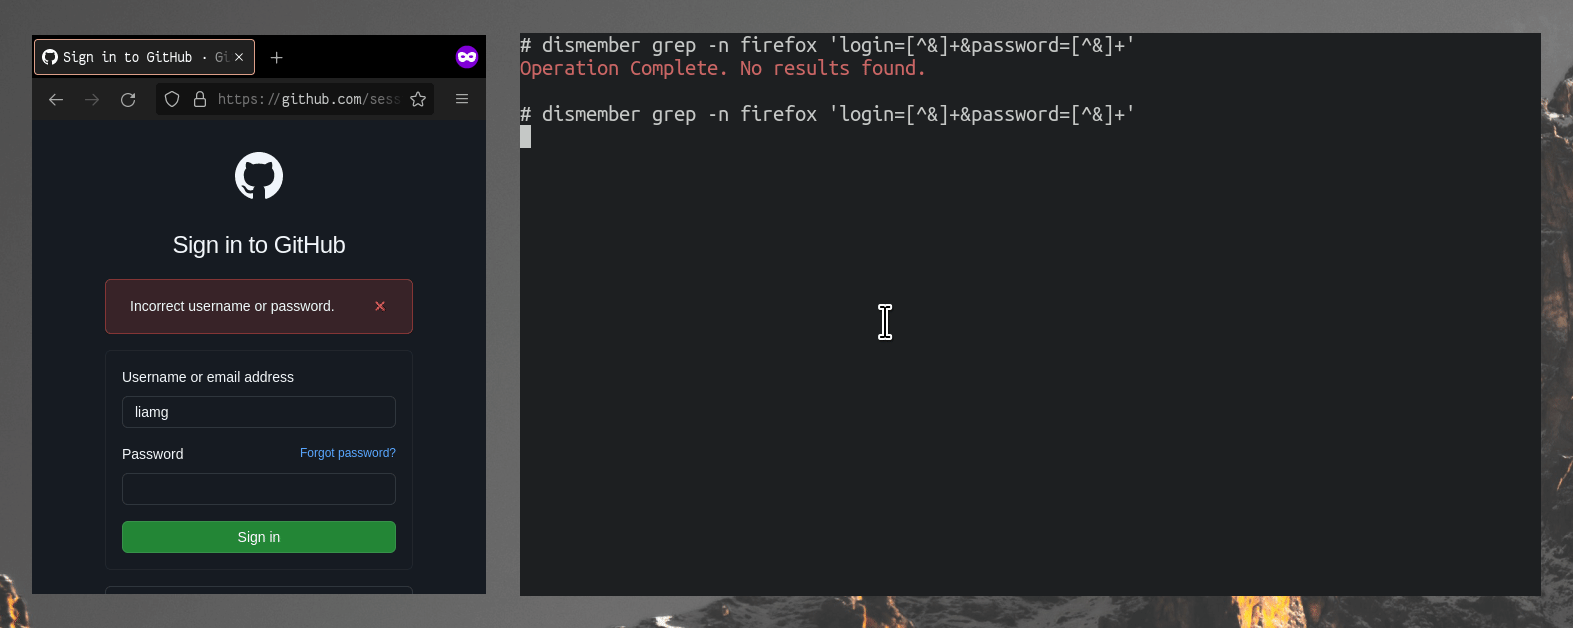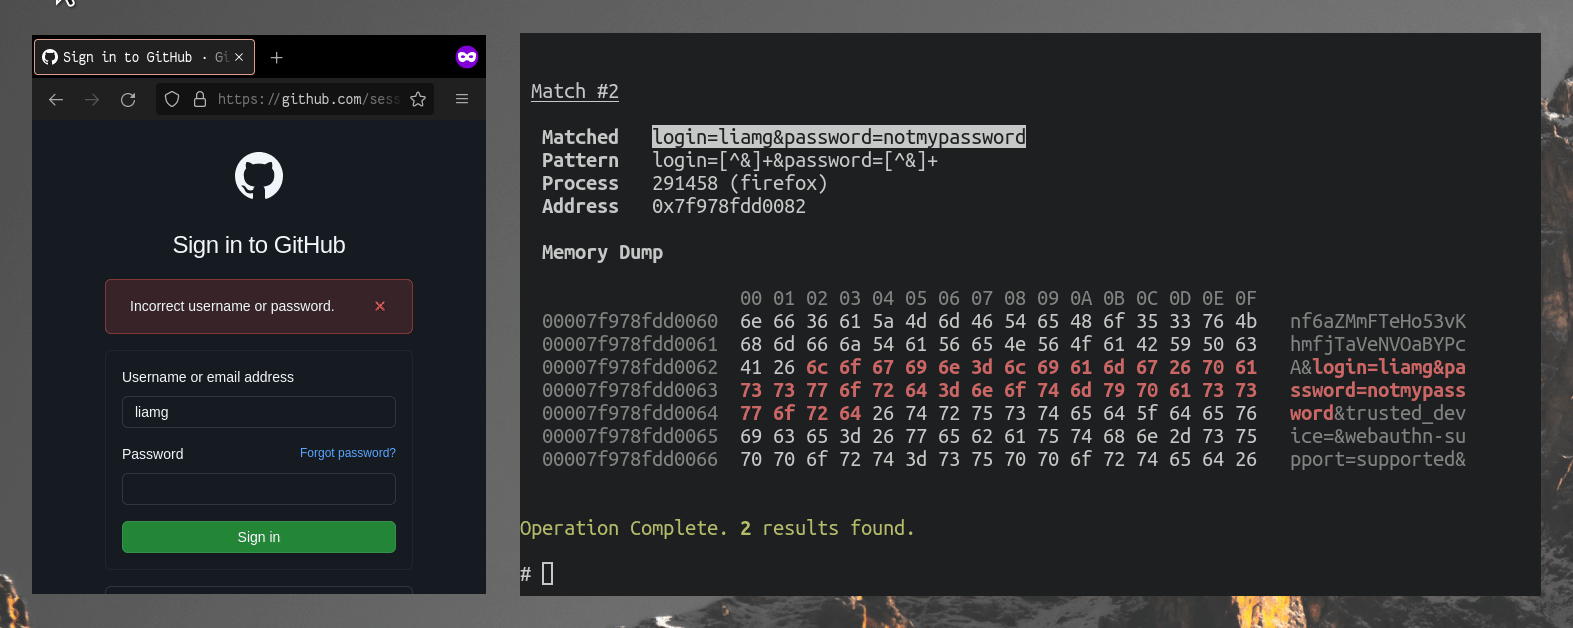 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
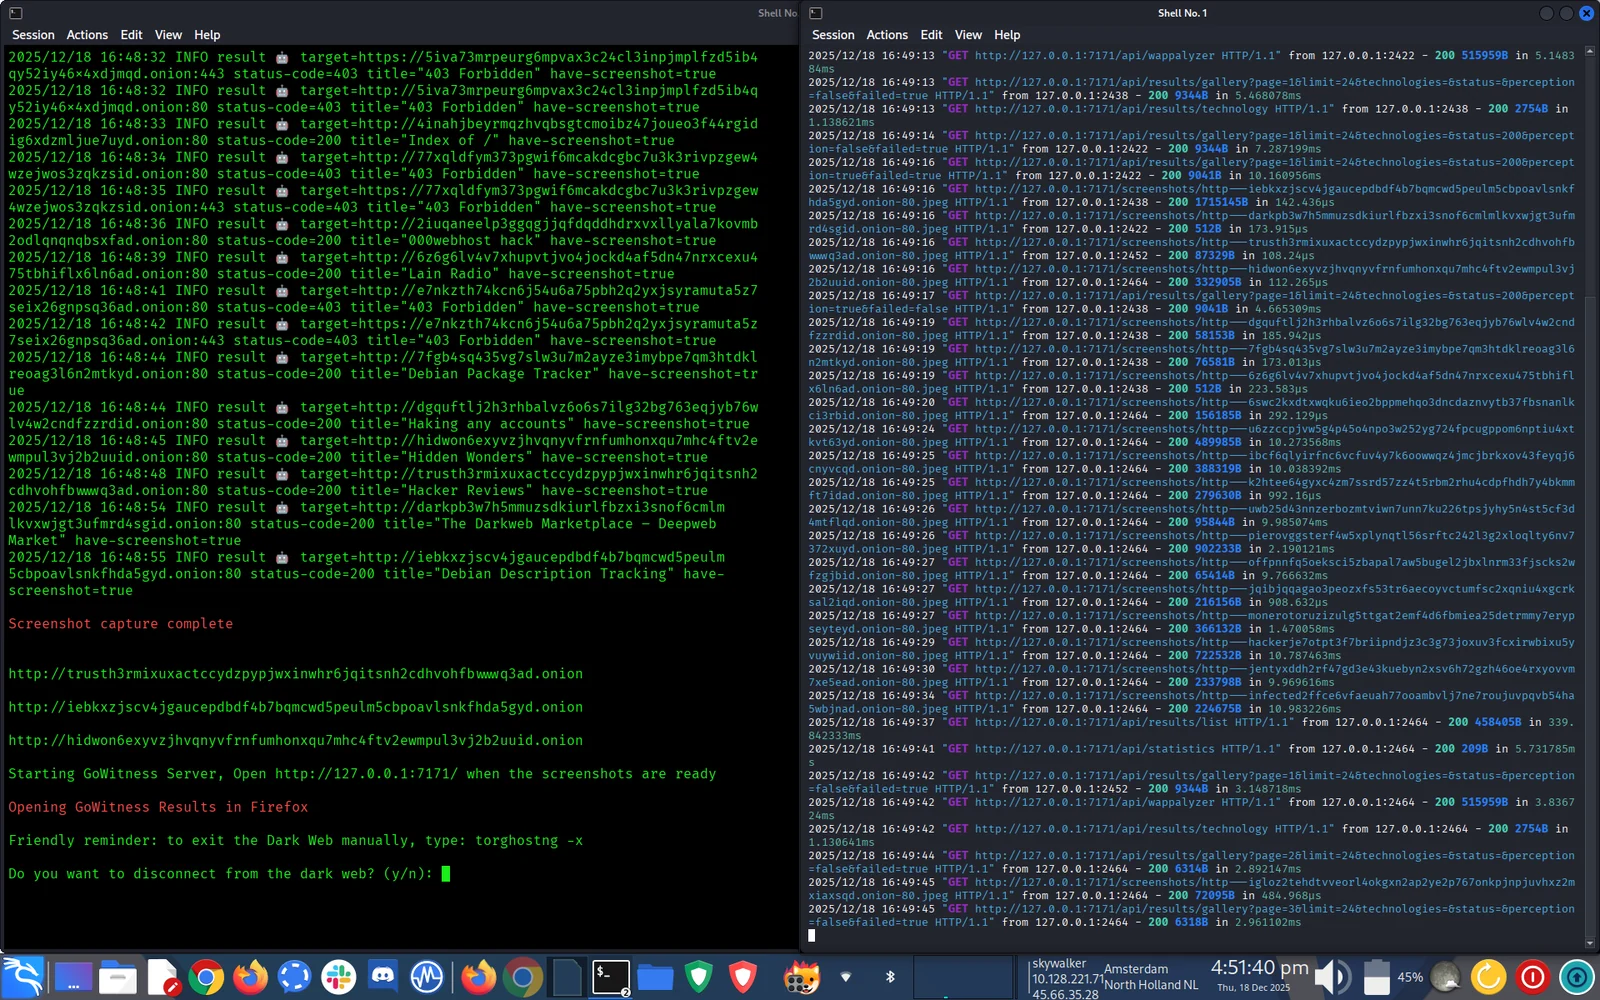 aryanguenthner/darkfox
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 guibacellar/tex
Telegram intelligence collection tool for researchers and investigators. Scrapes groups, messages, media, and user data with OCR, Elasticsearch…
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 busindre/dumpzilla
Extract all forensic interesting information of Firefox, Iceweasel and Seamonkey browsers
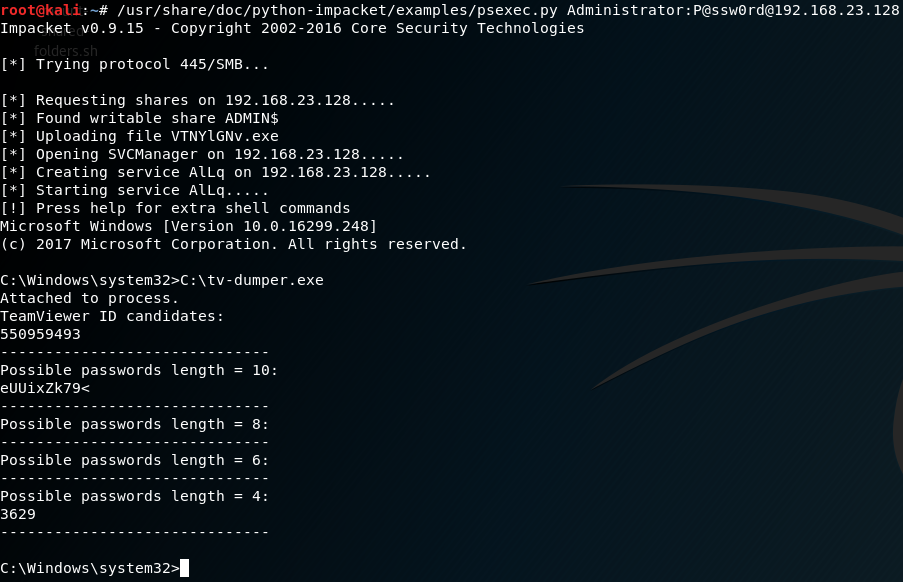 attackercan/teamviewer-dumper
Dump TeamViewer ID and password from memory. Works much better than other tools.