
Scanning
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
ctfeducationexploitation+6
aidilzlkfli/scanningAnalysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
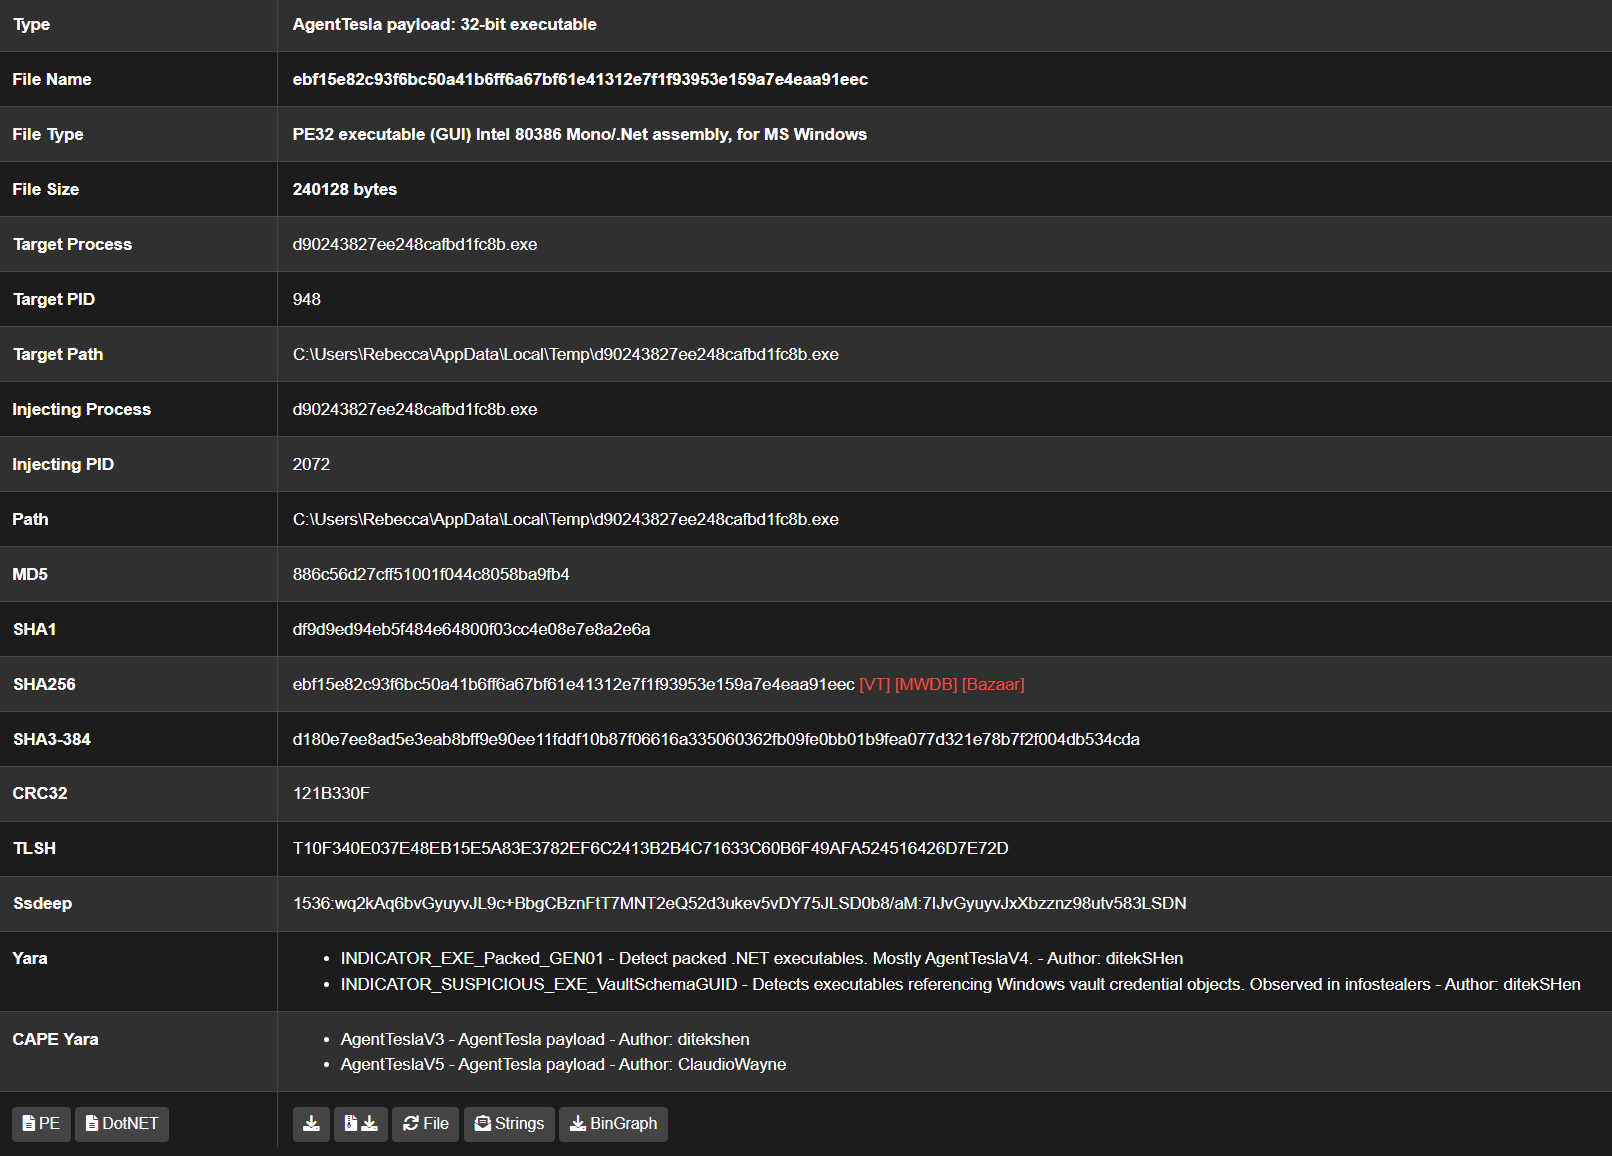 kevoreilly/capev2
Malware Configuration And Payload Extraction
 s0md3v/orbit
Blockchain Transactions Investigation Tool
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
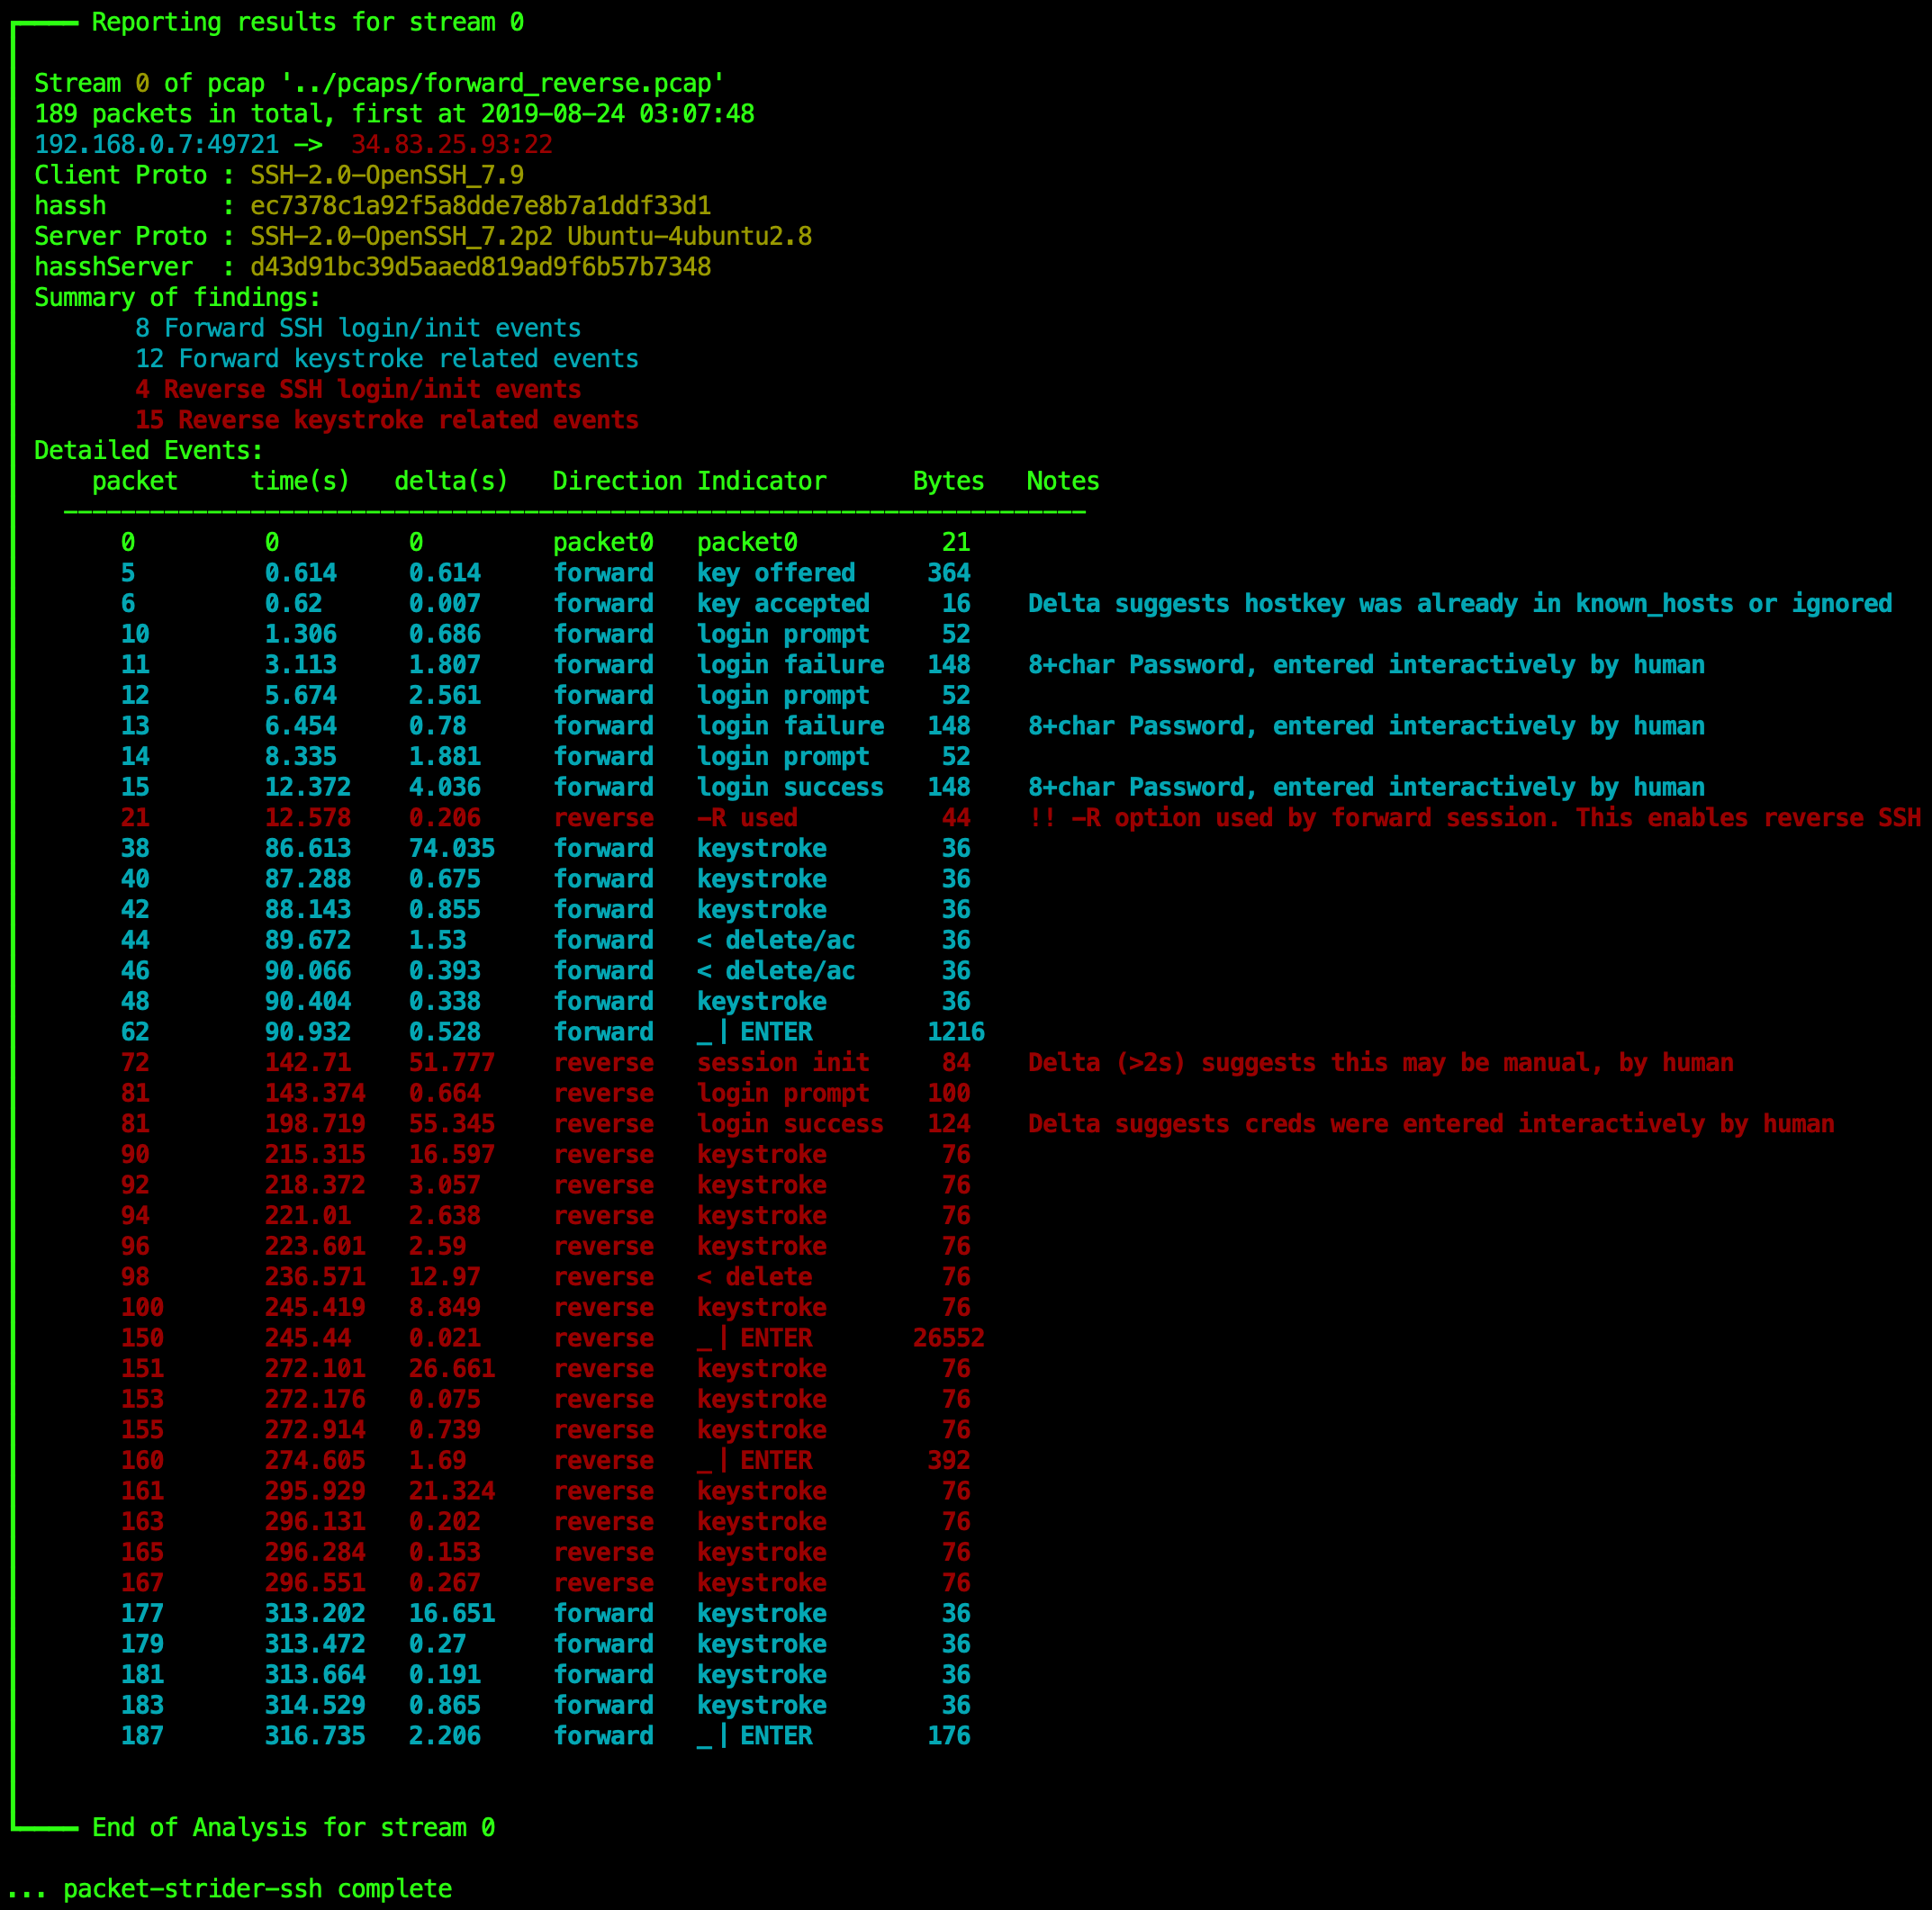 benjeems/packetstrider
A network packet forensics tool for SSH
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
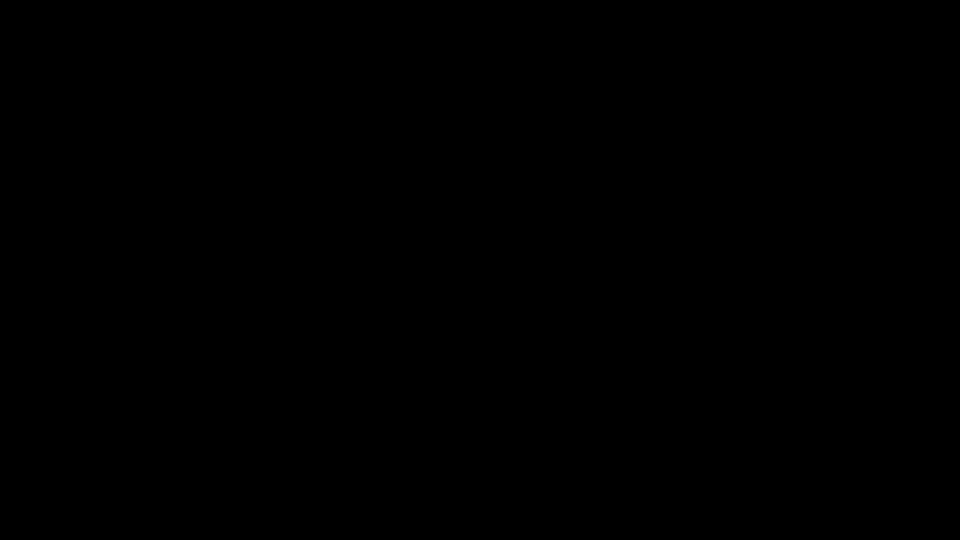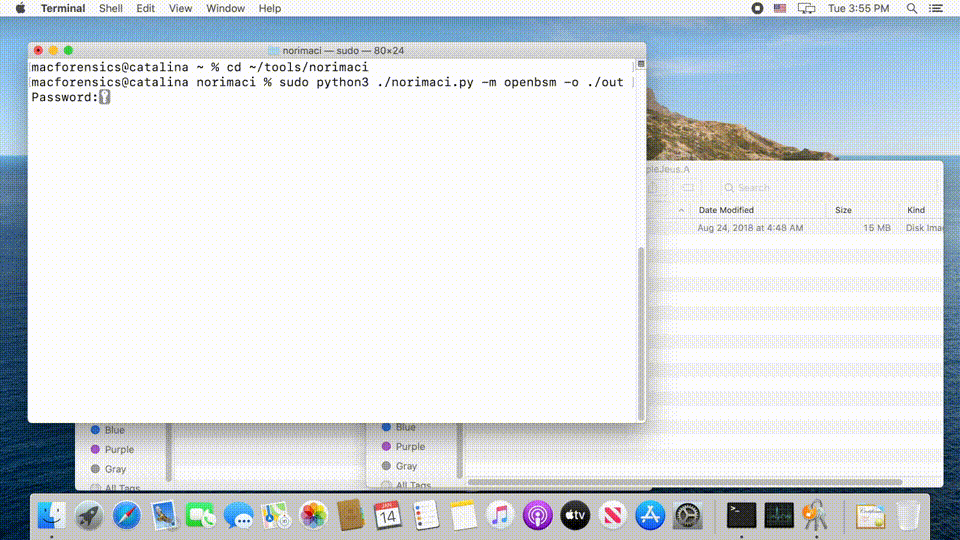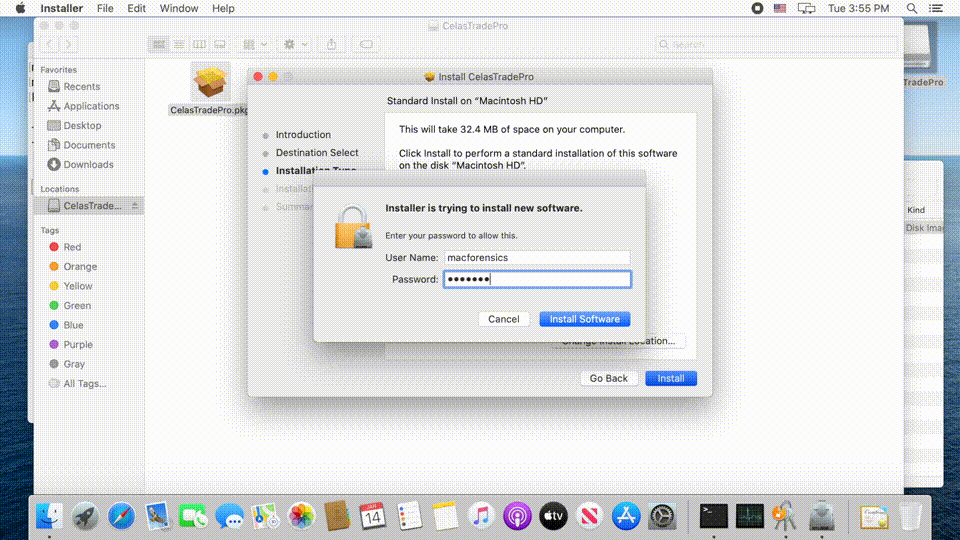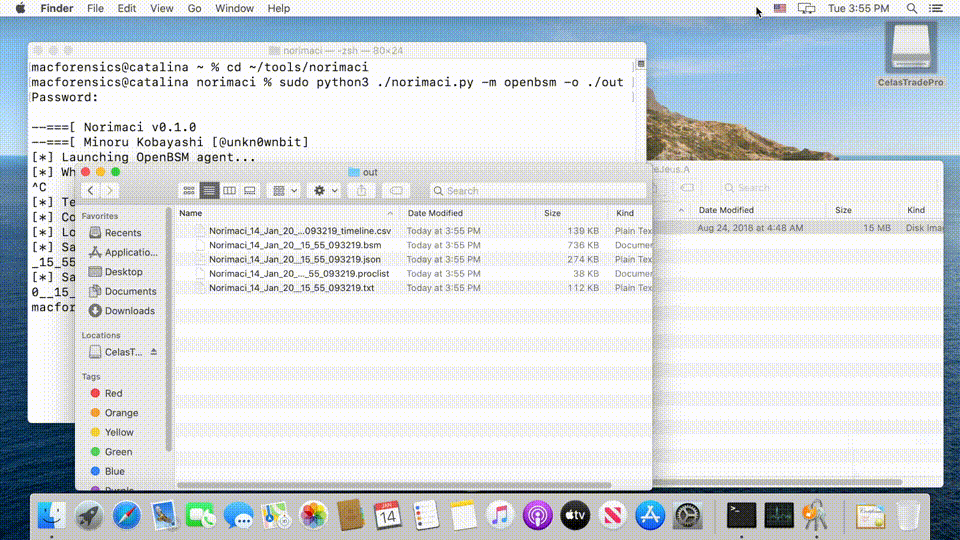 mnrkbys/norimaci
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 thomasareed/pict
Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 eciavatta/caronte
A tool to analyze the network flow during attack/defence Capture the Flag competitions
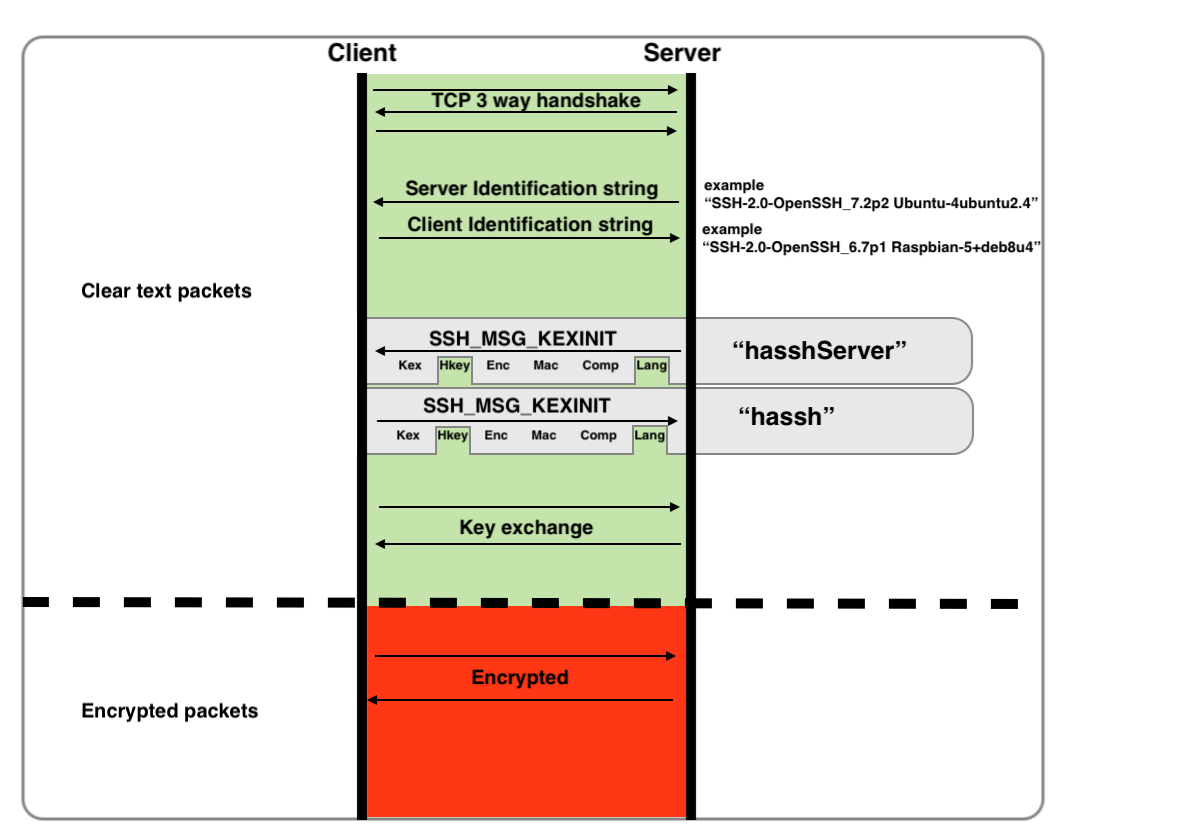 salesforce/hassh
HASSH is a network fingerprinting standard which can be used to identify specific Client and Server SSH implementations. The fingerprints can be…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 clausing/scripts
Collection of Python and Perl scripts for digital forensics, incident response, and network analysis, including hash signature tooling and packet…