

systeminformer
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
debuggersdigital-forensicsforensics+6
15.6k
winsiderss/systeminformerReal-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

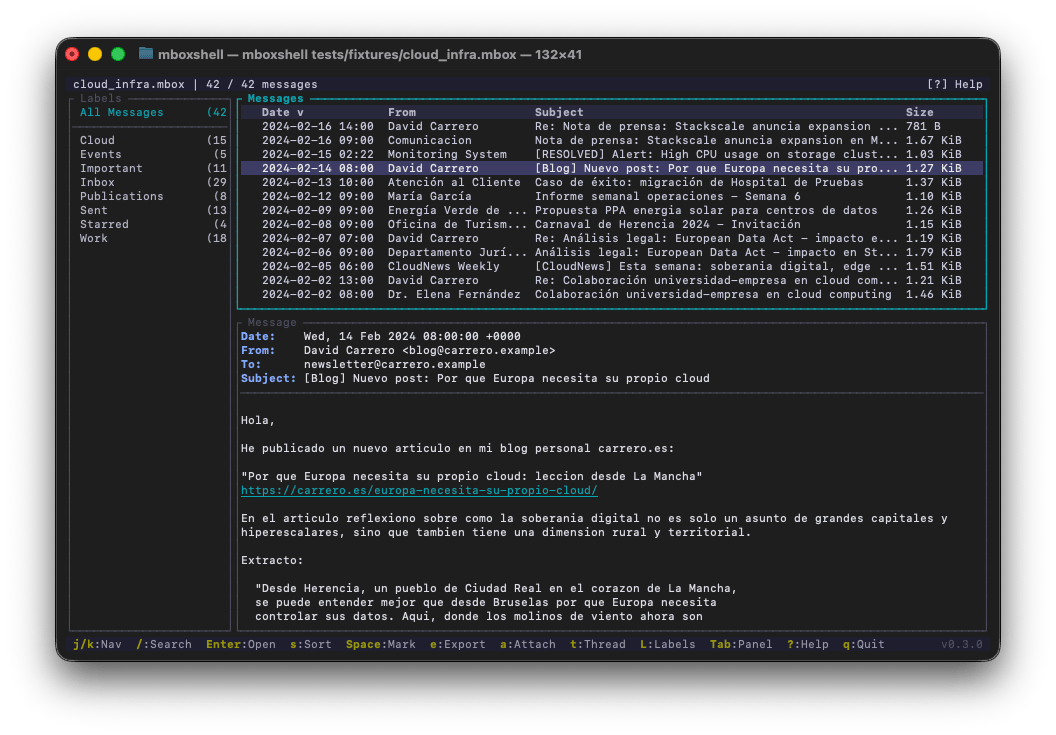 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
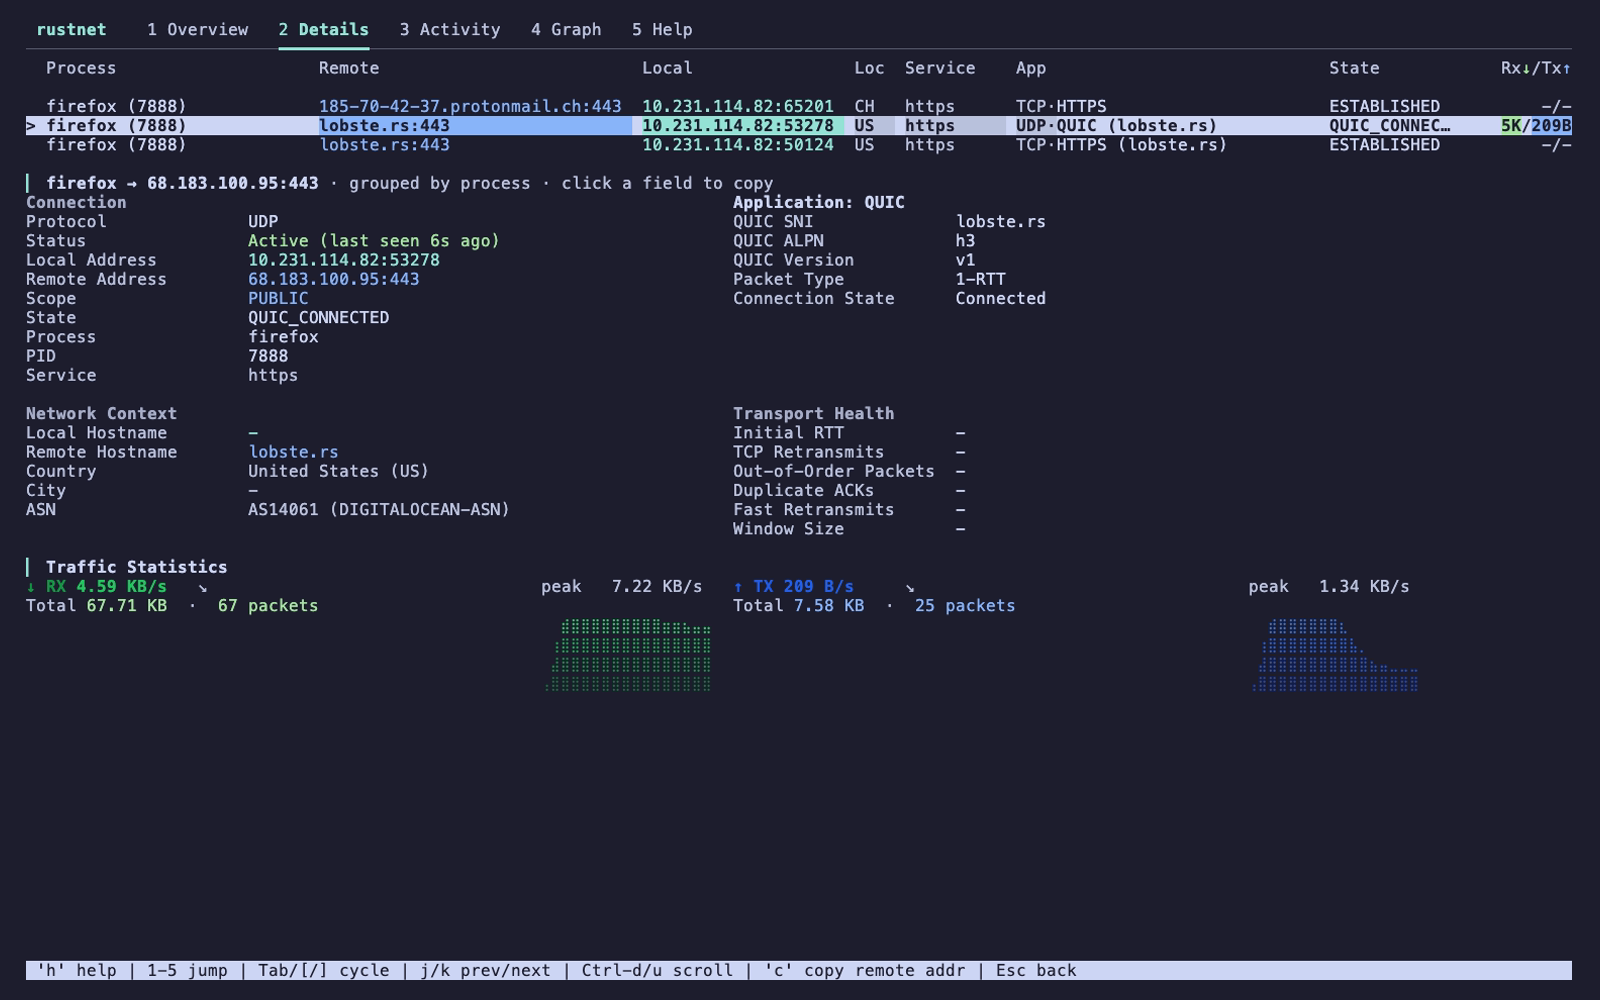 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 nextronsystems/iocs
Indicators of compromise from to analysis and research by Nextron Threat Research team
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 hasamba/dfir-companion
DFIR forensics companion server + capture extension
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…