

Wireshark
 wireshark/wireshark
Wireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.
dns-analysisforensicsnetwork-forensics+3
1.6k
wireshark/wiresharkWireshark's official code repository. You can keep the releases coming by donating at https://wiresharkfoundation.org/donate/.

 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
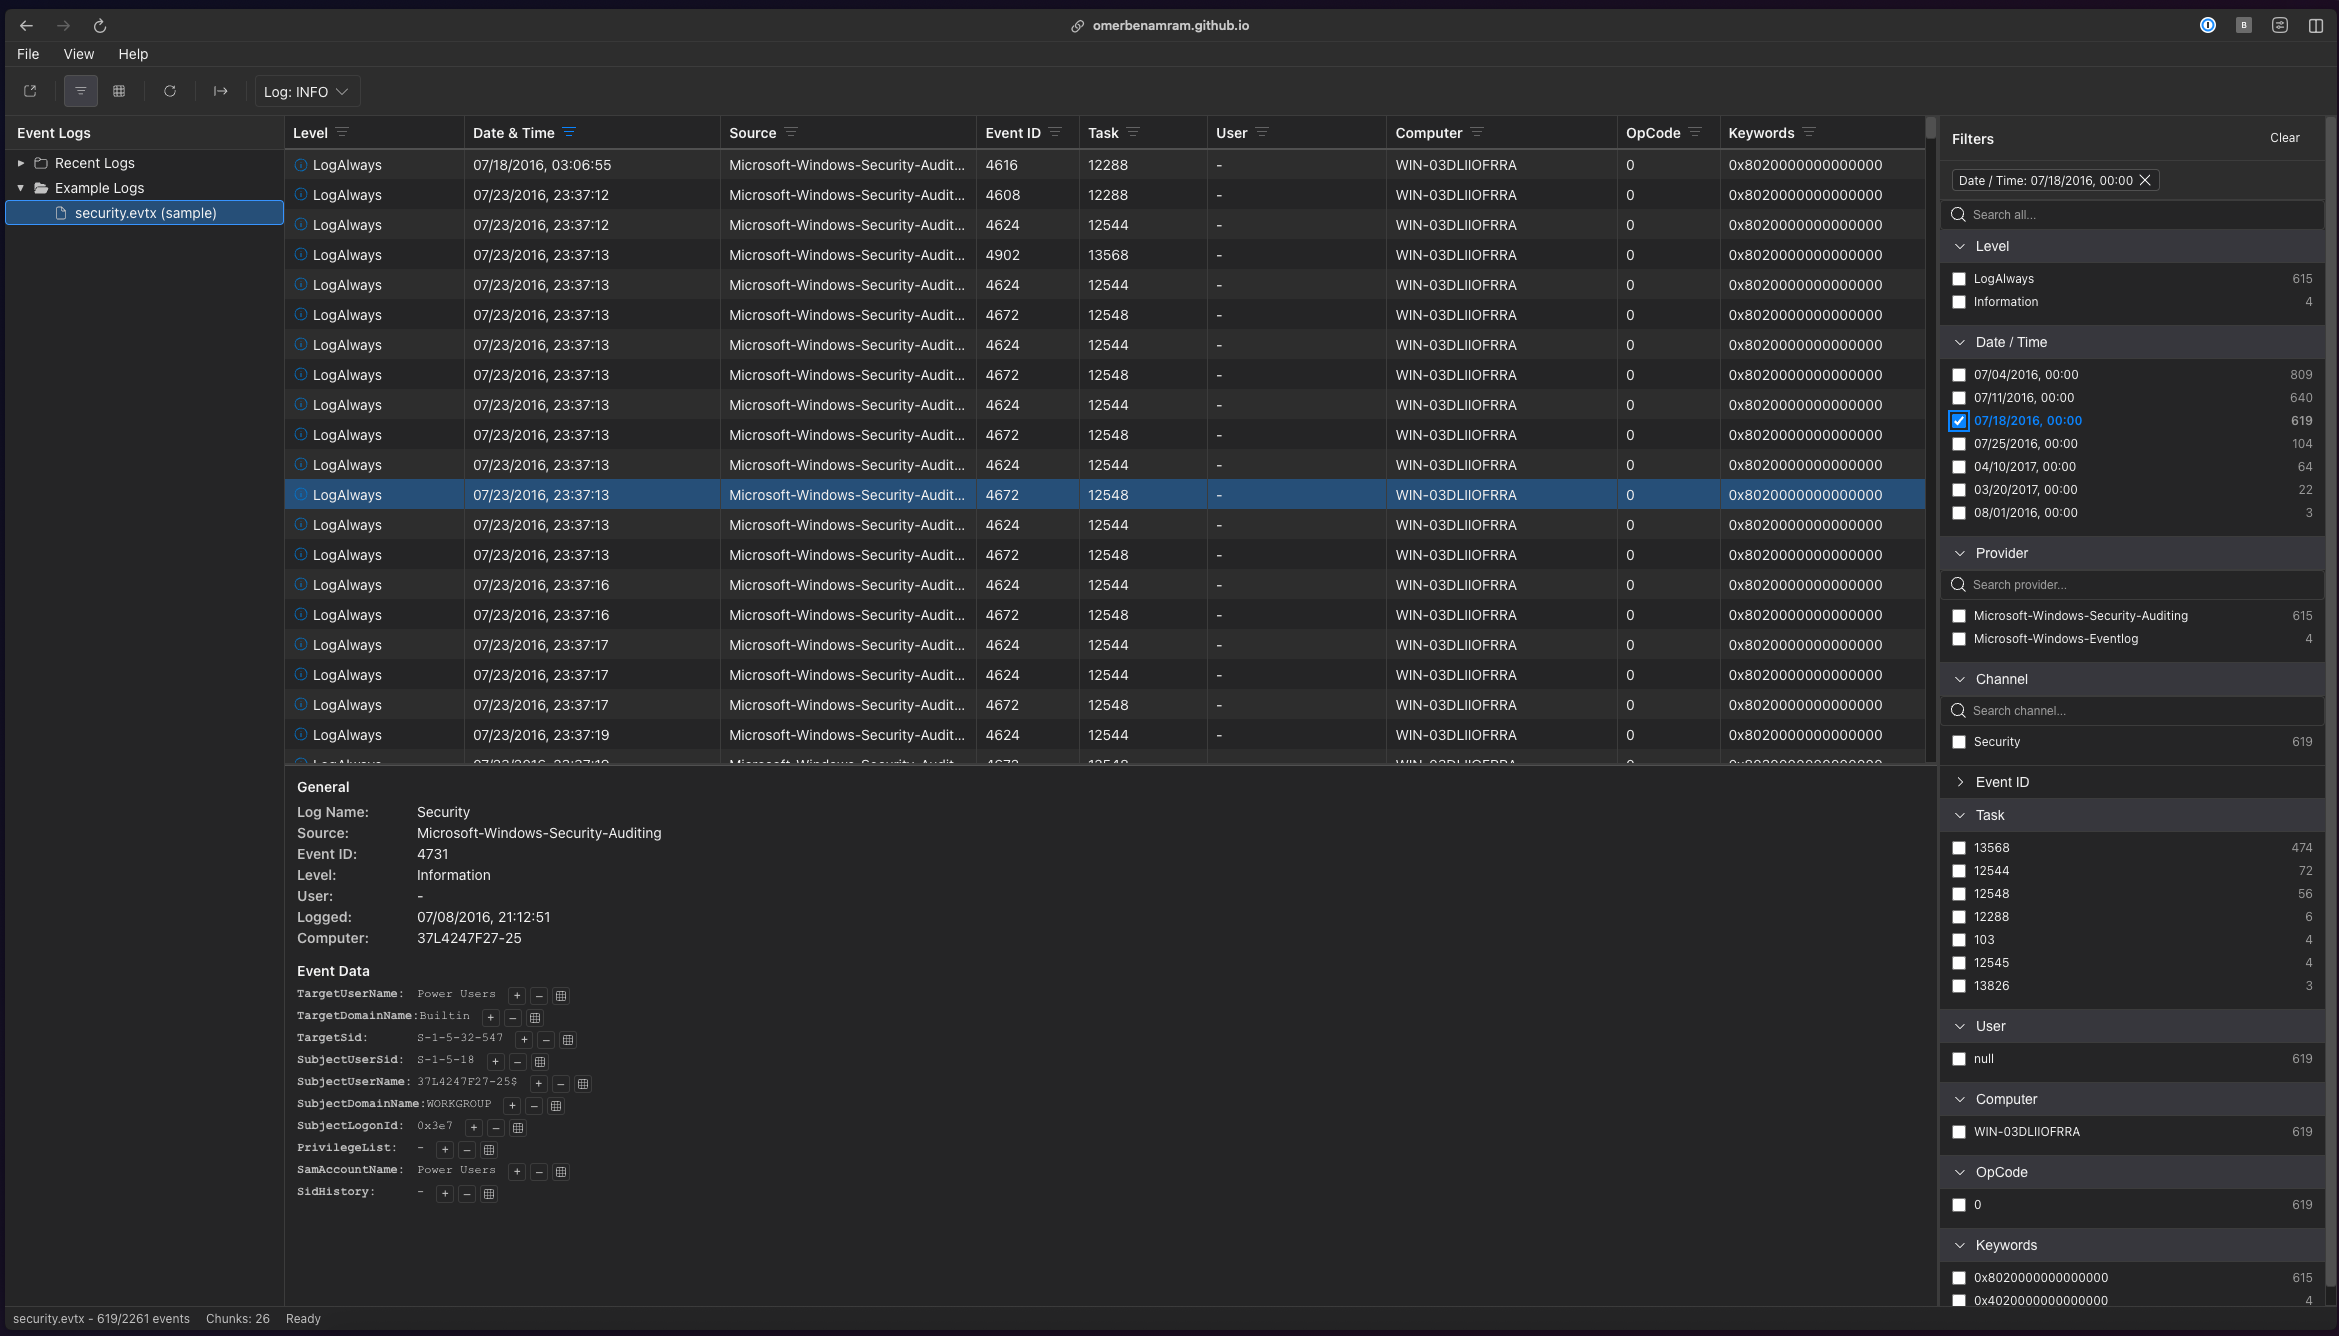 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
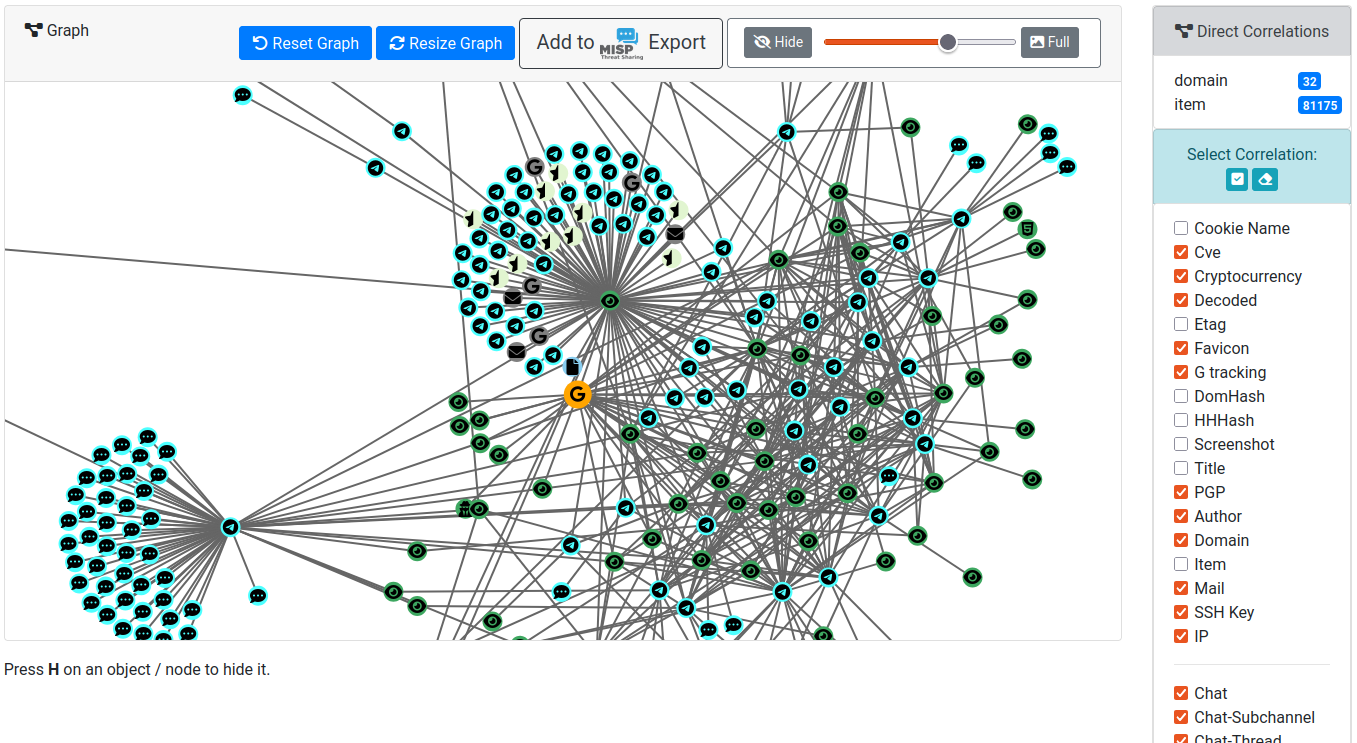 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
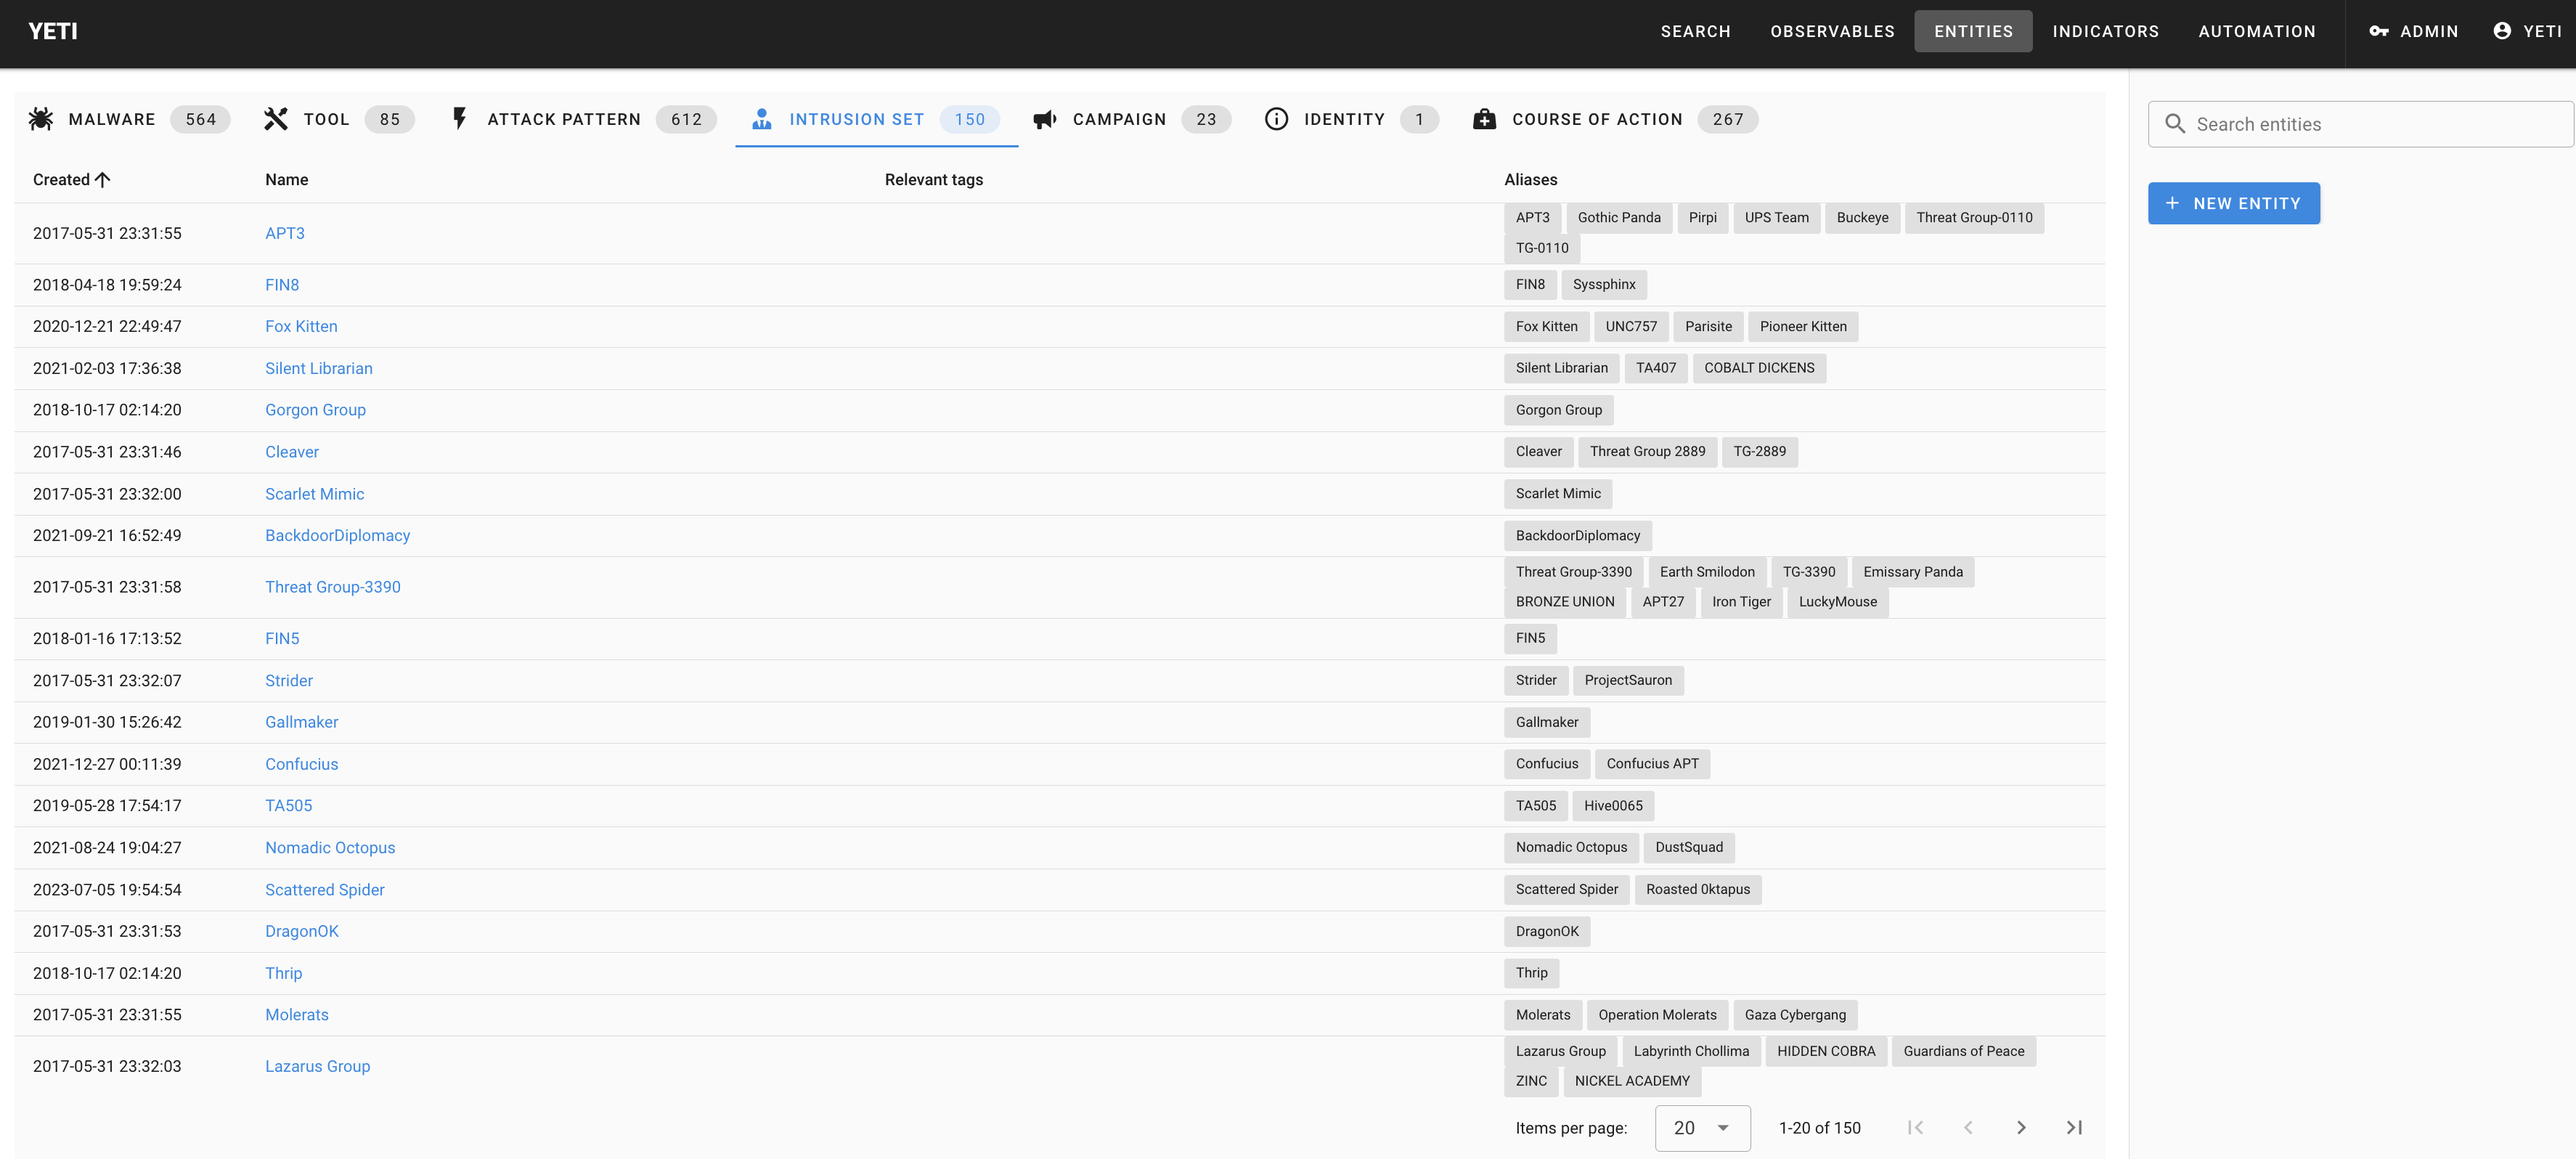

 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…