
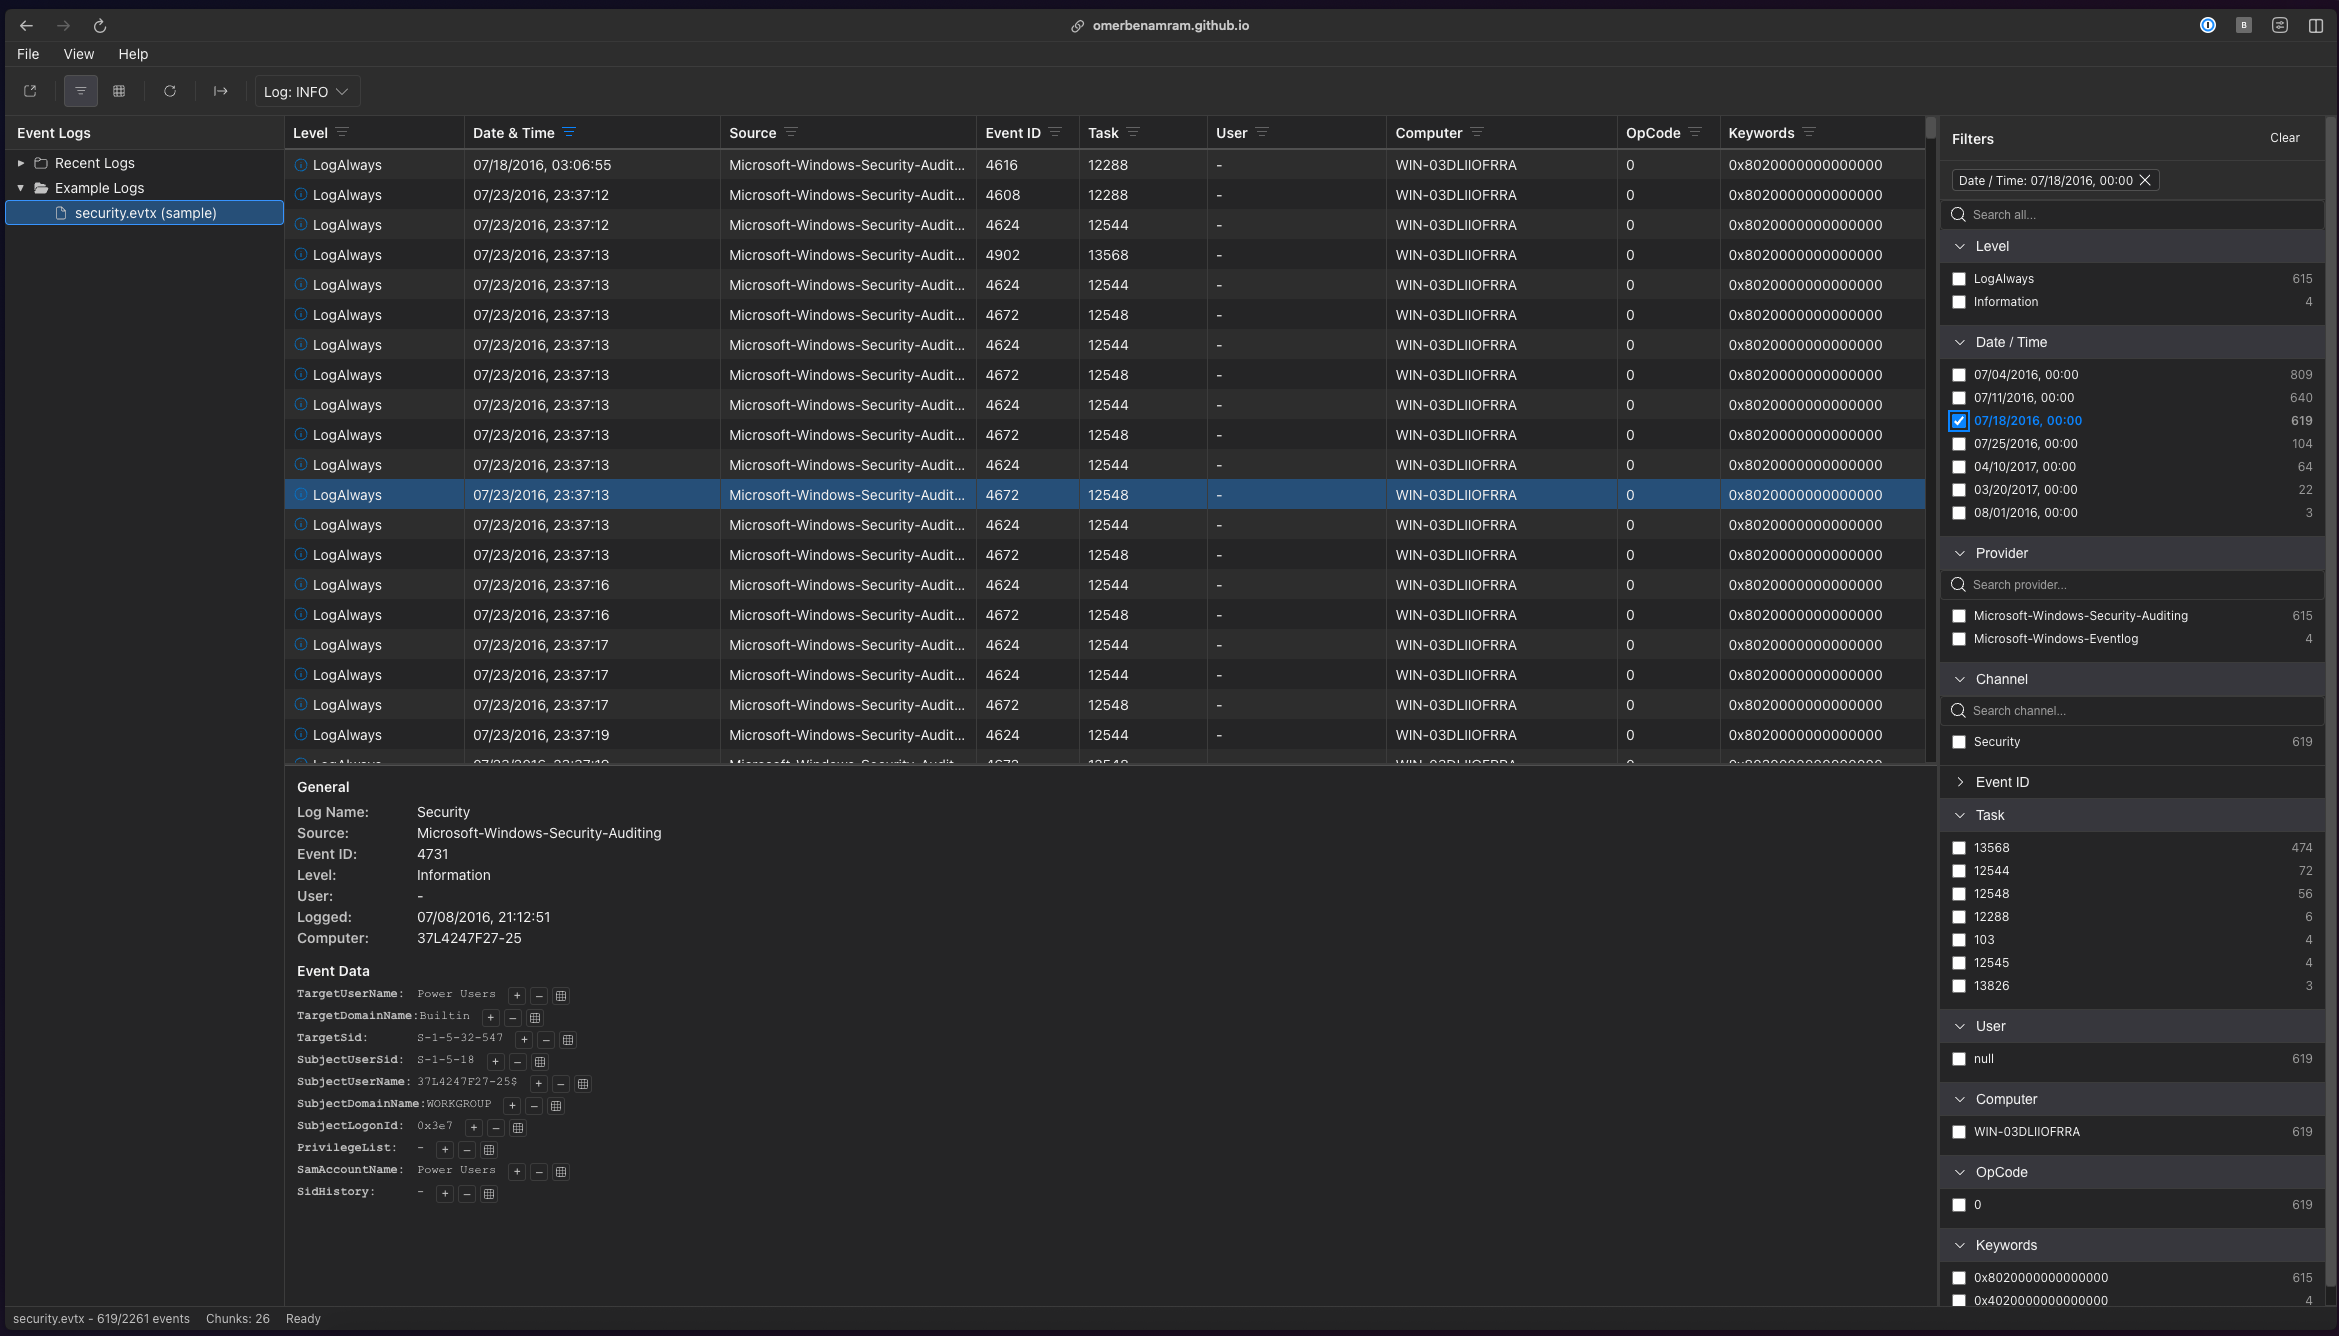
evtx
 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
digital-forensicsforensicsincident-response+1
omerbenamram/evtxA Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
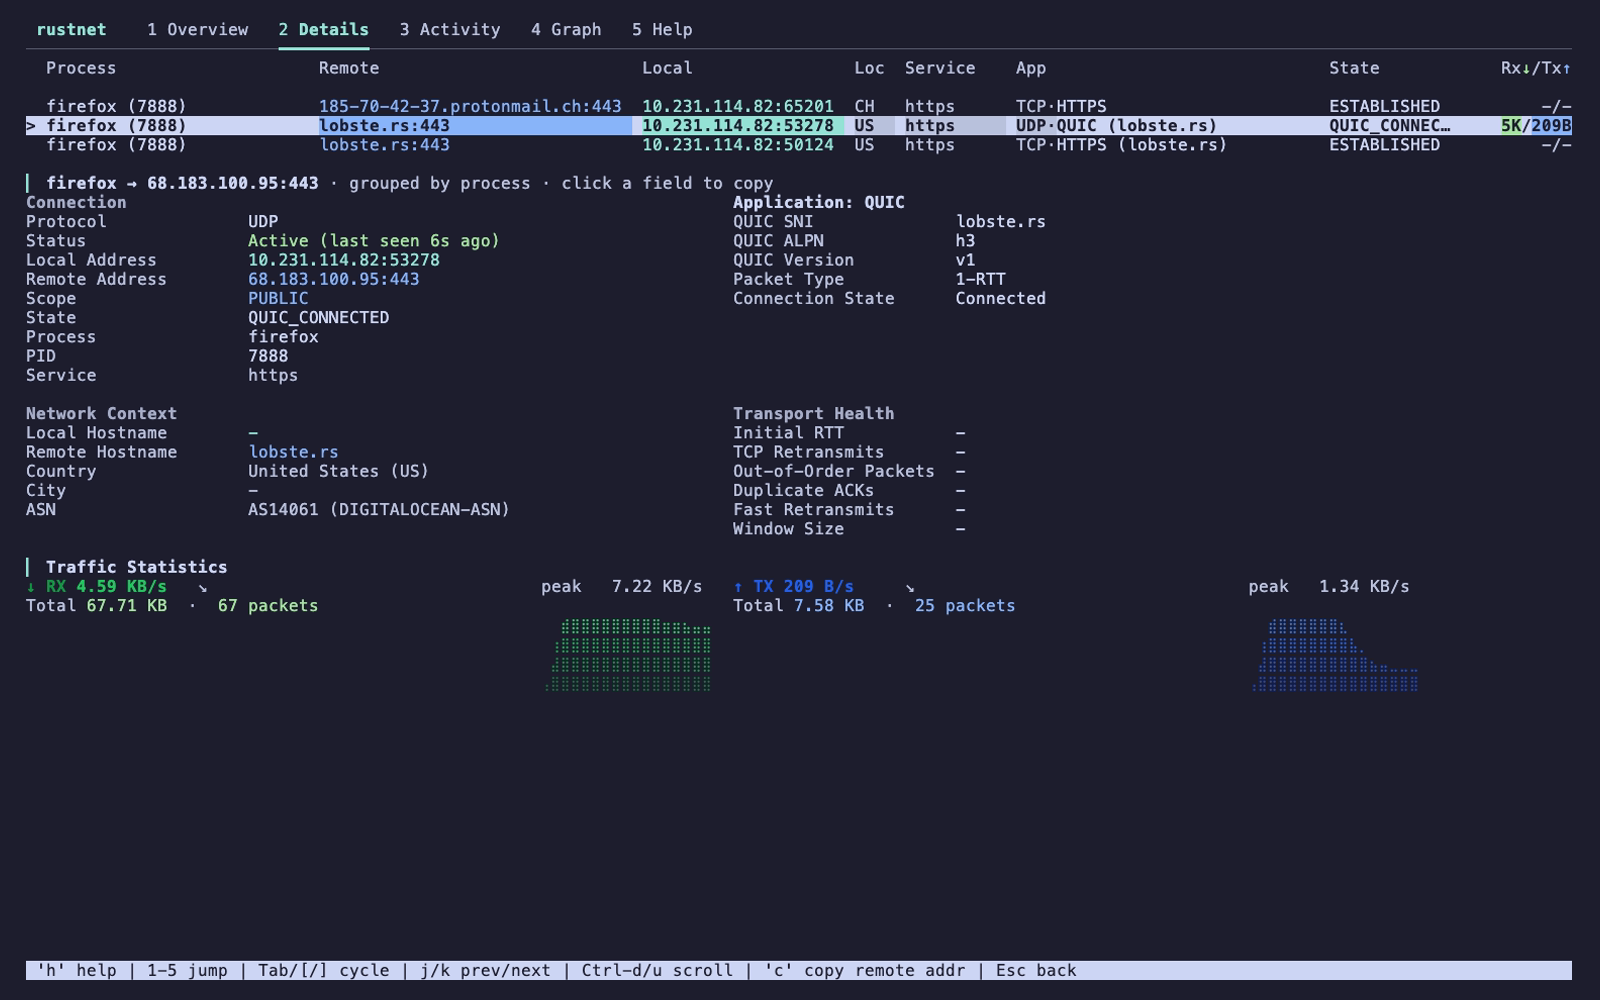 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research
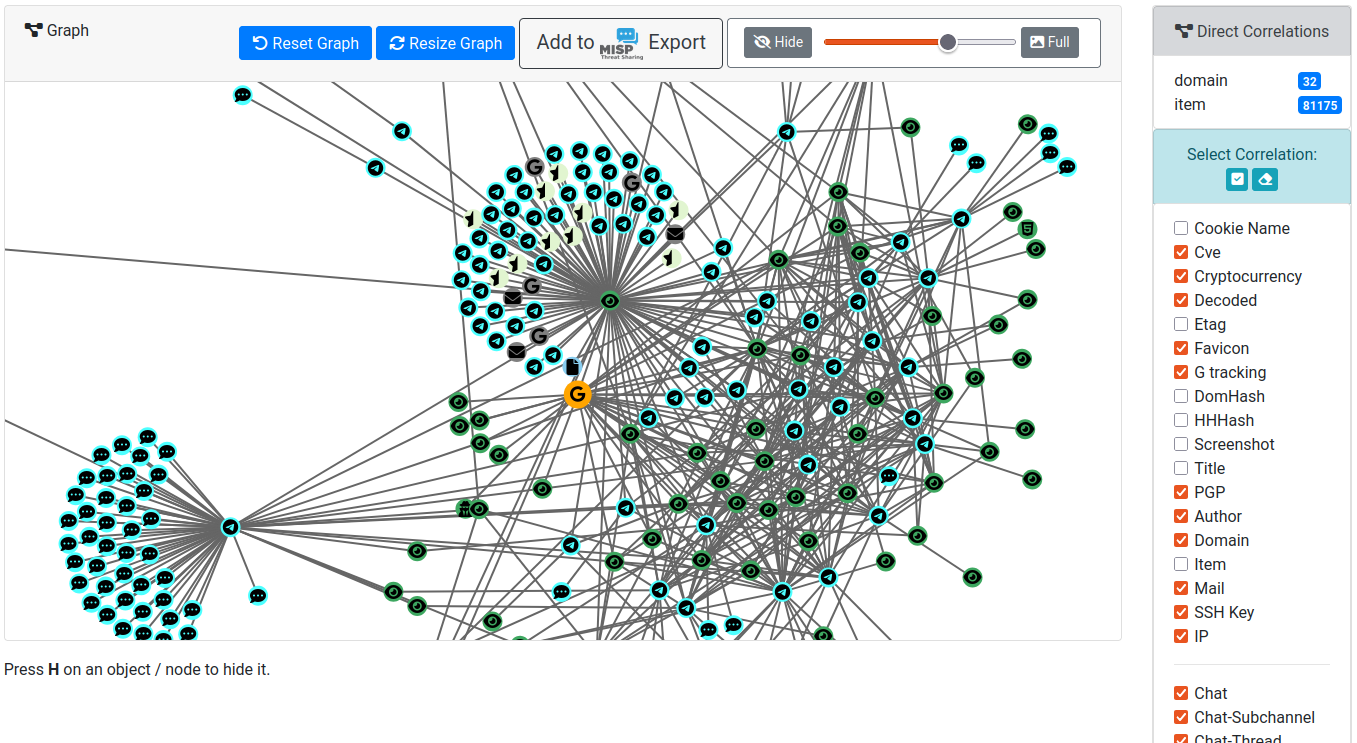 circl/ail-framework
AIL framework - Analysis Information Leak framework. Project moved to https://github.com/ail-project
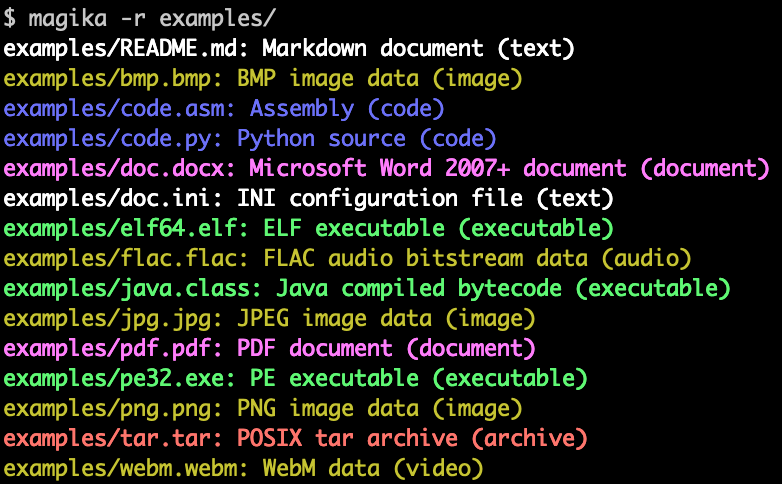 google/magika
Fast and accurate AI powered file content types detection
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 onekey-sec/unblob
Extract files from any kind of container formats
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
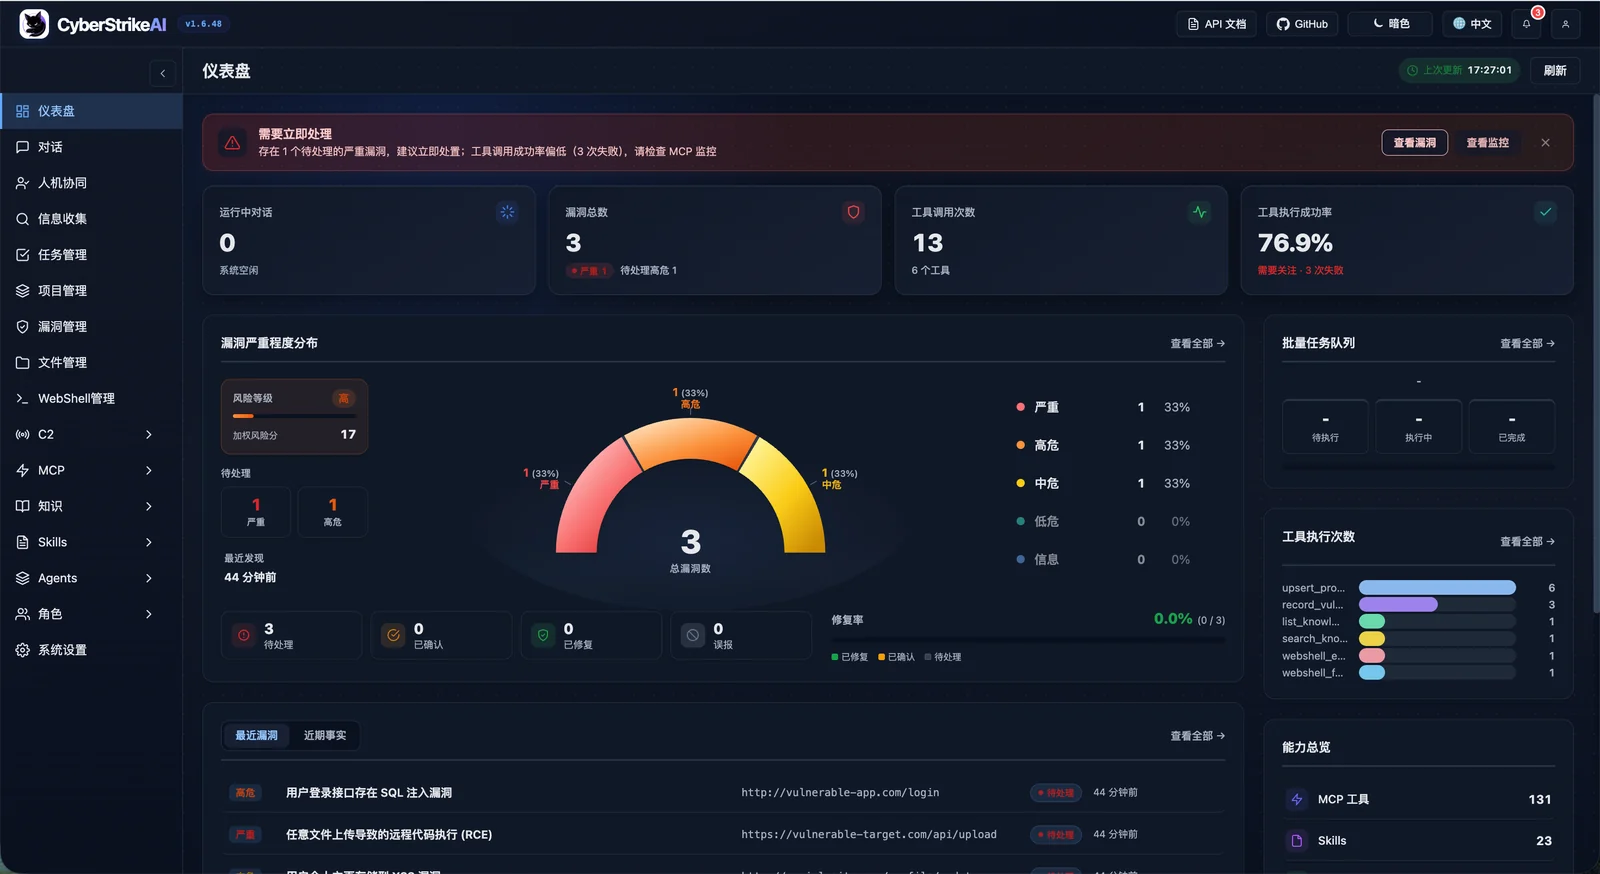 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
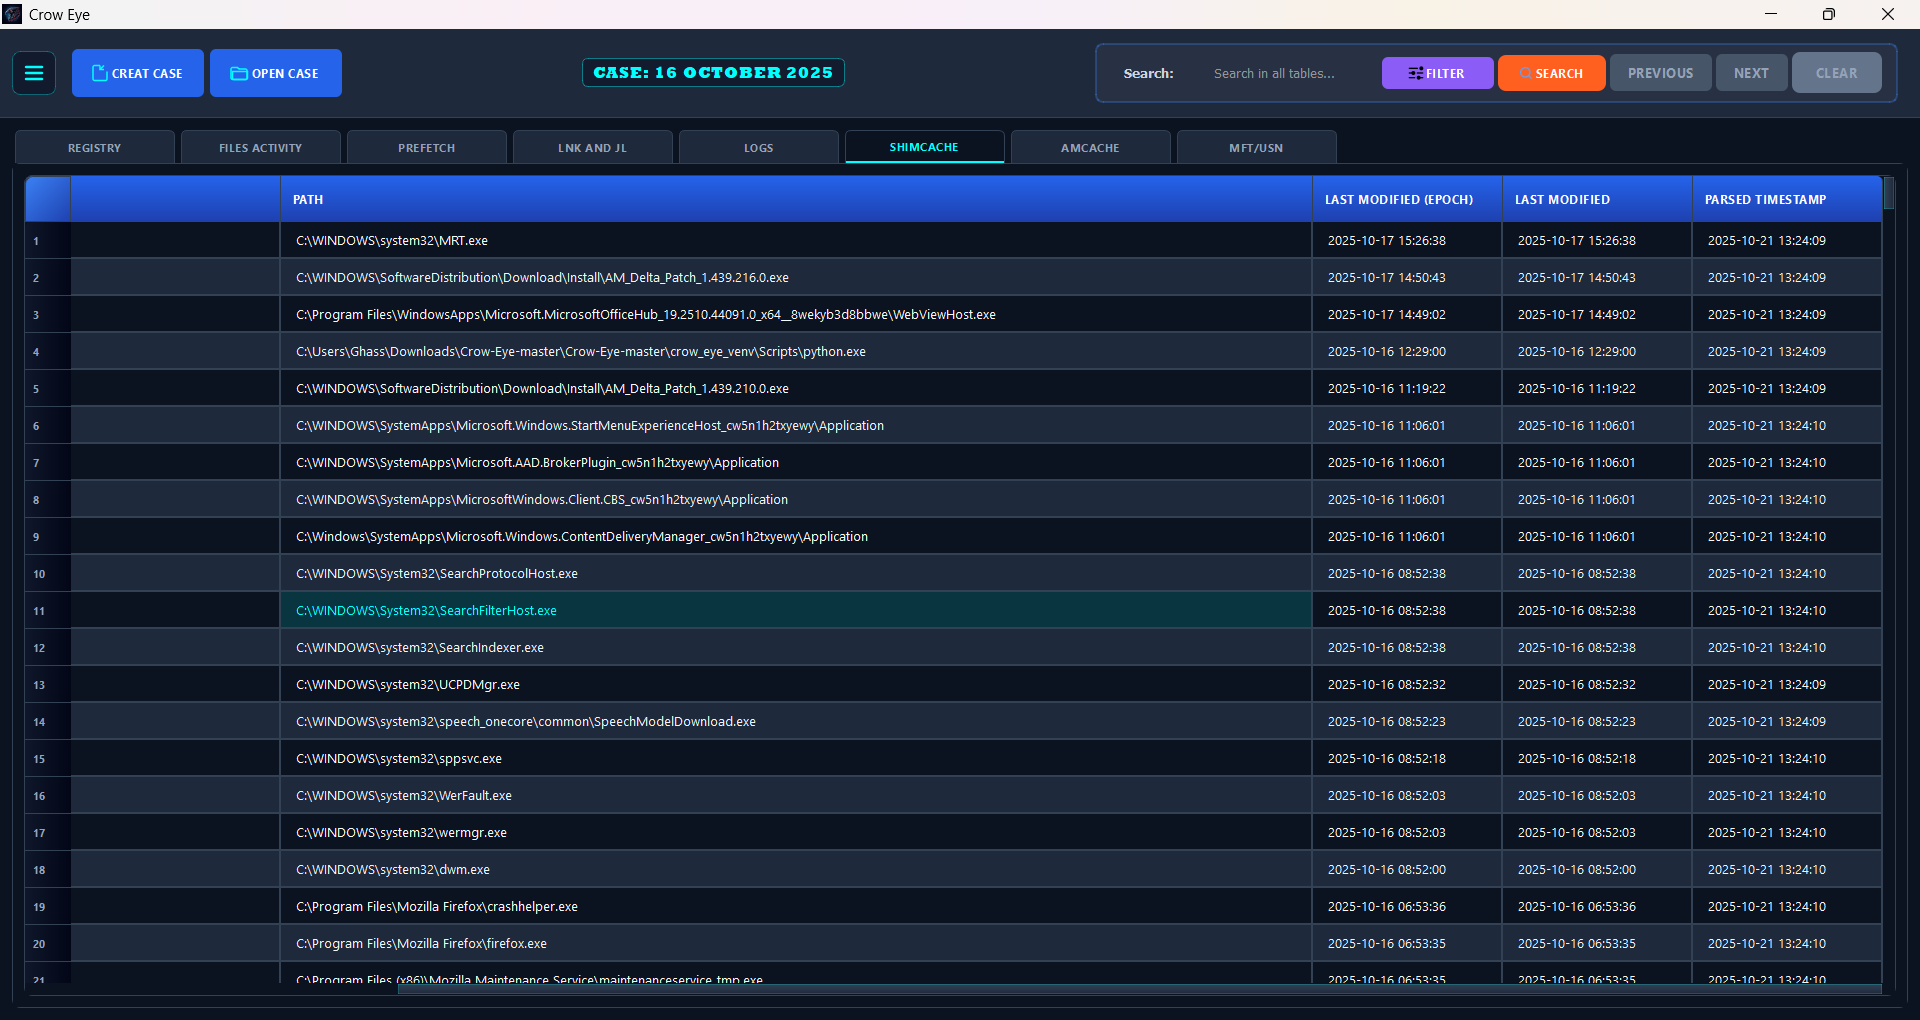 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
 winsiderss/systeminformer
Real-time Windows system monitor with advanced process, network, and disk analysis, stack trace debugging, malware detection, and service management.…
 tjnel/certgraveyard_yara
Automated YARA rule generation from the Cert Central compromised certificate database.
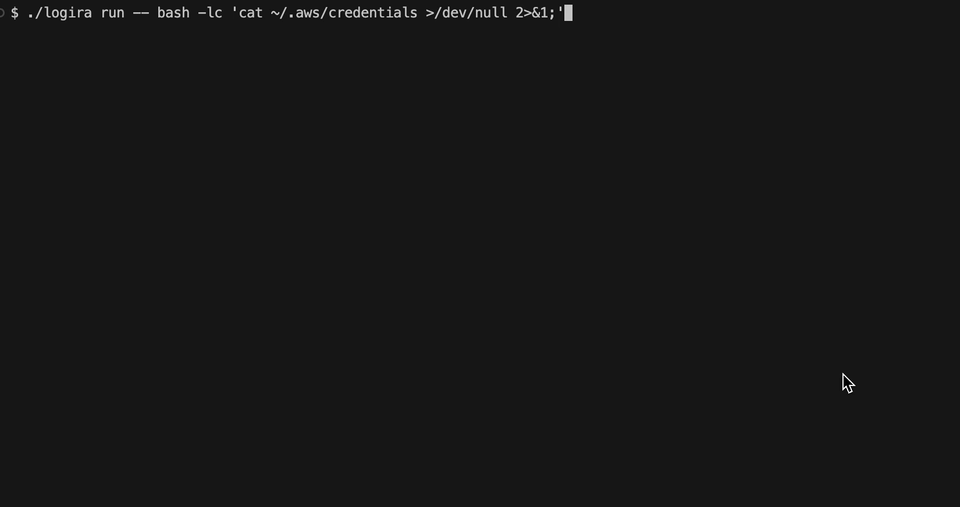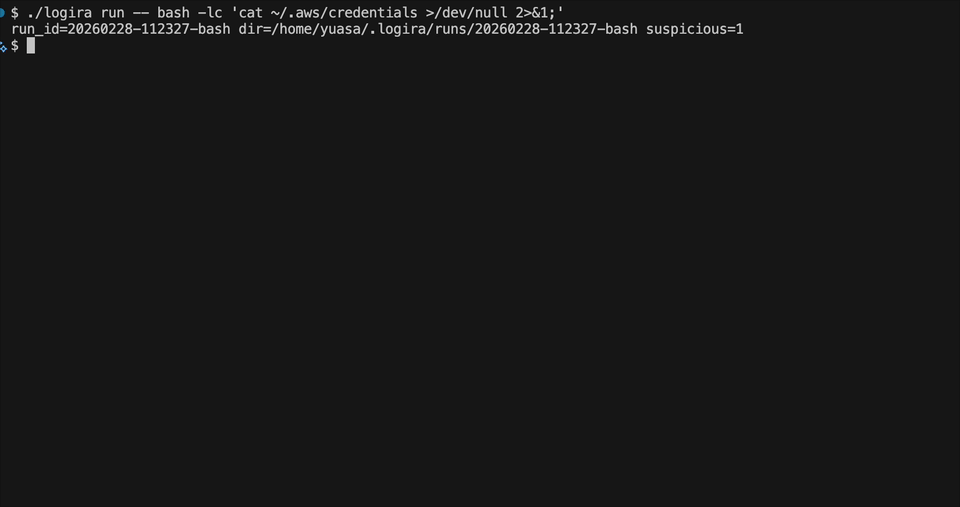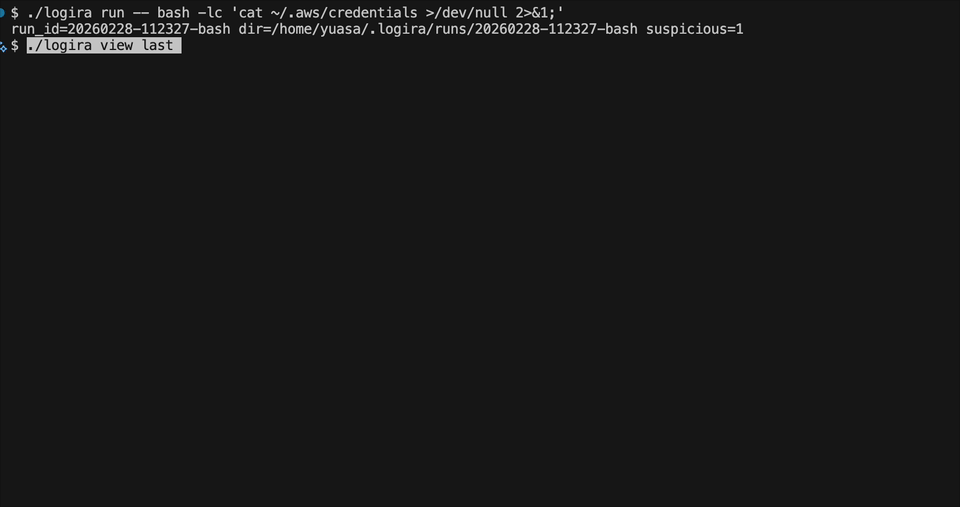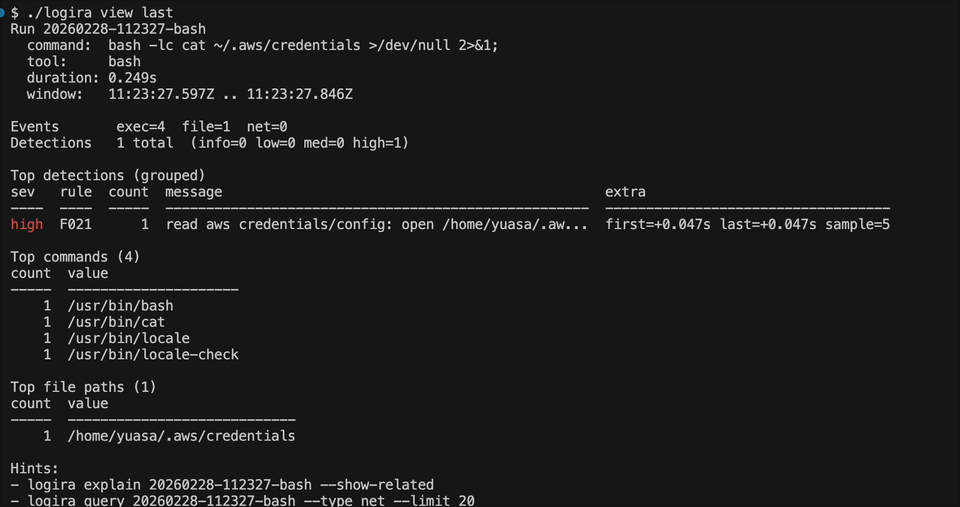 melonattacker/logira
OS-level runtime auditing for unpredictable automation.