
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
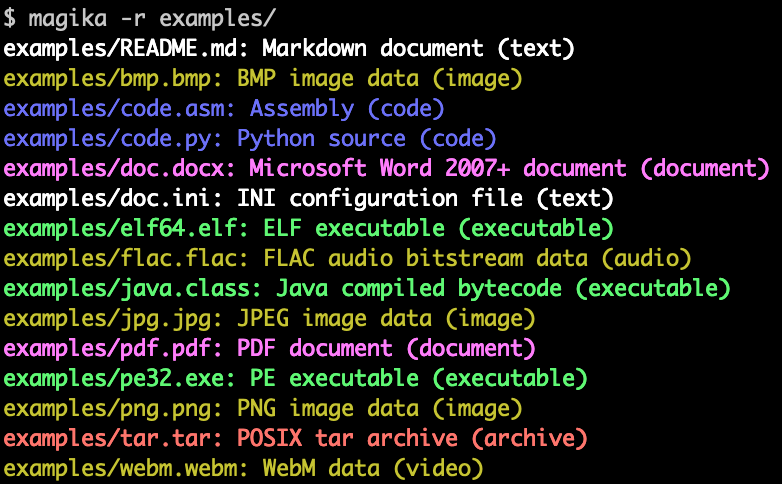
magika preview

magika

GitHubgoogle/magika

Fast and accurate AI powered file content types detection

code-analysisforensicsgeneral-purpose-utilities+3
18.7k8h 40m ago
Hayabusa-Bulk-Runner preview

Hayabusa-Bulk-Runner

GitHubrorywag/hayabusa-bulk-runner

Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
defensive-toolsdigital-forensicsforensics+5
181 day ago
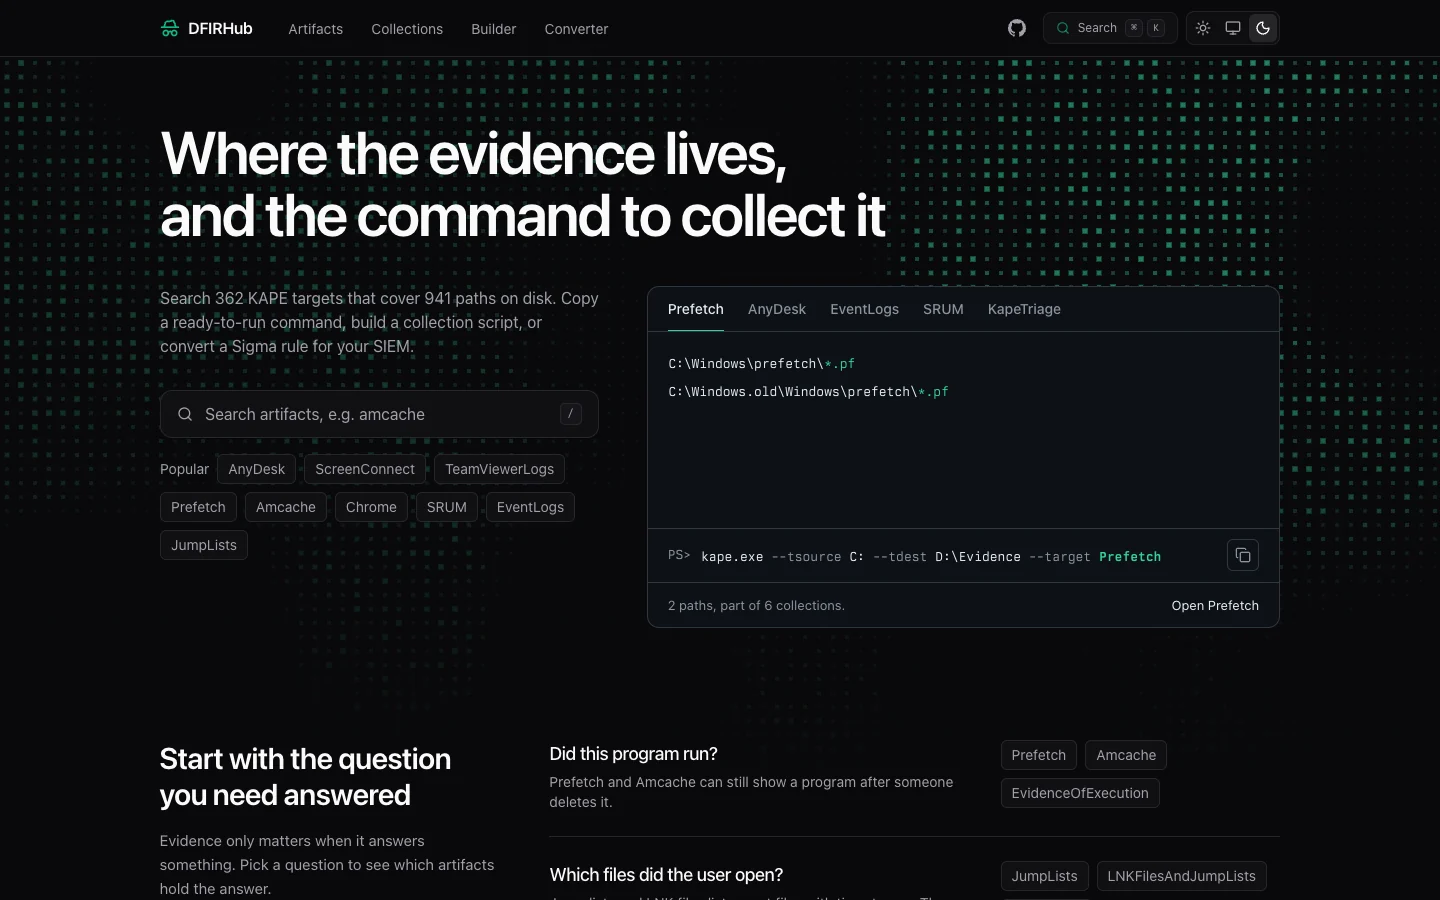
DFIRHub preview

DFIRHub

GitHublascc/dfirhub

Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
curated-resourcesdigital-forensicsforensics+4
102 days ago
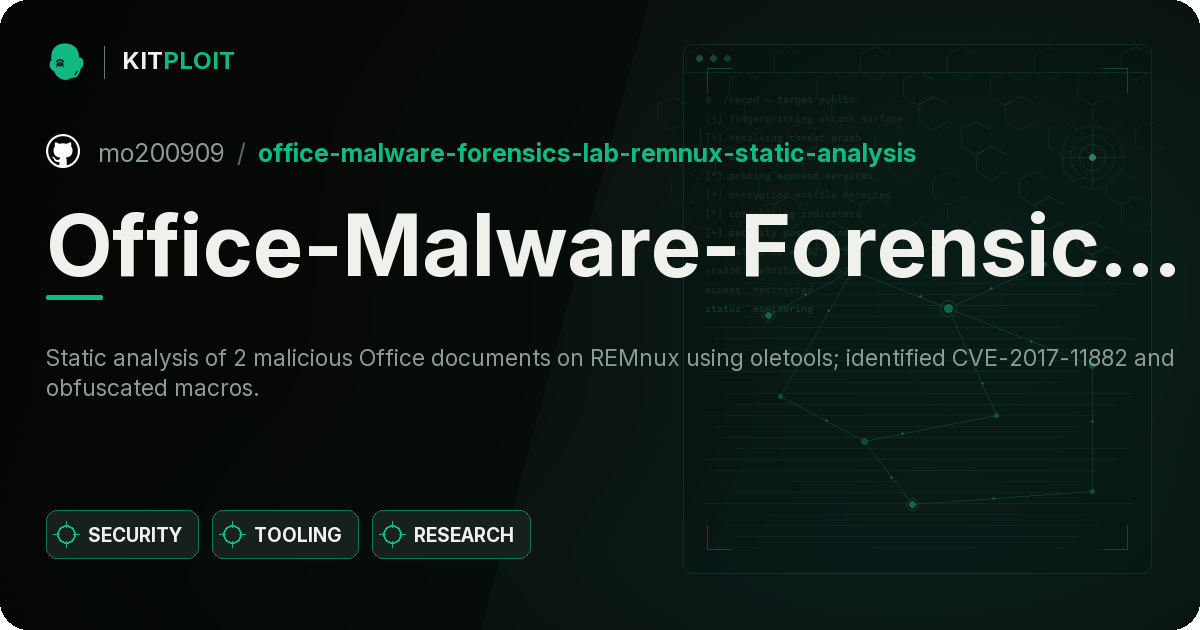
Office-Malware-Forensics-Lab-REMnux-Static-Analysis preview

Office-Malware-Forensics-Lab-REMnux-Static-Analysis

GitHubmo200909/office-malware-forensics-lab-remnux-static-analysis

Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.

code-analysisdigital-forensicseducation+6
3 days ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…

defensive-toolsdigital-forensicsforensics+8
3919 days ago
halo-record preview

halo-record

GitHubbkuan001/halo-record

Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
ai-securityforensicsincident-response+1
8525 days ago
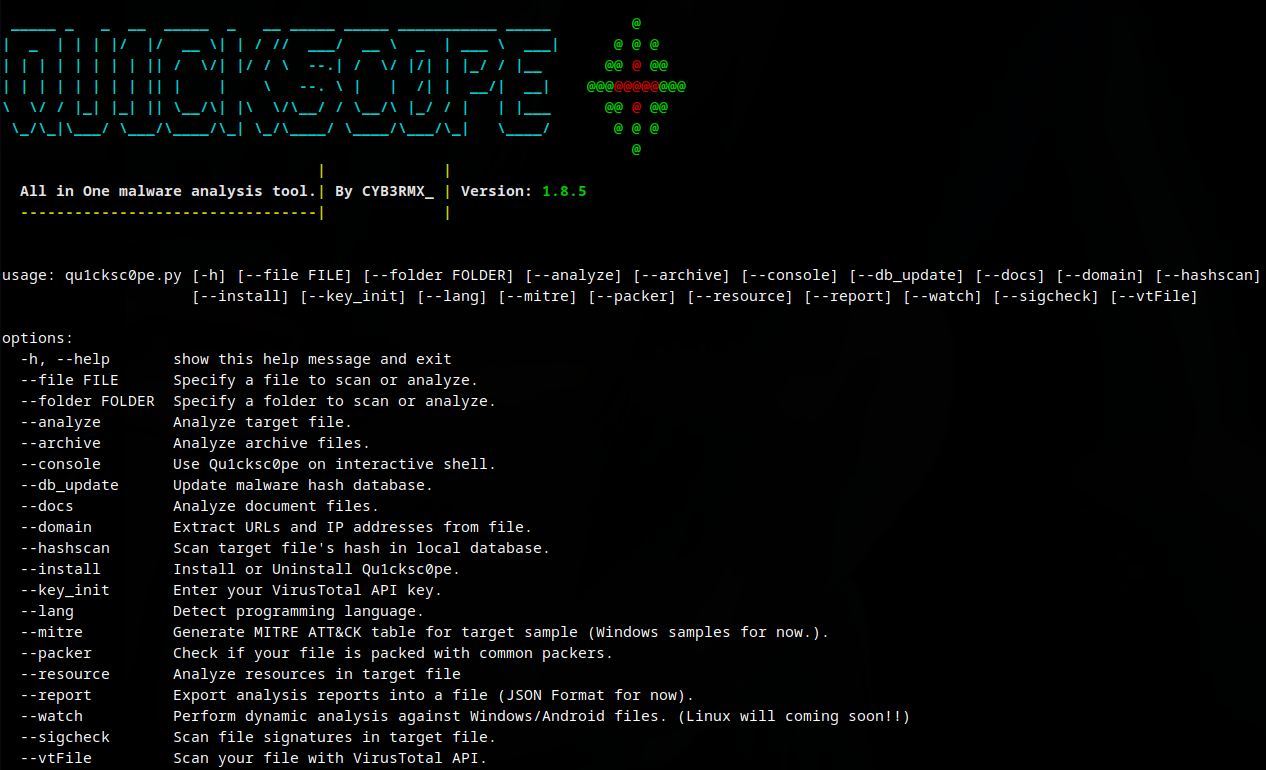
Qu1cksc0pe preview

Qu1cksc0pe

GitHubcyb3rmx/qu1cksc0pe

All-in-One malware analysis tool.
android-securitydynamic-analysis-sandboxingforensics+4
2.1k1 month ago
binviz preview

binviz

GitHubkarankantaria/binviz

Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
binary-analysiseducationforensics+4
92 months ago
douglas-042-HQ preview

douglas-042-HQ

GitHubdouglas-042/douglas-042-hq

Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
defensive-toolsforensicsincident-response+5
2 months ago
horus preview

horus

GitHub6abd/horus

An OSINT / digital forensics tool built in Python
digital-forensicsencryption-decryption-toolsforensics+3
1.1k3 months ago
UnConfuserEx preview

UnConfuserEx

GitHubzypherion-technologies/unconfuserex

A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
binary-analysiscode-analysisdynamic-analysis-sandboxing+6
443 months ago
wp2shell-scan preview

wp2shell-scan

GitHubinstawp/wp2shell-scan

Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default
defensive-toolsforensicsincident-response+5
63 months ago
r2gopclntabParser preview

r2gopclntabParser

GitHubasherdll/r2gopclntabparser

A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.

binary-analysisdebuggersforensics+3
176 months ago
GDA-android-reversing-Tool preview

GDA-android-reversing-Tool

GitHubcharles2gan/gda-android-reversing-tool

the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
android-securityctfdynamic-analysis-sandboxing+9
4.9k6 months ago
StegoLab preview

StegoLab

GitHubvatsal200600/stegolab

All-in-one Image Steganography Toolkit for CTFs & Forensics
ctfdigital-forensicsforensics+2
26 months ago
CVE-2025-8088-WinRAR-Zero-Day-Path-Traversal preview

CVE-2025-8088-WinRAR-Zero-Day-Path-Traversal

GitHubadityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal

An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.
educationexploitationforensics+6
121 year ago
RedHunt-OS preview

RedHunt-OS

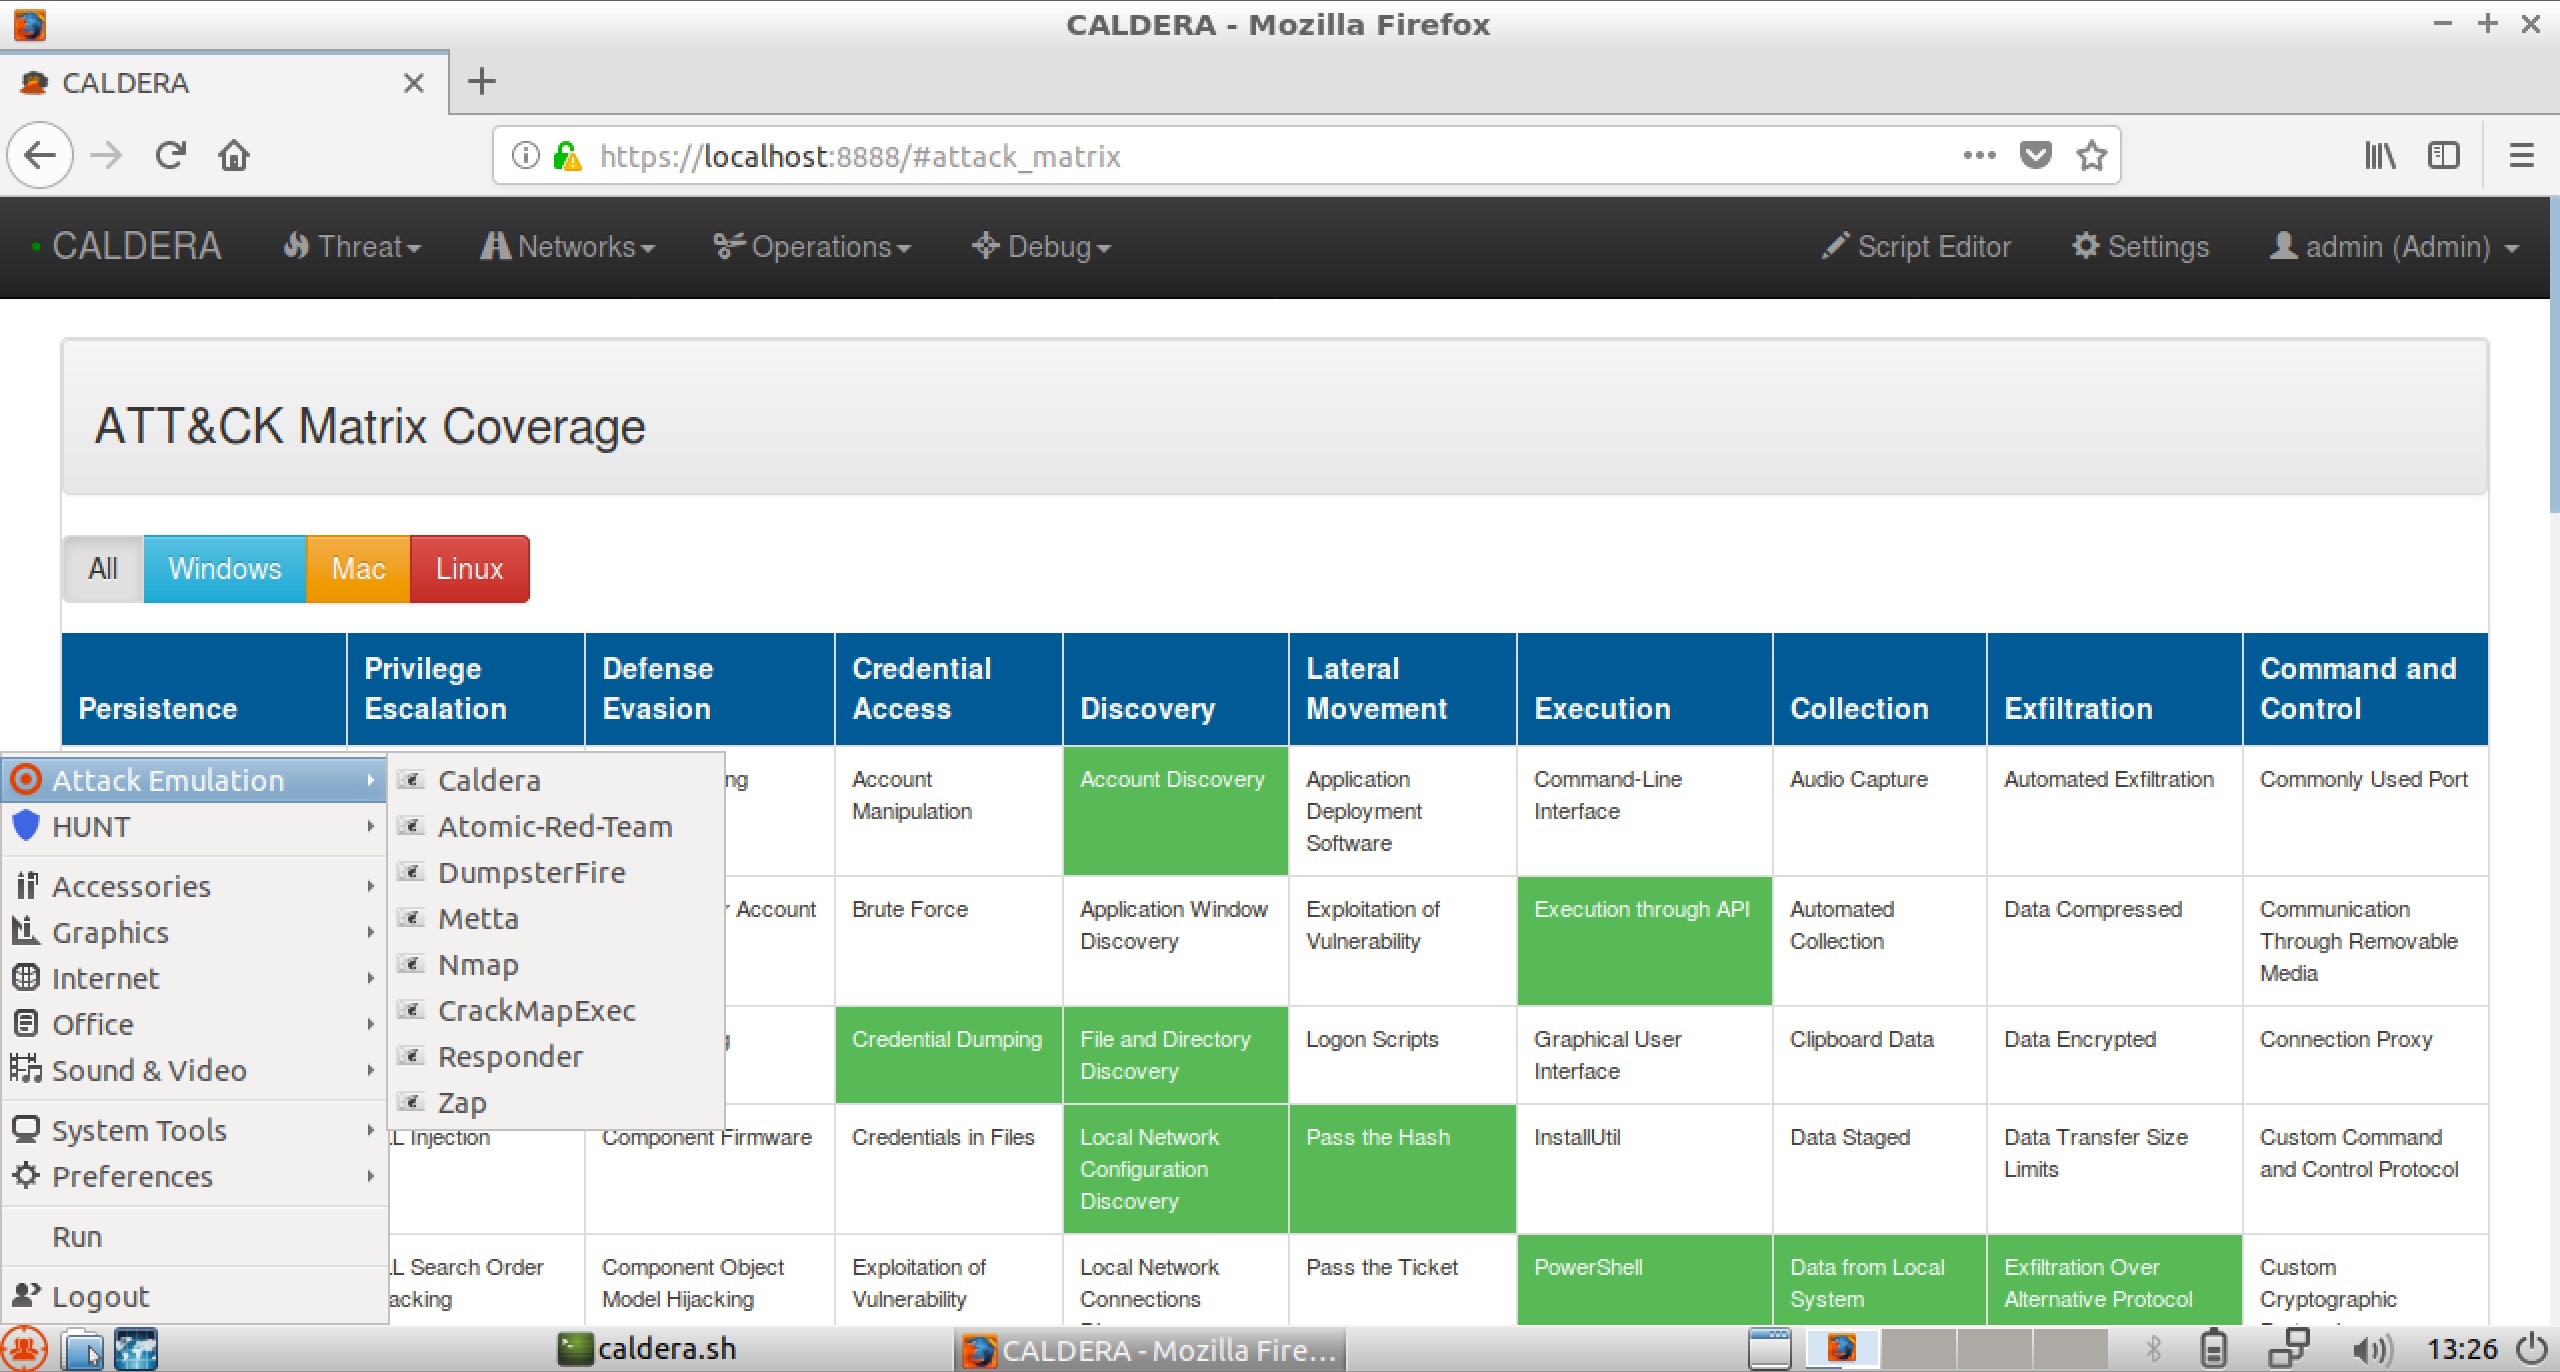
GitHubredhuntlabs/redhunt-os

Virtual Machine for Adversary Emulation and Threat Hunting
educationexploit-frameworksforensics+7
1.3k1 year ago
S1EM preview

S1EM

GitHubv1d1an/s1em

This project is a SIEM with SIRP and Threat Intel, all in one.

educationforensicsincident-response+6
4631 year ago
Previous12Next