

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 onekey-sec/unblob
Extract files from any kind of container formats
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
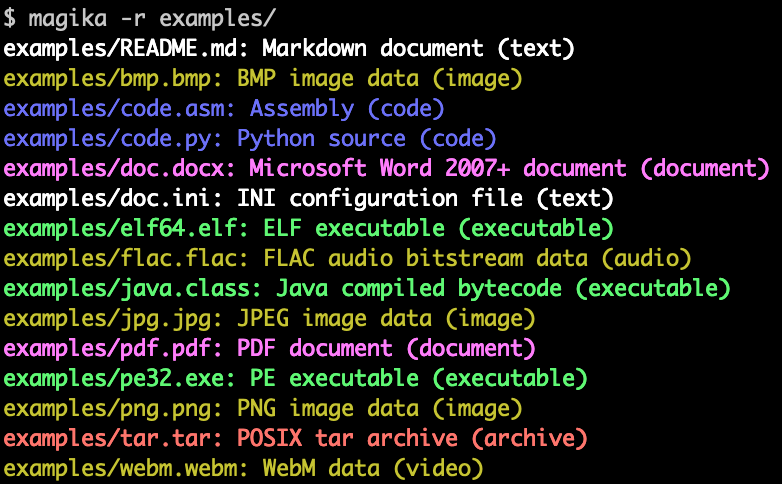 google/magika
Fast and accurate AI powered file content types detection
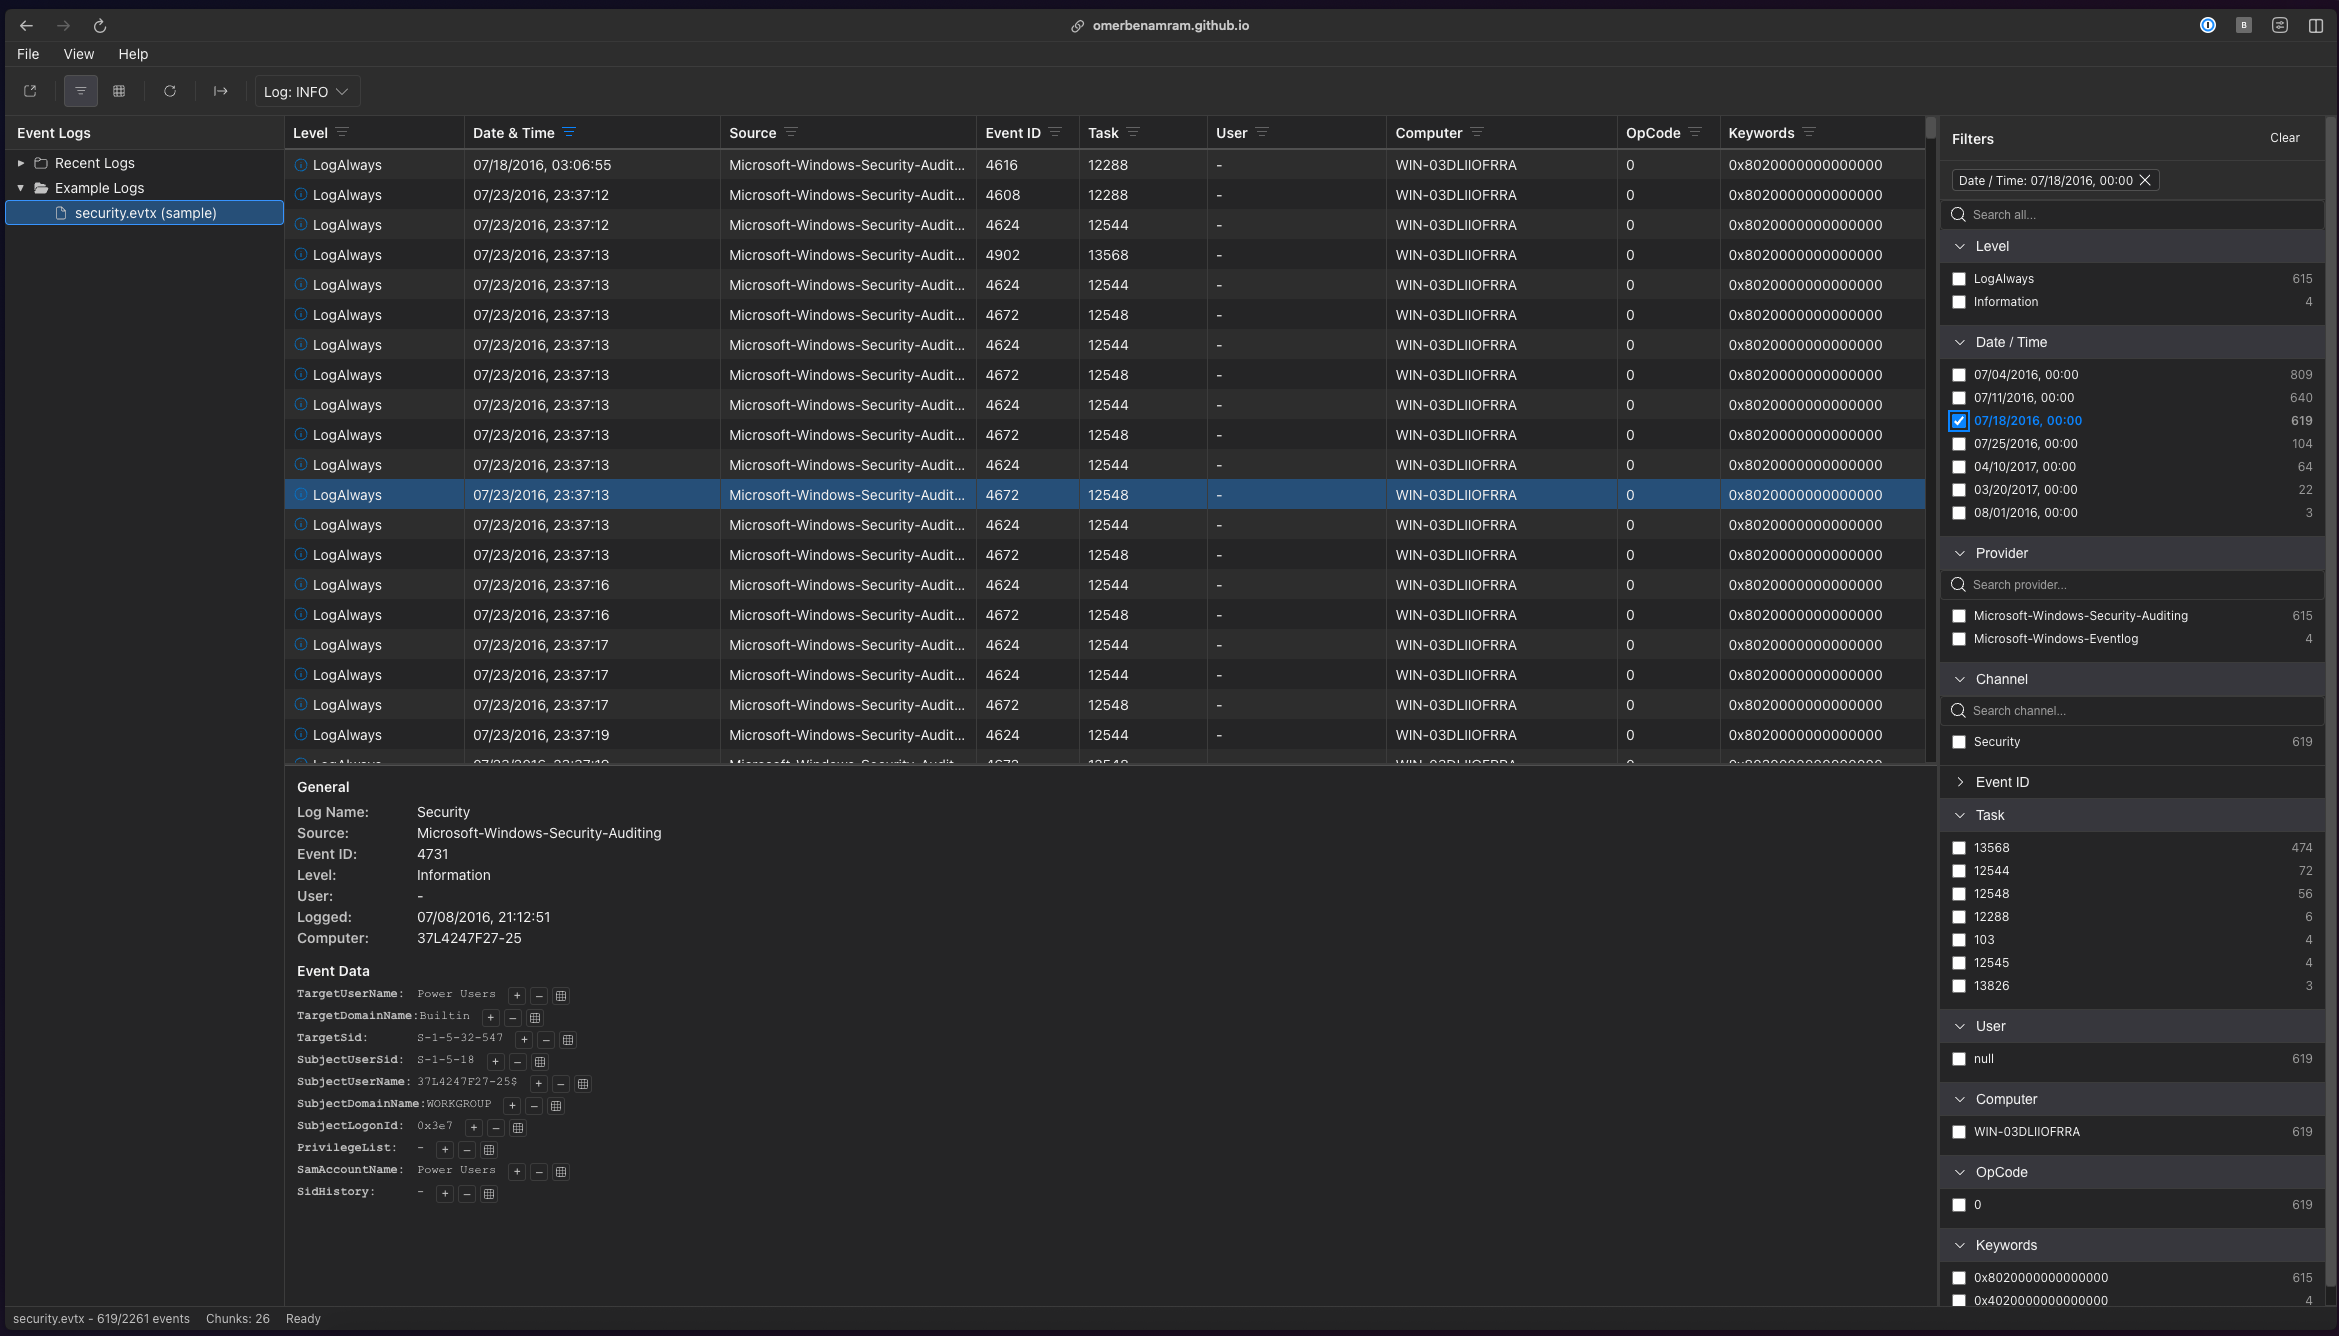 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 mo200909/office-malware-forensics-lab-remnux-static-analysis
Static analysis of 2 suspicious Office documents on REMnux using oletools; one matched CVE-2017-11882, the other was inconclusive.
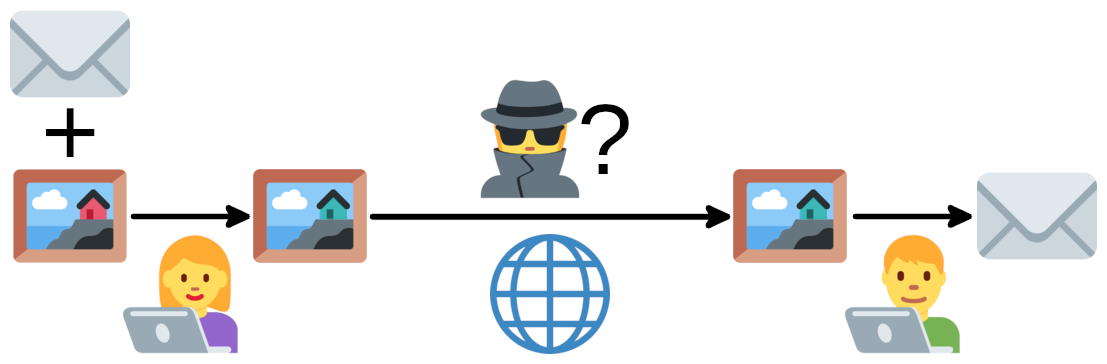 ragibson/steganography
Least Significant Bit Steganography for bitmap images (.bmp and .png), WAV sound files, and byte sequences. Simple LSB Steganalysis (LSB extraction)…
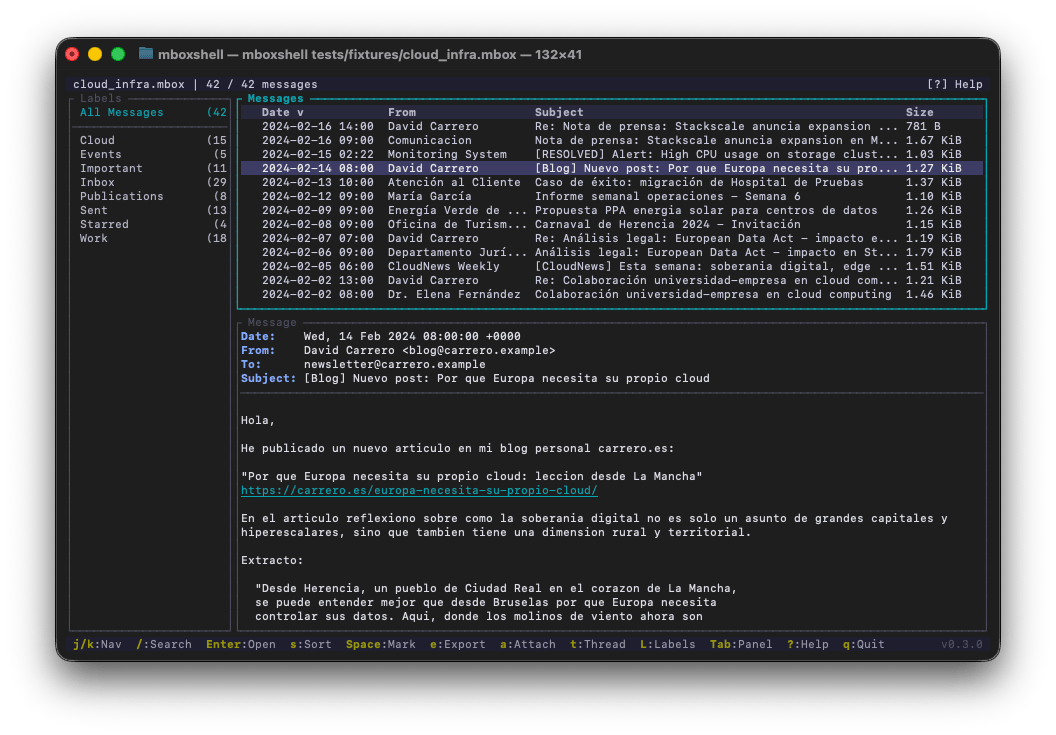 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 cleasbycode/jdvrif
Steganography Tool for JPG Images

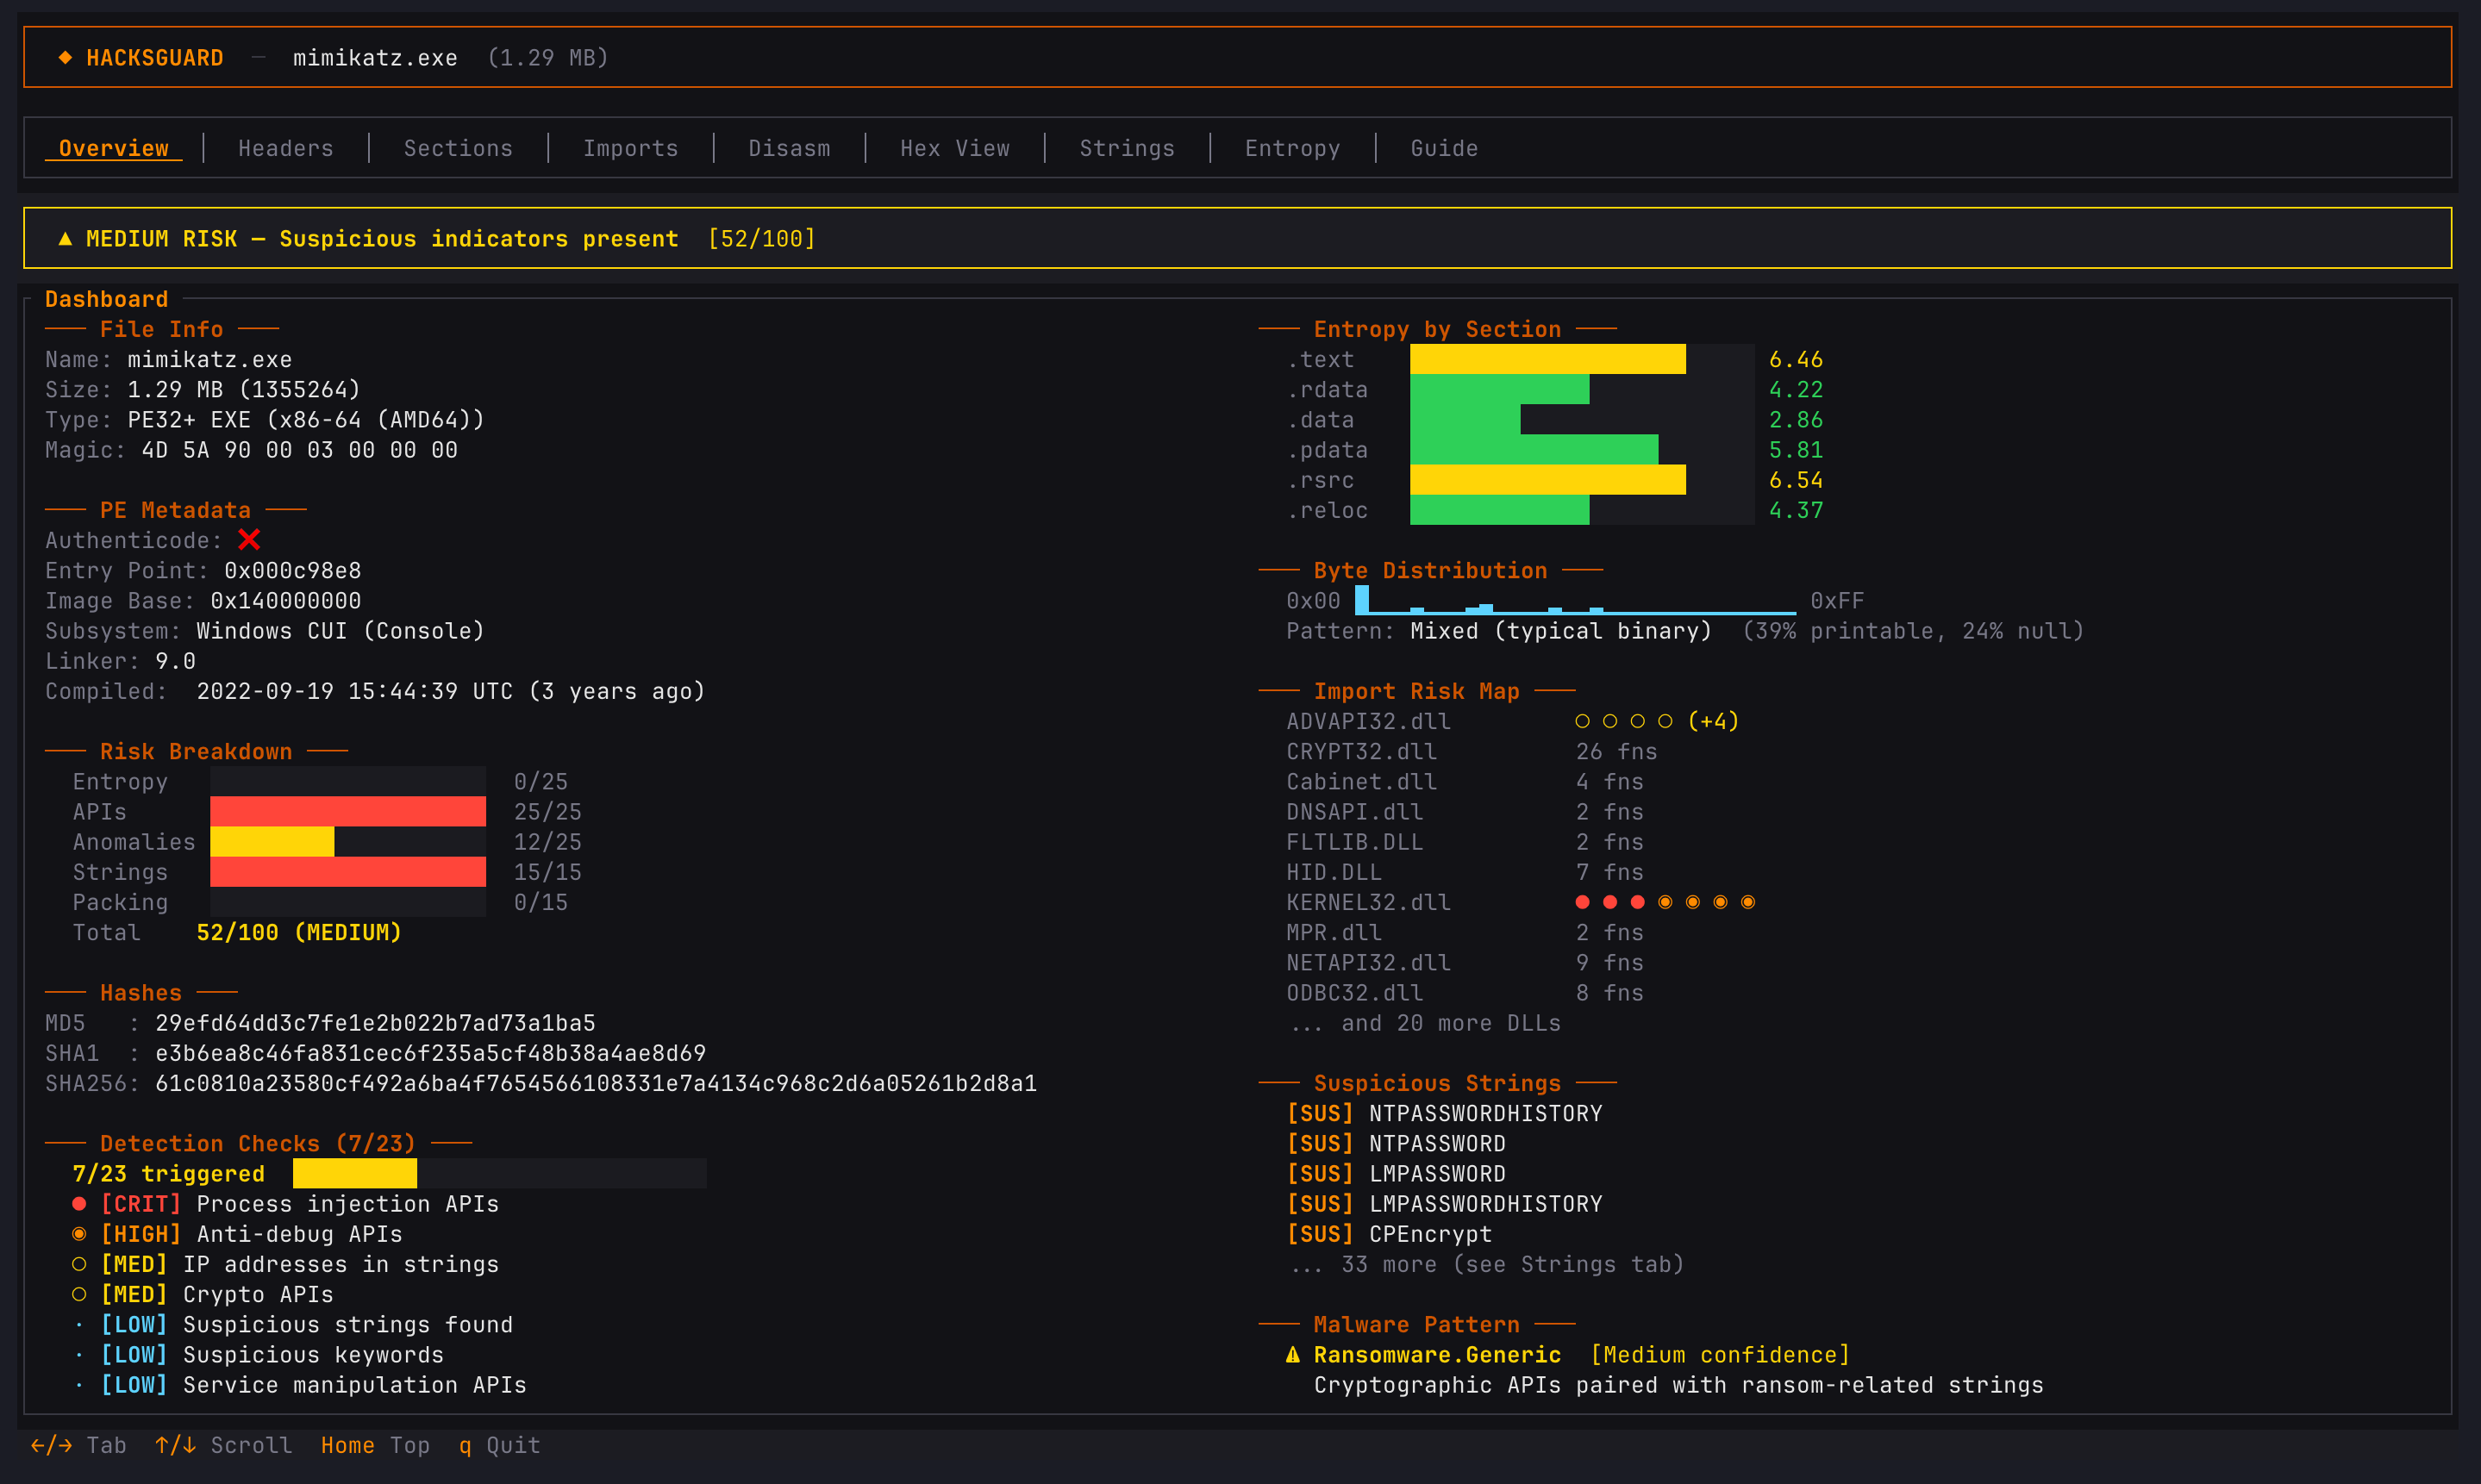 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
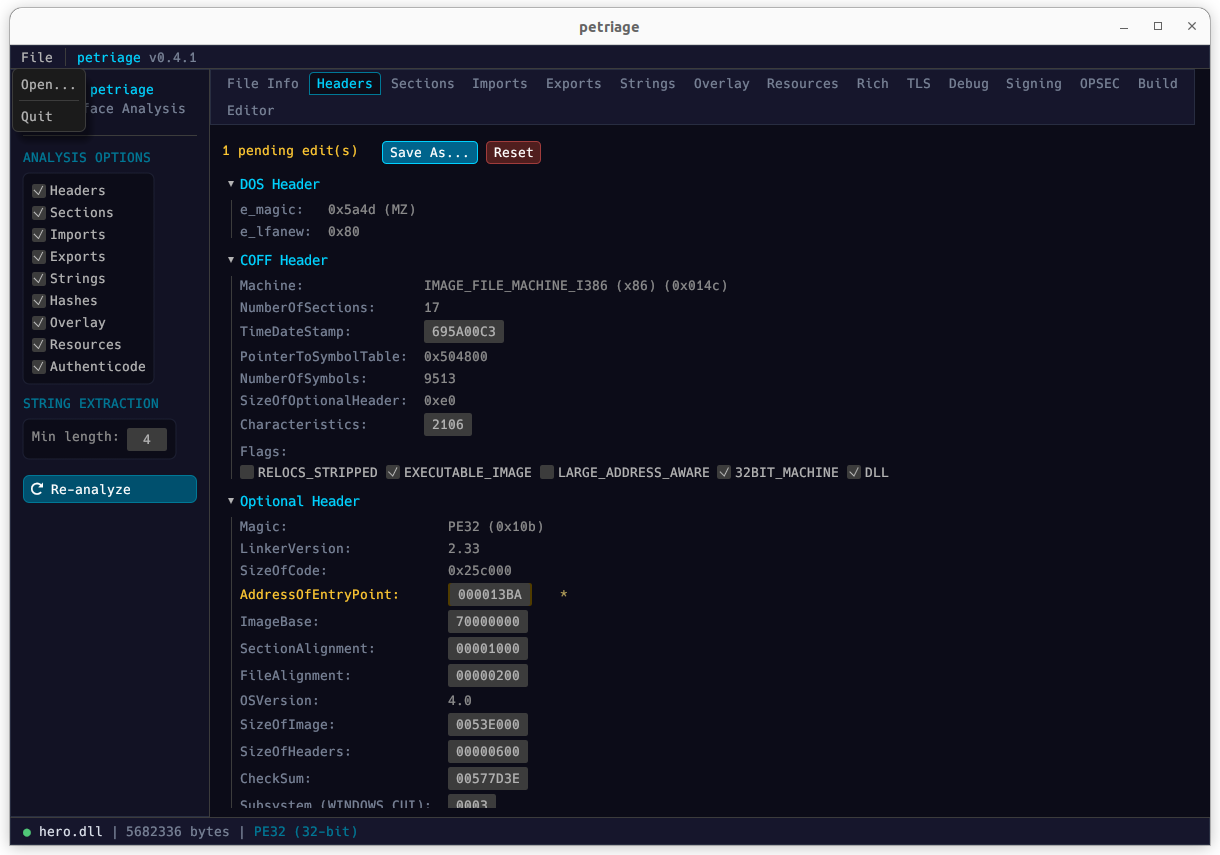 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
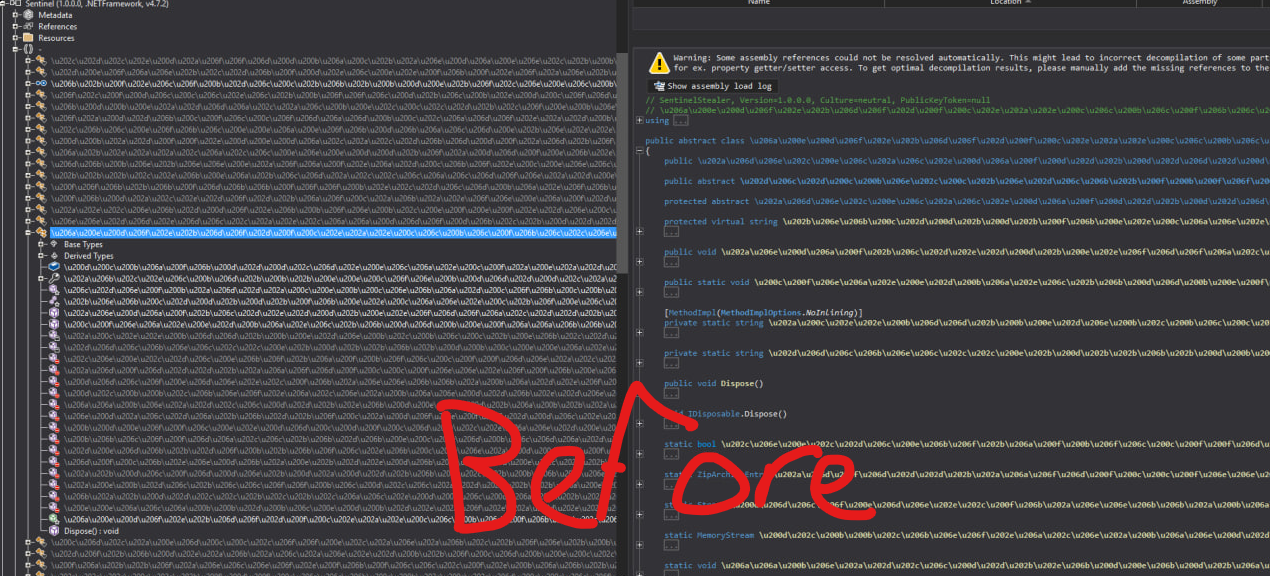 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.