

kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
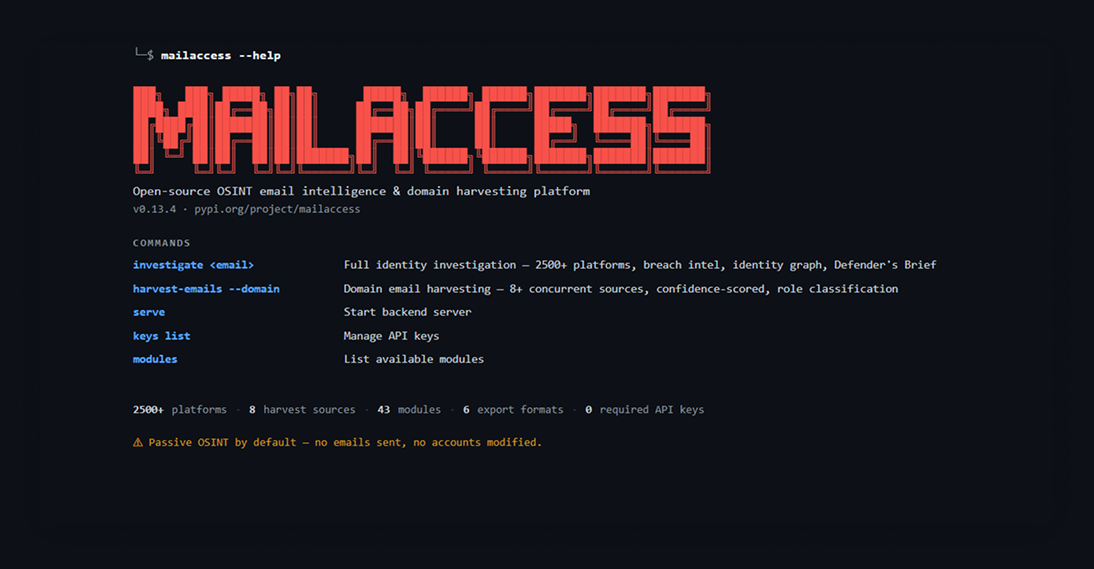 katrielmoses/mailaccess
Free email OSINT tool, 2500+ platforms, identity clustering, breach detection. No API keys required. pip install mailaccess
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
 abdibimantara/maldoc-analysis
Pada bulan maret 2023, terdapat sample baru yang terindentifikasi sebagai malware. Malware tersebut berasal dari file berekstensi.xls dan .doc dan…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 proxymanapp/tcpviewer
The best-in-class macOS app to See every packet clearly on your Mac. Alternative to Wireshark
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
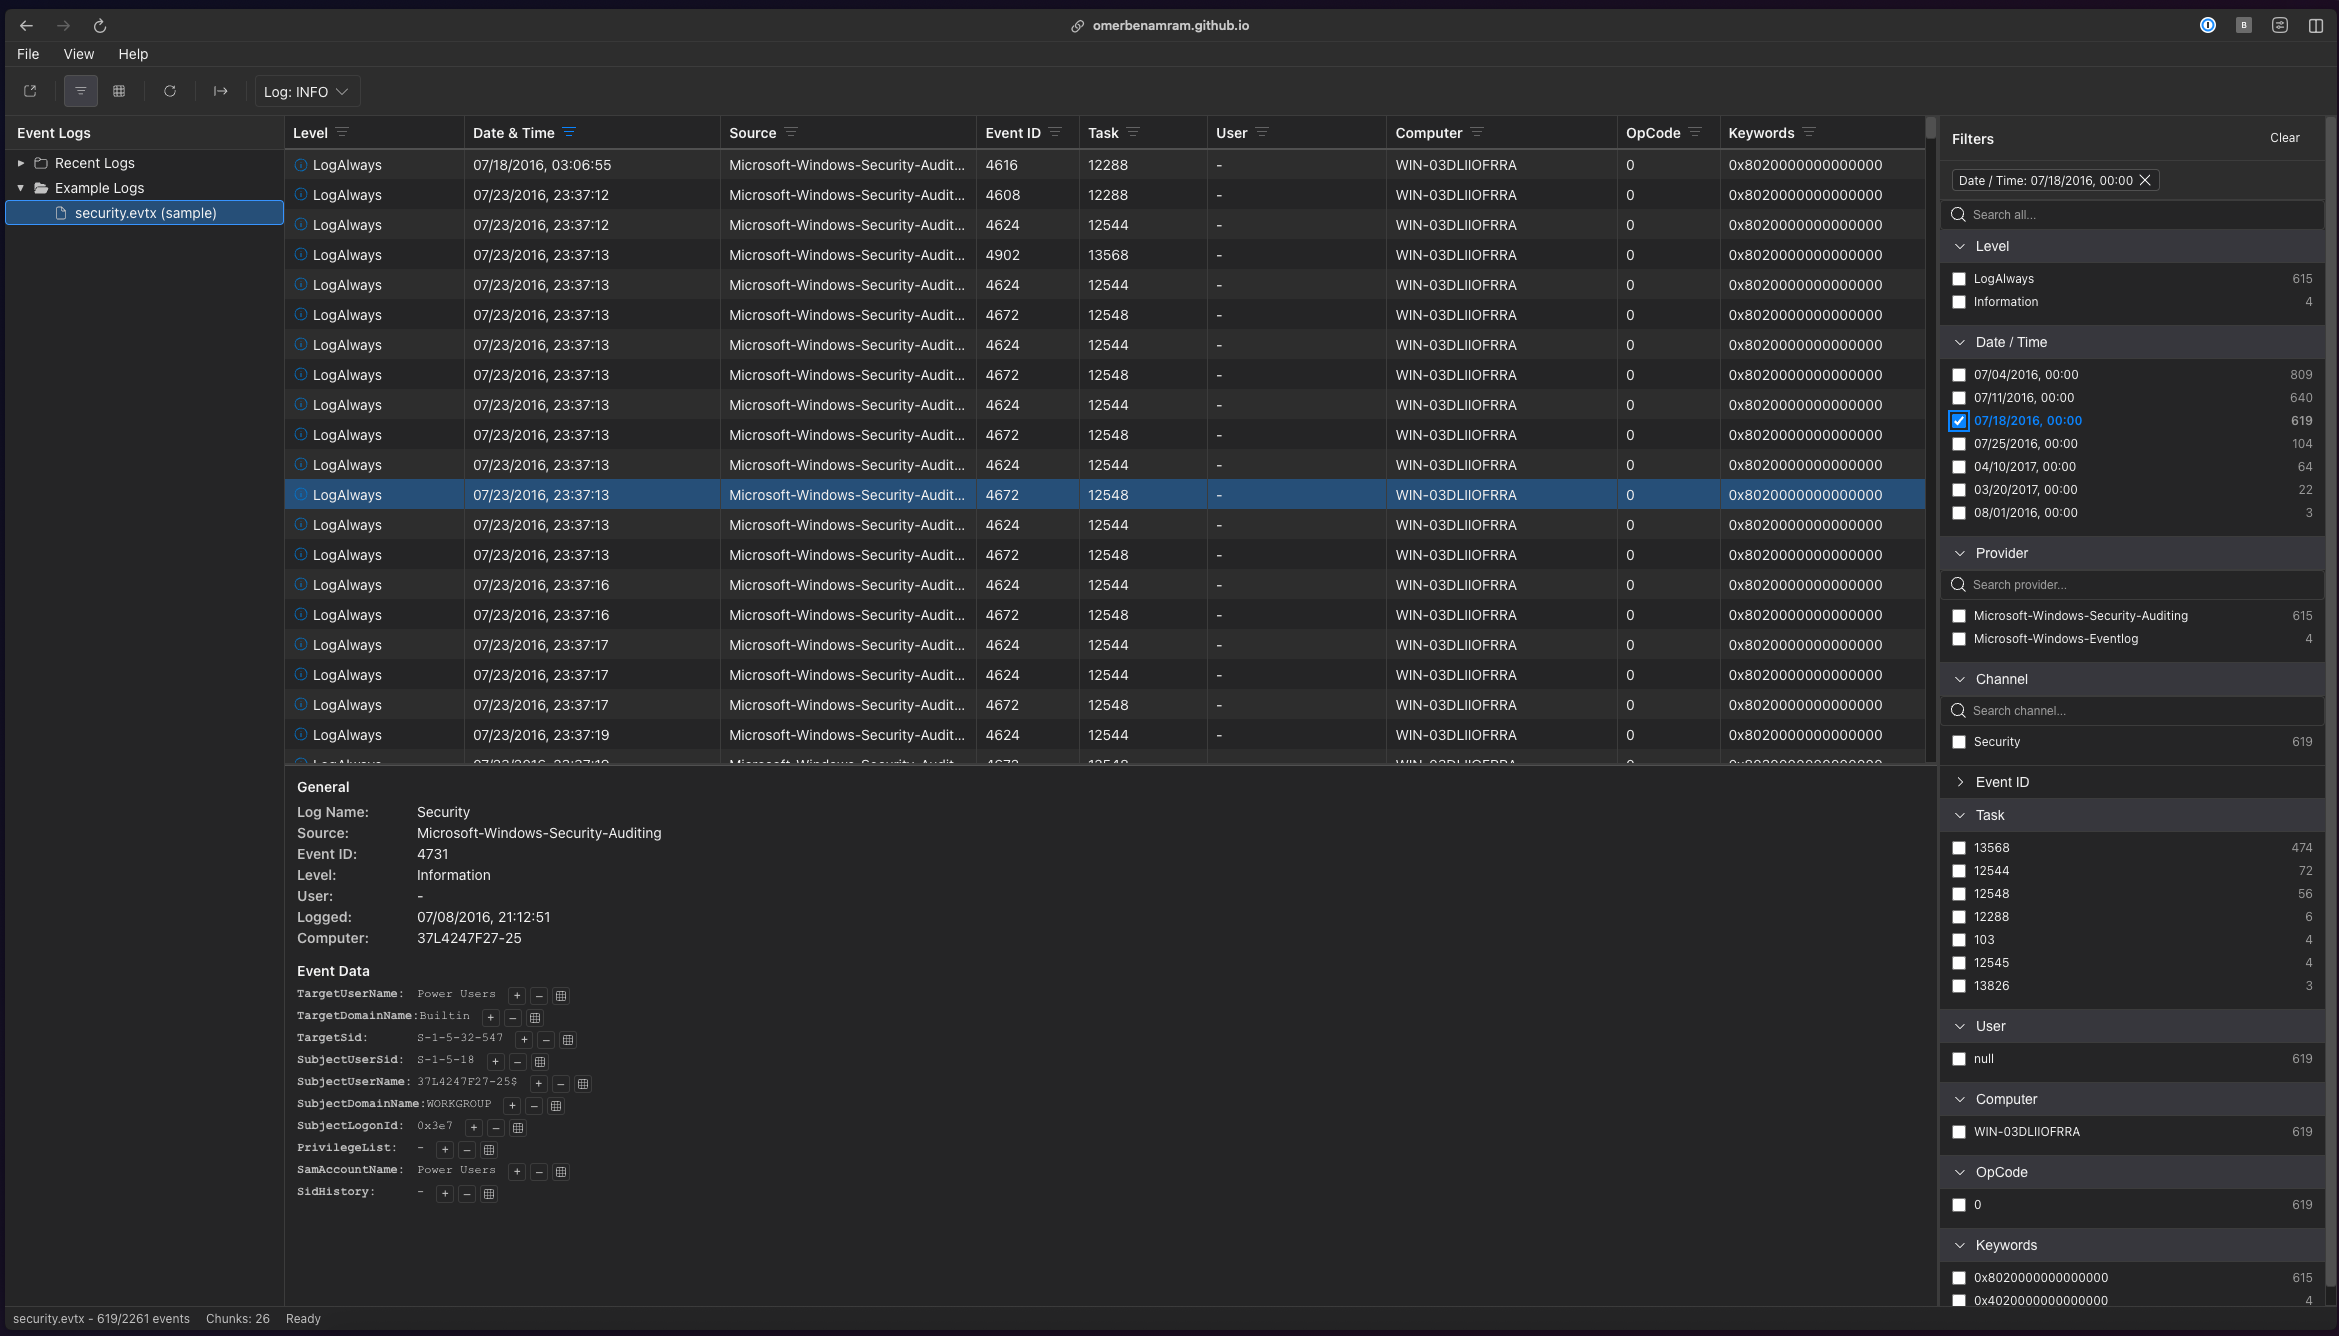 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
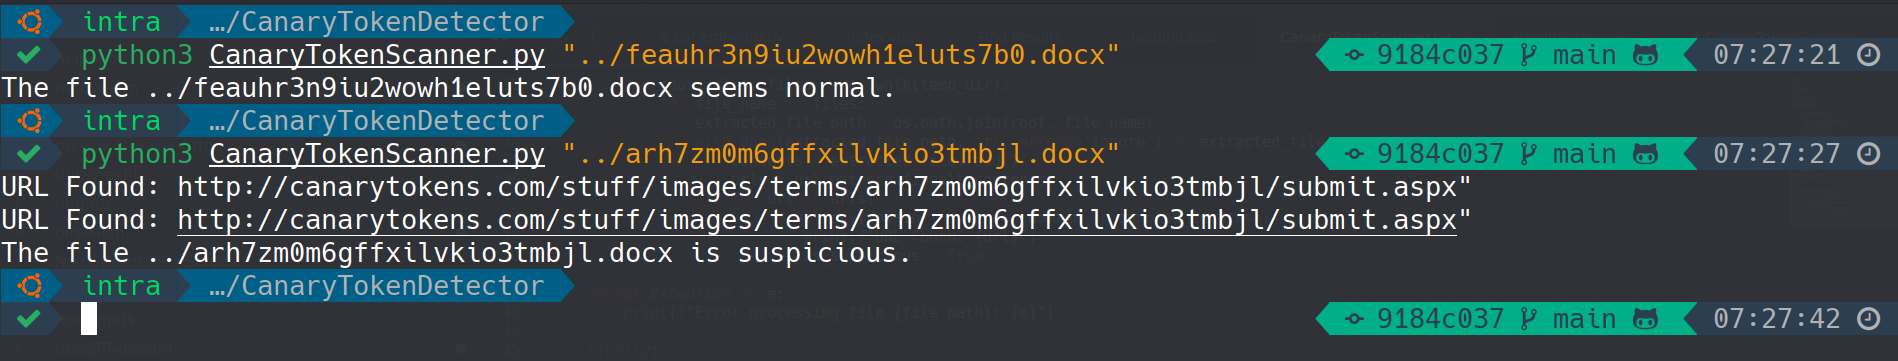 0xnslabs/canarytokenscanner
Detects CanaryTokens in Office docs and PDFs (docx, xlsx, pptx, pdf) without triggering alerts