

Kage-DFIR-toolkit
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
39
karim852/kage-dfir-toolkitWindows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 rorywag/hayabusa-bulk-runner
Bulk-run Hayabusa across a folder of triage collections, one run per host, with per-host reports and a cross-host triage dashboard
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
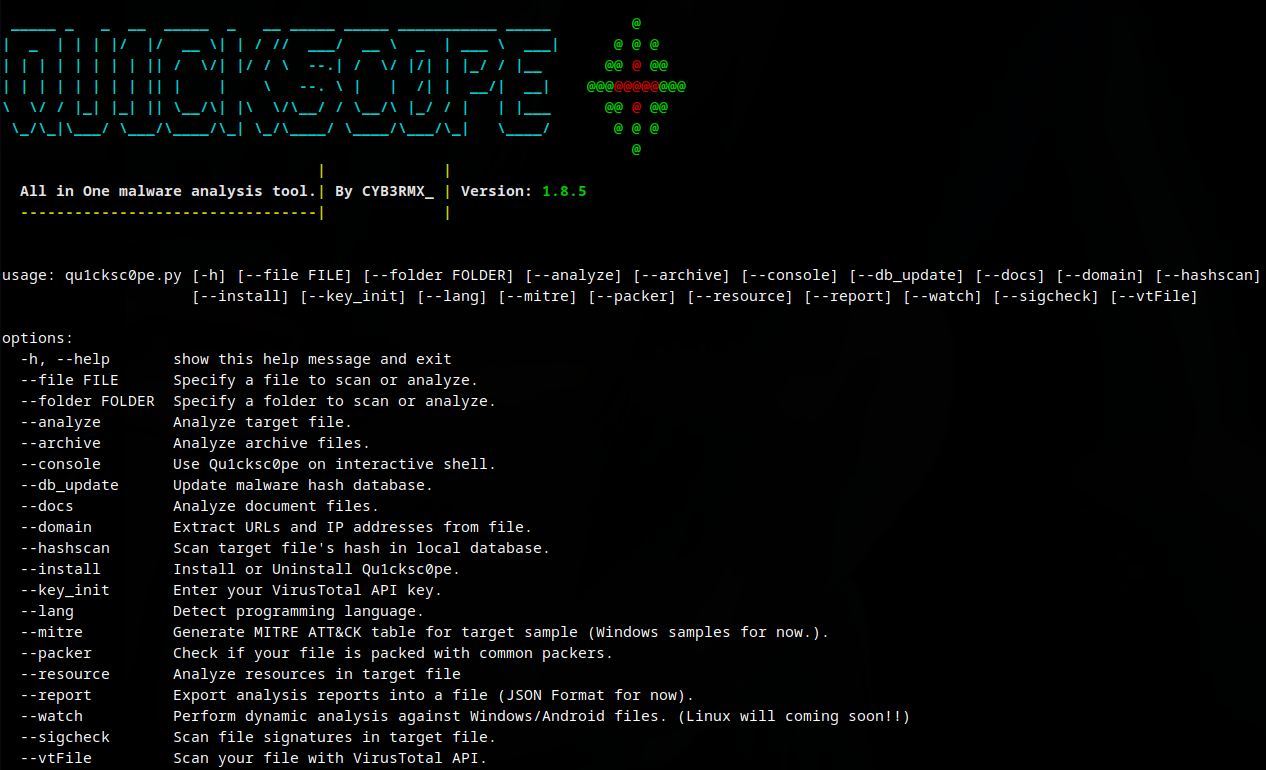 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
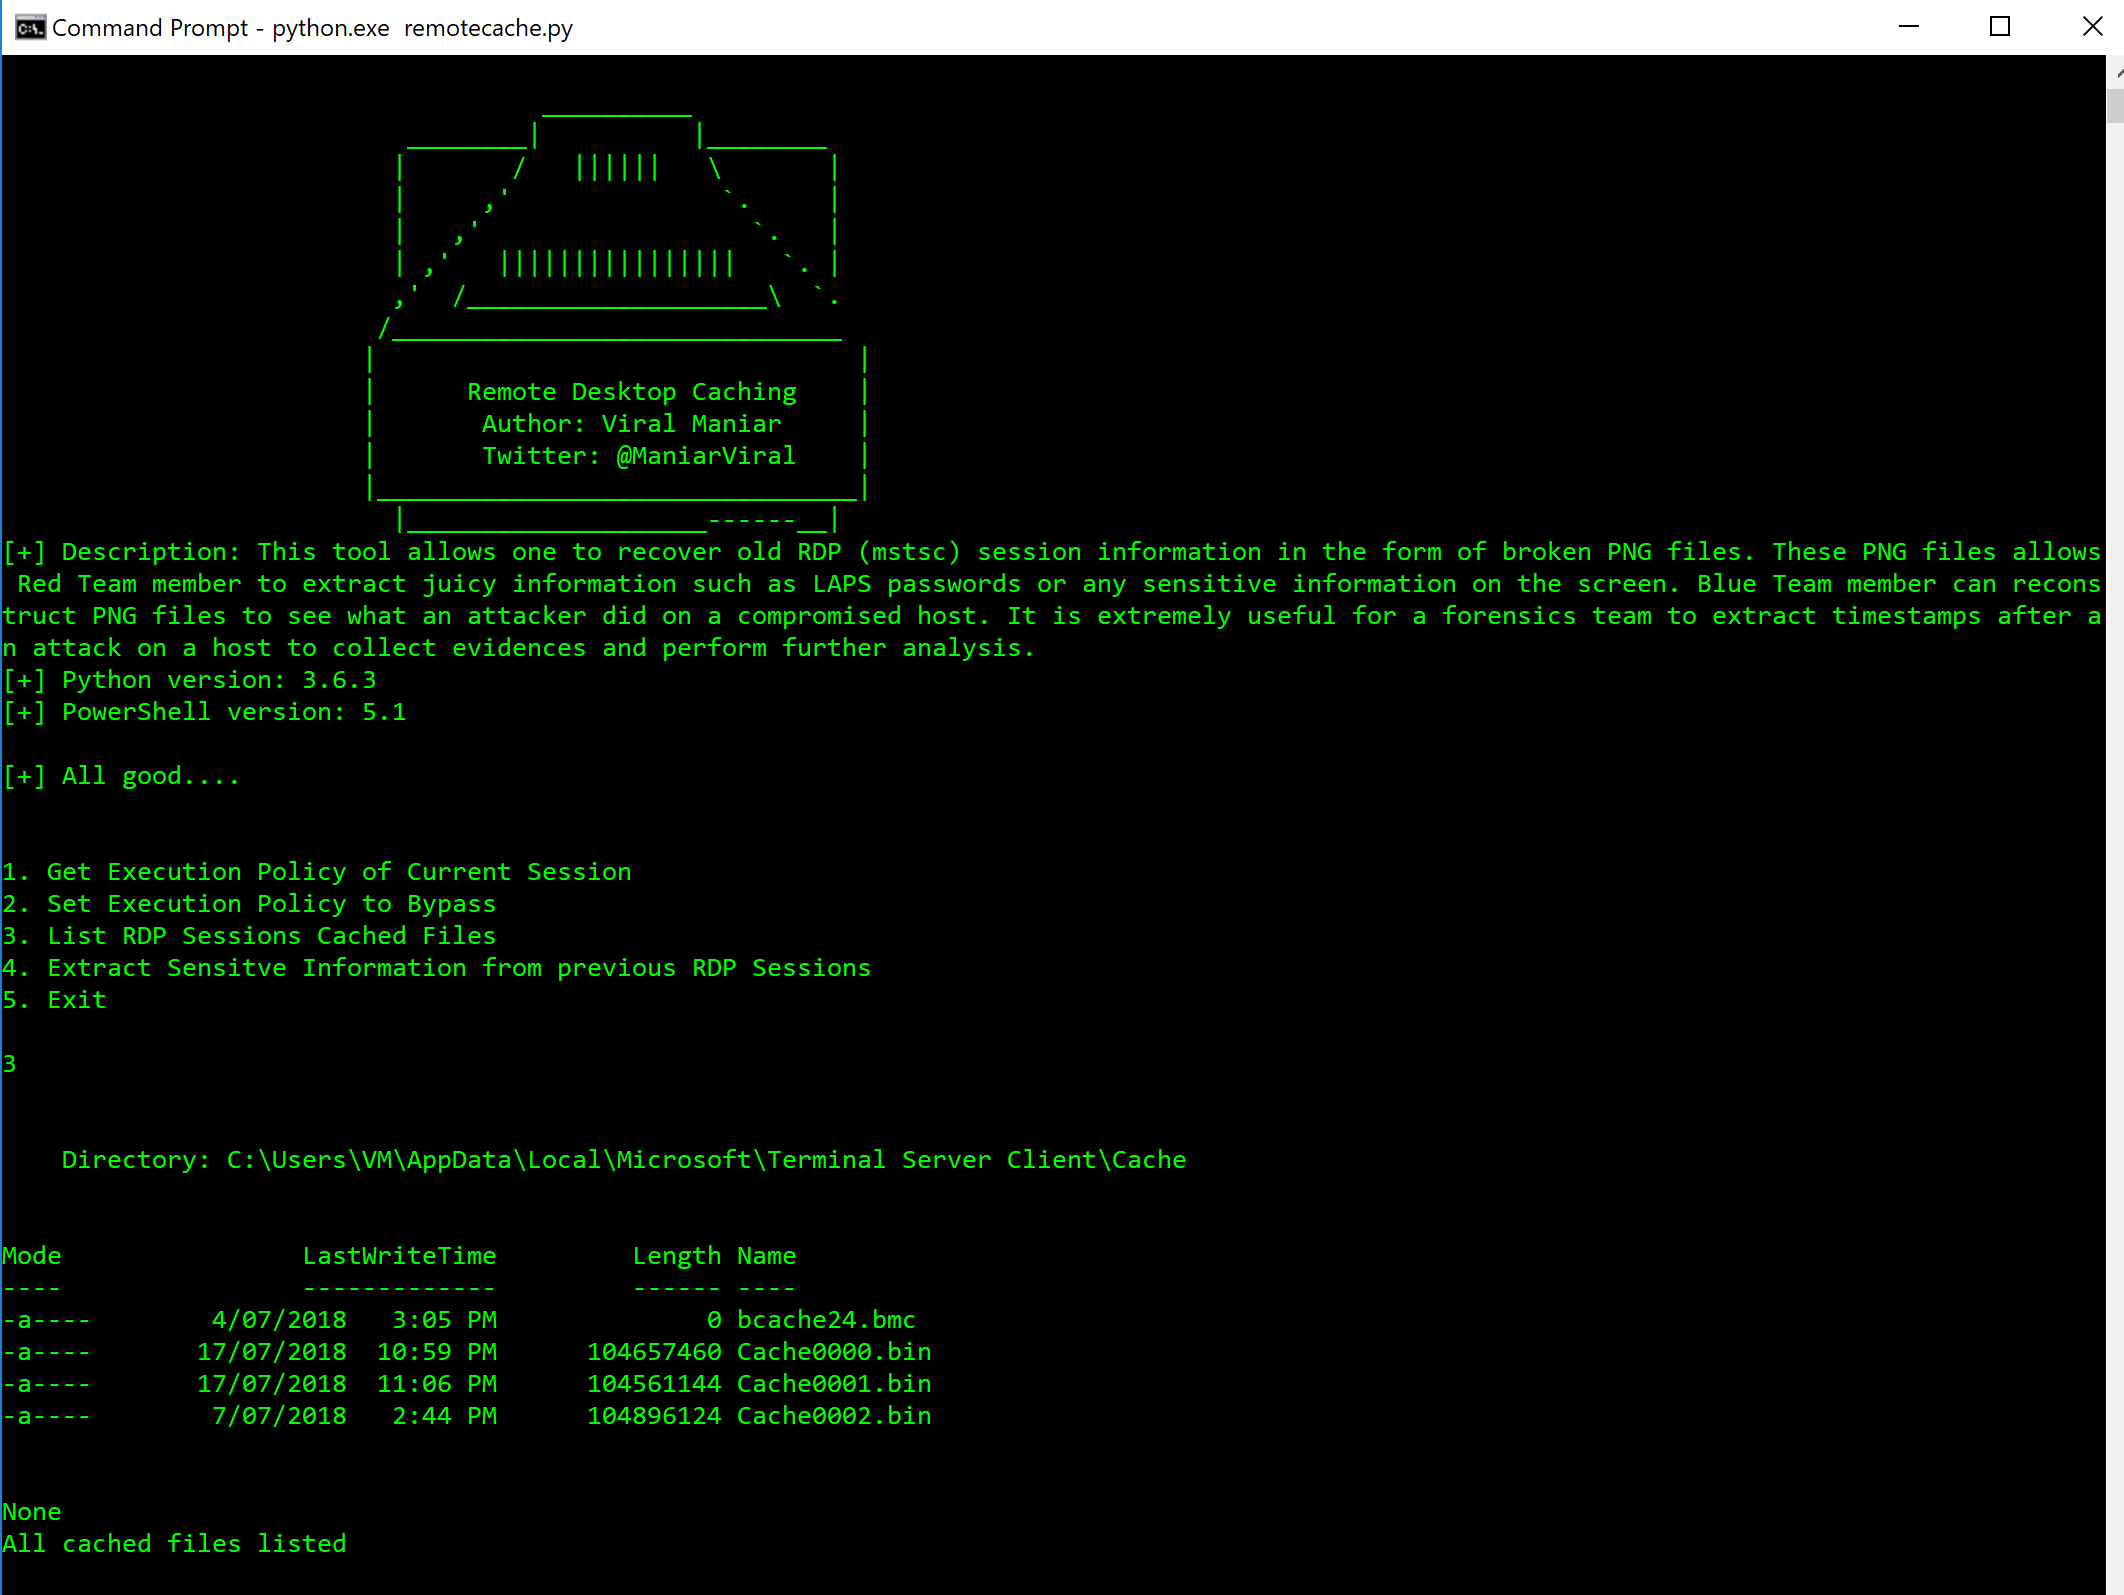 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 charles2gan/gda-android-reversing-tool
the fastest and most powerful android decompiler(native tool working without Java VM) for the APK, DEX, ODEX, OAT, JAR, AAR, and CLASS file. which…
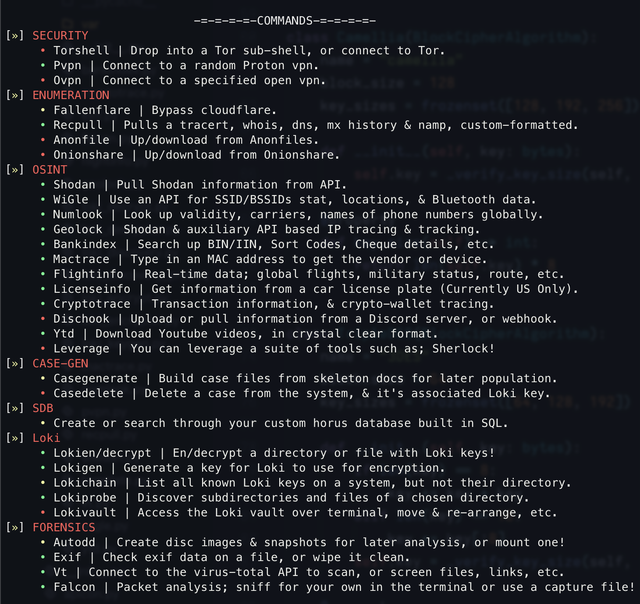 6abd/horus
An OSINT / digital forensics tool built in Python
 instawp/wp2shell-scan
Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default
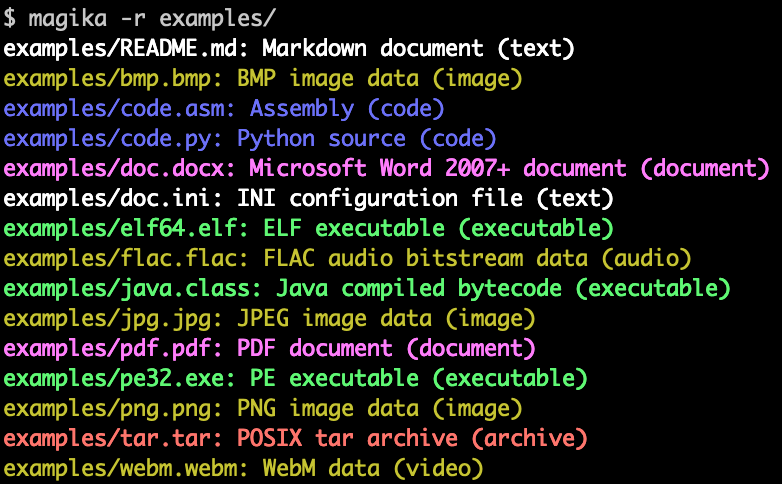 google/magika
Fast and accurate AI powered file content types detection
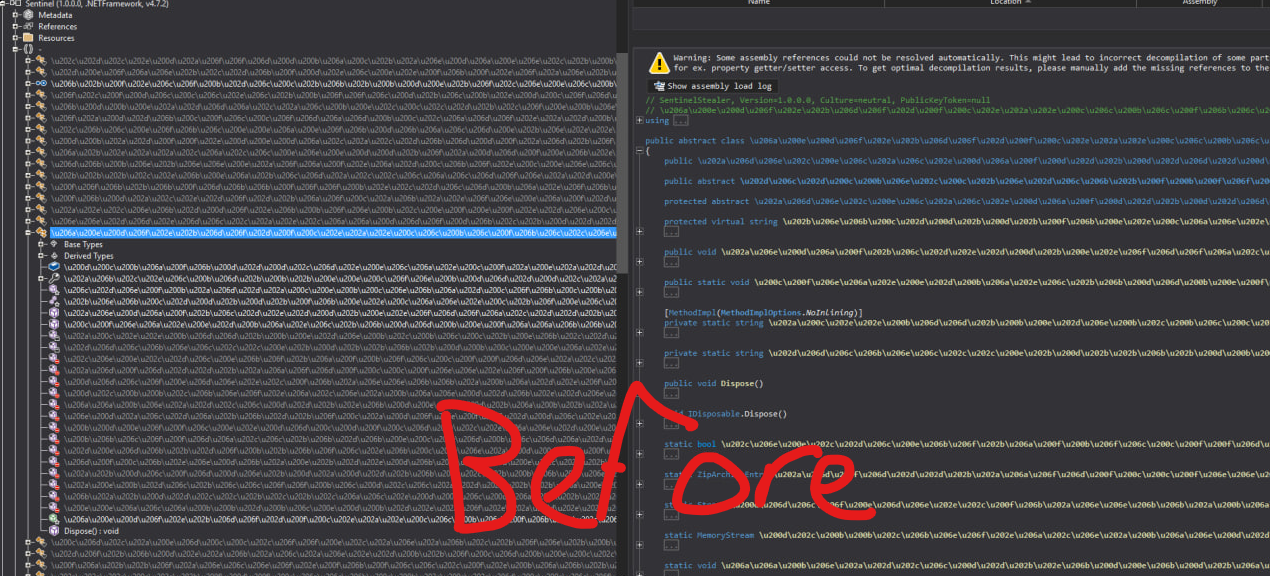 zypherion-technologies/unconfuserex
A ConfuserEx2 deobfuscator with support for anti tamper, compressor, constants, control flow, and resource recovery.
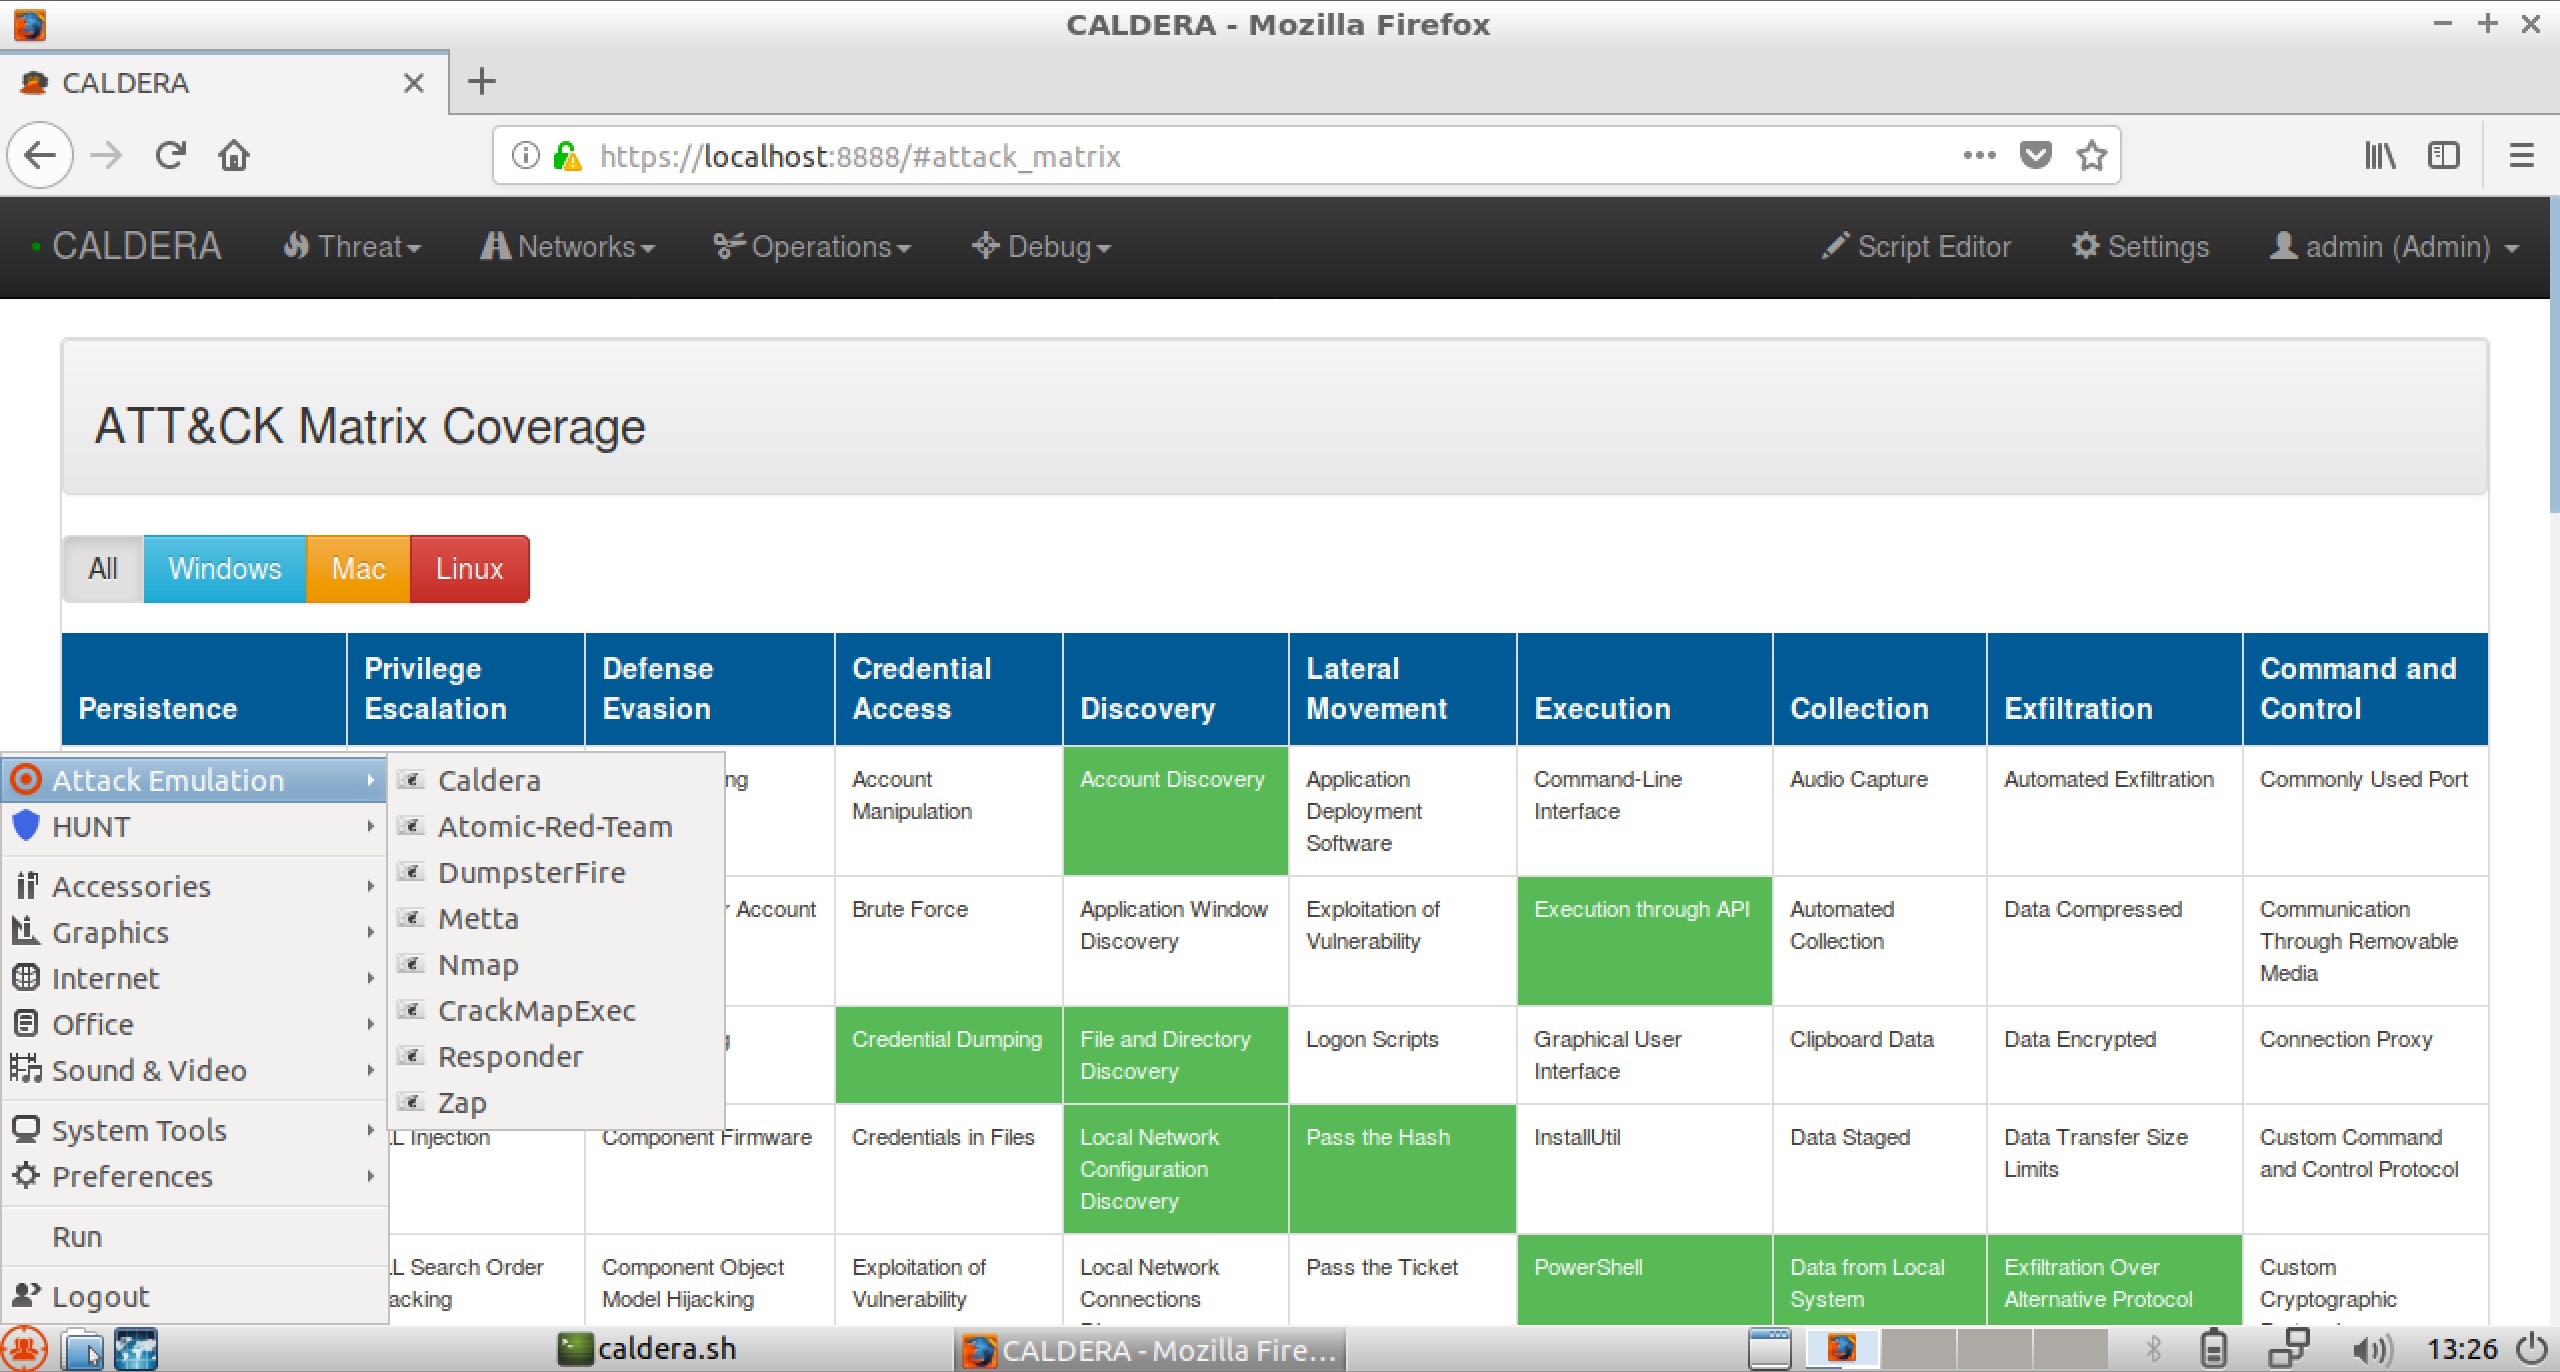 redhuntlabs/redhunt-os
Virtual Machine for Adversary Emulation and Threat Hunting
 adityabhatt3010/cve-2025-8088-winrar-zero-day-path-traversal
An engaging walkthrough on uncovering, patching, and securing the WinRAR CVE-2025-8088 with a hands-on hacker’s twist.
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.