

PAGASUS-PRO
 thakur2309/pagasus-pro
Python ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
android-securitydata-exfiltrationeducation+8
534
thakur2309/pagasus-proPython ADB-based Android device management and security audit toolkit with an interactive menu for root detection, permission dumps, debuggable app…
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 sjzar/chatlog
chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs
 cakescats/airborn-ios-cve-2025-24252
iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…
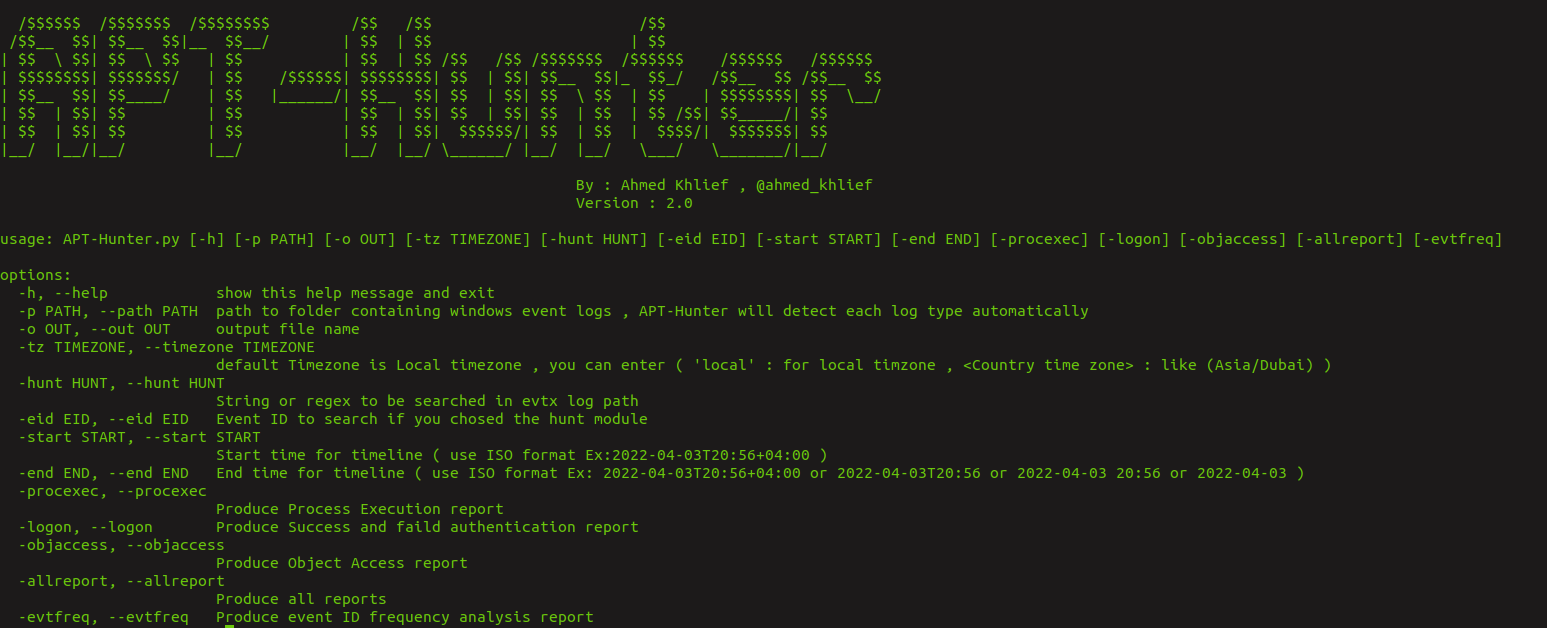 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…
 spieglt/whatfiles
Log what files are accessed by any Linux process
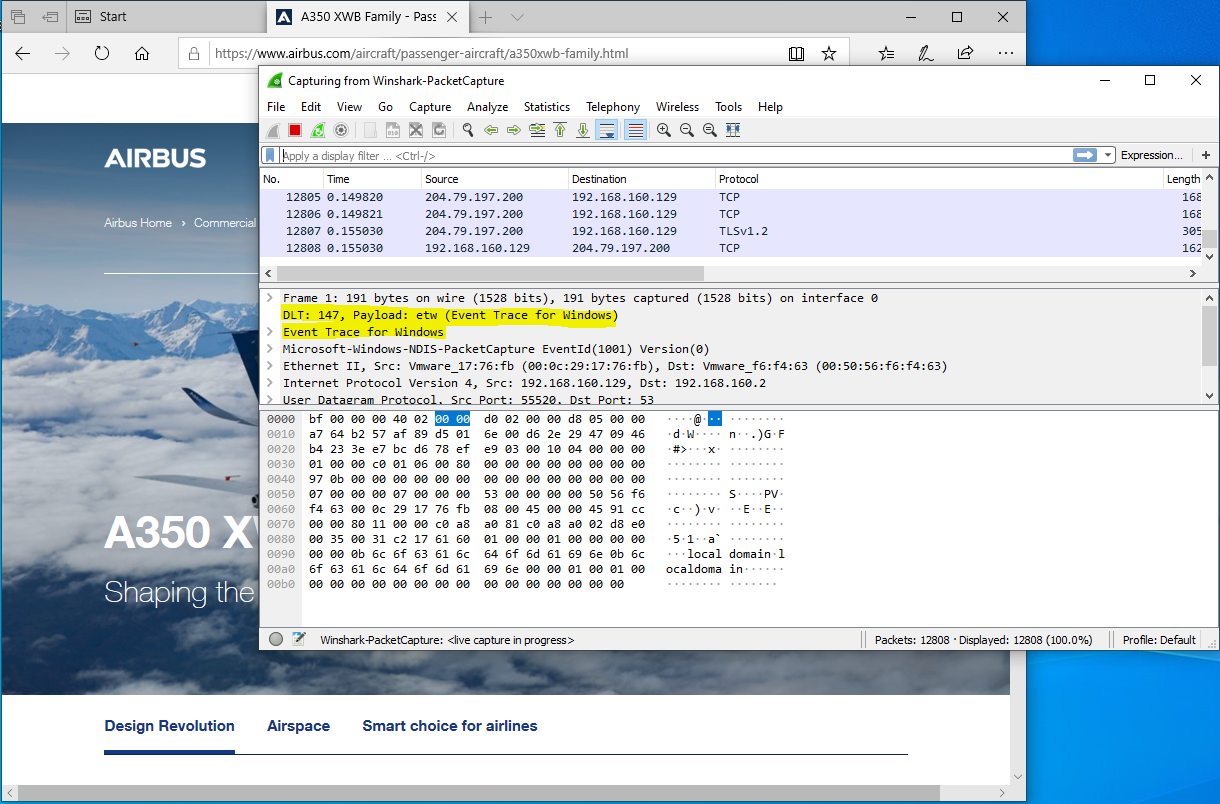 airbus-cert/winshark
A wireshark plugin to instrument ETW
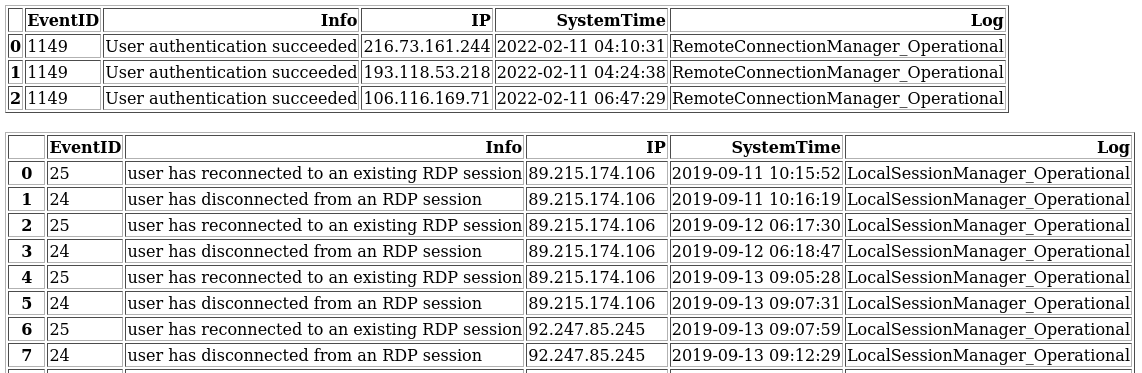 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.