

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 emanuele-f/pcapdroid
No-root network monitor, firewall and PCAP dumper for Android
 ytisf/thezoo
Curated repository of live malware samples and source code for educational malware analysis and research, with an organized database and CLI tools…
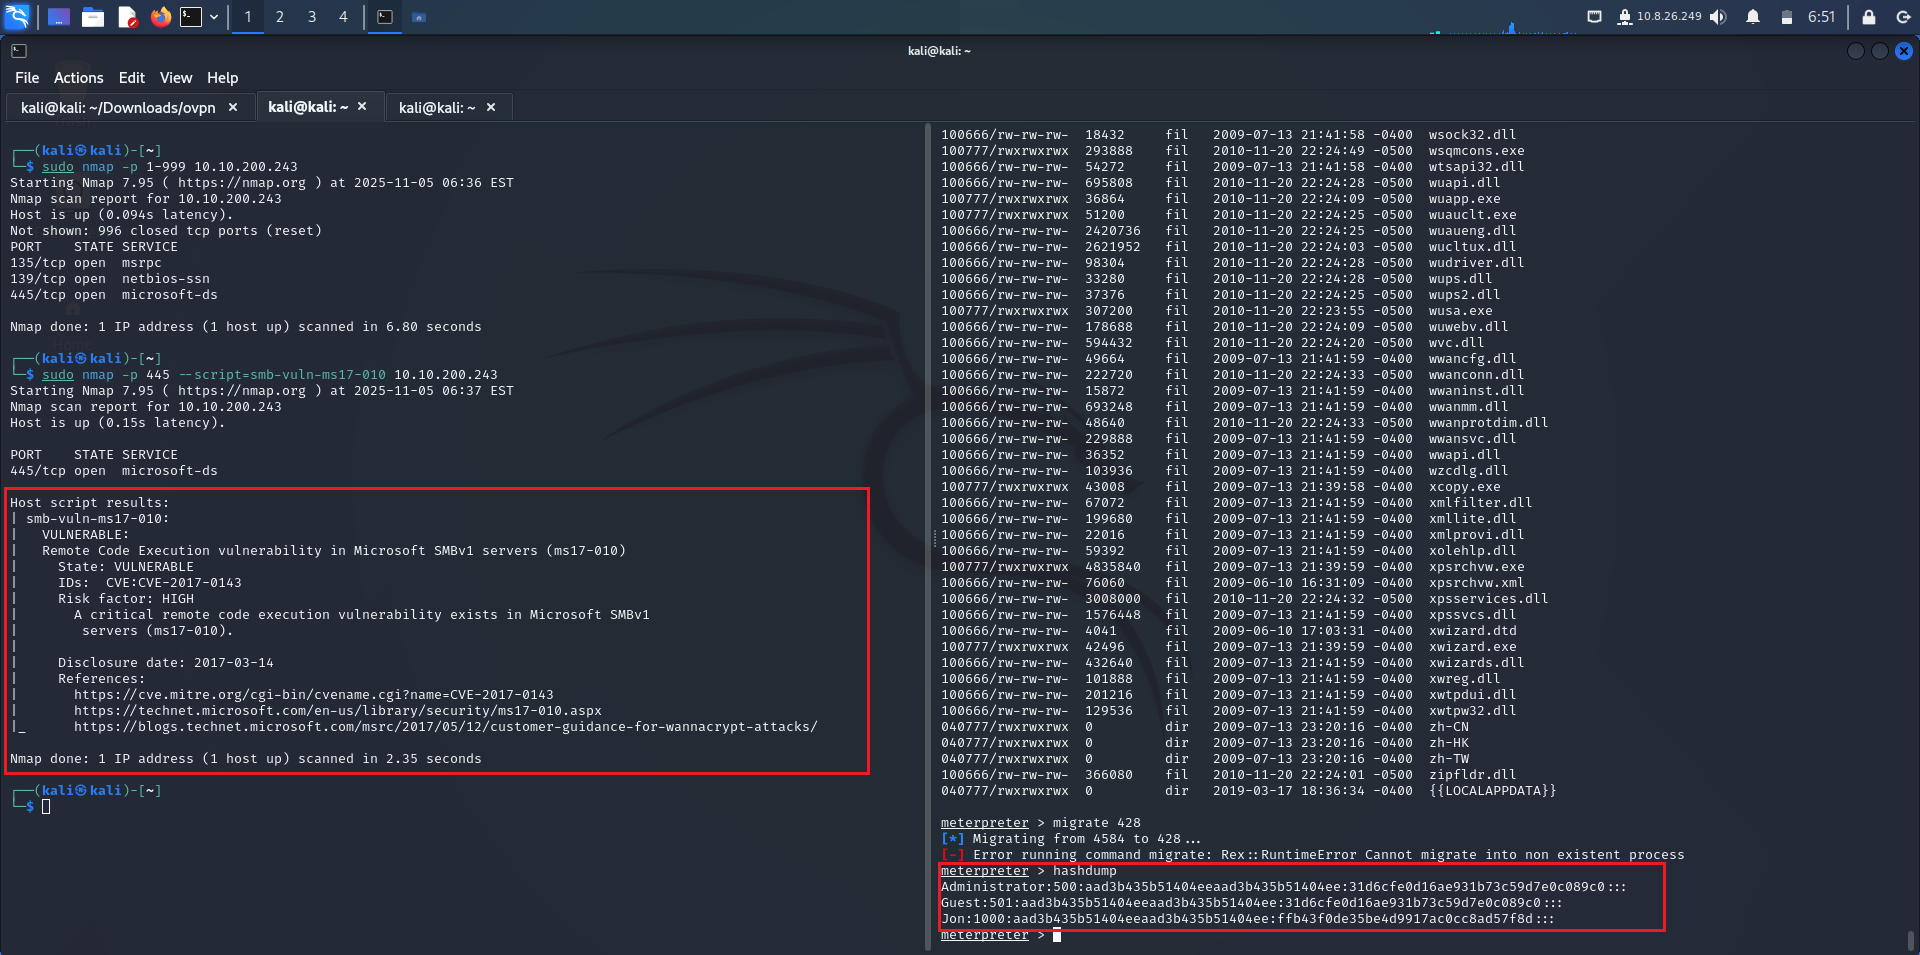 firetemple/blackash-cve-2017-0144
CVE-2017-0144
 ernos/browser-xpi-malware-scanner
A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…
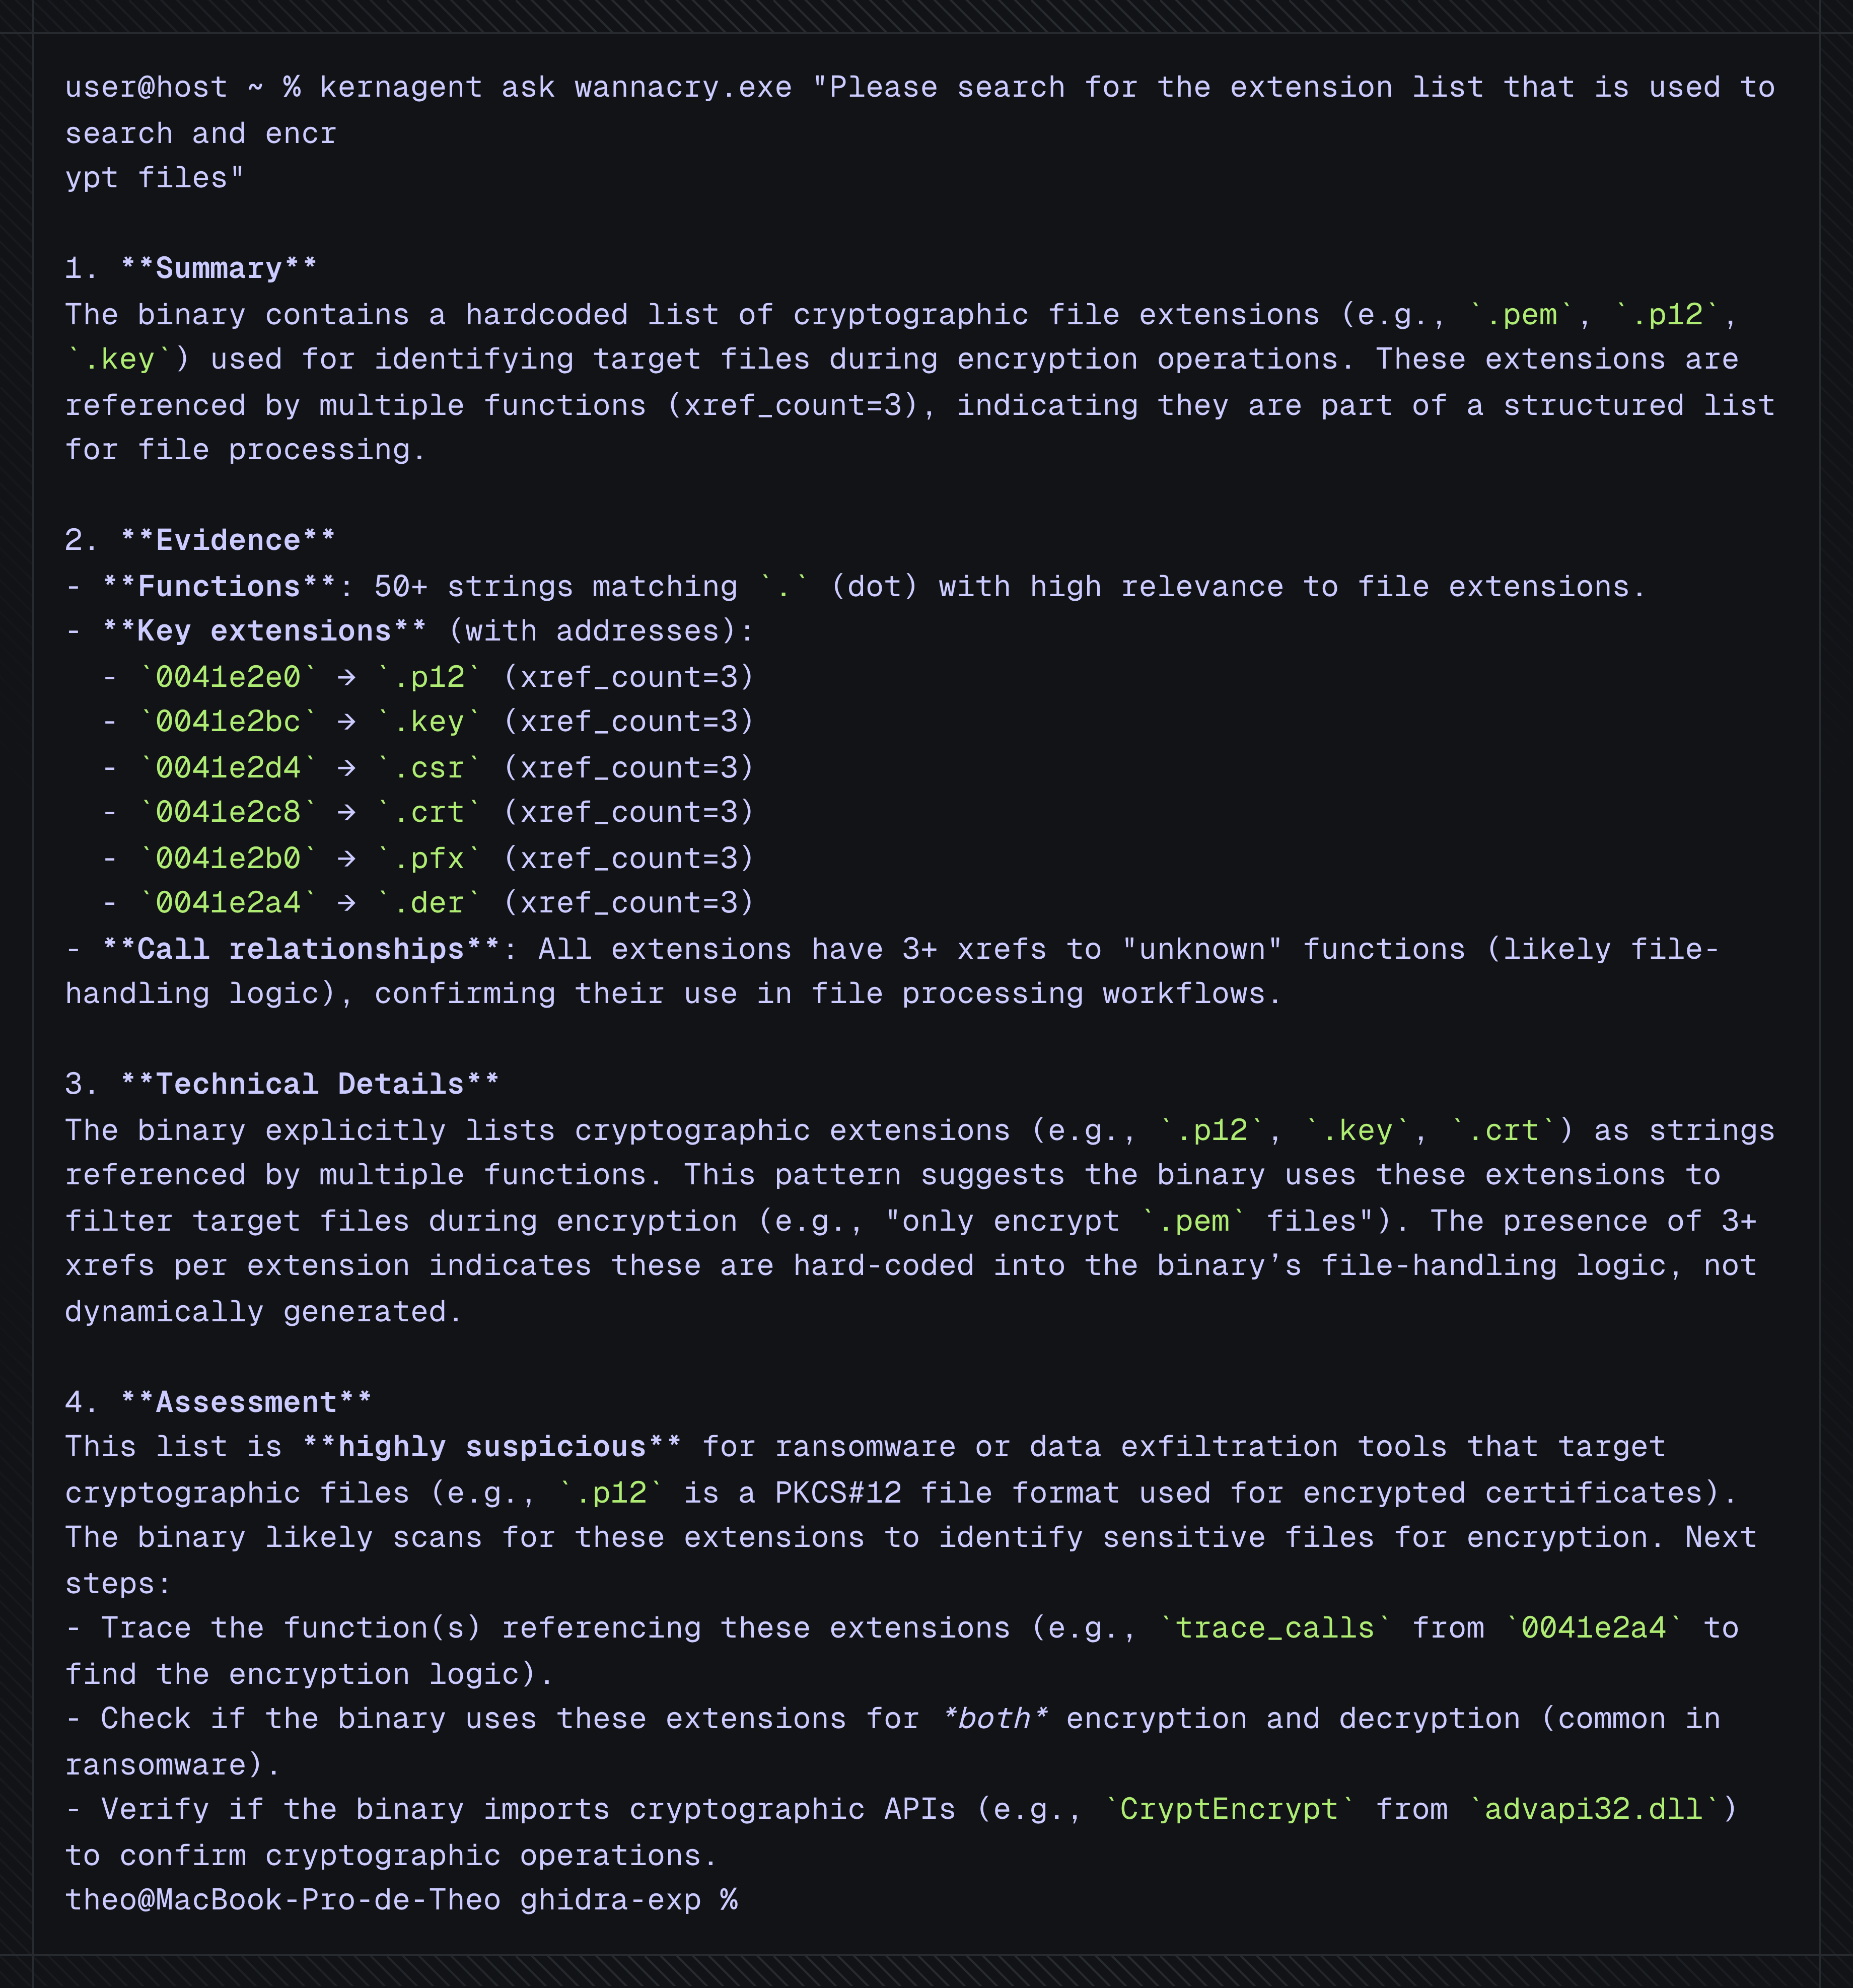 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.
 eonraider/blackhat-python3
Source code for the book "Black Hat Python" by Justin Seitz. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 mandiant/flare-floss
FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
 secrary/ssma
SSMA - Simple Static Malware Analyzer [This project is not maintained anymore by me]
 mishra0230/cve-2023-38831
CVE-2023-38831 - WinRAR
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 aidilzlkfli/scanning
Analysis of network scan results, service vulnerabilities, OS fingerprinting, and critical Nessus findings including Ghostcat (CVE-2020-1938).
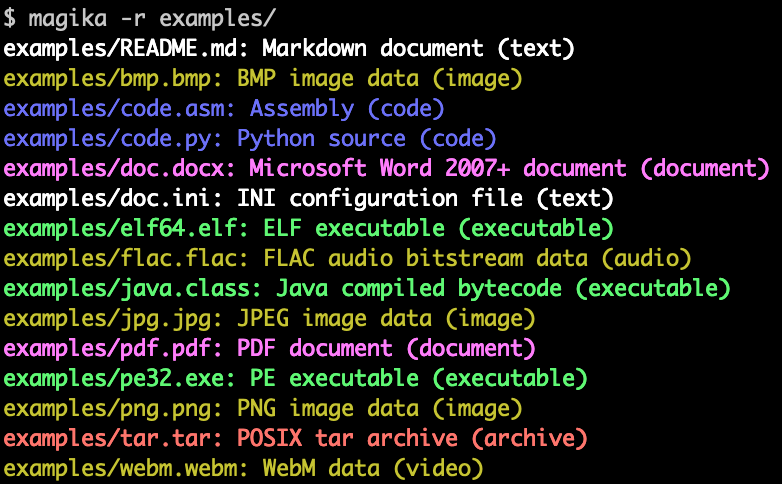 google/magika
Fast and accurate AI powered file content types detection