
workshop_firmware_reverse_engineering
 emproof-com/workshop_firmware_reverse_engineering
Workshop on firmware reverse engineering
binary-analysiseducationembedded-systems-security+6
451
emproof-com/workshop_firmware_reverse_engineeringWorkshop on firmware reverse engineering
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
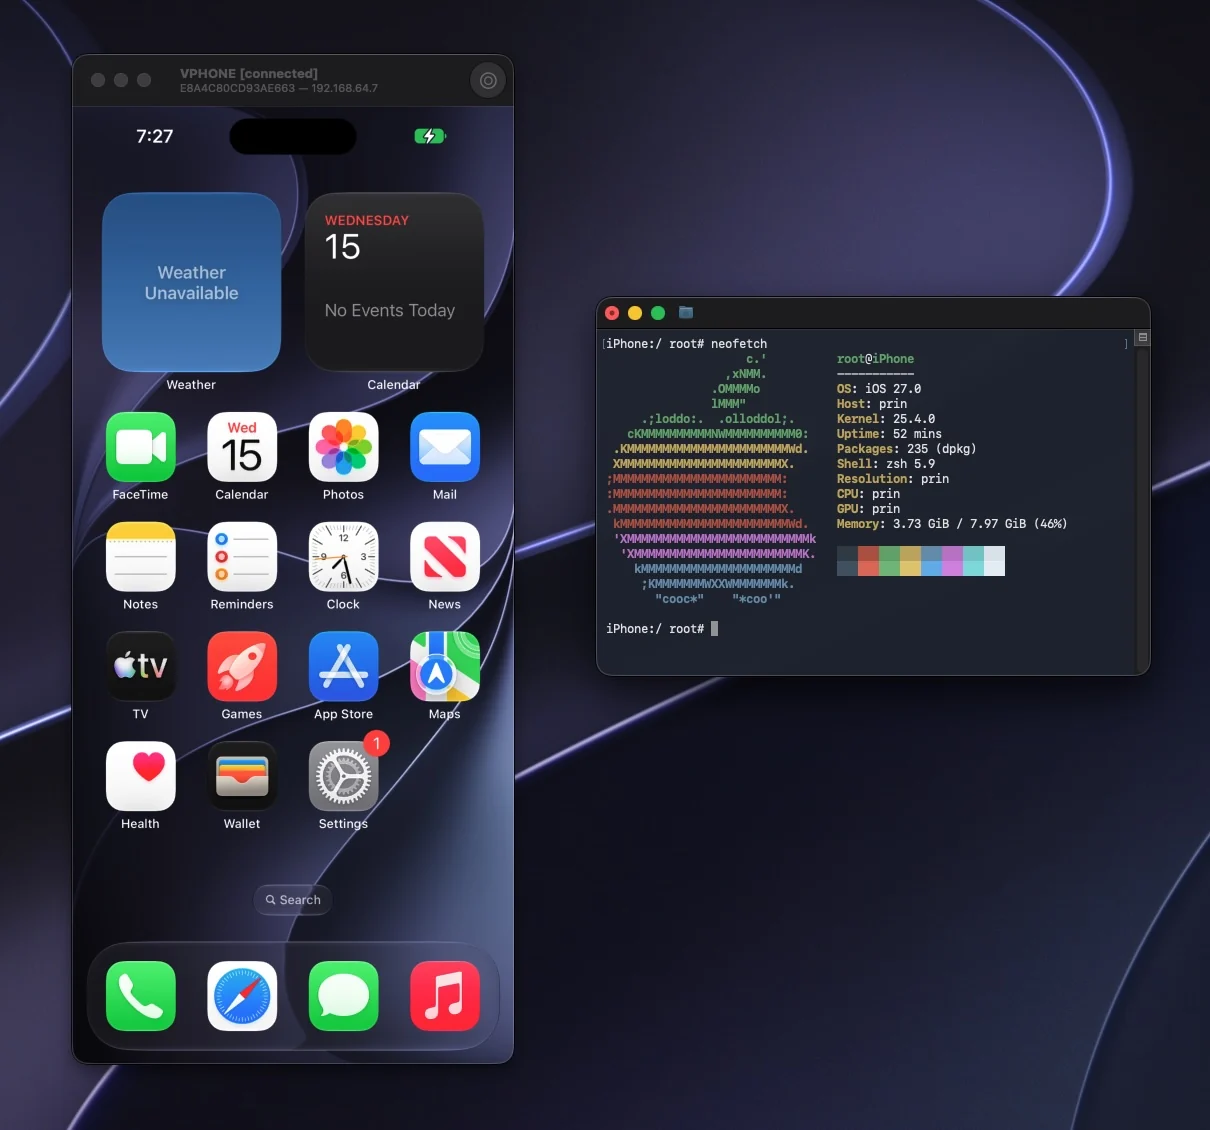 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 trungnguyen1909/qemu-t8030
iPhone 11 emulated on QEMU
 bazad/ida_kernelcache
An IDA Toolkit for analyzing iOS kernelcaches.
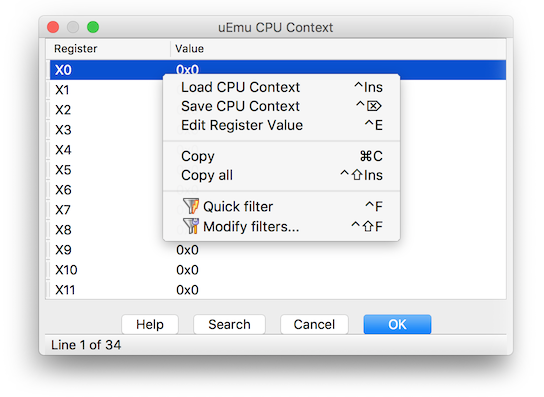 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
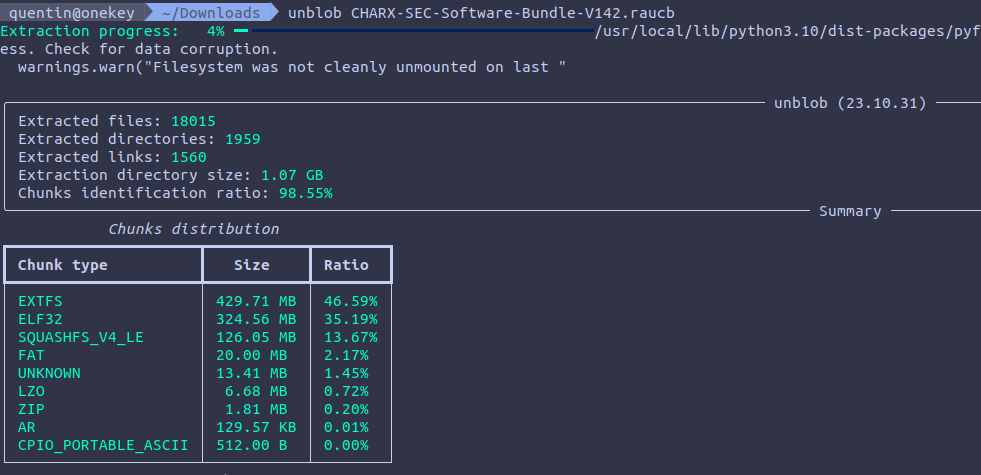 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 xairy/lights-out
Tools for controlling webcam LED on ThinkPad X230
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 asarr22/root-my-galaxy-s938b
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 sunrayvision/vision-msi-thermal-control
MSI Modern 15H AI C1MGT-096IT Linux thermal management - Reverse engineered EC control with fan profiles and battery threshold
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
 cyber-defence-campus/netgear_r6700v3_circled
Demonstrate some functionalities of Morion by generating an exploit for CVE-2022-27646 (stack buffer overflow on Netgear R6700v3 routers).
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 zgsnj123/cve-2025-45467
Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…