
mousejack
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
exploitationfirmware-analysishardware-iot-security+3
bastilleresearch/mousejackResearch tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
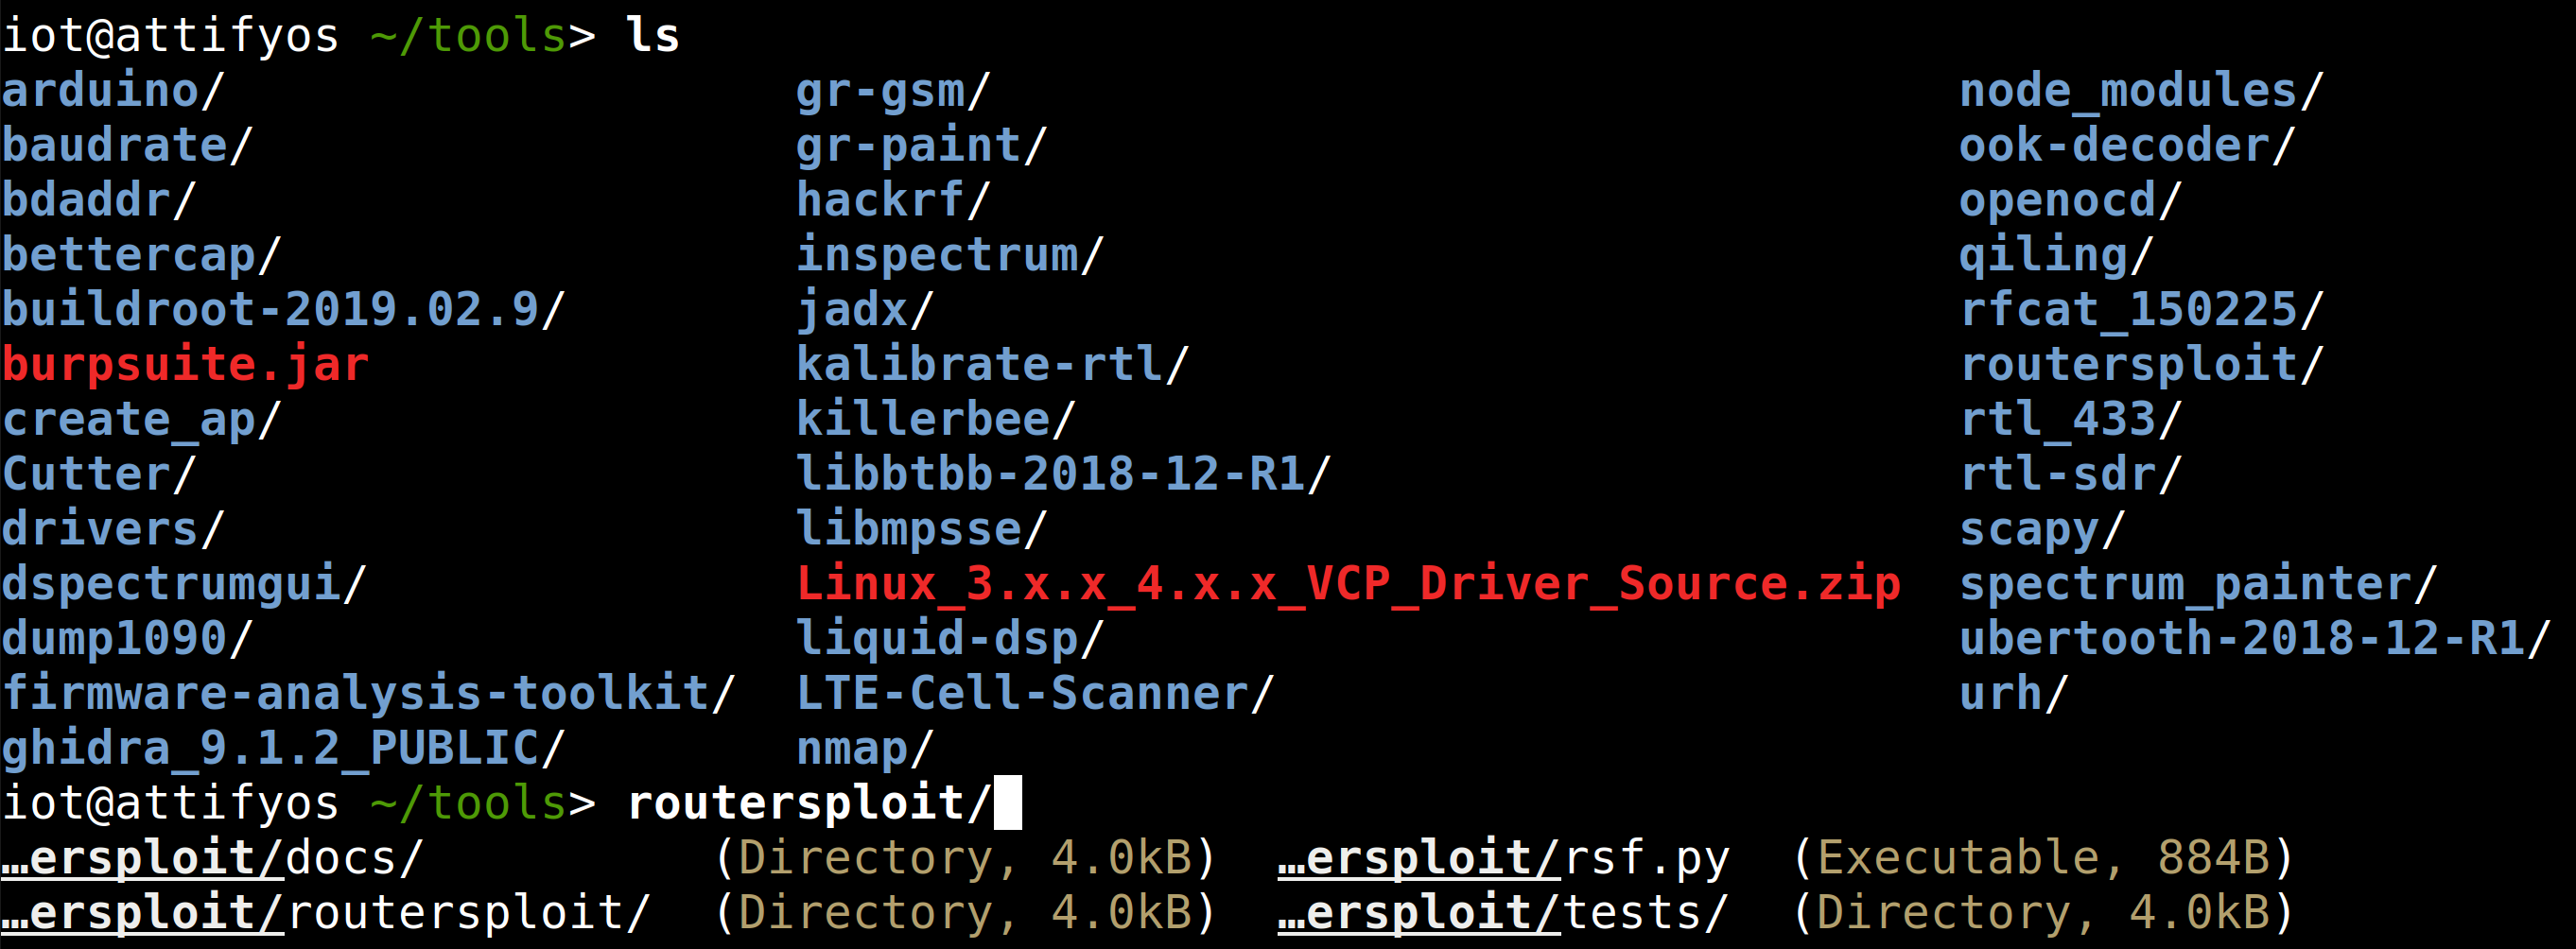 adi0x90/attifyos
Attify OS - Distro for pentesting IoT devices
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 fans0n-fan/treck20-related
PoC for CVE-2020-11896 Treck TCP/IP stack and device asset investigation
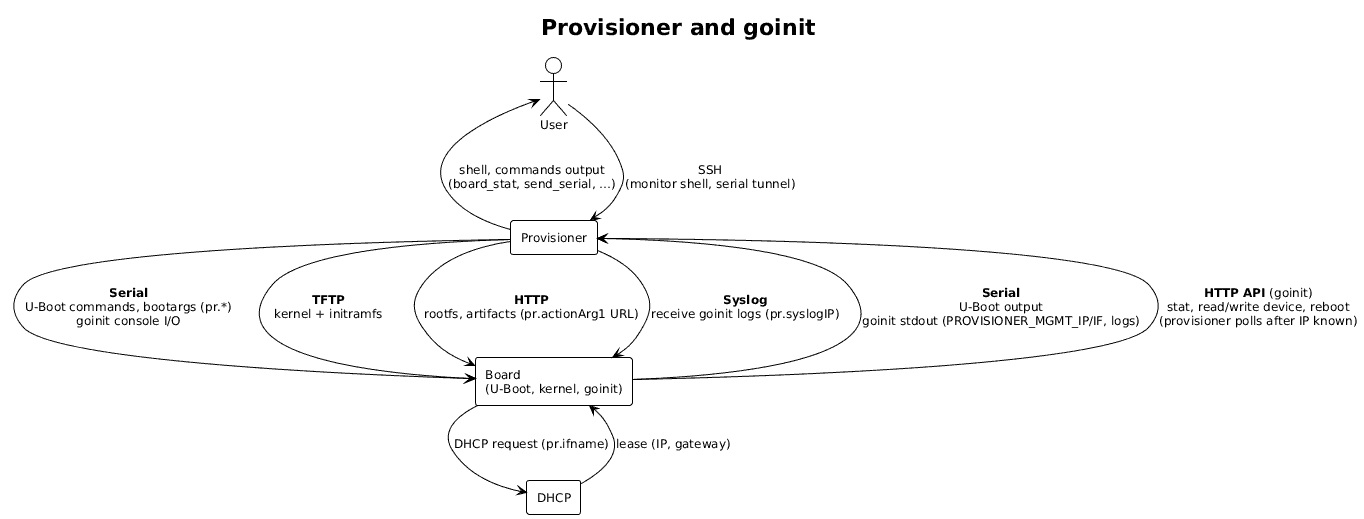 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 lukejenkins/cve-2022-24693
Documentation and reproduction steps for CVE-2022-24693: hardcoded credentials in Baicells Nova436Q and Neutrino 430 firmware, enabling remote SSH…
 infobyte/nec_aterm_tools
Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.
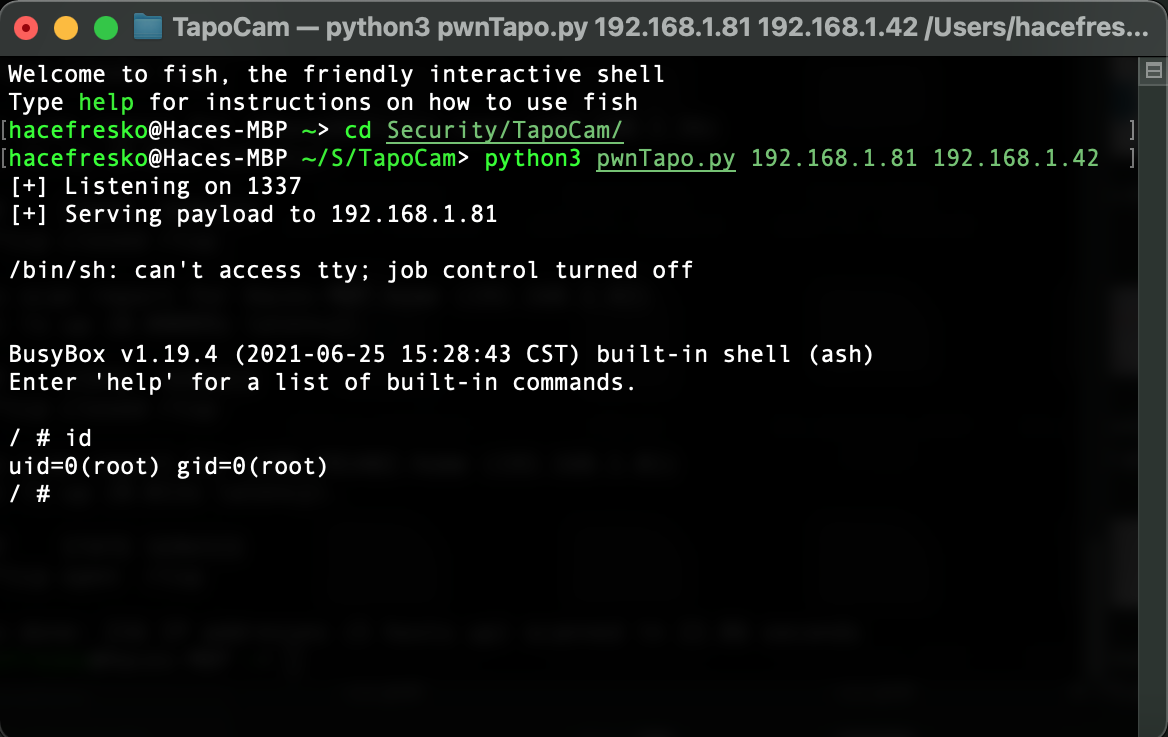 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 zgsnj123/cve-2025-45467
Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…
 spiralbl0ck/sigint_through_brother_printers
Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 nmatt0/moria
IoT firmware identification and extraction
 minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 ejfkdev/reyee_decrypt
Decrypt Ruijie ReyeeOS firmware (v1/v2) and encrypted config backups; recover plaintext passwords