
CVE-2025-67399
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
embedded-systems-securityexploitationfirmware-analysis+4
rupeshsurve04/cve-2025-67399Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 sumeetit/cve-2022-20607
In the Pixel cellular firmware, there is a possible out of bounds write due to a missing bounds check. This could lead to remote code execution with…
 abandon1337/cve-2024-0762
Proof-of-concept exploit for CVE-2024-0762, a buffer overflow vulnerability in UEFI firmware, demonstrating exploitation techniques for security…
 myasnik/hardware-hacking-cheatsheet
Hardware Hacking Cheatsheet
 hessandrew/cve-2020-0557_intel-sa-00338
https://www.intel.com/content/www/us/en/security-center/advisory/intel-sa-00338.html
 kaisersource/cve-2021-3166
Proof-of-concept exploit for CVE-2021-3166 targeting ASUS DSL-N14U routers via malicious firmware upload, triggering a denial-of-service condition.
 risuxx/cve-2023-34853
Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…
 justinsteven/cve-2020-10759-poc
Proof of Concept for CVE-2020-10759 (fwupd signature validation bypass)
 fallenskill1/cve-2024-22853
D-LINK Go-RT-AC750 GORTAC750_A1_FW_v101b03 has a hardcoded password for the Alphanetworks account, which allows remote attackers to obtain root…
 icycu123/cve-2024-1781
CVE-2024-1781
 nevercodecorrect/lede-17.01.3
Version-contains-cve-2019-12272
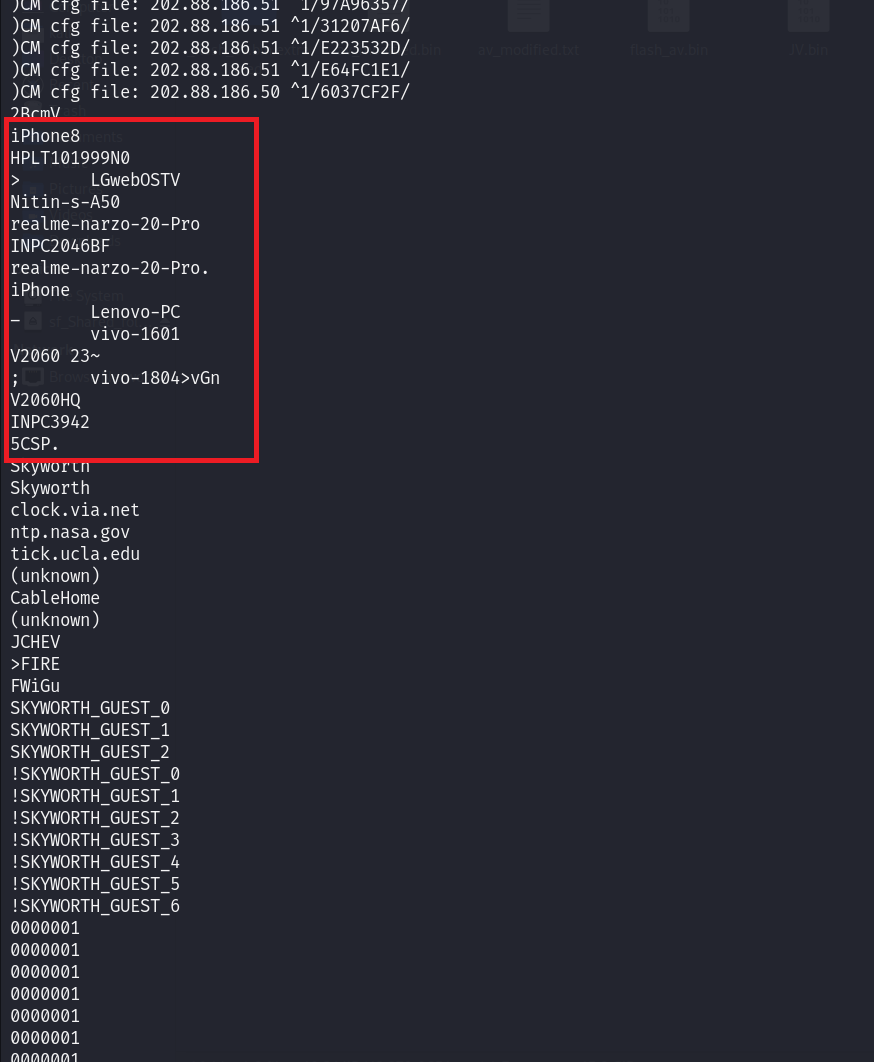 nitinronge91/sensitive-information-disclosure-via-spi-flash-firmware-for-hathway-router-cve-2024-46383
CVE-2024-46383
 pauljrowland/bootholefix
This script will remediate the BootHole bug identified in CVE-2020-25632 and/or CVE-2021-20233.
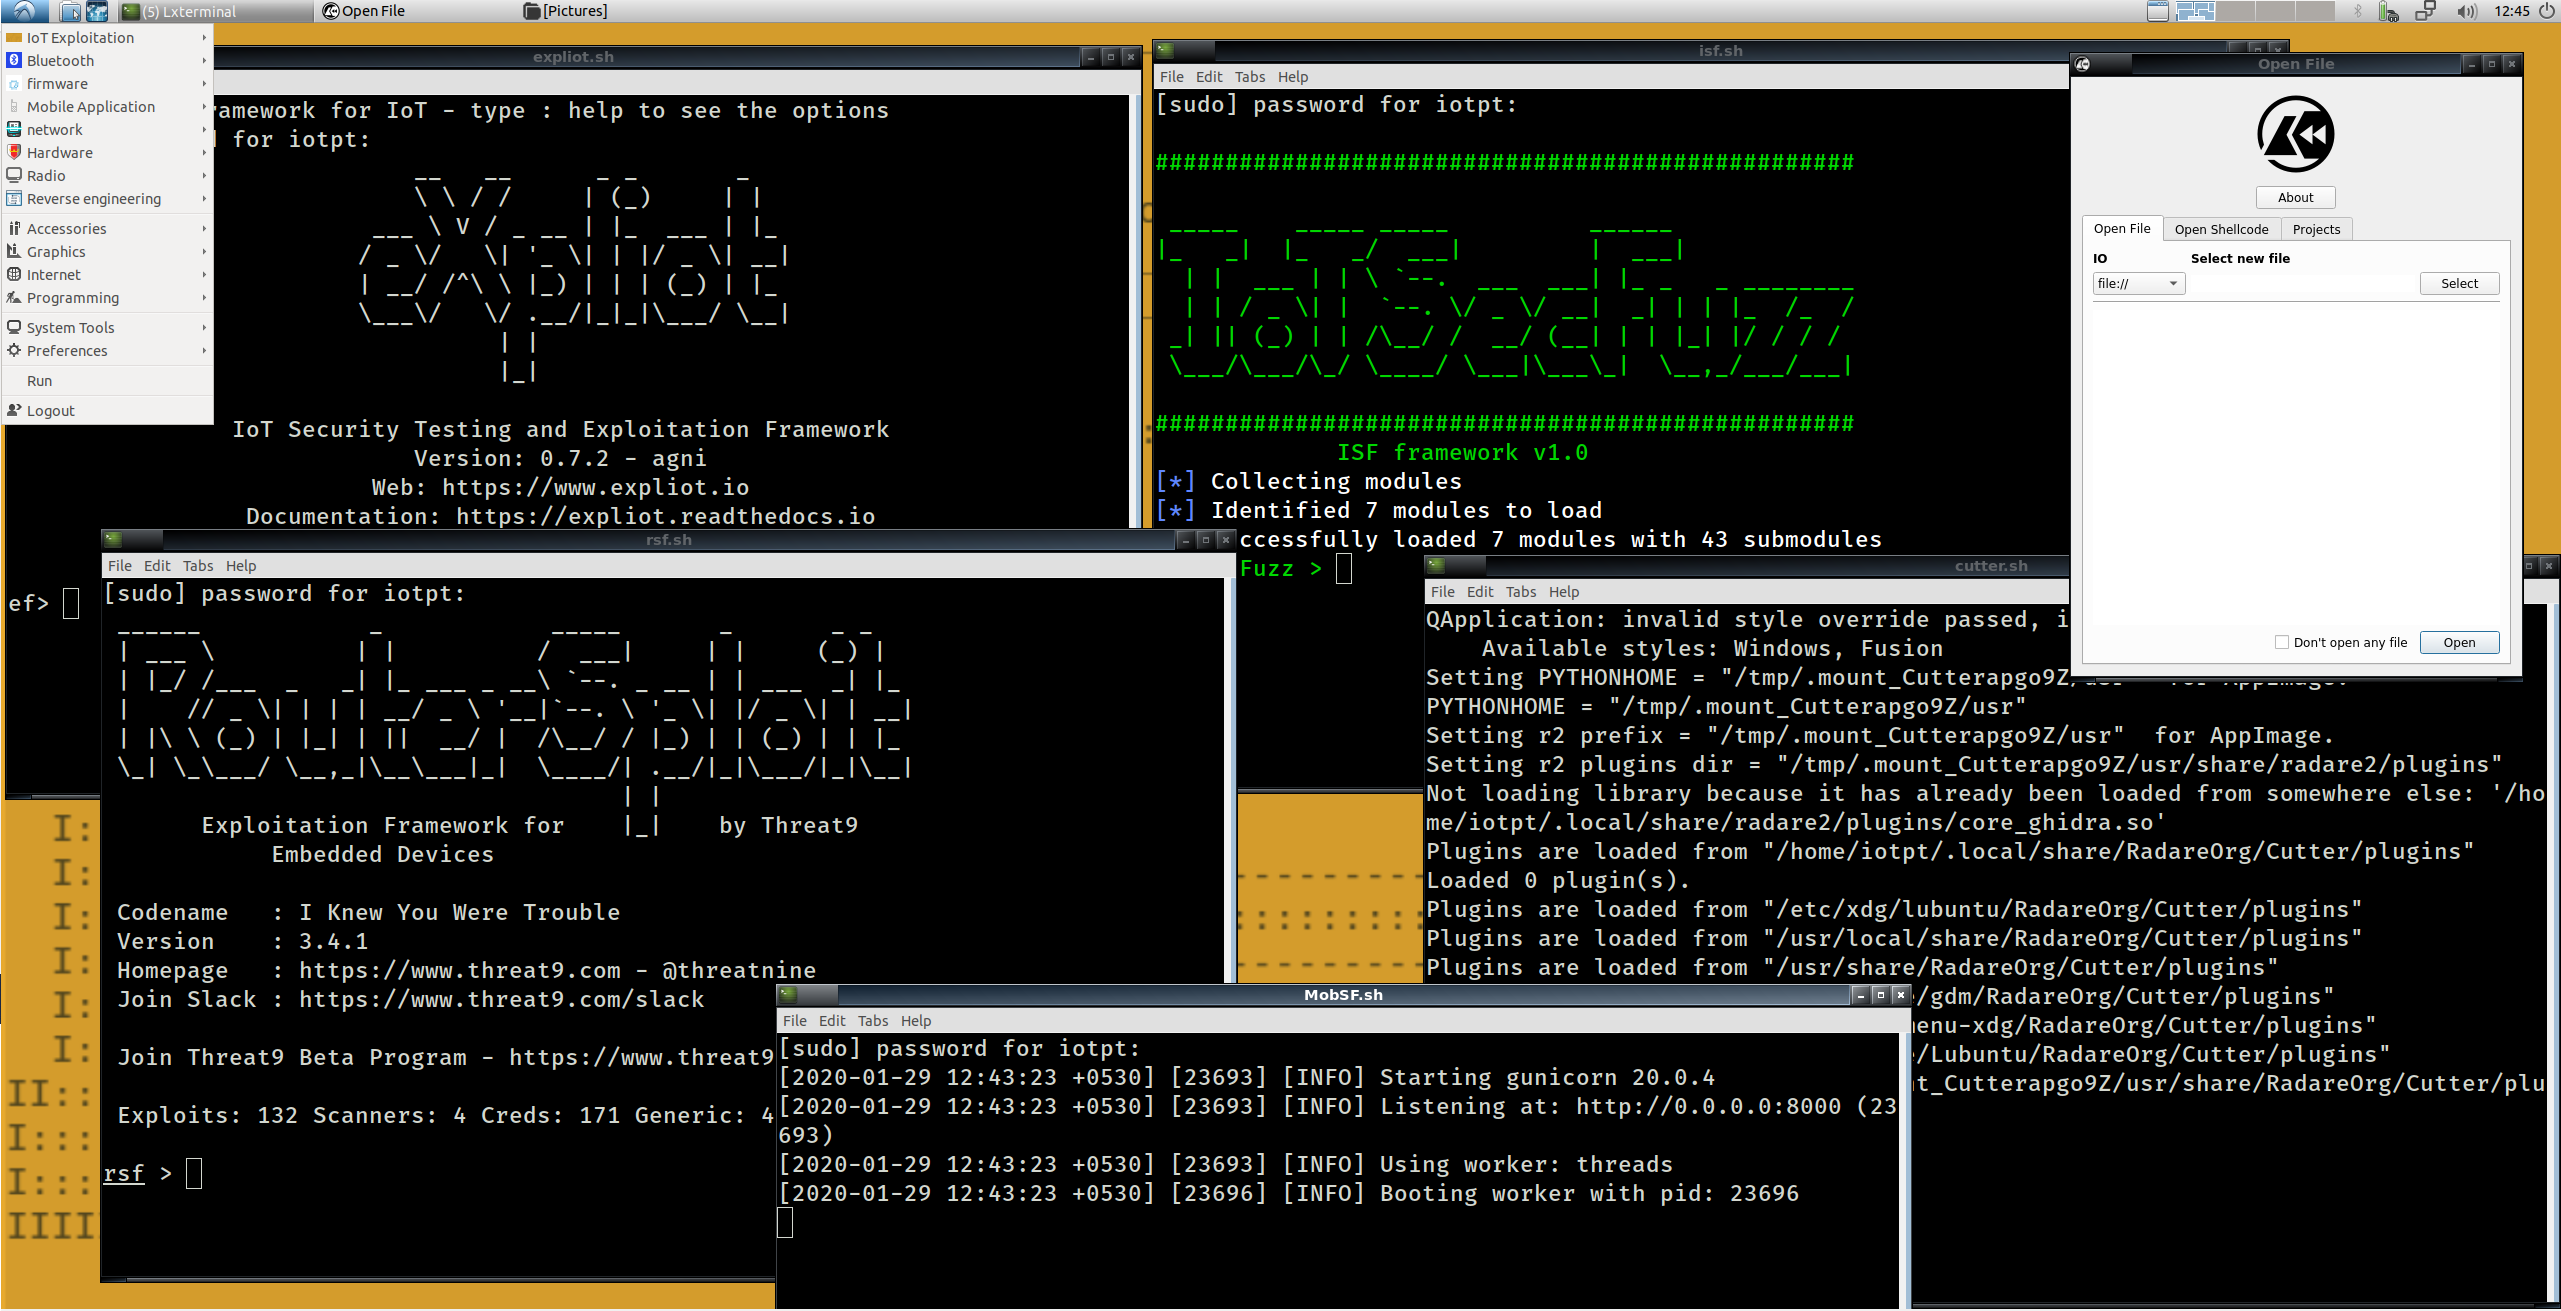 iot-ptv/iot-pt-v1
A Virtual environment for Pentesting IoT Devices
 linuxoid-cn/mi8e5-unlocker-by-cve-2026-43499
基于 CVE-2026-43499 的 8E5 机型自动化解锁辅助工具,仅限授权安全研究与自有设备使用。
 microsoft/hvloader
HvLoader.efi is an EFI application for loading an external hypervisor loader
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 ptresearch/inteltxe-poc
Intel Management Engine JTAG Proof of Concept