

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy

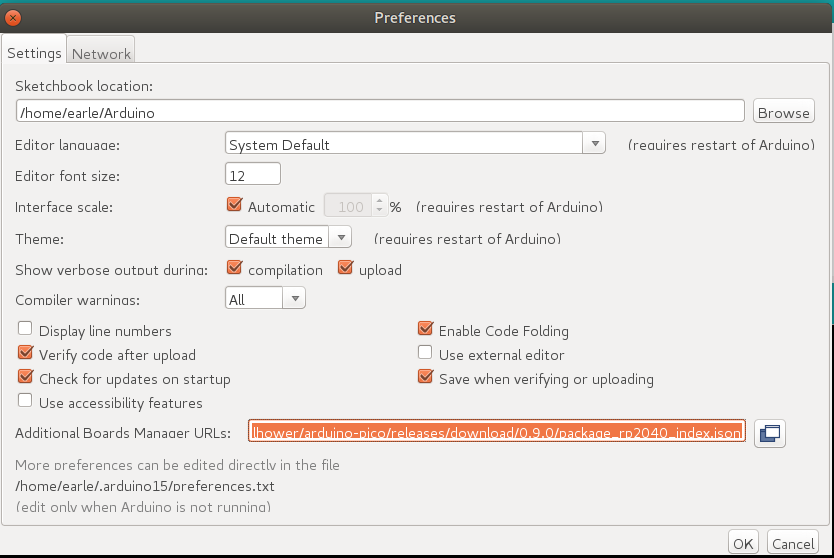 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 ricardoquesada/regenerator2000
An interactive disassembler for the CPU 6502, focused on Commodore 8-bit computers. Features a TUI with modern features like x-ref, undo/redo, flow…
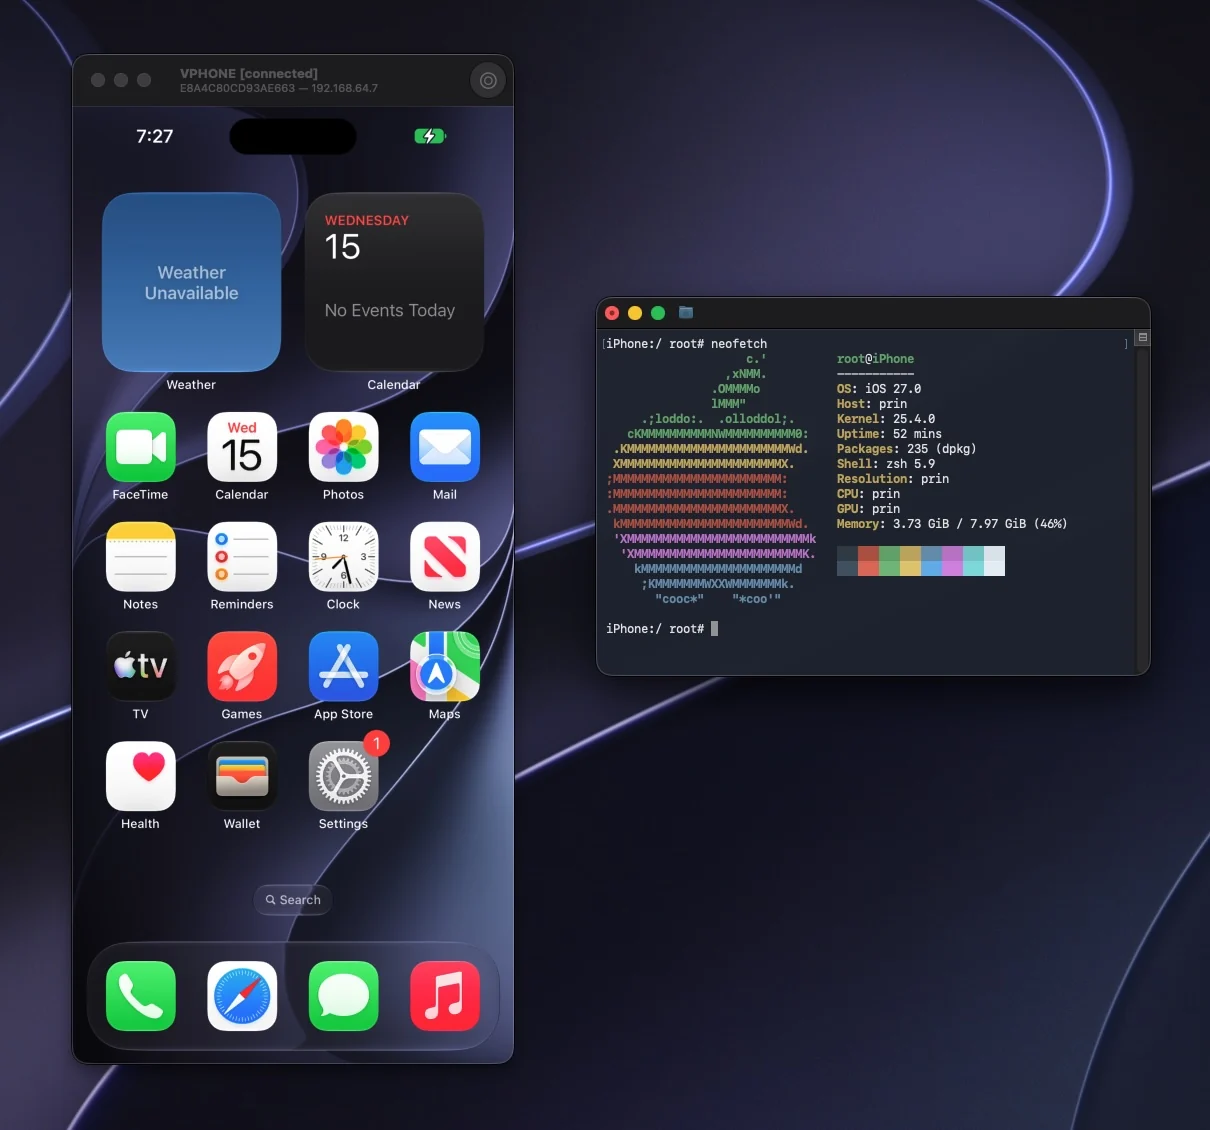 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
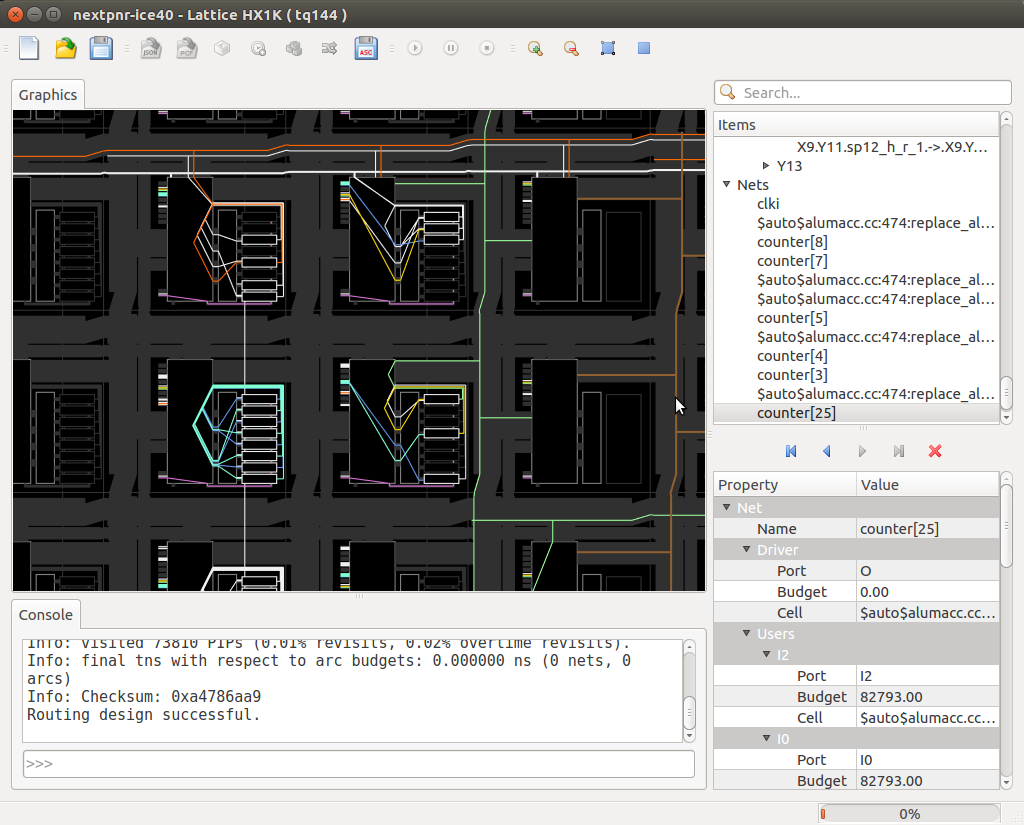 yosyshq/nextpnr
nextpnr portable FPGA place and route tool
 heapframe/seetong-ts81xxd3x-rce
CVE-2026-100886 | Unauthenticated Remote Code Execution toolkit.

 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 wolfssl/wolfssl
The wolfSSL library is a small, fast, portable implementation of TLS/SSL for embedded devices to the cloud. wolfSSL supports up to TLS 1.3 and DTLS…
 nmatt0/moria
IoT firmware identification and extraction
 angr/angr
A powerful and user-friendly binary analysis platform!