
ESP32-Bit-Pirate
 geo-tp/esp32-bit-pirate
A Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
bluetooth-securitydebuggersembedded-systems-security+5
6.0k
geo-tp/esp32-bit-pirateA Hardware Hacking Tool with Web-Based CLI That Speaks Every Protocol
 nmatt0/moria
IoT firmware identification and extraction
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 mrhenrike/embedxpl-forge
Embedded Device Security Assessment Framework — 700 modules, 350 CVEs, 55 vendors, APT Group Engine. Covers routers, IP cameras, GPON ONTs, ISP CPEs,…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 ejfkdev/reyee_decrypt
Decrypt Ruijie ReyeeOS firmware (v1/v2) and encrypted config backups; recover plaintext passwords
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 yeet-src/usbsnoop
Live, system-wide USB transfer sniffer in eBPF — decodes USB traffic inline (control SETUP, SCSI, HID) from two universal URB hooks. No usbmon, no…
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 ransc0rp1on/ripple20
This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…
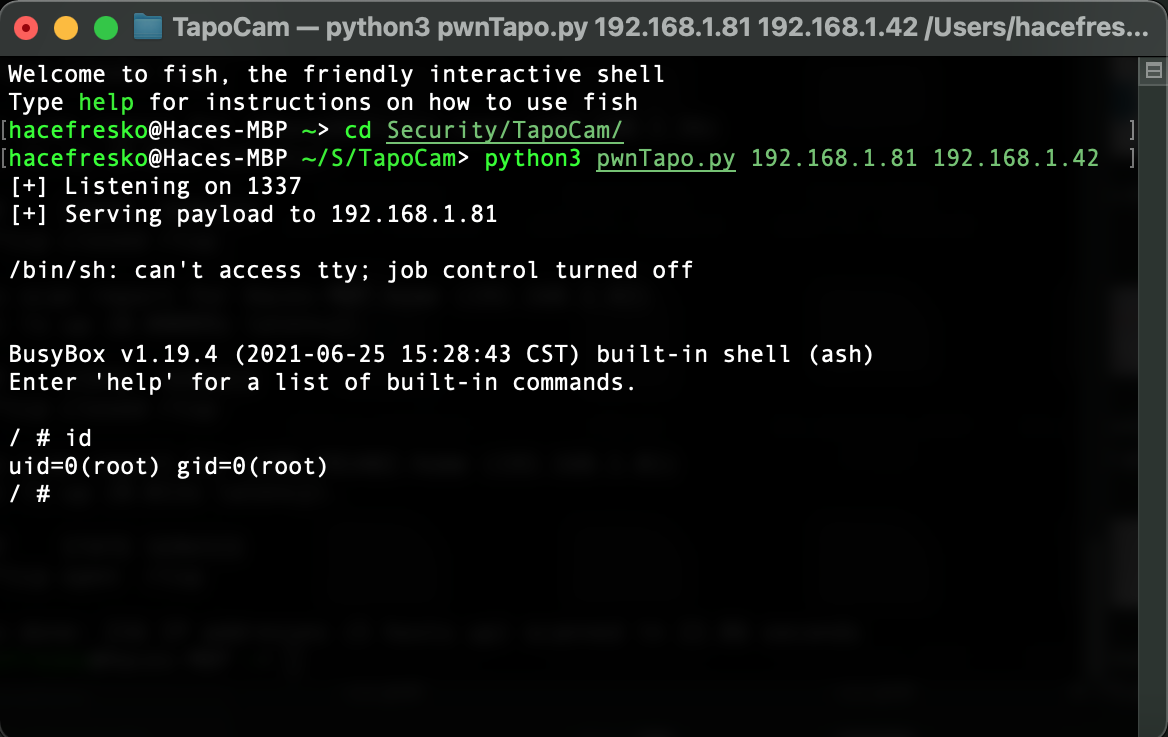 kaleth4/cve-2021-4045
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
 minanagehsalalma/cve-2021-21735-zte-zxhn-h168n-admin-compromise
CVE-2021-21735 write-up: ZTE ZXHN H168N V3.5 wizard-page information leak, firmware routing flaw, and the path from exposed PPPoE/WLAN data to full…
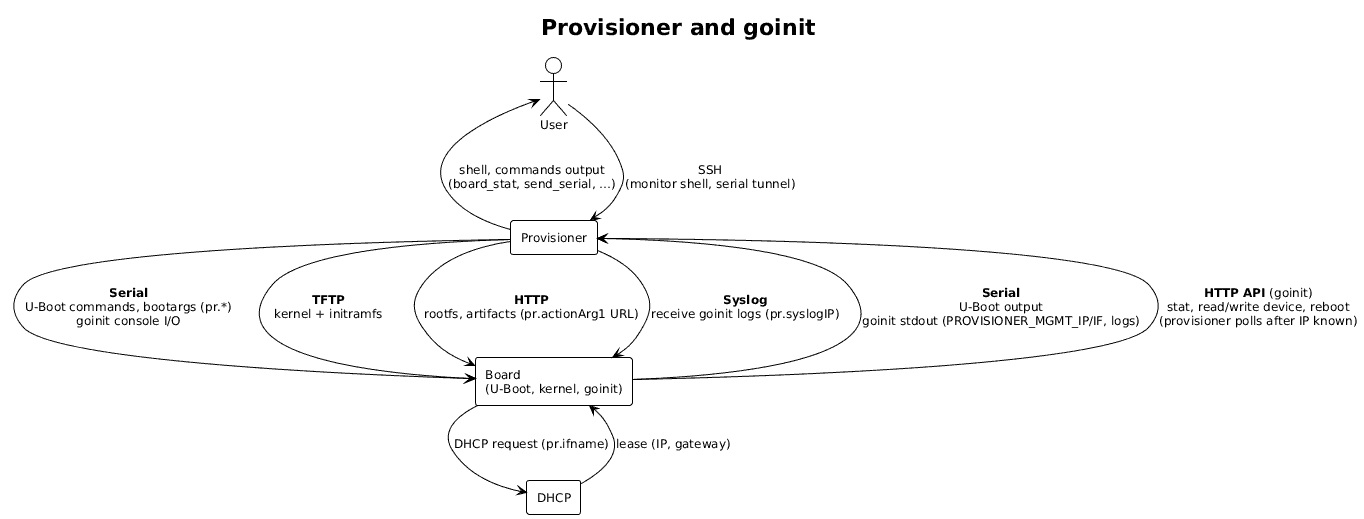 alessandrocarminati/provisioner
Provisioning and sharing system for SBCs
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 4d000/tenda-f3-v4
Python script to exploit CVE-2020-35391 on Tenda F3 V3/V4 routers, enabling unauthorized download of configuration, flash, and syslog files.
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…