

pwndbg
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
ai-assisted-reversingbinary-analysisbinary-exploitation+12
pwndbg/pwndbgExploit Development and Reverse Engineering with GDB & LLDB Made Easy
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 mandiant/flare-vm
A collection of software installations scripts for Windows systems that allows you to easily setup and maintain a reverse engineering environment on…
 quarkslab/conf-presentations
Quarkslab conference talks
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 greatscottgadgets/greatfet
GreatFET firmware and host software
 renode/renode
Open-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…
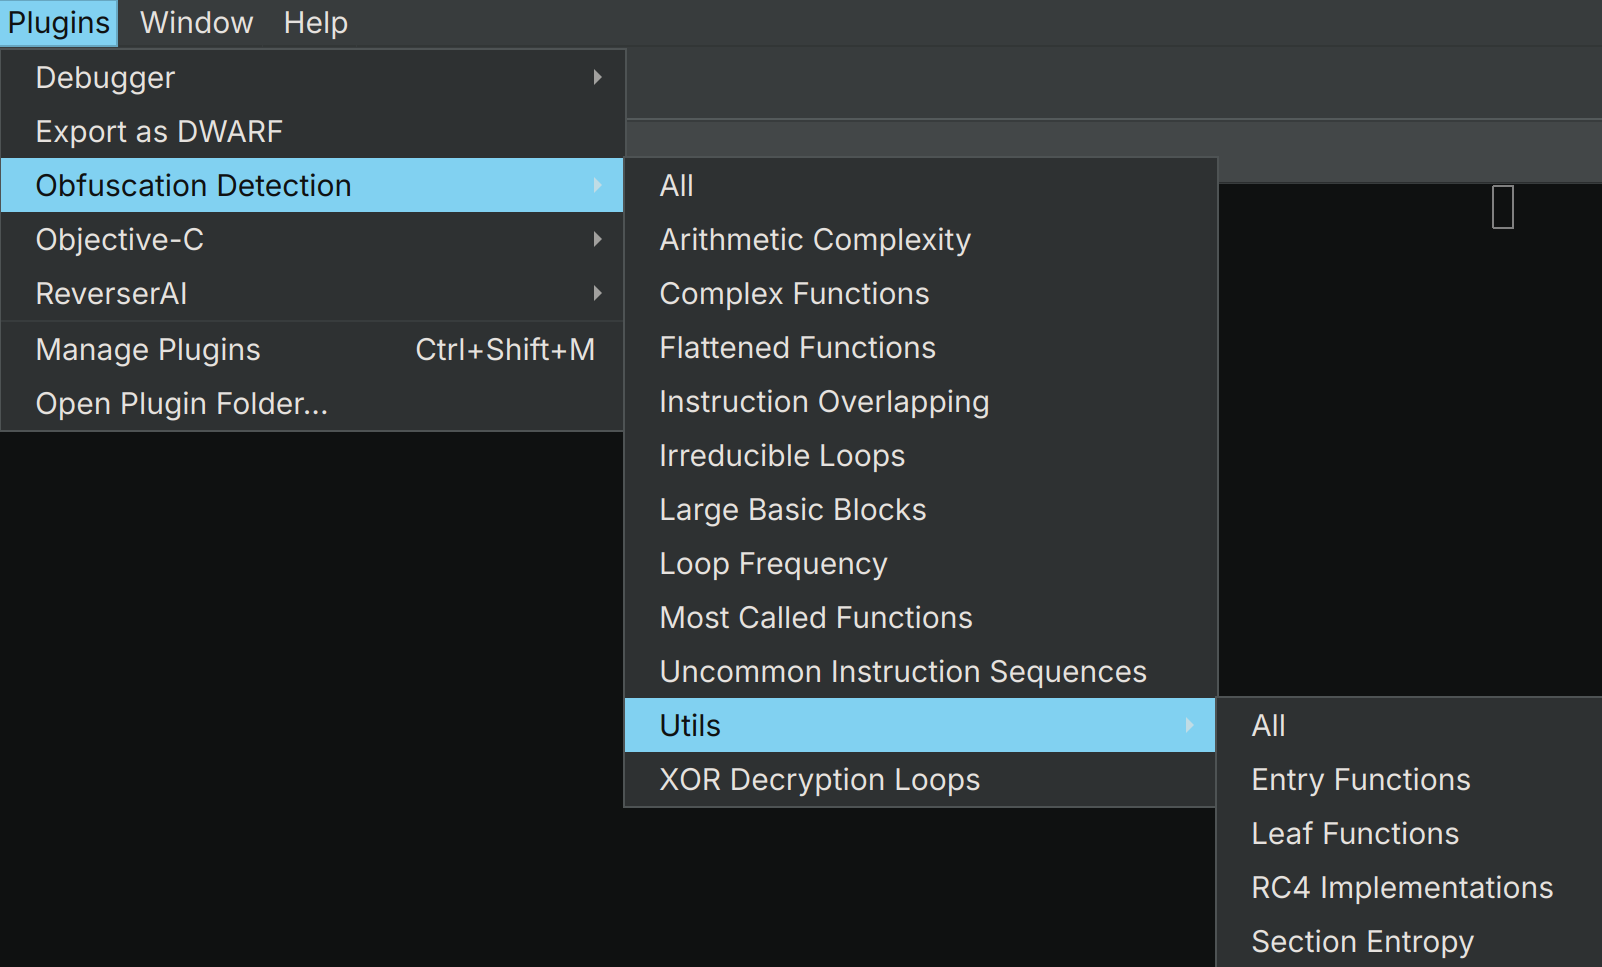 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
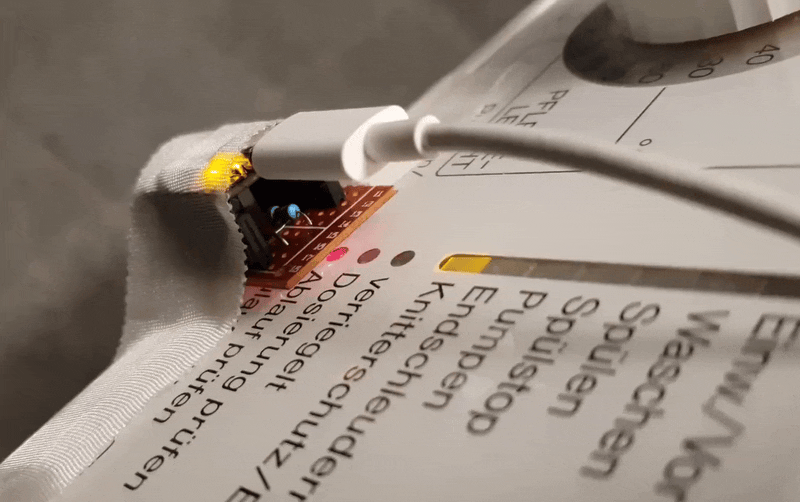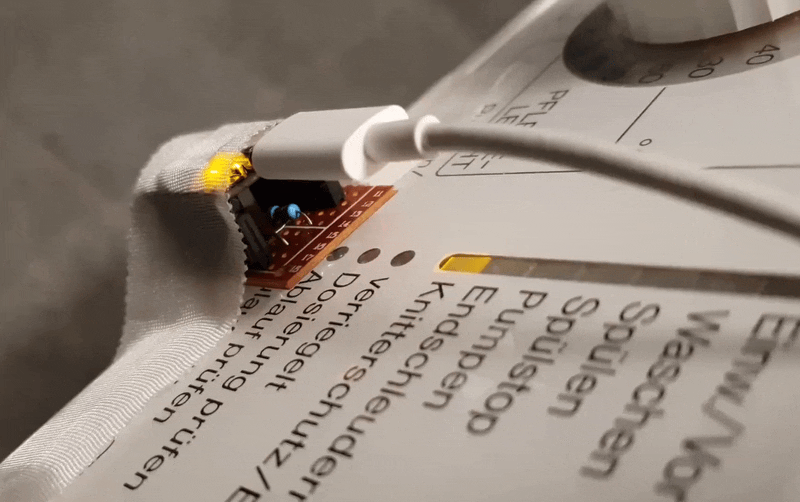 medusalix/freemdu
Open hardware and software tools for communicating with Miele appliances via their optical diagnostic interface
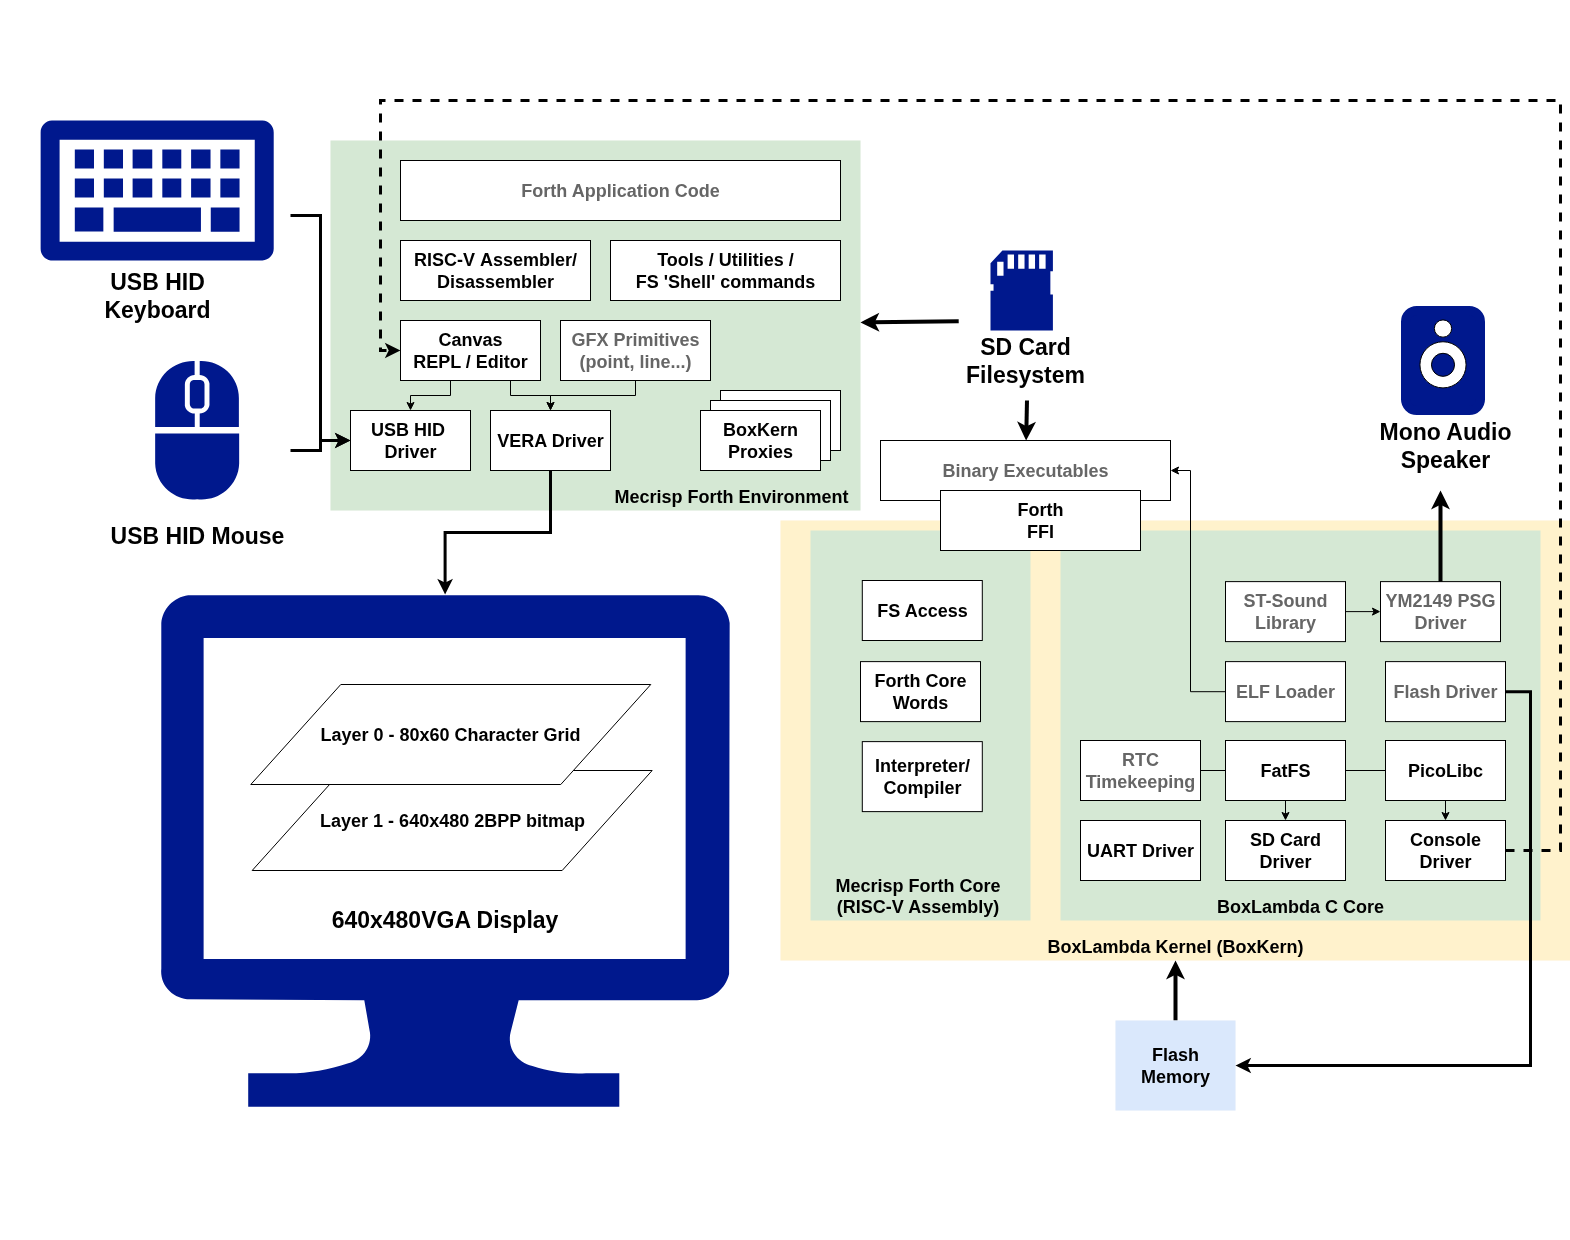 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
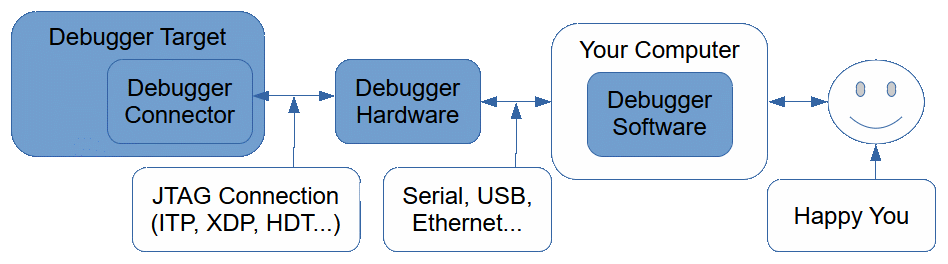 x86-jtag-open-research/x86-jtag-information
Documents Intel and AMD x86 JTAG debugger hardware, connectors, probe software, and target platforms for low-level system debugging and firmware…
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 owasp/iotgoat
Deliberately insecure OpenWrt-based firmware for hands-on IoT security training. Features vulnerability challenges mapped to the OWASP IoT Top 10 for…