Barzakh
 yasindce1998/barzakh
Ring -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
defensive-toolsembedded-systems-securityfirmware-analysis+6
yasindce1998/barzakhRing -4 to Ring 0: offense-defense firmware research platform. We build the bootkits, then we catch them. Closed-loop. Zero trust in silicon.
 wrongbaud/spidump
Tool for reconstructing SPI flash images via logic analyzer captures
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 orbitcurve/firmware-reverse-engineering
Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.
 danyw24/zyxel-p870hn-hardware-hacking
From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 mutur4/unisocbootroms
This is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694
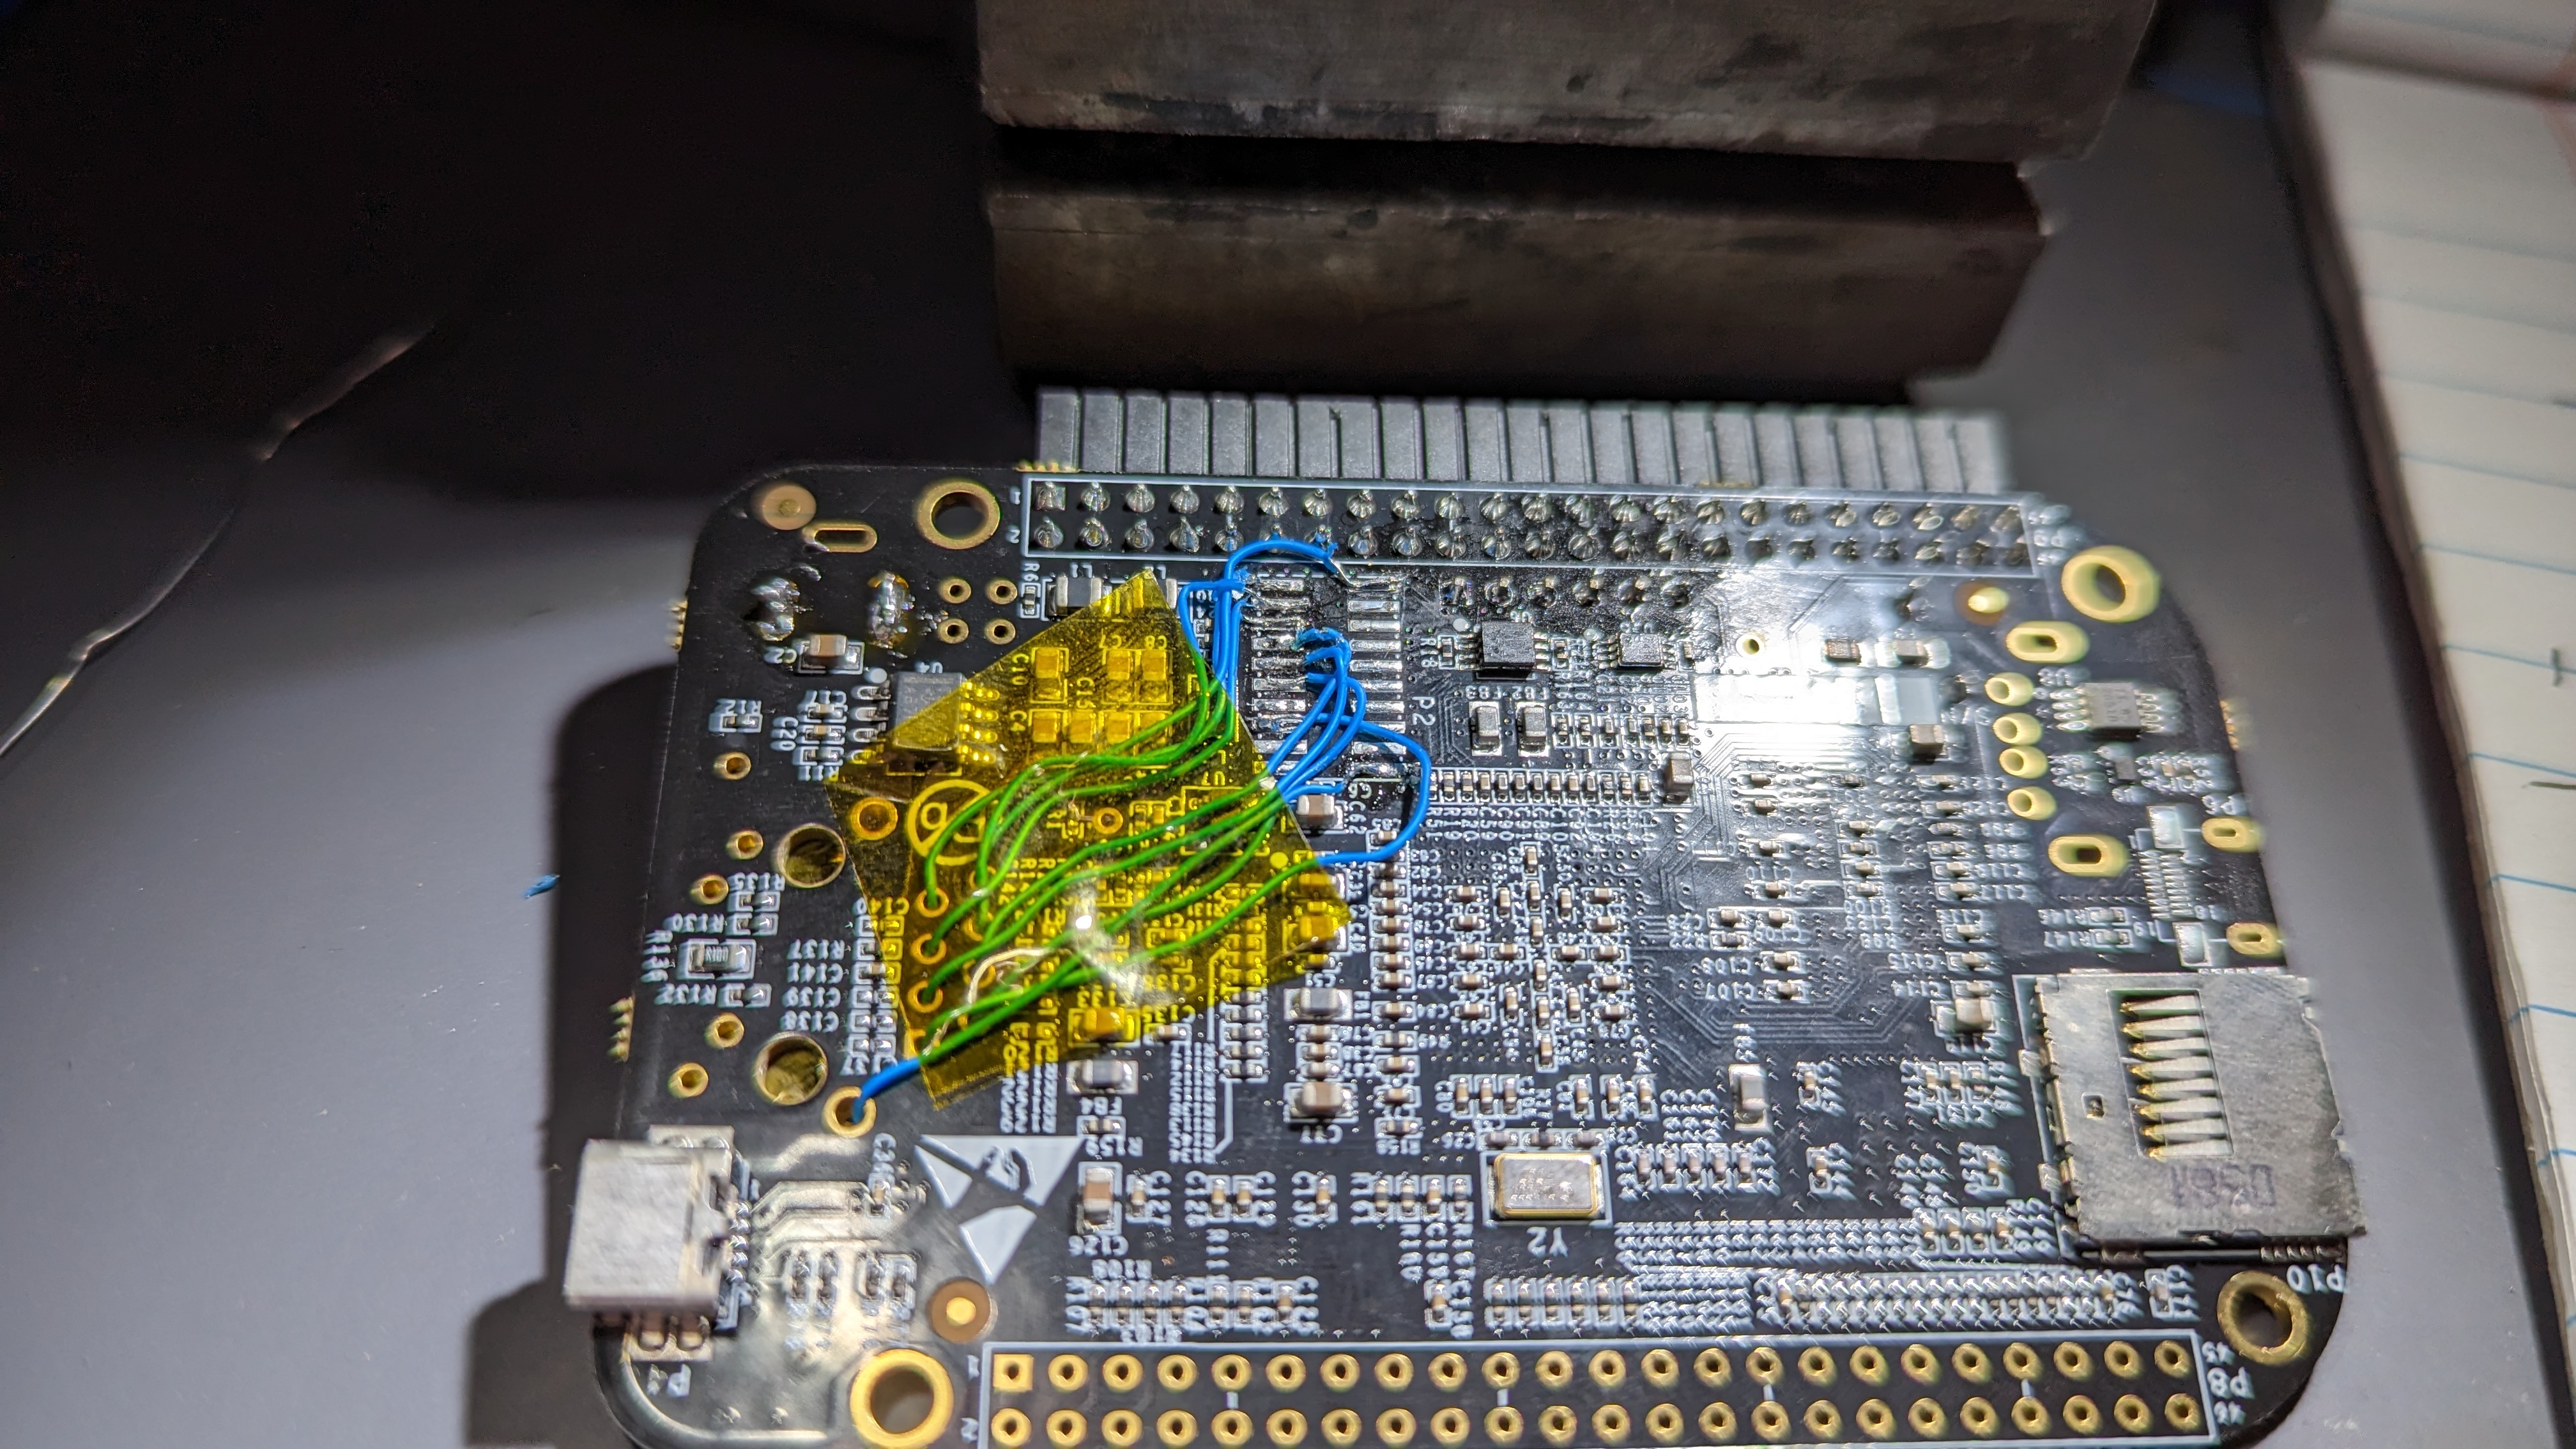 sjgallagher2/am335xbootrom
Reverse engineering the TI AM3358 boot ROM
 george0papasotiriou/cve-2026-21009-ecdsa-nonce-reuse-in-iot-firmware-signing
Educational Python simulation demonstrating ECDSA nonce reuse in IoT firmware signing, showing how an attacker can recover private keys from two…
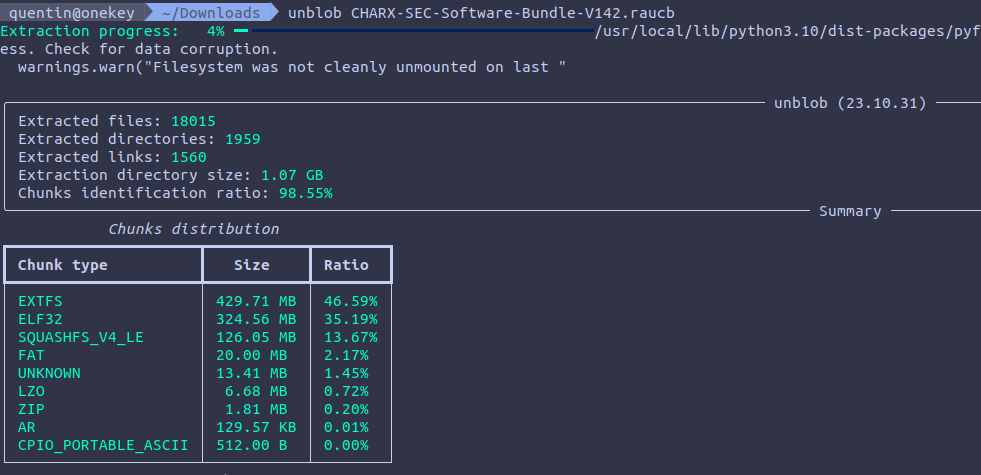 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
 george0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http
Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…