
broadcom-wps
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
embedded-systems-securityfirmware-analysishardware-iot-security+7
308
qkaiser/broadcom-wpsTools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
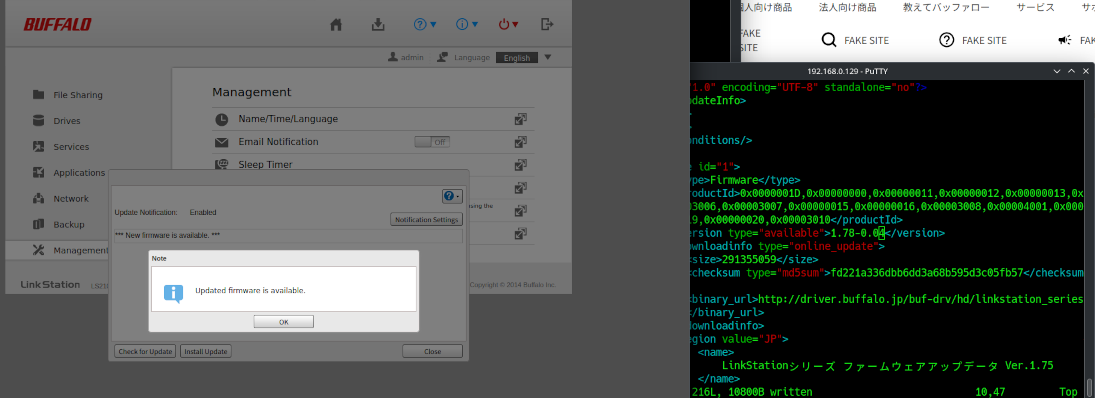 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 jm00nj/hpe-aruba-aos8-vulnerabilities
ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 e-r-butch/f9360-cve43499
SM-F9360 (Galaxy Z Fold4, q4q) locked-bootloader KernelSU root — CVE-2026-43499 temp root → LD_PRELOAD DEFEX bypass → no-LTO clang-12 kernelsu.ko.…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 icicle-emu/icicle
Emulation-based fuzzer for MSP430 firmware that finds and analyzes memory-corruption bugs with detailed crash reports and reproducible inputs.
 george0papasotiriou/cve-2026-8888-printer-firmware-unsigned-update-via-http
Demonstrates CVE-2026-8888, an unsigned printer firmware update over HTTP, including a malicious update server and vulnerable printer emulator for…
 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 ivmks74/iiita-iot-security-research
IoT Security research conducted during my internship at IIIT Allahabad, leading to CVE-2026-65893, CVE-2026-65894, and the CERT-In Vulnerability Note…
 fans0n-fan/treck20-related
PoC for CVE-2020-11896 Treck TCP/IP stack and device asset investigation
 ransc0rp1on/ripple20
This comprehensive package contains everything needed to detect, analyze, and remediate Ripple20 (CVE-2020-11898) vulnerabilities in your…
 rupeshsurve04/cve-2025-67399
Documentation of CVE-2025-67399: physical UART debug interface exploitation on AIRTH Smart Home AQI Monitor (BK7231N SoC) enabling unauthorized…
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
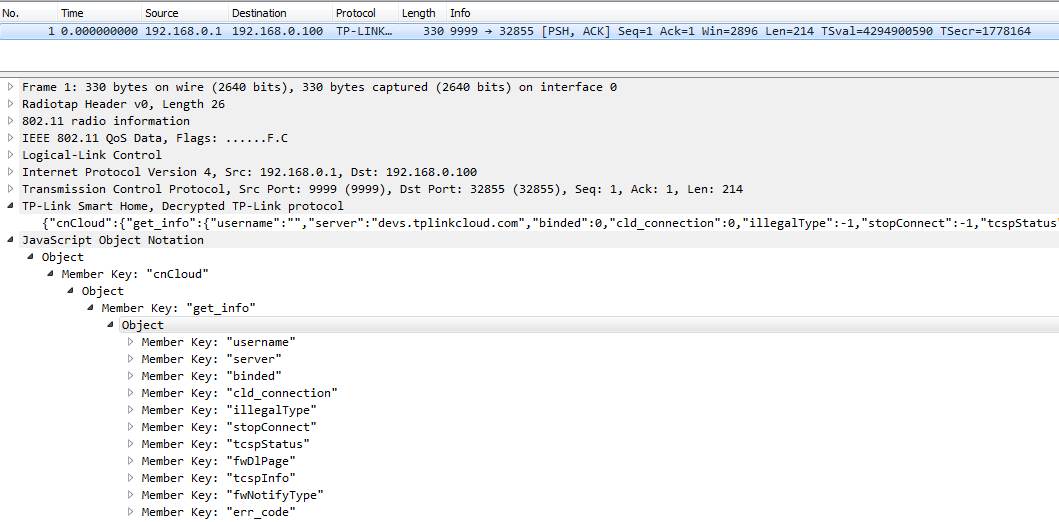 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector