

mcp-reverse
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
ai-assisted-reversingbinary-analysisctf+9
416
1llu50ry/mcp-reverseMCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 jaredreabow/reverse-engineering-with-ai
Research methods for reverse engineering encrypted firmware and software with AI-assisted analysis, independent validation, and public-source…
 alltechdev/mtk-imei-switcheroo
Read and write IMEI records and WiFi/Bluetooth addresses in MediaTek NVRAM files or partition images. Includes interactive ADB tools for rooted…
 giveen/decomp.anything
decomp.wtf fork: Windows PE matching, MinGW/clang-cl toolchains, and an optional REA MCP bridge
 blacktop/ipsw-diffs
Publishes per-build diffs of iOS, iPadOS, and macOS IPSW firmware releases, enabling binary-level comparison of system components across versions and…
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 florentineprinzessinzusachsen/badbox-h713-projector
Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 redzrush101/zte-blade-v40-vita-unlock
Unlocking the ZTE Blade V40 Vita (P606F02 / Unisoc UMS9230 / UFS) bootloader via CVE-2022-38694 - Linux scripts, the FBE post-unlock hang fix, and…
 amd2g2zz/kunglao-agent
The reverse-engineering expert agent: plans its own analysis path, derives every fact from raw evidence, and converges under mechanical verification…
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 asarr22/root-my-galaxy-s938b
KSU installer for supported Samsung Galaxy firmware with CVE-2026-43499
 gadorach/vankyo-s30-bootloader-unlock
Vankyo MatrixPad S30 (Unisoc SC9863A) — Bootloader unlock via CVE-2022-38694 FDL1 method
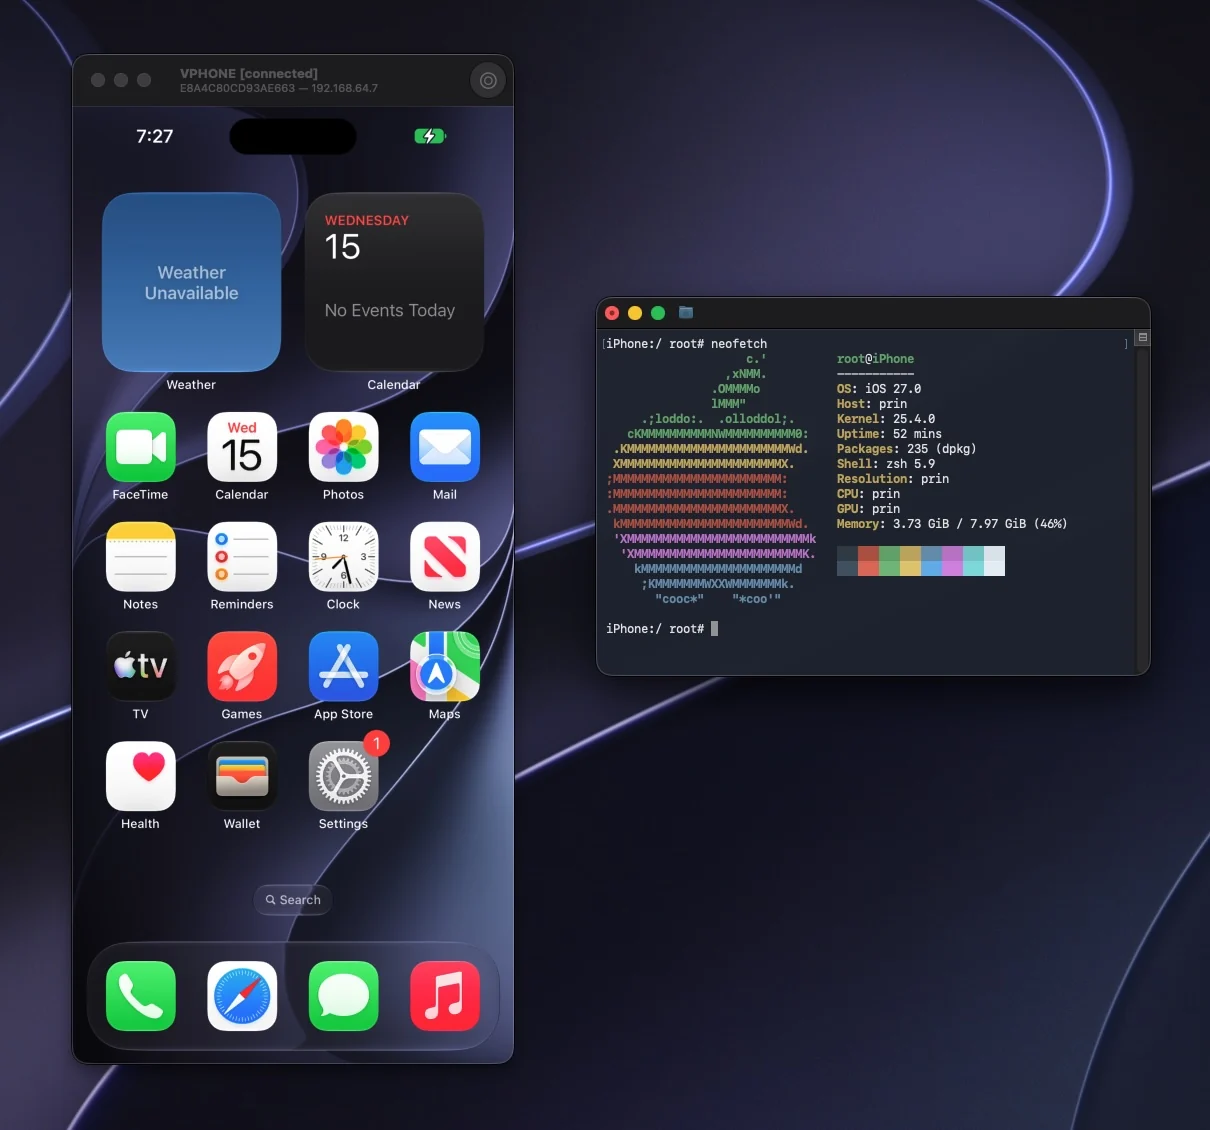 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…

 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.