
CVE-2025-5548
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
binary-exploitationdebuggerseducation+6
raulsineiro/cve-2025-5548Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 kevin-mizu/werkzeug-cve-2022-29361-poc
Proof-of-concept exploit for CVE-2022-29361, demonstrating remote code execution via Werkzeug debugger console in Python web applications.
 luisyapura/analisis-y-explotacion-de-cve-2025-5548
Educational lab for analyzing and exploiting CVE-2025-5548 (FreeFloat FTP Server buffer overflow) with step-by-step guides, debugger setup, and…
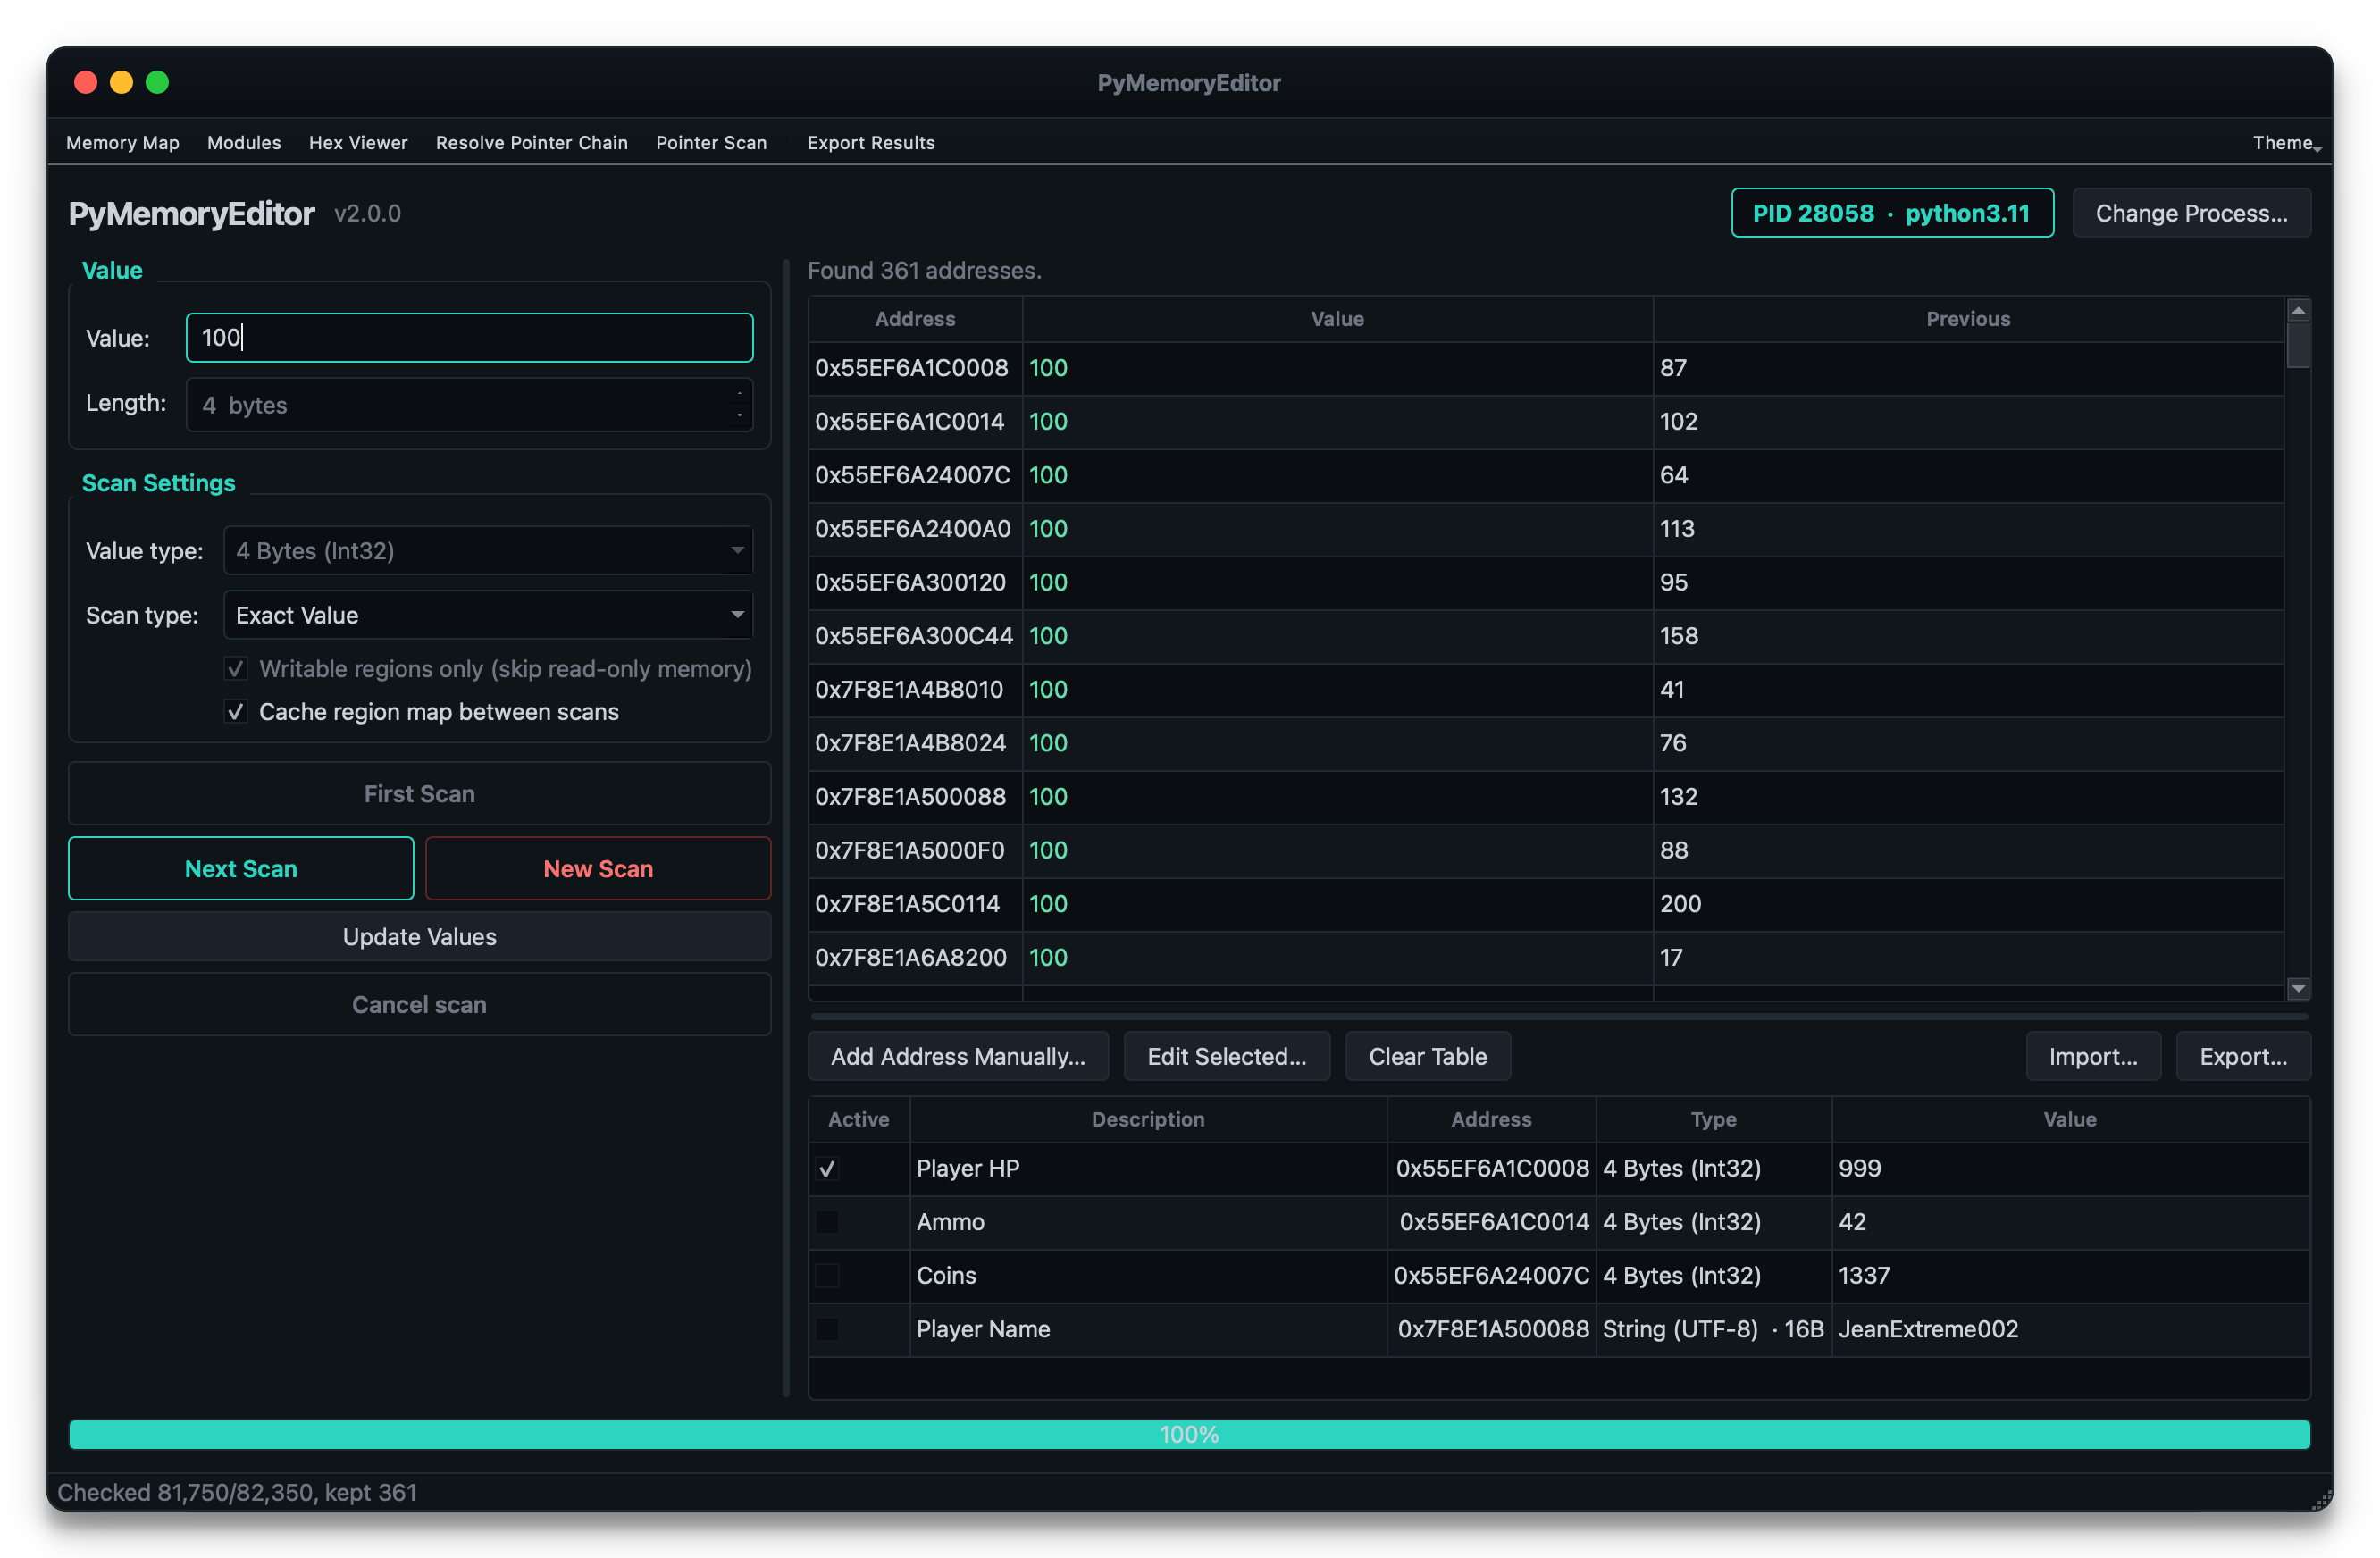 jeanextreme002/pymemoryeditor
A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
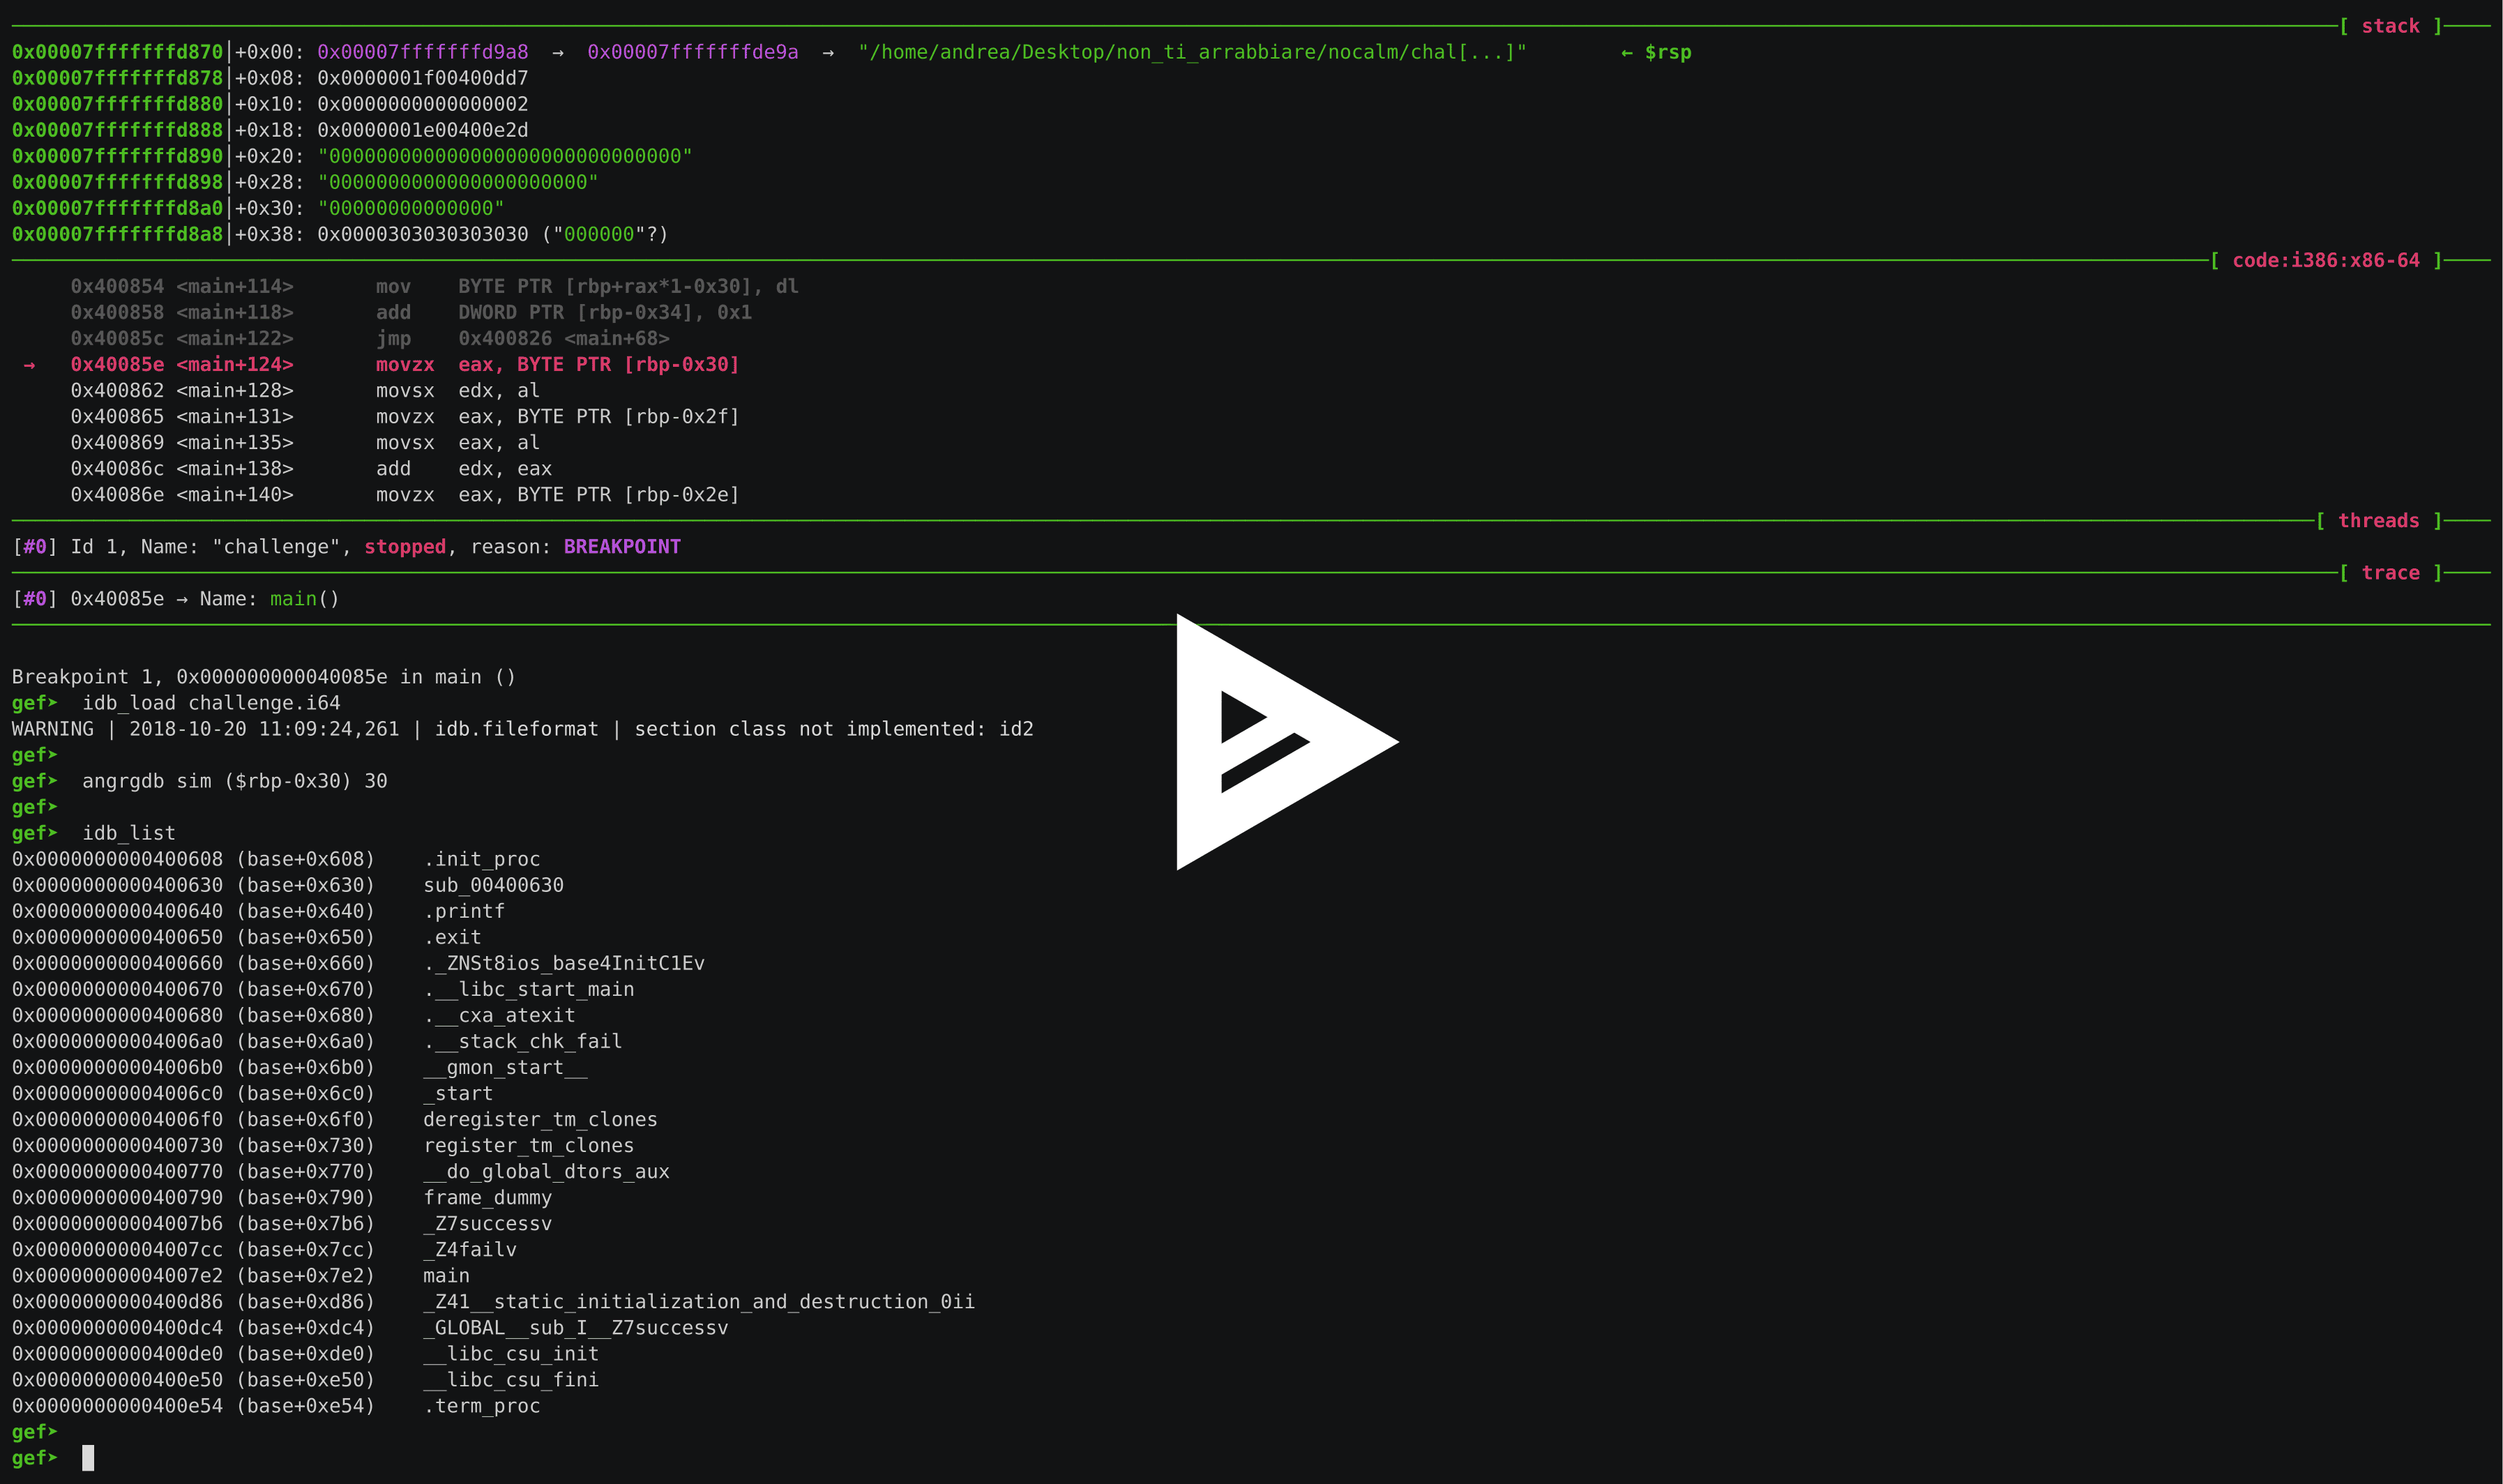 andreafioraldi/angrgdb
Use angr inside GDB. Create an angr state from the current debugger state.
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 openrce/paimei
A reverse engineering framework written in Python.
 nccgroup/libslub
Python library for examining Linux kernel SLUB heap allocations and structures within GDB, enabling deeper understanding of kernel heap internals for…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 gengstah/windbg-mcp
An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
 phantomn/virtualbox_cve-2019-2525-cve-2019-2548
Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 miscusi-peek/cheatengine-mcp-bridge
Connect your favorite AI agents directly to Cheat Engine via MCP. Automate reverse engineering, pointer scanning, and memory analysis using natural…
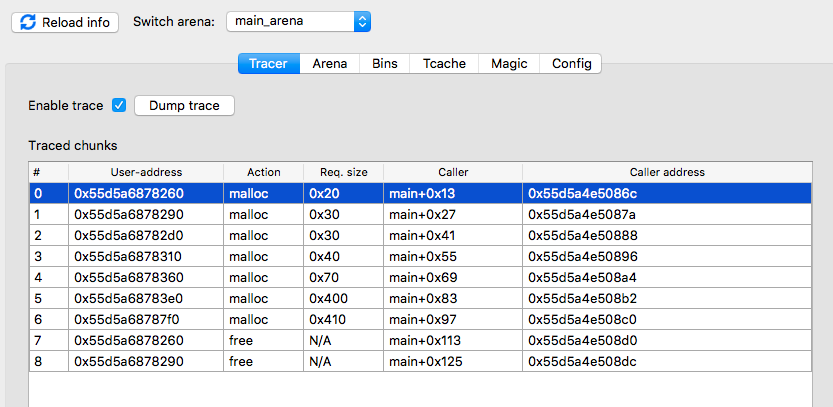 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…