
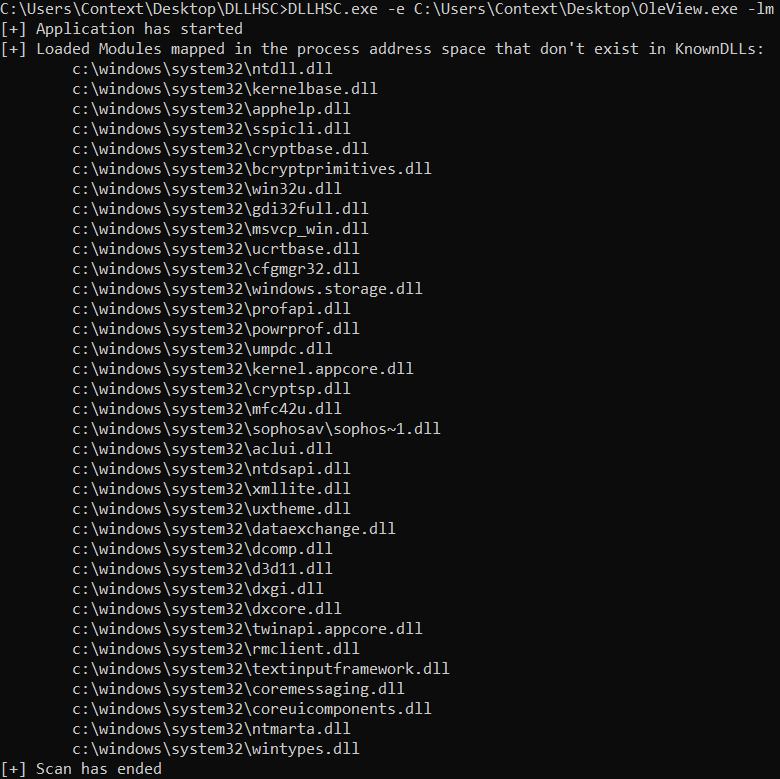
DLLHSC
 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
binary-analysisexploitationpayload-development+1
158
ctxis/dllhscAutomated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 doudouhala/cve-2017-8464-exp-generator
this tool can generate a exp for cve-2017-8486, it is developed by python
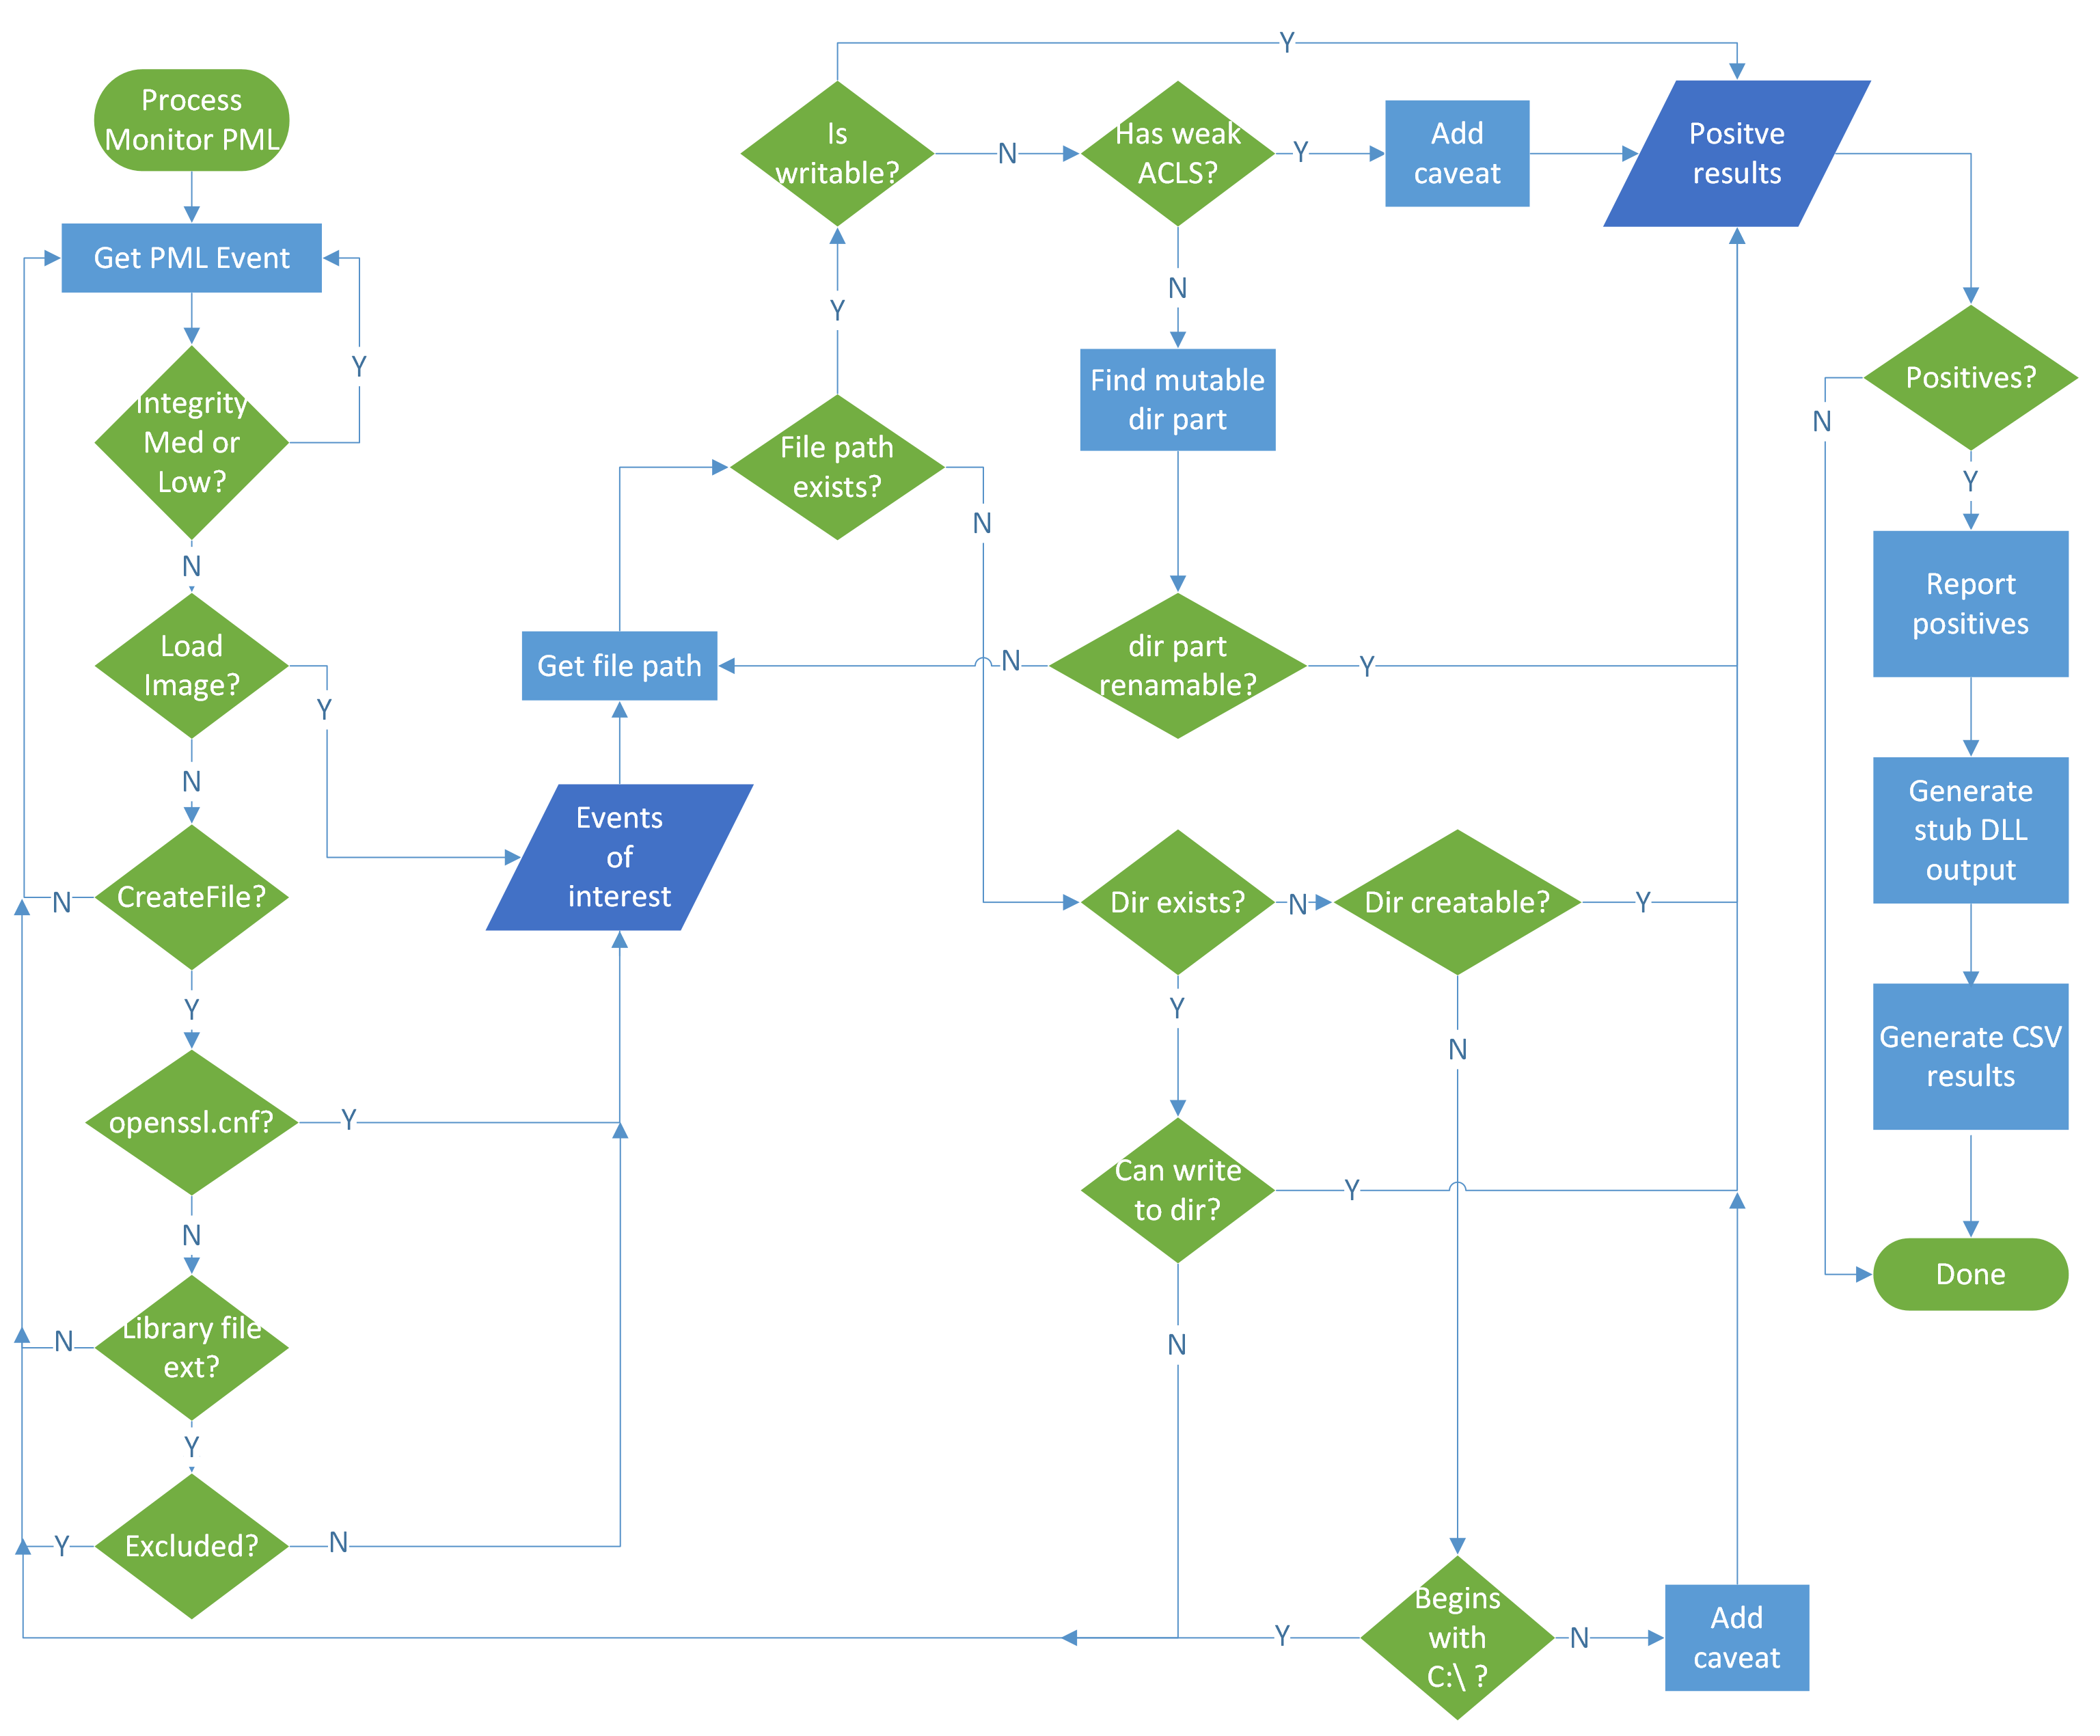 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
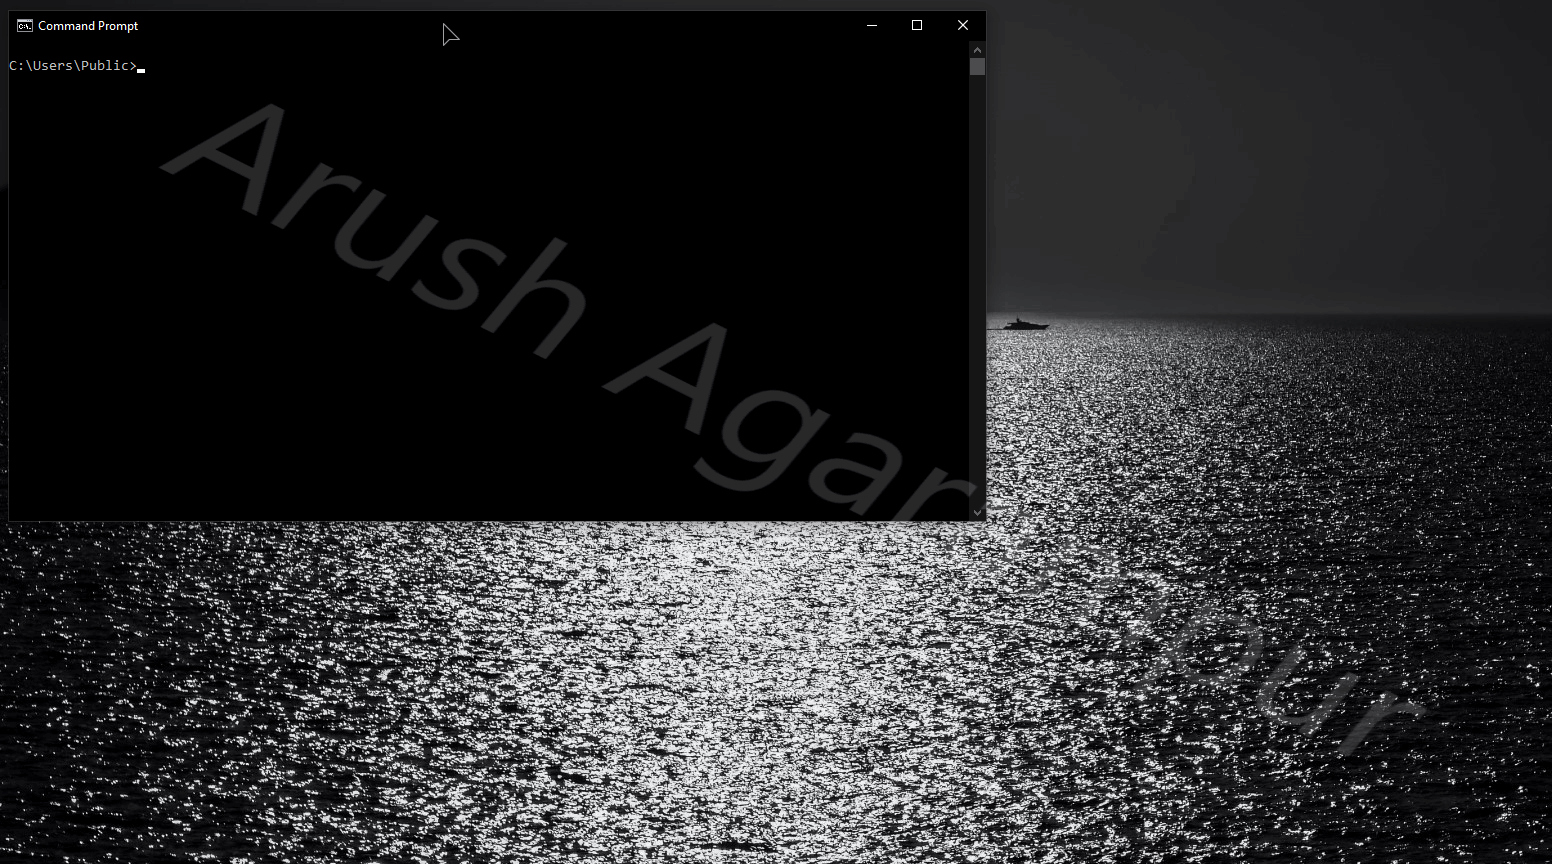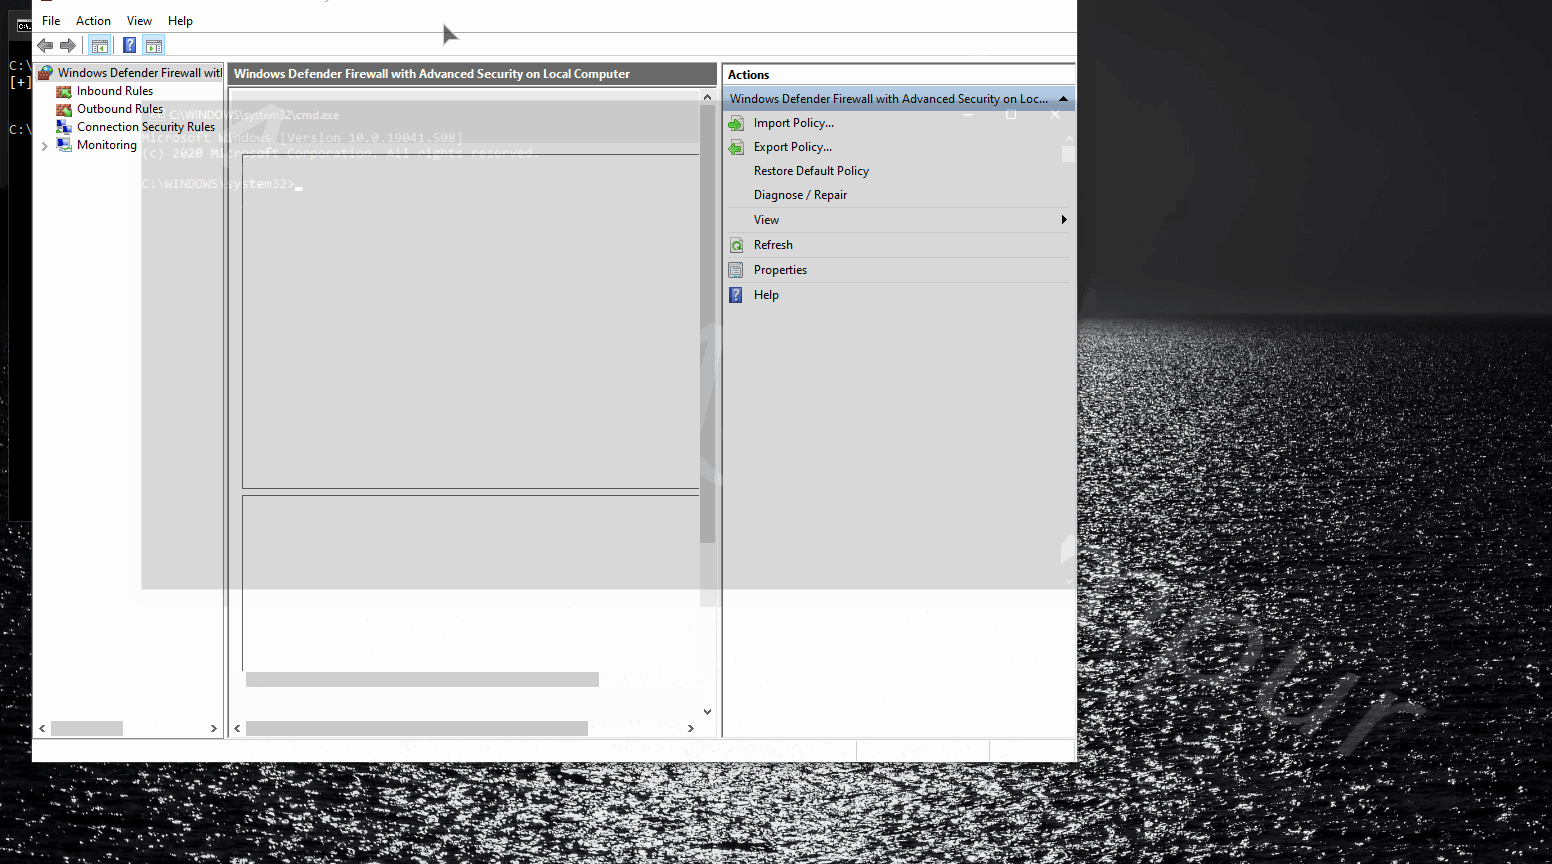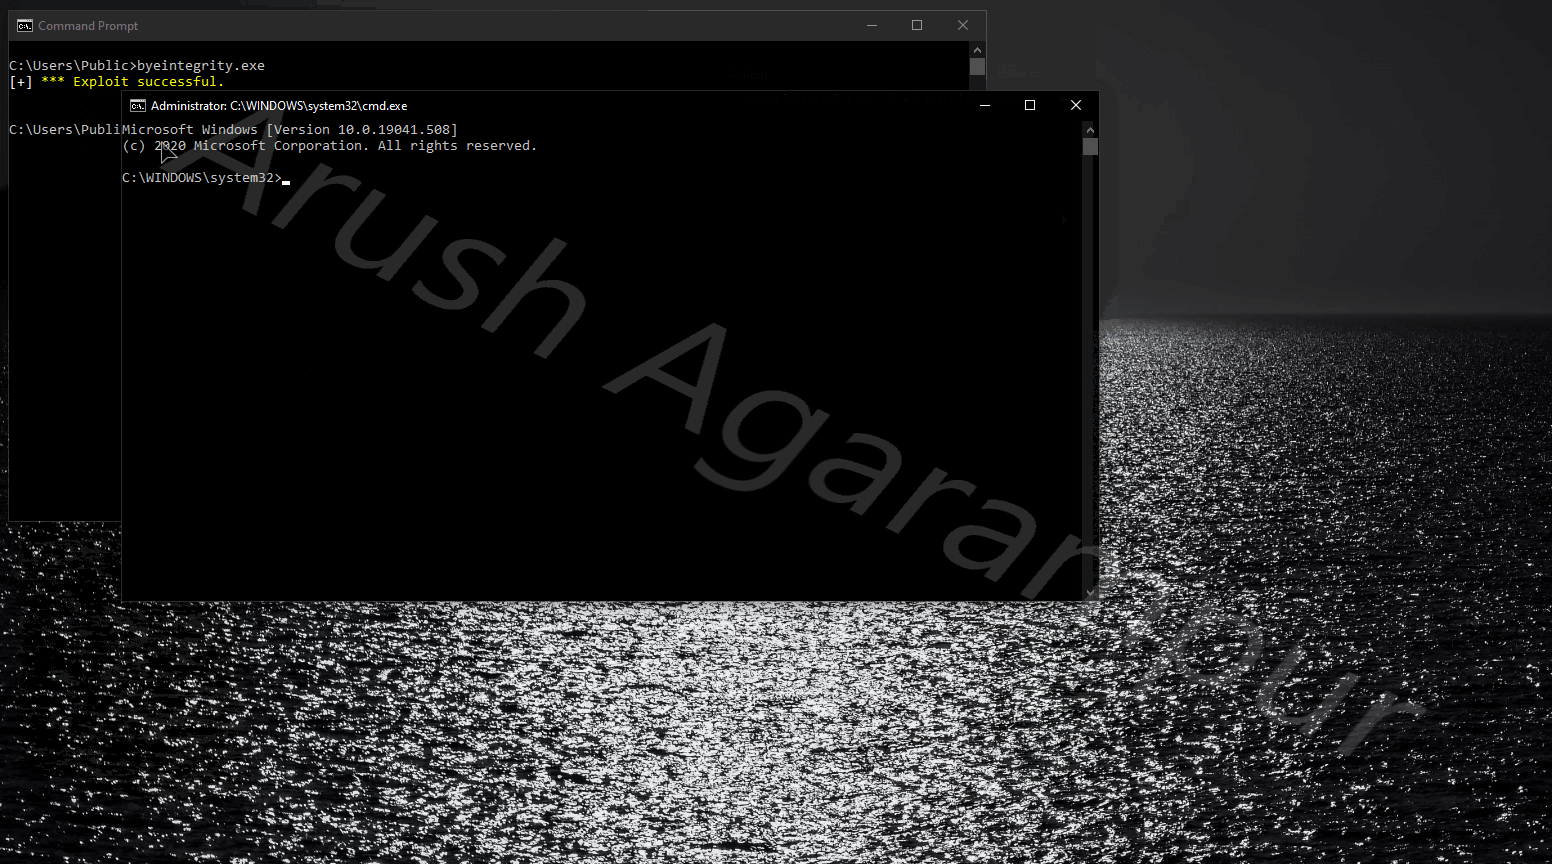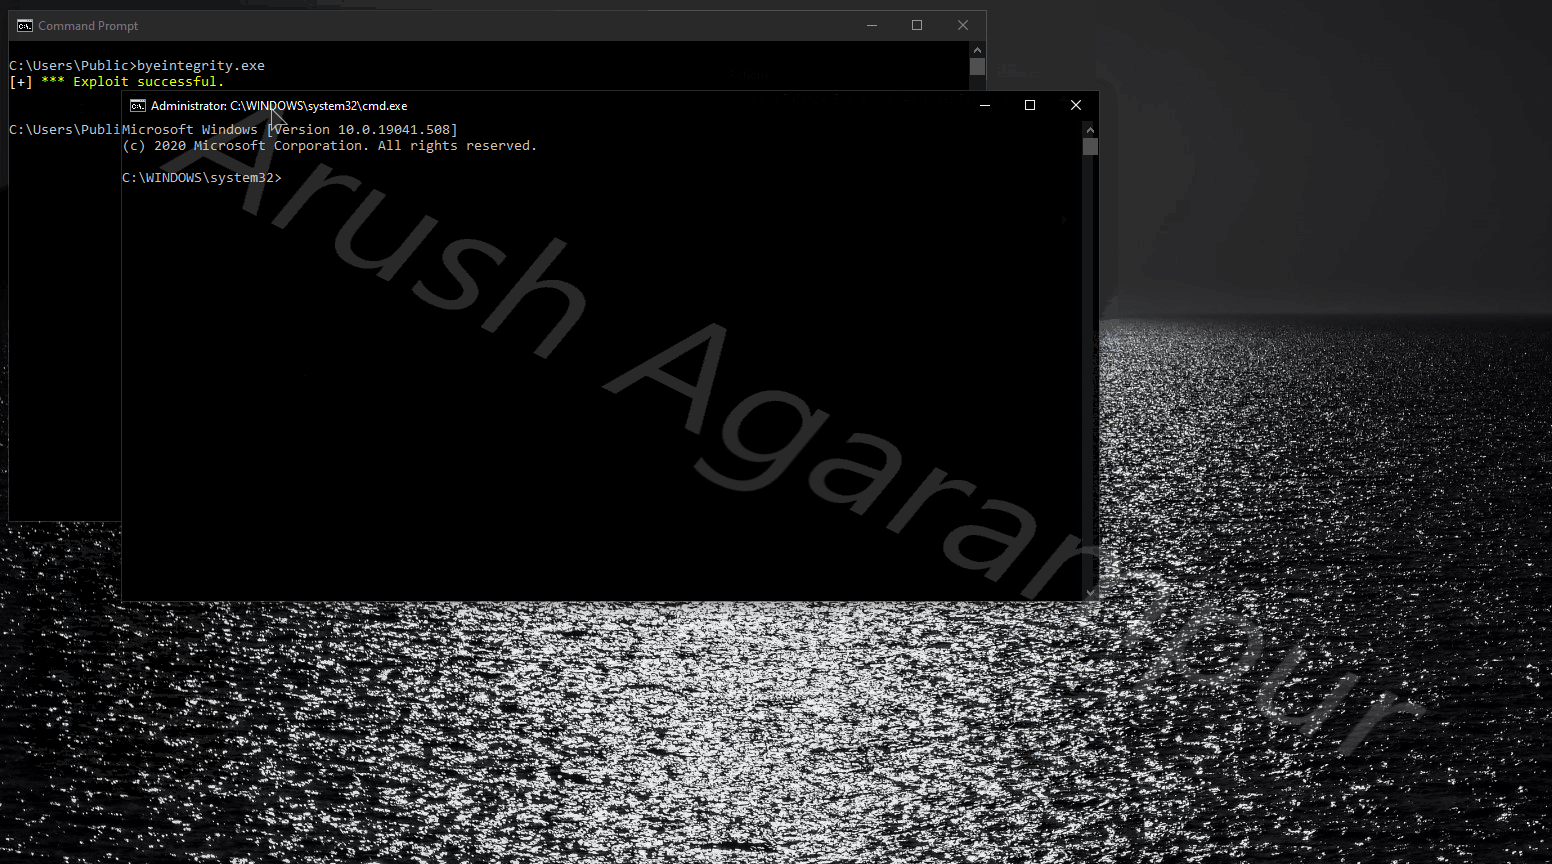 azagarampur/byeintegrity-uac
Bypass UAC by hijacking a DLL located in the Native Image Cache
 jonyfilc/printspoofer-reflectivedll
The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…
 ideaslocas/adll
Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
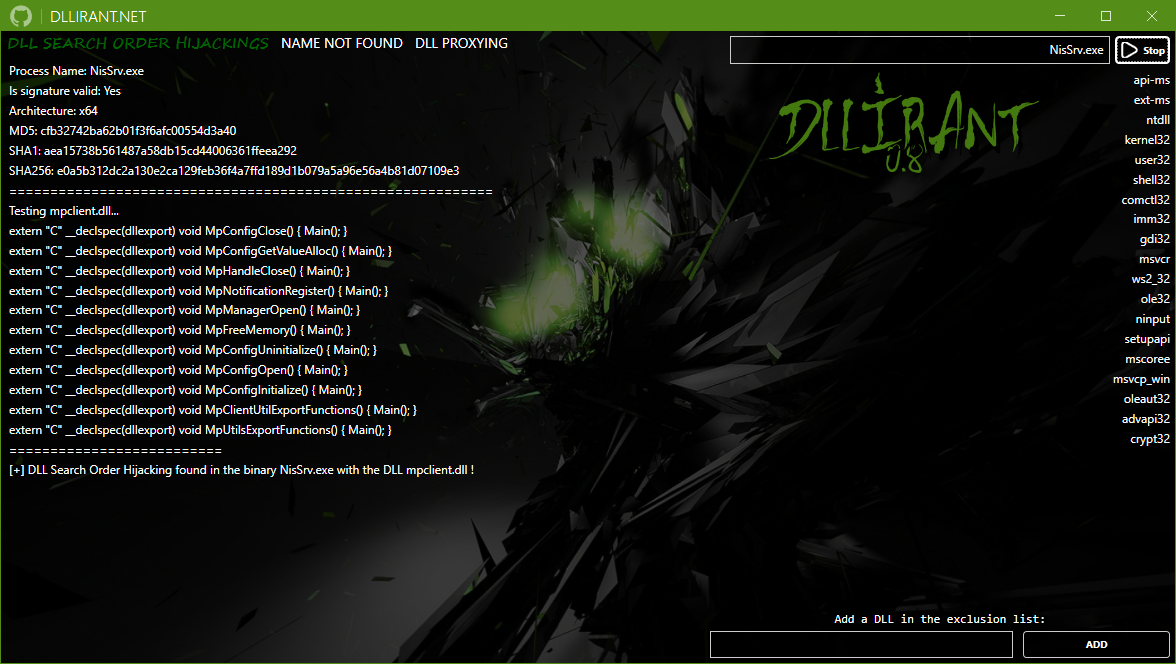 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 al1ex/remotedllinjector
RemoteDLLInjector
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
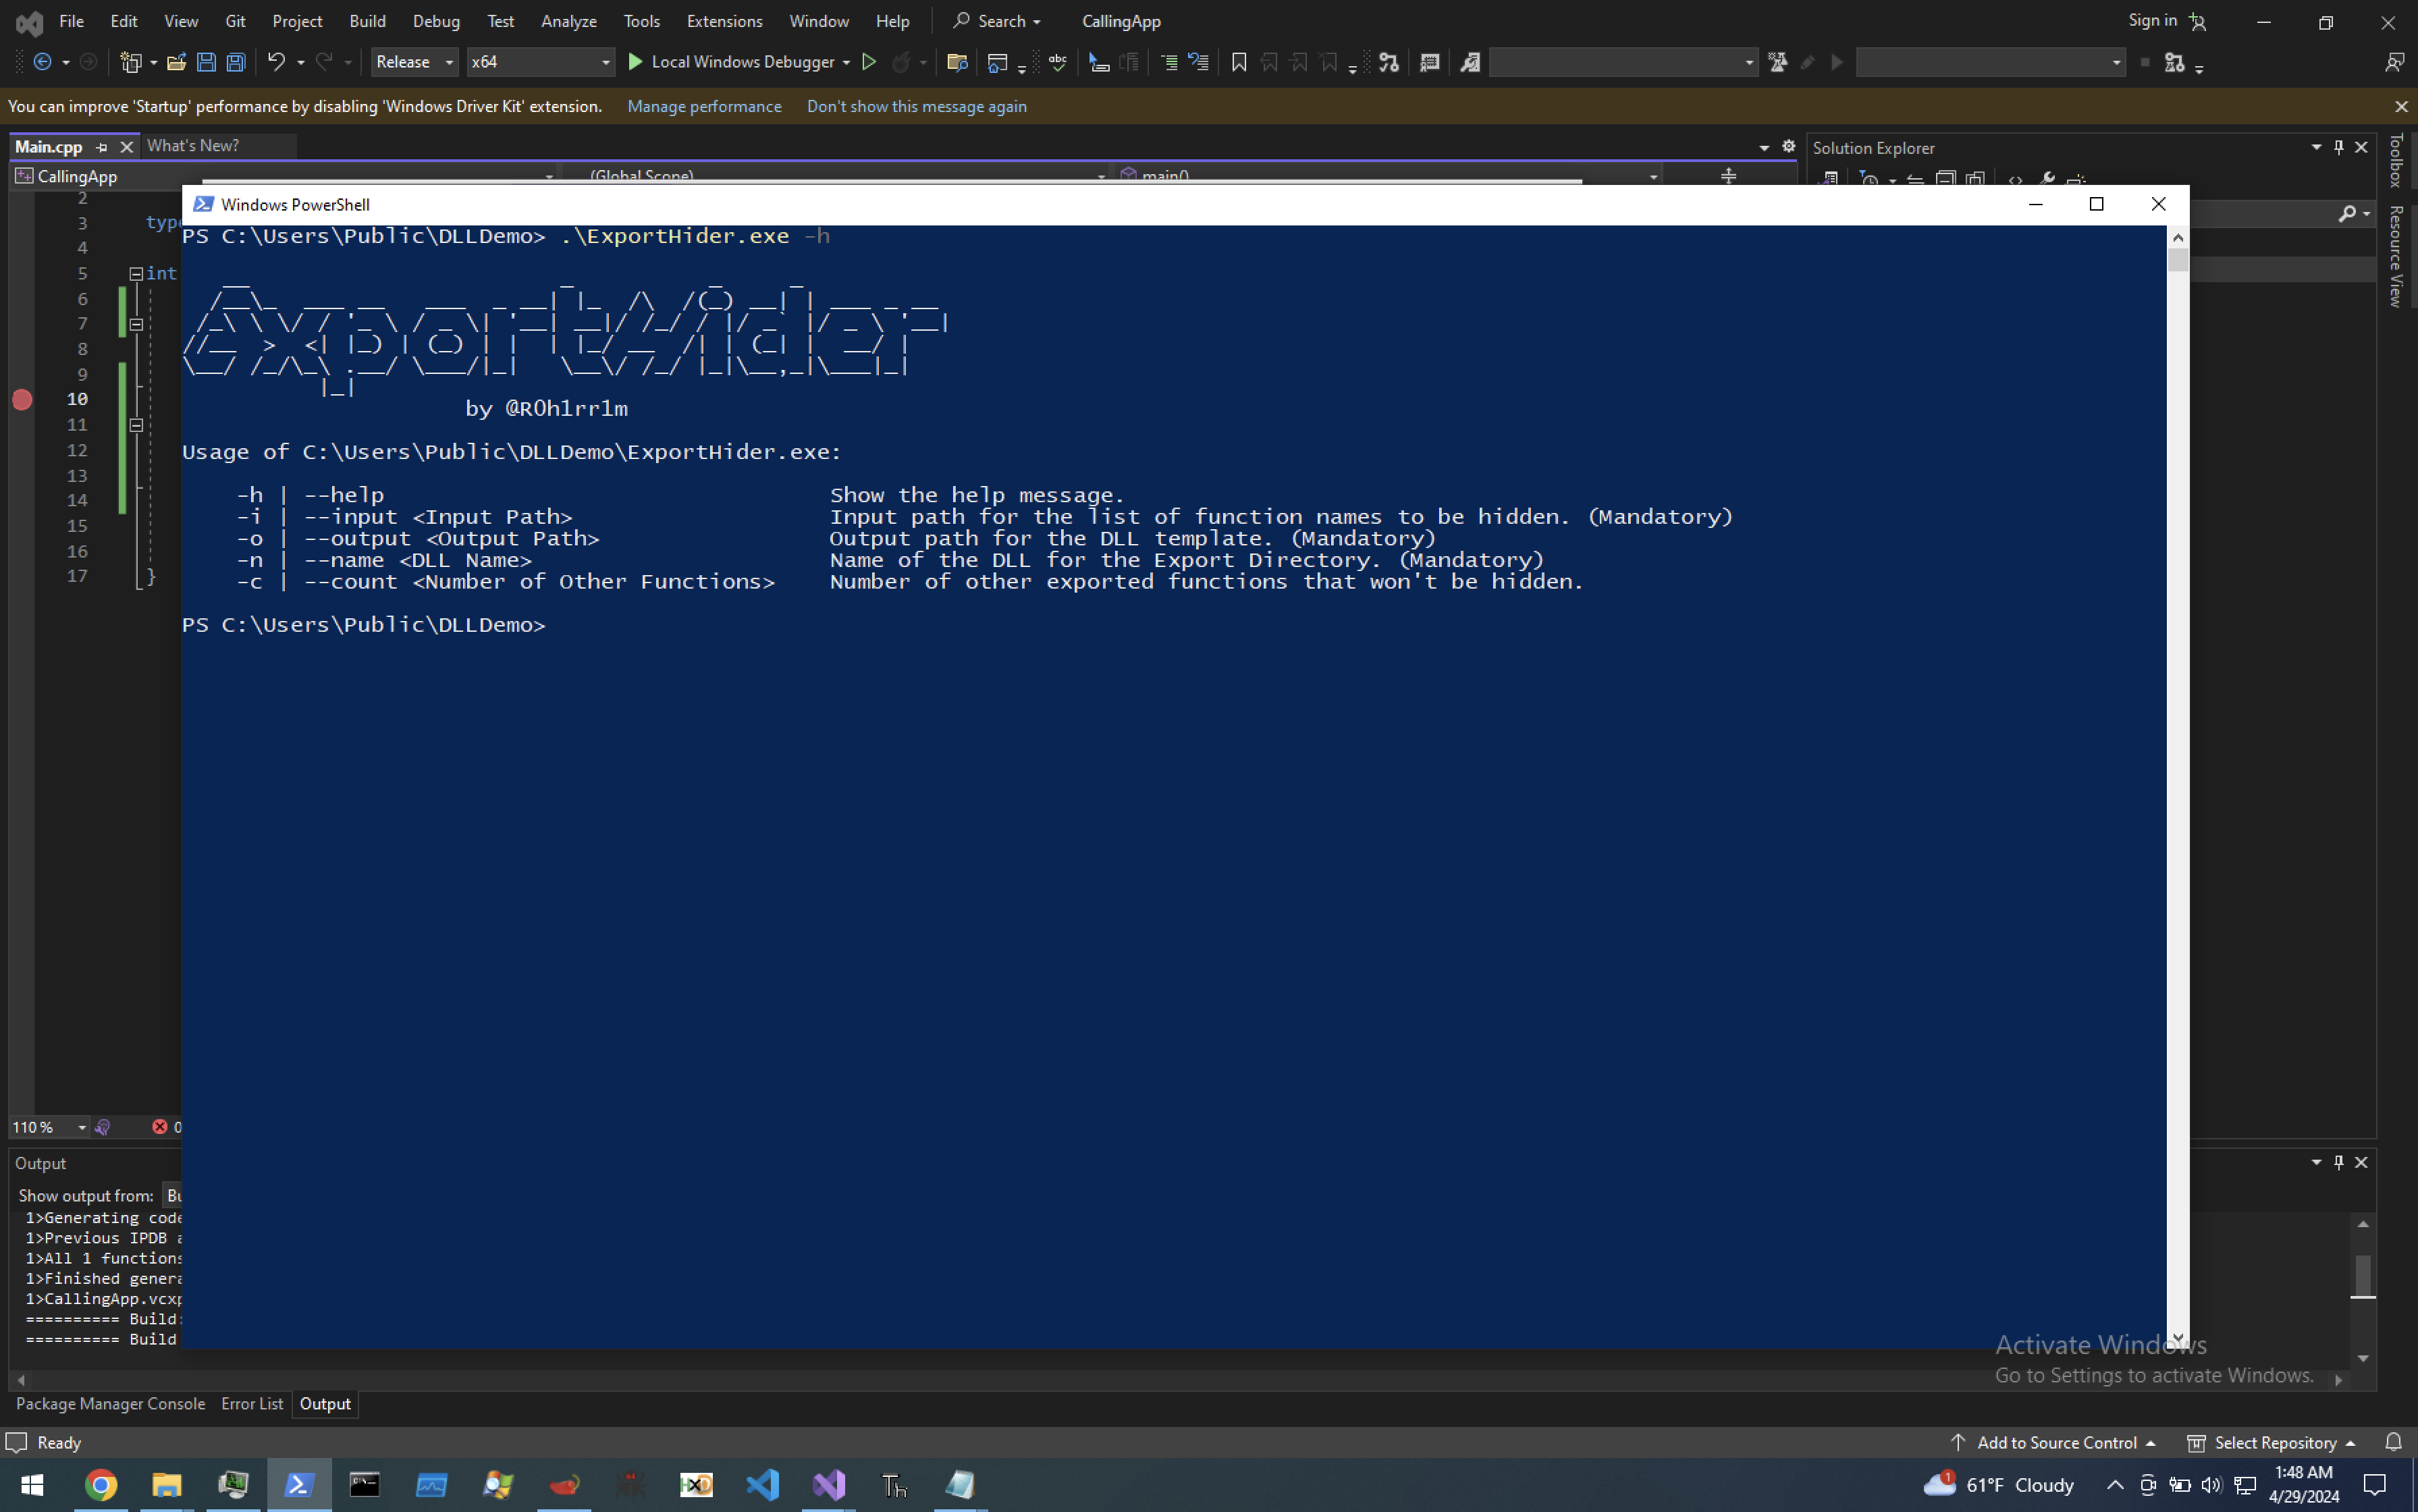 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
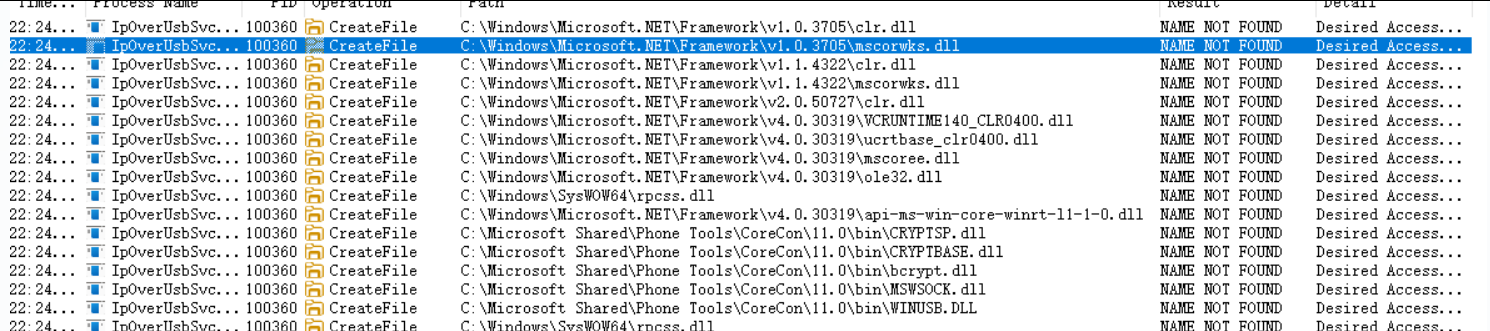 q1uf3ng/cve-2025-47962-poc
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
 0xkickit/icue_dllhijack_lpe-cve-2024-22002
Proof-of-concept exploit for CVE-2024-22002, demonstrating local privilege escalation via DLL hijacking in CORSAIR iCUE's update service to run code…
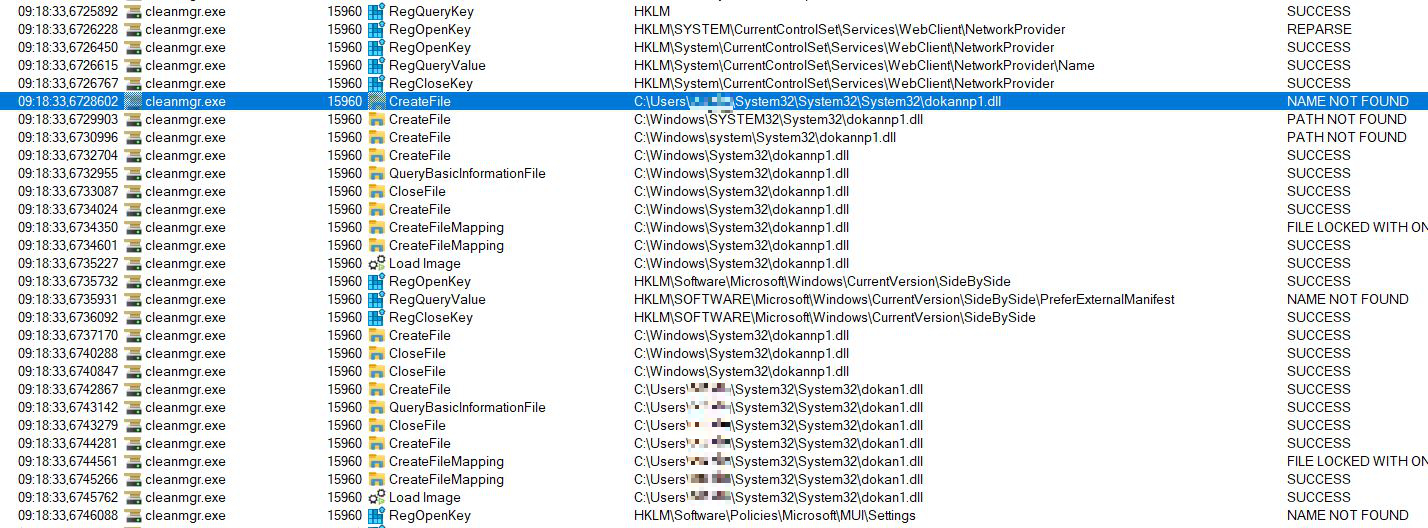 dmitri131313/cve-2025-21420-poc
We found a way to DLL sideload with cleanmgr.exe
 edubr2020/rp_recordclip_dll_hijack
Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.