
CVE-2024-43451-POC
 ronf98/cve-2024-43451-poc
CVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
exploitationmalware-analysispassword-cracking+3
ronf98/cve-2024-43451-pocCVE-2024-43451 is a Windows NTLM vulnerability that allows an attacker to force authentication and capture NTLM hashes by using malicious shortcuts.
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 b4shfire/stegcrack
Exploit script for CVE-2021-27211
 wiire-a/cve-2017-9476
Hidden AP with Deterministic Credentials
 helica-core/eap_pwn
poc of CVE-2023-52160
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
 und3sc0n0c1d0/bruteforce-to-keepass
This script complements the results obtained through the keepass-password-dumper tool when exploiting the CVE-2023-32784 vulnerability affecting…
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
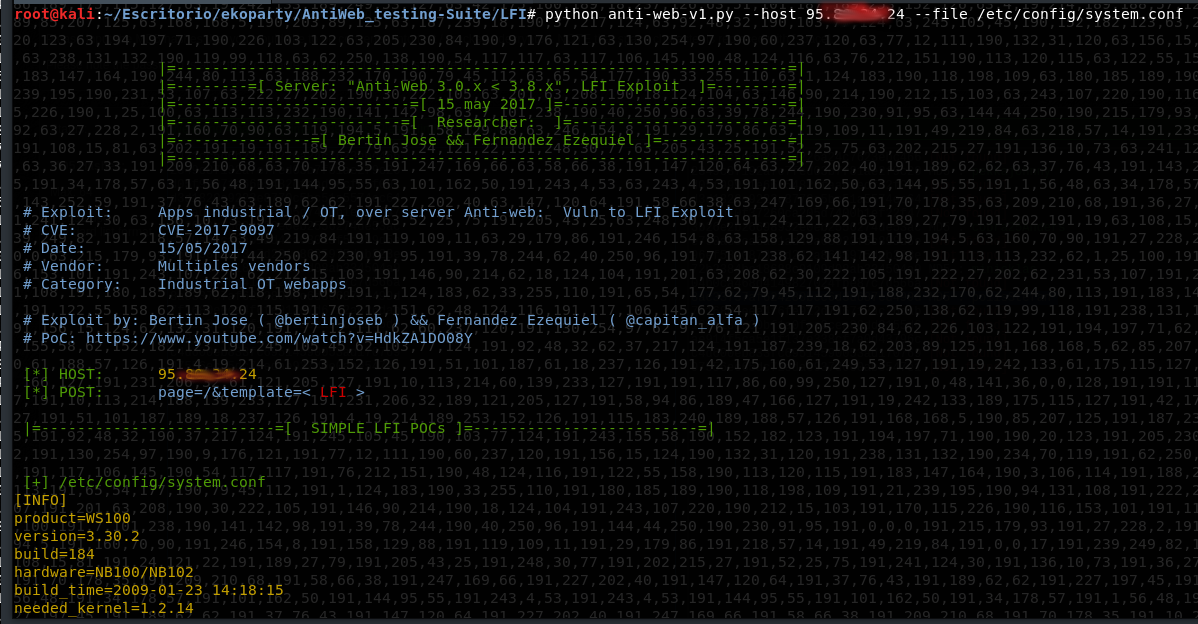 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 0xcccc666/cve-2020-1472_tool-collection
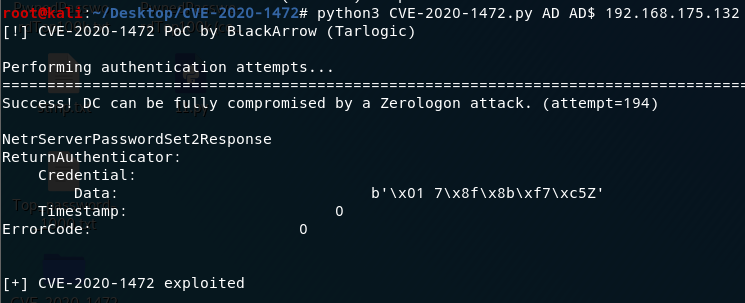
cve-2020-1472_Tool collection
 azrenom/cms-made-simple-2.2.9-cve-2019-9053
Exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks the…