
gha-lab-d14c91f1bb
 pvharmo2/gha-lab-d14c91f1bb
Security-research lab: reproduction of CVE-2025-58371 (GitHub Actions command injection via PR title in Discord PR Notifier), snapshot of…
curated-resourceseducationexploitation+1
pvharmo2/gha-lab-d14c91f1bbSecurity-research lab: reproduction of CVE-2025-58371 (GitHub Actions command injection via PR title in Discord PR Notifier), snapshot of…
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 peakcyber-security/cve-2025-14847
CVE-2025-14847 | MongoBleed vulnerability proof of concept project
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 tranqtruong/detect-bluekeep
a simple tool to detect the exploitation of BlueKeep vulnerability (CVE-2019-0708)
 1h3ll/cve-2025-50364_csrf_add_category-phpgurukul-cve
Proof-of-concept CSRF exploit targeting CVE-2025-50364 in PHPGurukul Maid Hiring Management System v1.0 that adds arbitrary admin categories via a…
 byt3bl33d3r/gcat
A PoC backdoor that uses Gmail as a C&C server
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
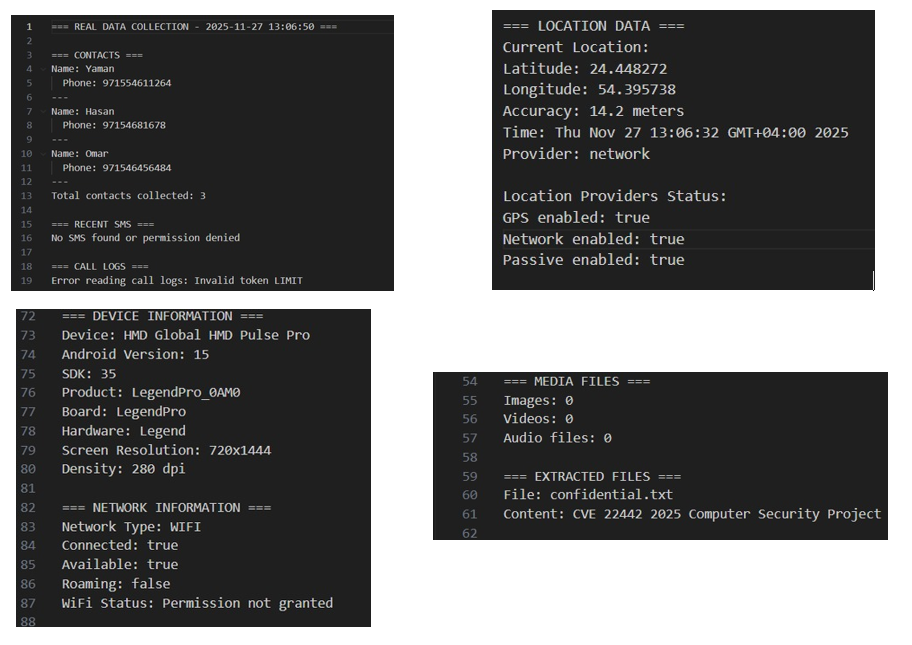 hasan-al-hussein/android-workprofile-exploit
Controlled defensive analysis of CVE-2025-22442 work-profile provisioning, policy timing, and enterprise isolation.
 zanks08/cve-2023-44487-demo
Demo for detection and mitigation of HTTP/2 Rapid Reset vulnerability (CVE-2023-44487)
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
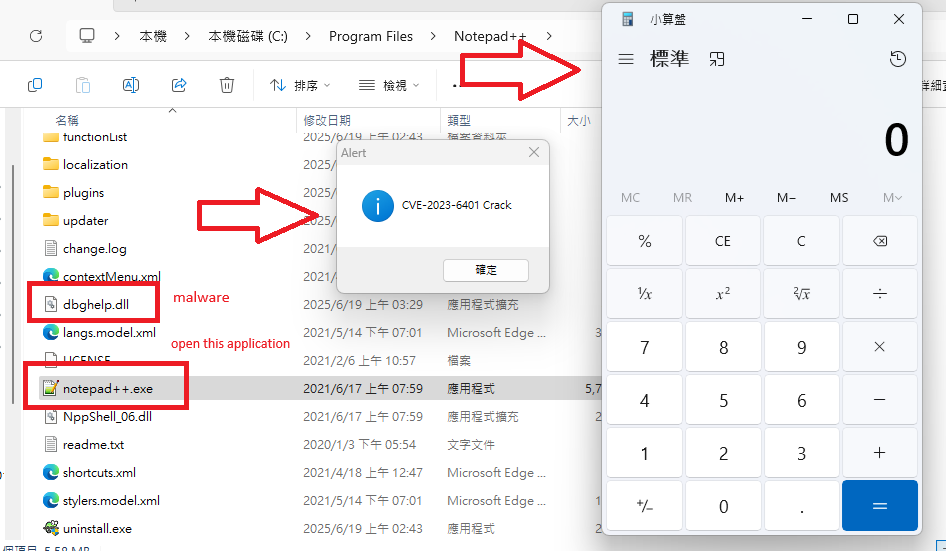 mekitoci/cve-2023-6401
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…
 dream434/cve-2021-42013-apache
On October 4, 2021, Apache HTTP Server Project released Security advisory on a Path traversal and File disclosure vulnerability in Apache HTTP Server…
 kkc73/weblogic-cve-2020-14882
This is a repository that aims to provide research material on CVE-2020-14882 as part of a project in partial fullfilment of ACS EDU Program.