
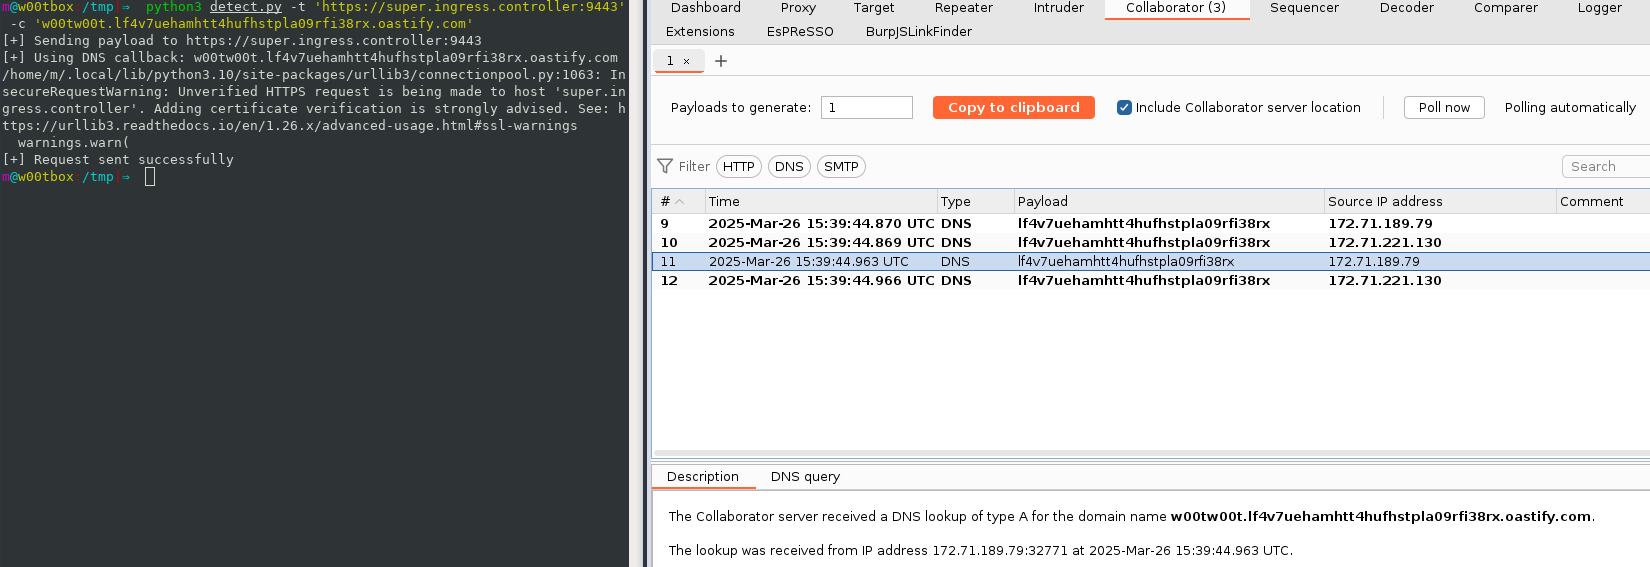
ingressnightmare-detection-poc
 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
cloud-securityexploitationmisconfiguration+3
m-q-t/ingressnightmare-detection-pocProof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 bvcyber/cve-2020-1472
Python script using Impacket to test for CVE-2020-1472 (Zerologon) vulnerability via Netlogon authentication bypass on Windows domain controllers.
 mcw0/poc
Issues has been disabled for these PoC's, as they are simply PoC, Public Domain and unsupported.
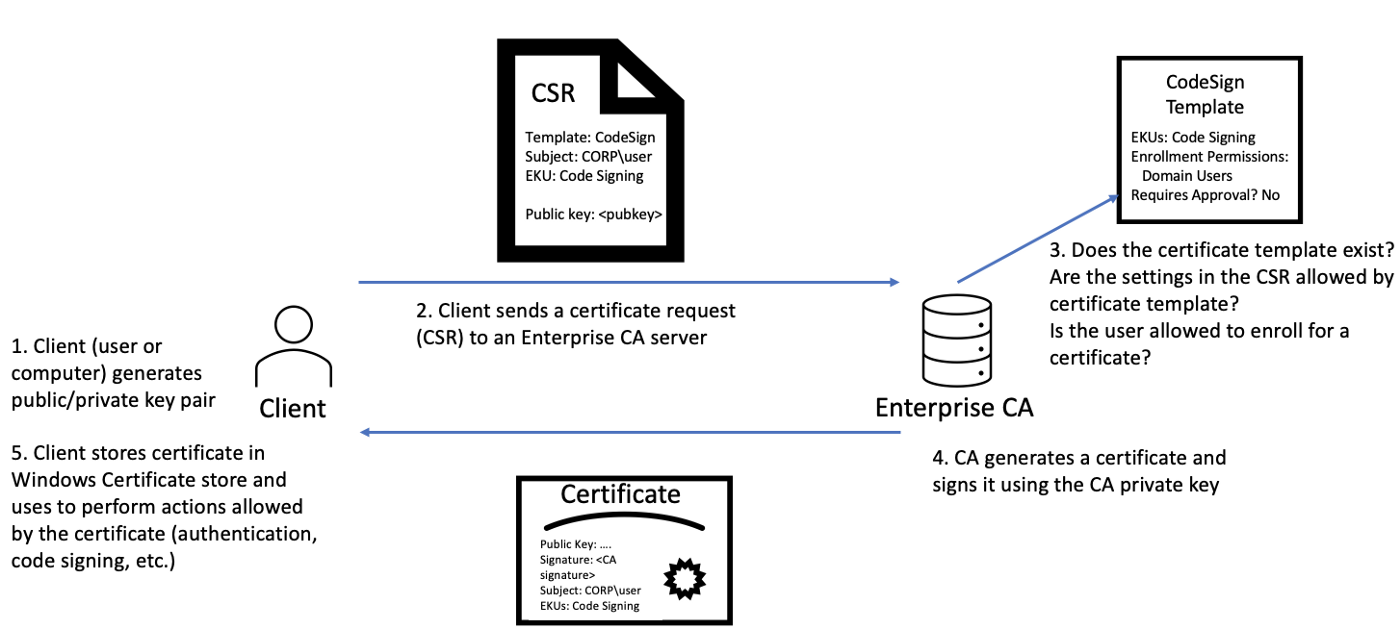 ghostpack/forgecert
Forge certificates for Active Directory authentication using stolen Certificate Authority private keys, enabling persistent domain access with forged…
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 fox-it/cve-2019-1040-scanner
SMB vulnerability scanner that detects CVE-2019-1040 by sending invalid NTLM authentication packets, enabling MIC Remove relay attacks for domain…
 mordavid/donpwner
Advanced Domain Controller attack and credential analysis tool leveraging DonPAPI database
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 cybrly/badsuccessor
Exploits the Windows Server 2025 dMSA privilege escalation vulnerability to enumerate writable OUs, escalate to arbitrary domain users, extract…
 knqyf263/cve-2019-6467
Dockerized proof-of-concept exploit for CVE-2019-6467, a BIND nxdomain-redirect vulnerability, enabling DNS cache poisoning via non-existent domain…
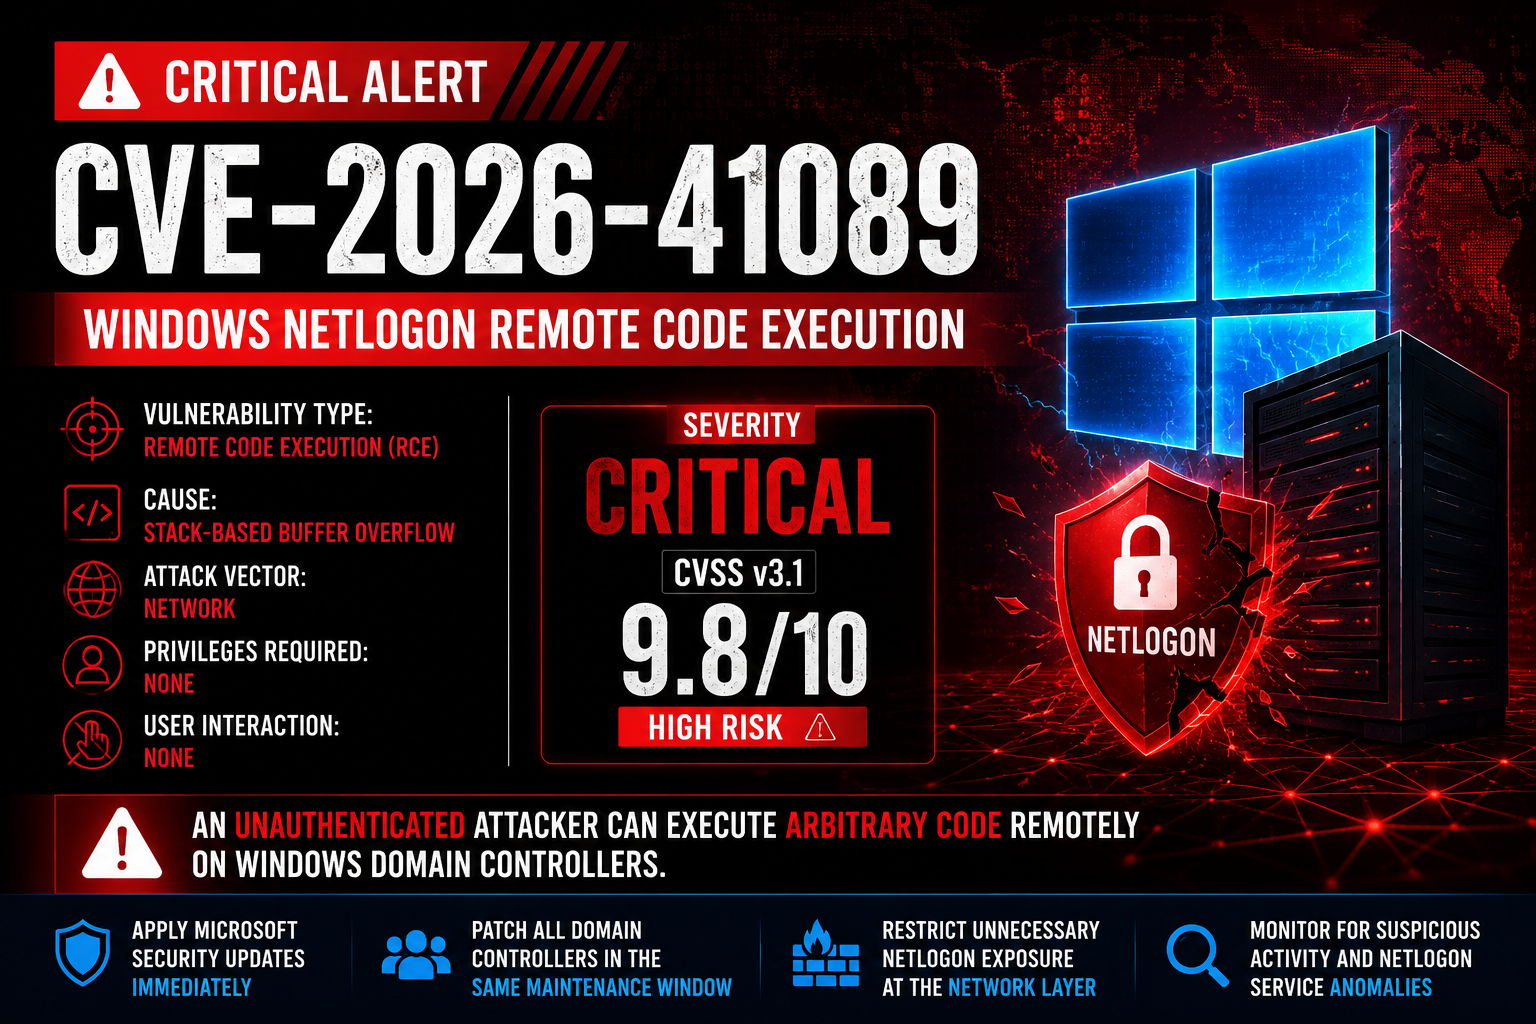 hydrasoft/cve-2026-41089-netlogon-rce
Technical analysis and Proof-of-Concept (PoC) for CVE-2026-41089, a critical unauthenticated Remote Code Execution (RCE) vulnerability in the Windows…
 sq00ky/zero-logon-exploit
Python script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.
 ac3lives/kyocera-cve-2022-1026
An unauthenticated data extraction vulnerability in Kyocera printers, which allows for recovery of cleartext address book and domain joined passwords
 adarshvs/cve-2020-3580
Automated bulk IP or domain scanner for CVE 2020 3580. Cisco ASA and FTD XSS hunter.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 b34mr/zeroscan
Zeroscan is a Domain Controller vulnerability scanner, that currently includes checks for Zerologon (CVE-2020-1472), MS-PAR/MS-RPRN and SMBv2 Signing.