CVE-2019-9053---CMS-Made-Simple-SQL-Injection-Exploit-Modified-

This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…

This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…

Unauthenticated remote code execution exploit for Simple Image Gallery 1.0, with a detailed write-up and ExploitDB reference.

simple program for joomla scanner CVE-2023-23752 with target list

A short and sweet simple exploit script for the CVE-2012-2982 Authenticated RCE vulnerability in the /file/show.cgi/bin endpoint.

A simple simulation of the infamous CVE-2021-44228 issue.

Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…

PoC for CVE-2018-15133 (Laravel unserialize vulnerability)

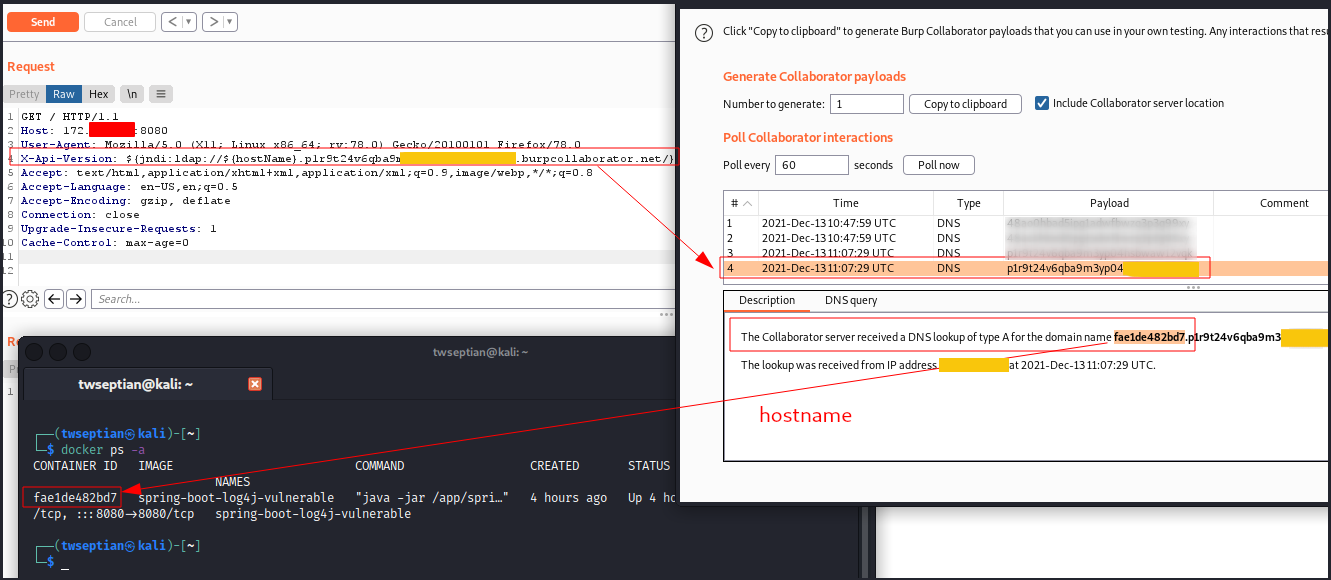
Spring Boot Log4j - CVE-2021-44228 Docker Lab

Adobe Magento SessionReaper LFI Vulnerability

log4j2 Log4Shell CVE-2021-44228 proof of concept

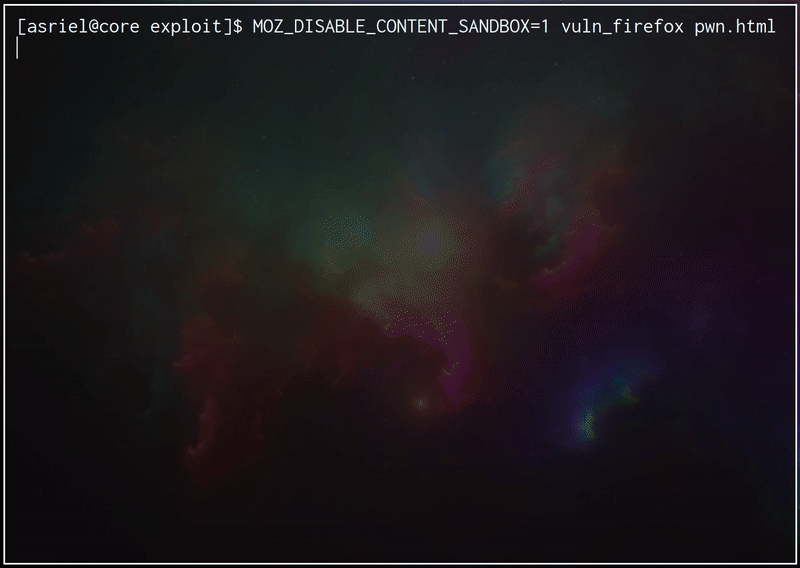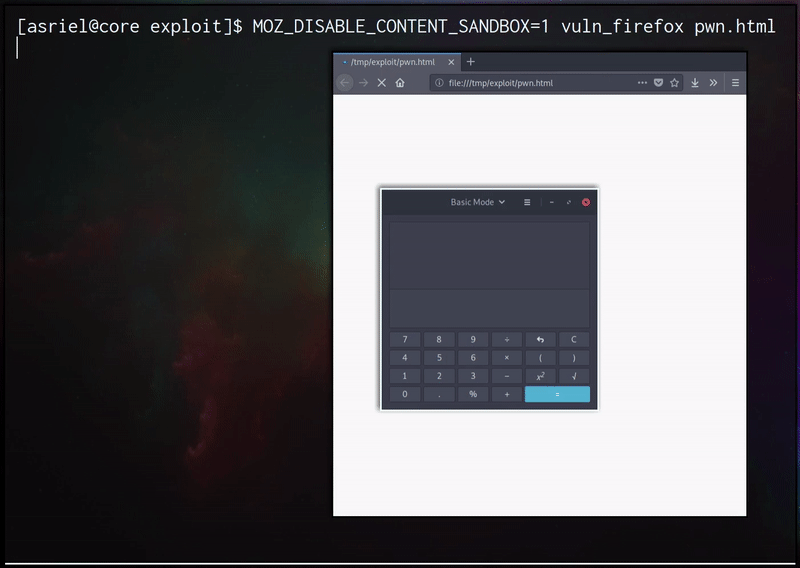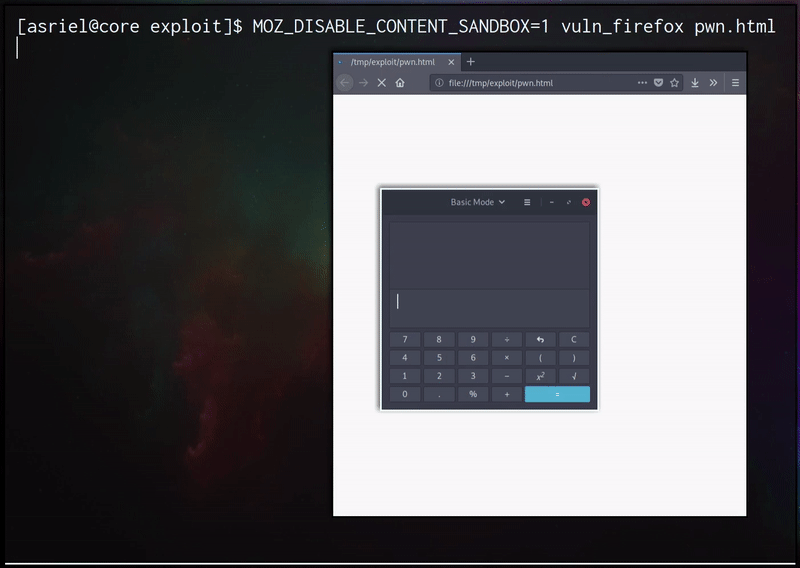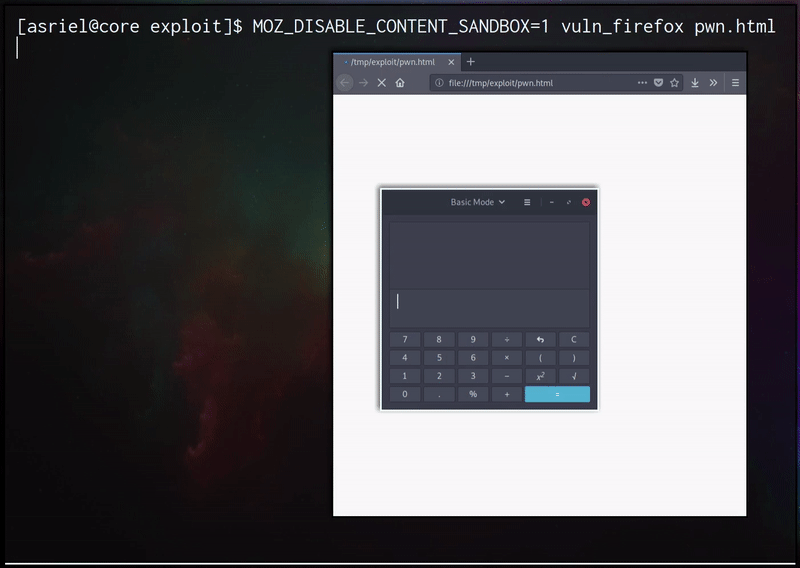
CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)

Apache Struts CVE-2017-5638 RCE exploitation

Proof-of-concept exploit for CVE-2026-55168 demonstrating authenticated arbitrary file write via symlink planting during backup restore in Runtipi.

Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes a Python script demonstrating…

PoC (Proof of Concept) de la CVE-2024-4367 - Vulnérabilité RCE dans libwebp. Démonstration complète incluant : création de payloads, scénarios…

CVE-2022-23305 Log4J JDBCAppender SQl injection POC

POC for CVE-2021-44228 within Springboot

Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…